CVE-2023-41425-RCE-WonderCMS-4.3.2

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…

This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…

This is Metasploit module who exploit the command injection vulnerability in control center of the agent Tesla.

This repository contains a Metasploit module implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…

Python PoC for CVE-2025-4138, a path traversal in Python's tarfile module abusing symlink chains to bypass PATH_MAX for arbitrary file write

FreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit

This exploit for CVE 2018-11759, vulnerability in apache mod_jk, module for load-balancer

fixed msf module for cve-2017-7269

PoC for CVE-2020-6287 The PoC in python for add user only, no administrator permission set. Inspired by @zeroSteiner from metasploit. Original…

This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…

Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

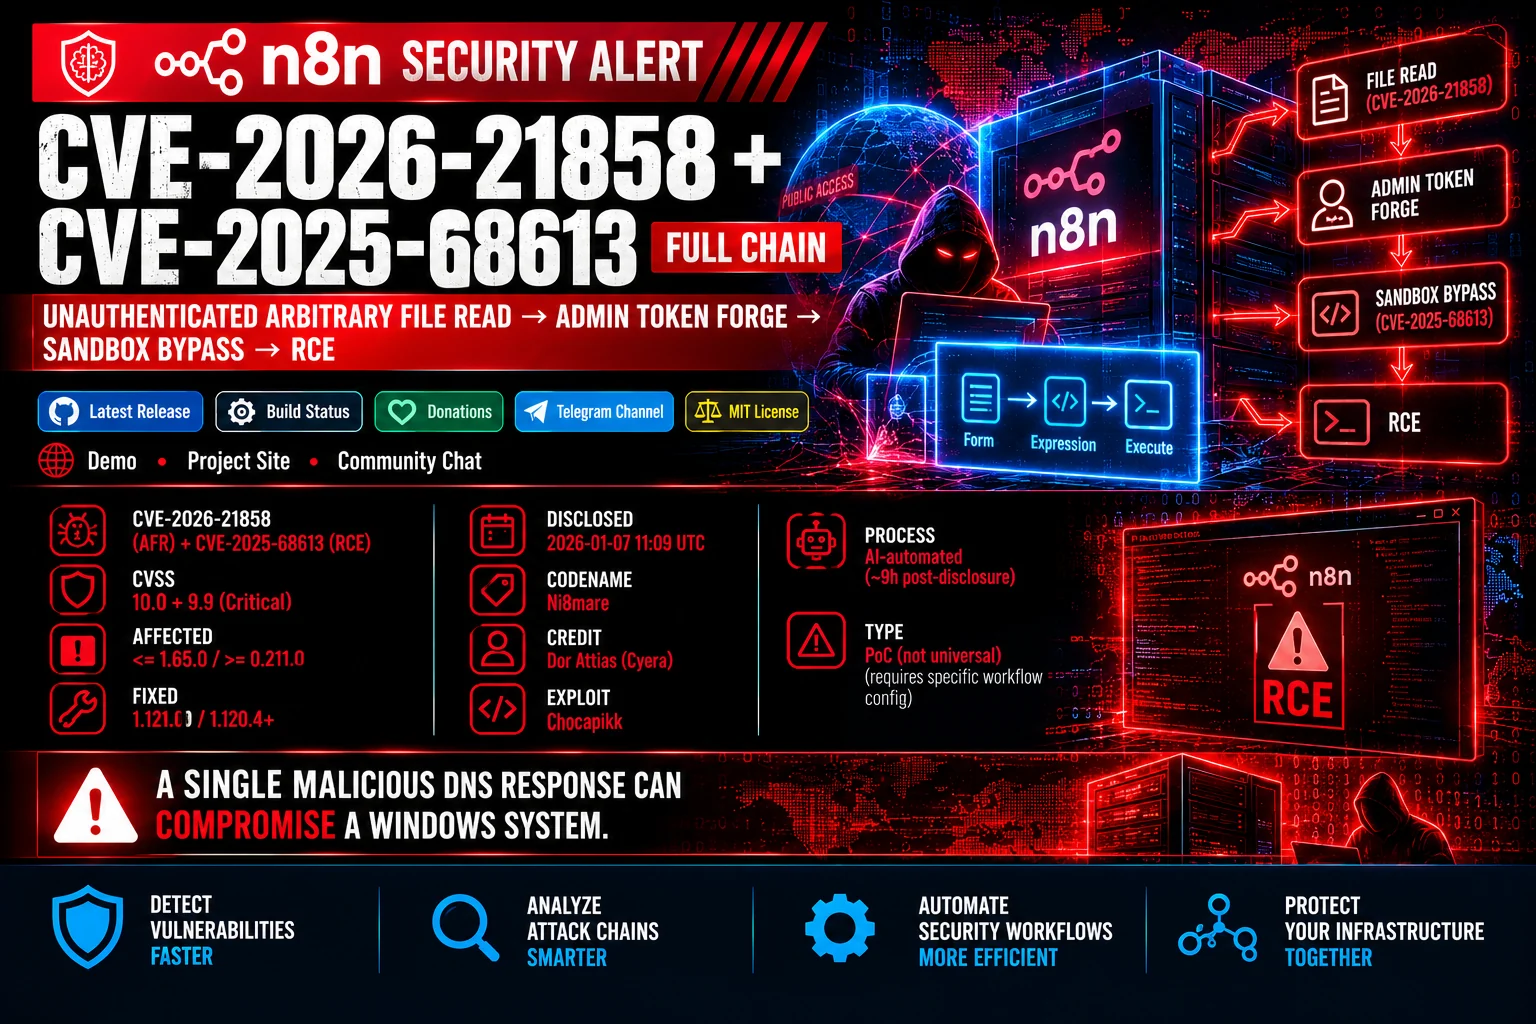
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…

Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…

Proof-of-concept exploit for CVE-2019-6340 targeting Drupal's RESTful web services module, with curl-based RCE payload and detailed reproduction…

Exploit for PrestaShop bockwishlist module 2.1.0 SQLi (CVE-2022-31101)

Proof-of-concept exploit module for CVE-2019-11043 (PHP-FPM remote code execution) with batch scanning capabilities for vulnerable Nginx…