Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
CitrixBleedCVE-2026-8452-2025-5777 preview

CitrixBleedCVE-2026-8452-2025-5777

GitHubmaxprog-svg/citrixbleedcve-2026-8452-2025-5777

CitrixBleed Exploit Tool - CVE-2025-5777 & CVE-2026-8452. Unauthenticated remote memory read from Citrix NetScaler ADC & Gateway. Steal admin session…

exploitationinformation-gatheringpenetration-testing+3

1 month ago
CVE-2026-89012 preview

CVE-2026-89012

GitHubfaceless0x7/cve-2026-89012

Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

api-securitydata-exfiltrationexploitation+6
626 days ago
CVE-2021-29156 preview

CVE-2021-29156

GitHubguidepointsecurity/cve-2021-29156

Proof-of-concept exploit for CVE-2021-29156, an LDAP injection vulnerability in ForgeRock OpenAM v13.0.0, enabling character-by-character brute force…

exploitationinformation-gatheringpenetration-testing+2
43 years ago
CVE-2025-52488 preview

CVE-2025-52488

GitHubsh4den/cve-2025-52488

This exploit targets a vulnerability in DNN (formerly DotNetNuke) versions 6.0.0 to before 10.0.1 that allows attackers to disclose NTLM hashes…

exploitationinformation-gatheringpassword-attacks+3
23 months ago
CVE-2025-24799 preview
Archived

CVE-2025-24799

GitHubrosemary1337/cve-2025-24799

Exploits GLPI CVE-2025-24799 via unauthenticated time-based blind SQL injection to extract usernames and password hashes from glpi_users for…

exploitationpenetration-testingvulnerability-analysis+2
1 year ago
CVE-2024-4956 preview

CVE-2024-4956

GitHubfin3ss3g0d/cve-2024-4956

Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…

exploitationhash-analysispassword-cracking+3
91 year ago
CMS-Made-Simple-2.2.9-CVE-2019-9053 preview

CMS-Made-Simple-2.2.9-CVE-2019-9053

GitHubboon-rekcah/cms-made-simple-2.2.9-cve-2019-9053

Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…

exploitationpassword-crackingpenetration-testing+2
1 year ago
CVE-2026-90817 preview

CVE-2026-90817

GitHubyulisec/cve-2026-90817

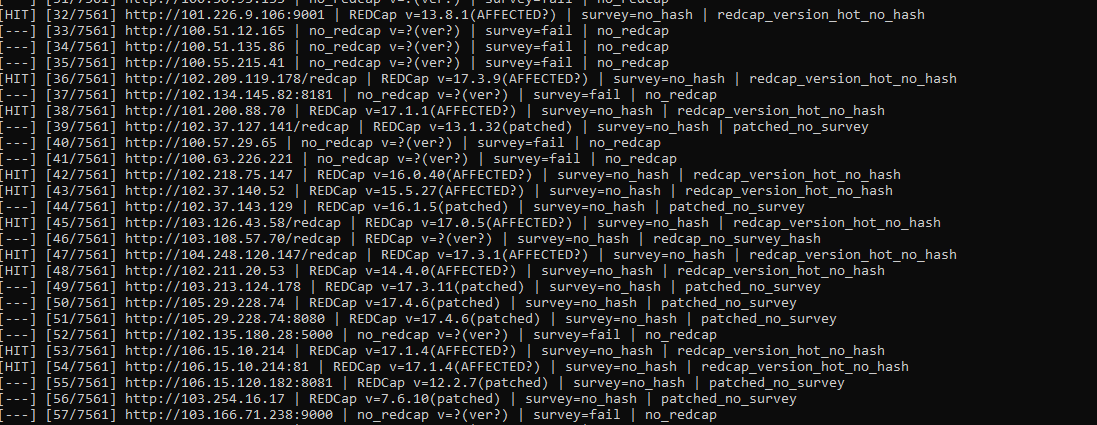
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…

exploitationinformation-gatheringpenetration-testing+6
114 days ago
CVE-2026-63030 preview

CVE-2026-63030

GitHub4minx/cve-2026-63030

CVE-2026-63030 (wp2shell) POC.

exploitationpassword-attackspenetration-testing+2
92 months ago
CVE-2019-9053-Exploit-Python-3 preview

CVE-2019-9053-Exploit-Python-3

GitHubmahamedm/cve-2019-9053-exploit-python-3

The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.

exploitationpassword-crackingpenetration-testing+2
81 year ago
CVE-2026-90817 preview

CVE-2026-90817

GitHubfarih123/cve-2026-90817

Python checker and configurable exploit hook for CVE-2026-90817, fingerprinting REDCap instances, validating survey hashes, and probing __passthru…

exploitationinformation-gatheringpenetration-testing+5
12 days ago
CVE-2019-14314 preview

CVE-2019-14314

GitHubimthoe/cve-2019-14314

Python exploit for CVE-2019-14314: authenticated SQL injection in NextGEN Gallery 3.2.10 WordPress plugin, extracting password hashes from the…

exploitationpassword-attackspenetration-testing+2
86 years ago
Exploit-CVE-2023-6063-PoC-Vuln preview

Exploit-CVE-2023-6063-PoC-Vuln

GitHubzhairiazzeddine/exploit-cve-2023-6063-poc-vuln

Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…

exploitationpassword-crackingpenetration-testing+4
28 days ago
CVE-2019-9053 preview

CVE-2019-9053

GitHub4nner/cve-2019-9053

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…

exploitationpassword-crackingpenetration-testing+3
113 years ago
CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit preview

CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

GitHubelizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

exploitationpassword-crackingpenetration-testing+2
55 months ago
Exploit_CVE-2021-24762 preview

Exploit_CVE-2021-24762

GitHubc4cnm/exploit_cve-2021-24762

This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.

exploitationpassword-crackingpenetration-testing+2
111 months ago
CVE-2019-9053 preview

CVE-2019-9053

GitHubkalidas-7/cve-2019-9053

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…

exploitationinformation-gatheringpassword-cracking+3
1 year ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubdavcwikla/cve-2019-9053-exploit

Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…

exploitationpassword-crackingpenetration-testing+2
2 years ago
Previous1234Next