
CVE-2024-23692-RCE
Exploit for CVE-2024-23692, a remote code execution vulnerability in Rejetto HTTP File Server (HFS) 2.3 and below. Includes mass scanning with zmap…

Exploit for CVE-2024-23692, a remote code execution vulnerability in Rejetto HTTP File Server (HFS) 2.3 and below. Includes mass scanning with zmap…

XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.

RFI to RCE Nagios/NagiosXI exploitation

Go-based exploit for Icinga Web 2 (CVE-2022-24715) enabling remote code execution against vulnerable instances. Port of original Python PoC.

Go-based exploit for CVE-2023-38646 in Metabase, enabling remote code execution and reverse shell connection to an attacker-controlled host.

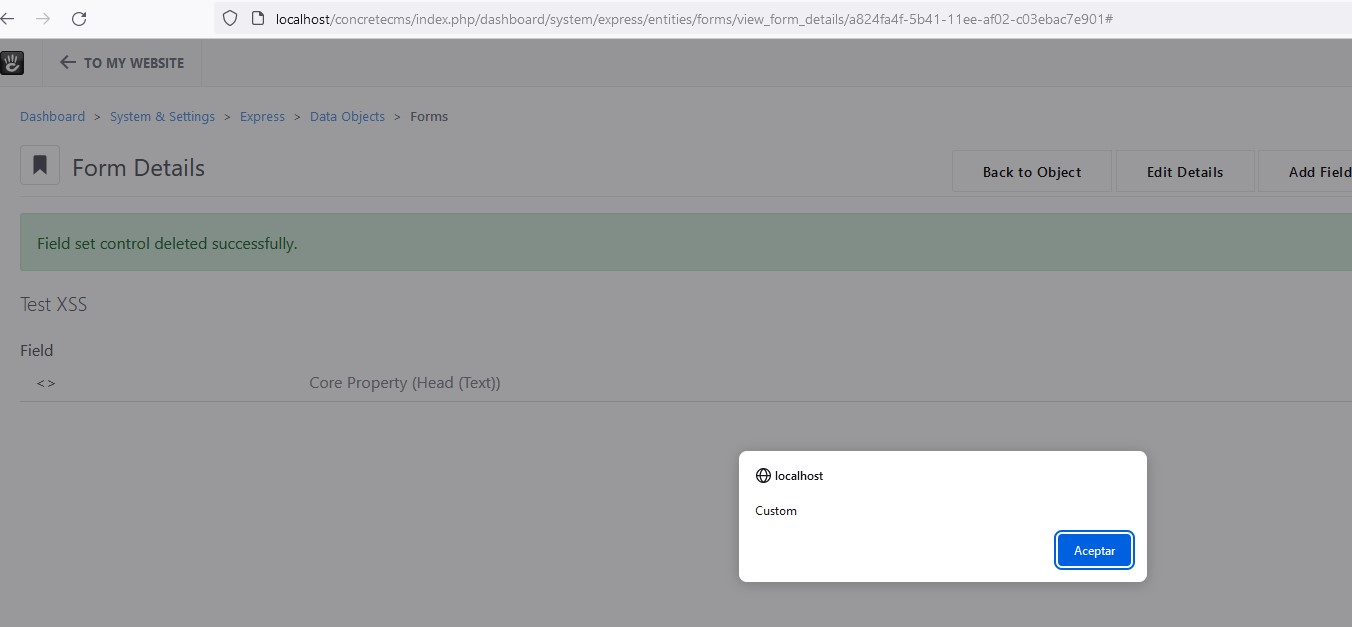
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Form of the…

CVE-2017-17215 HuaWei Router RCE (NOT TESTED)

CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…

Persistent XSS on Comtrend AR-5387un router

Proof-of-concept for authenticated stored cross-site scripting (XSS) vulnerability in Multilaser RE 170 router firmware 2.2.6733, with reproduction…

Exploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.

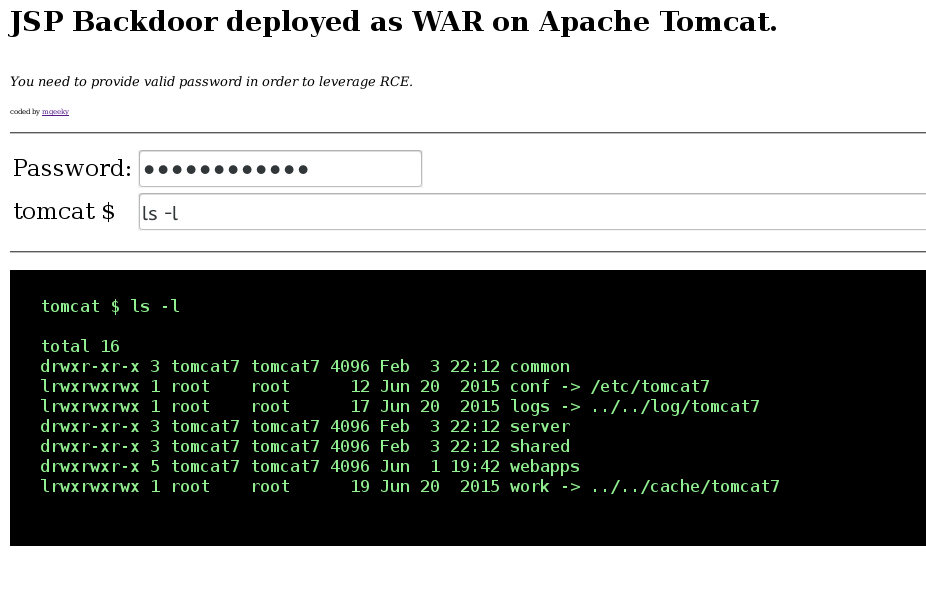
Apache Tomcat auto WAR deployment & pwning penetration testing tool.

Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…

React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…

CVE-2026-1689 Unauthenticated RCE for the Tenda HG10

MOVEit Transfer 2020 web application Stored Cross-Site Scripting (XSS)

https://hackerone.com/reports/865652

A rapid HTTP downgrade smuggling scanner written in Go.