CVE-2014-6271
 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
command-and-controlexploitationpayload-generation+3
mritunjay-k/cve-2014-6271Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 0nyx-my7h/cve-2025-43921
Proof-of-concept exploit and advisory for CVE-2025-43921, an authentication bypass in GNU Mailman 2.1.39 that allows unauthenticated creation of…
 0nyx-my7h/cve-2025-43920
PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…
 kaleth4/cve-2026-32746
Proof-of-concept exploit for CVE-2026-32746, a critical remote code execution vulnerability in GNU Inetutils telnetd via LINEMODE SLC buffer…
 im-hanzou/jbwper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2022-4061 - JobBoardWP < 1.2.2 - Unauthenticated Arbitrary File Upload
 knightc0de/shellshock_vuln_exploit
Python exploit for CVE-2014-6271 (Shellshock) targeting vulnerable CGI scripts with reverse shell handler, supporting HTTP/HTTPS, custom paths, and…
 jayglxr/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…
 ilokaas/cve-2026-24061-payload
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 midox008/cve-2026-24061
GNU Inetutils telnetd Remote Authentication Bypass
 mr-zapi/cve-2026-24061
Nuclei template for detecting CVE-2026-24061, a critical telnet argument injection in GNU inetutils telnetd allowing unauthenticated root access.
 typeconfused/cve-2026-24061
GNU telnetd service from GNU InetUtils authentication-bypass
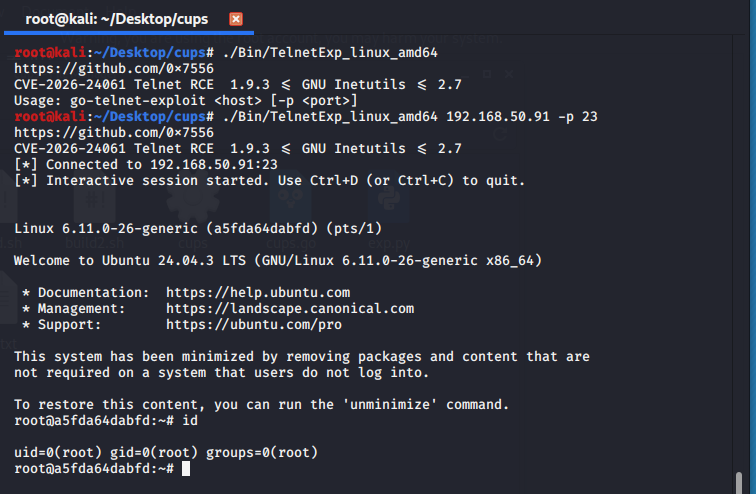 0x7556/cve-2026-24061
Cross-platform remote code execution exploit for GNU Inetutils telnet (versions 1.9.3 to 2.7), targeting CVE-2026-24061 with a simple command-line…
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 im-hanzou/upger
Automatic Mass Tool for checking vulnerability in CVE-2022-4060 - WordPress Plugin : User Post Gallery <= 2.19 - Unauthenticated RCE
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
 harygovind/cve-2026-24061
CVE-2026-24061-PoC