
GraphQLGrapper
 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
api-security-testinginformation-gatheringpenetration-testing+3
21
m19o/graphqlgrapperBurp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
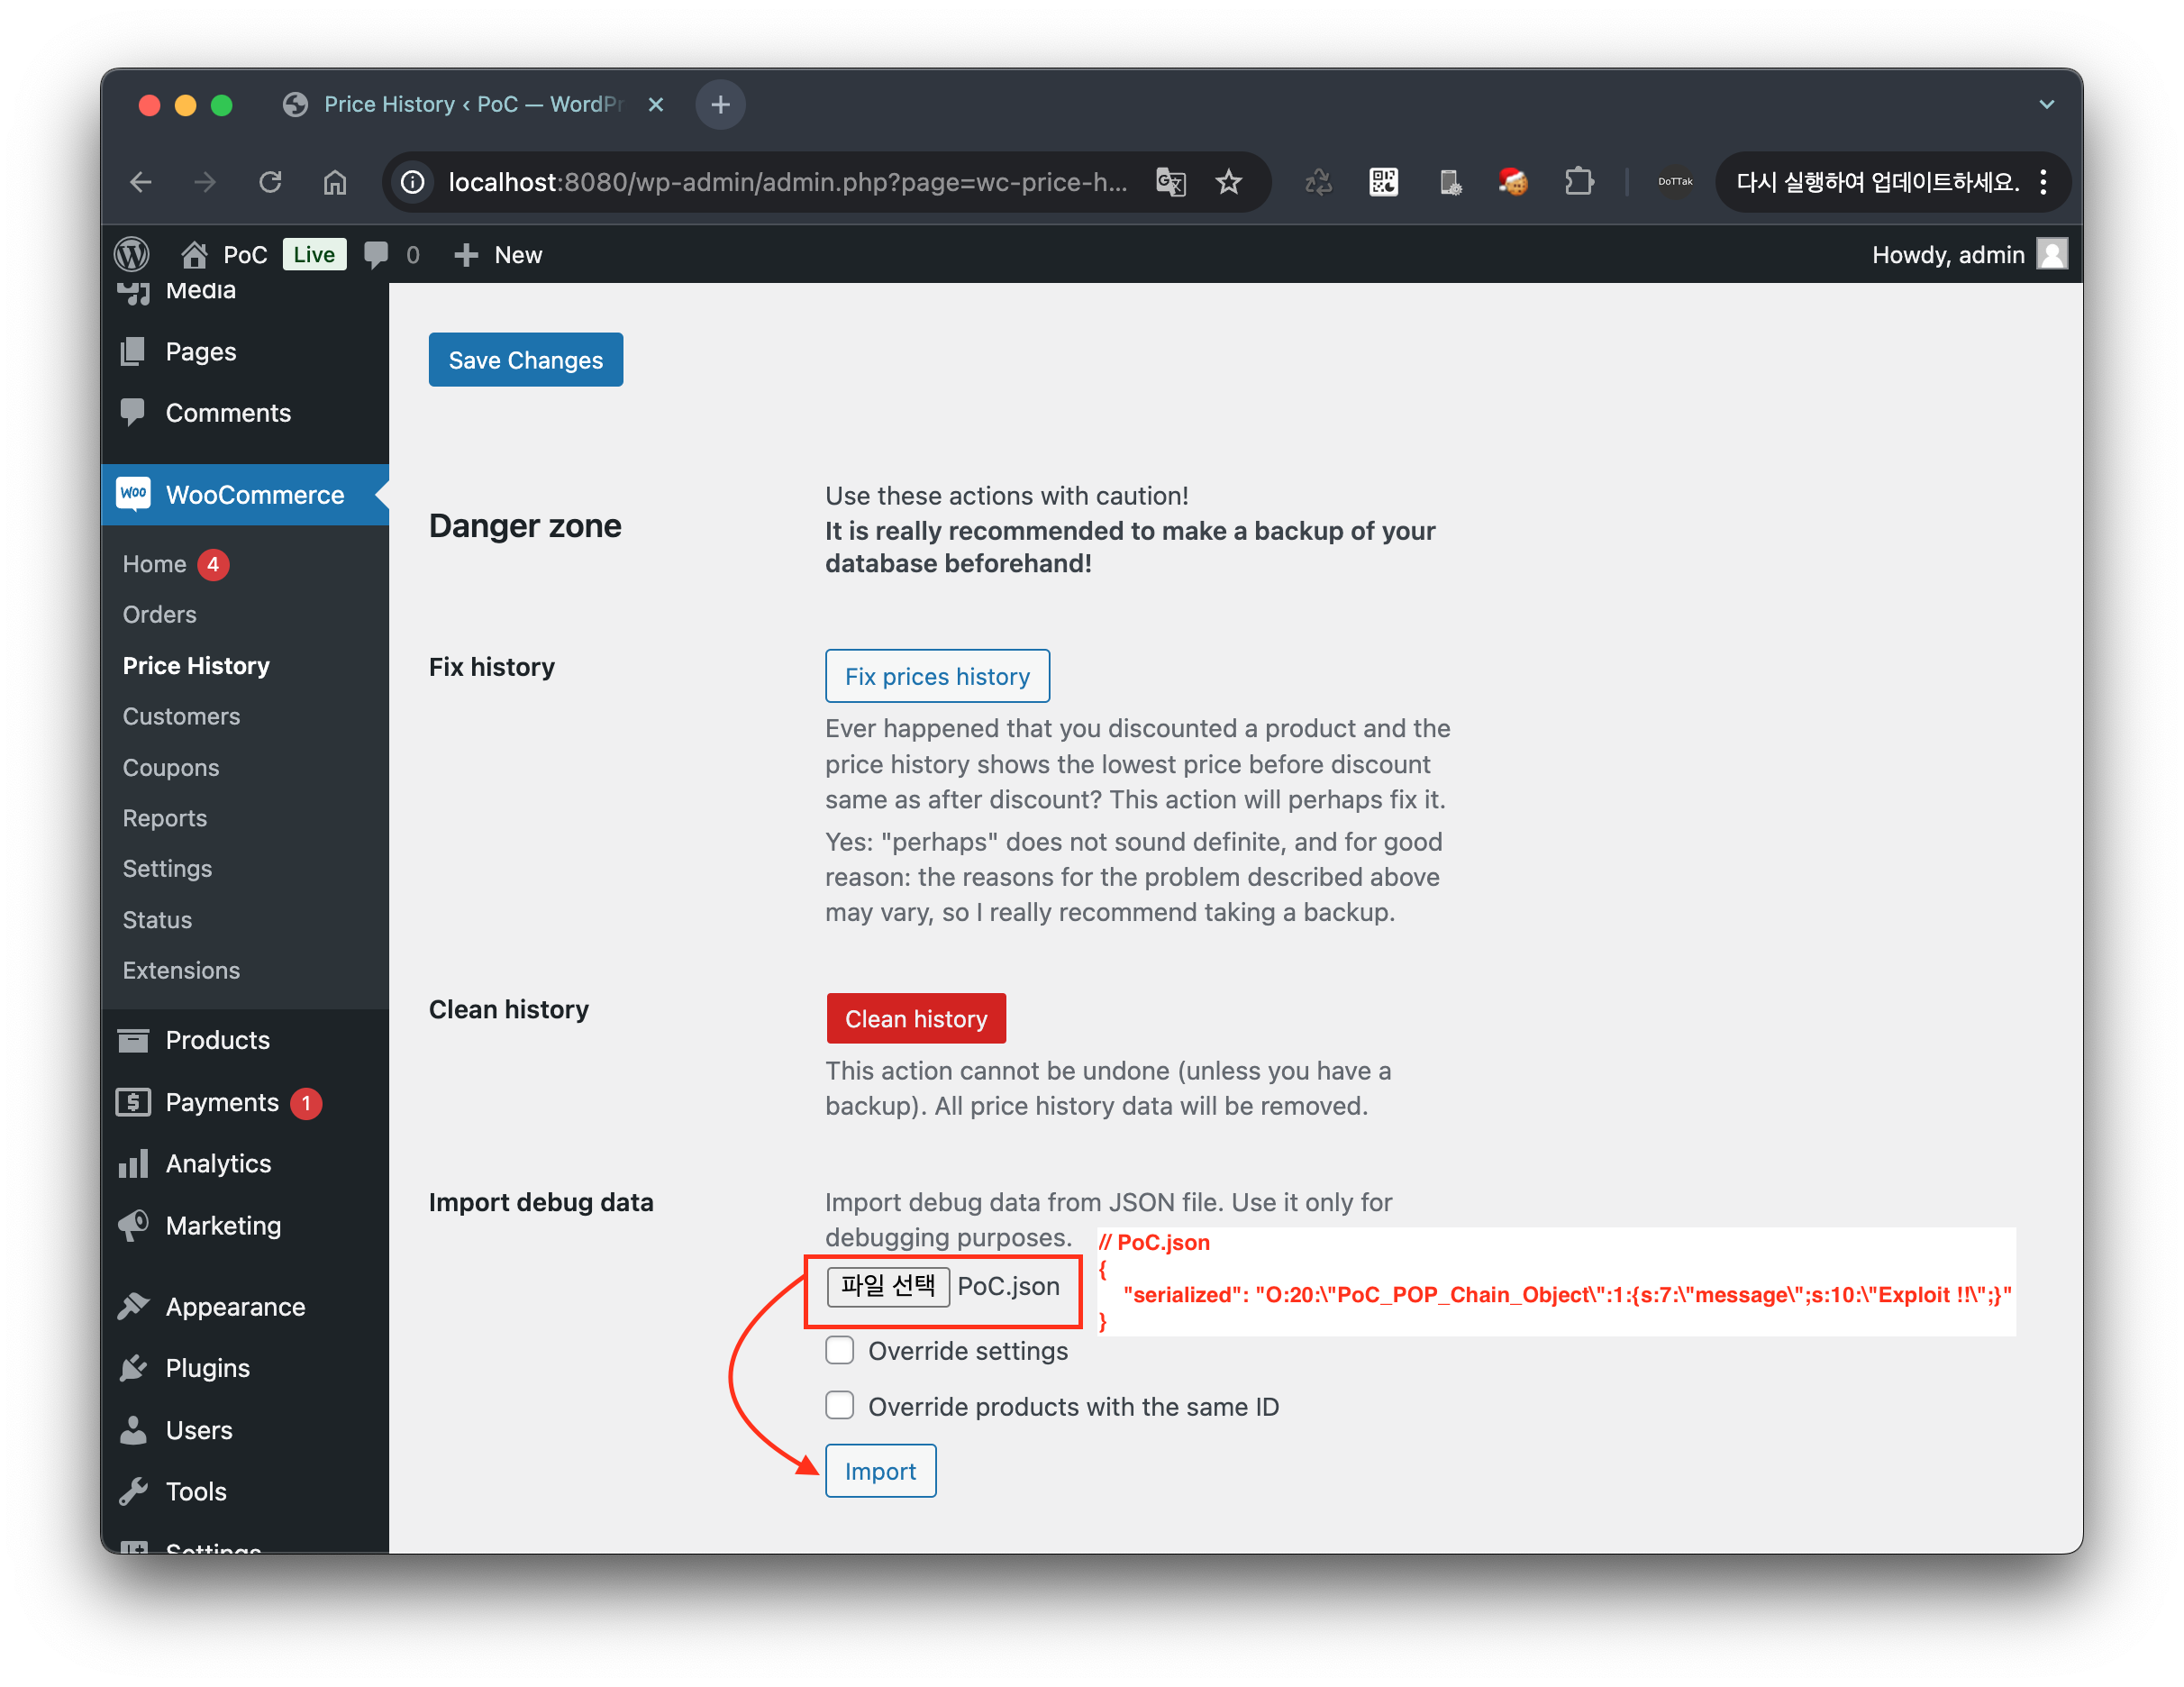 dottak/cve-2025-22510
PoC of CVE-2025-22510
 0xn4no/cve-2026-30048
Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
 izxci/cve-2026-7459
Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…
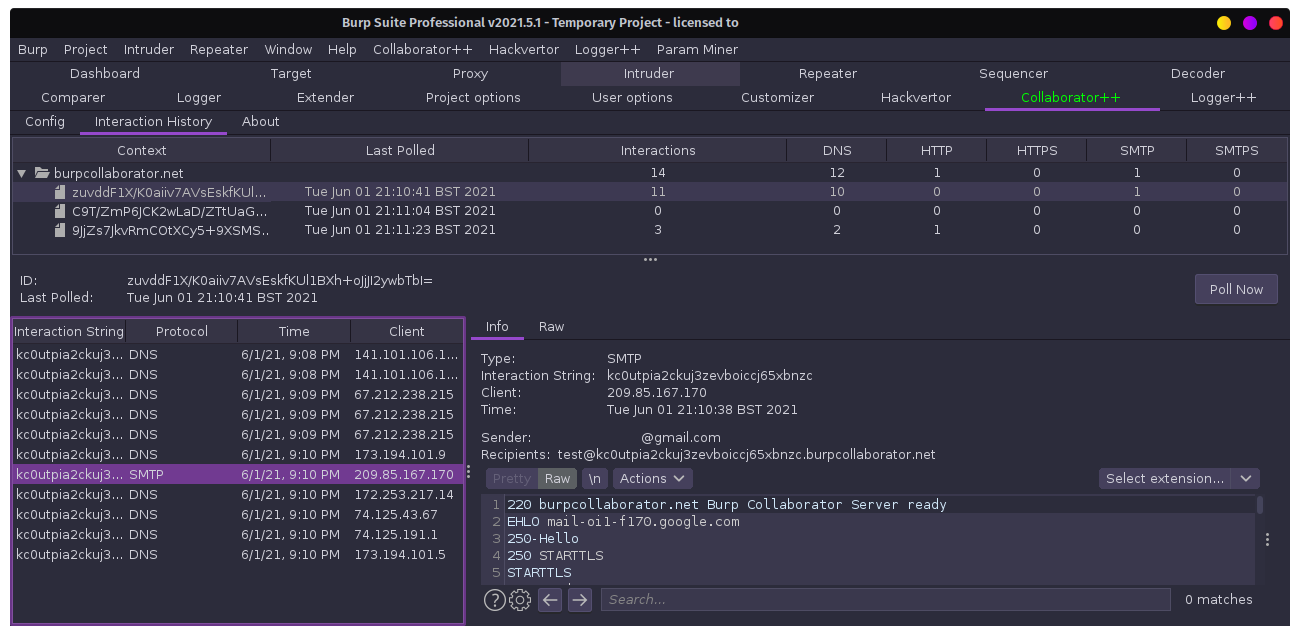 nccgroup/collaboratorplusplus
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…
 5kr1pt/glpi-logbleed
PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter
 mrr0b0t19/cve-2025-55182-shellinteractive
Interactive RCE exploit for CVE-2025-55182 targeting Next.js/React Server Components deserialization vulnerability. Features automatic detection,…
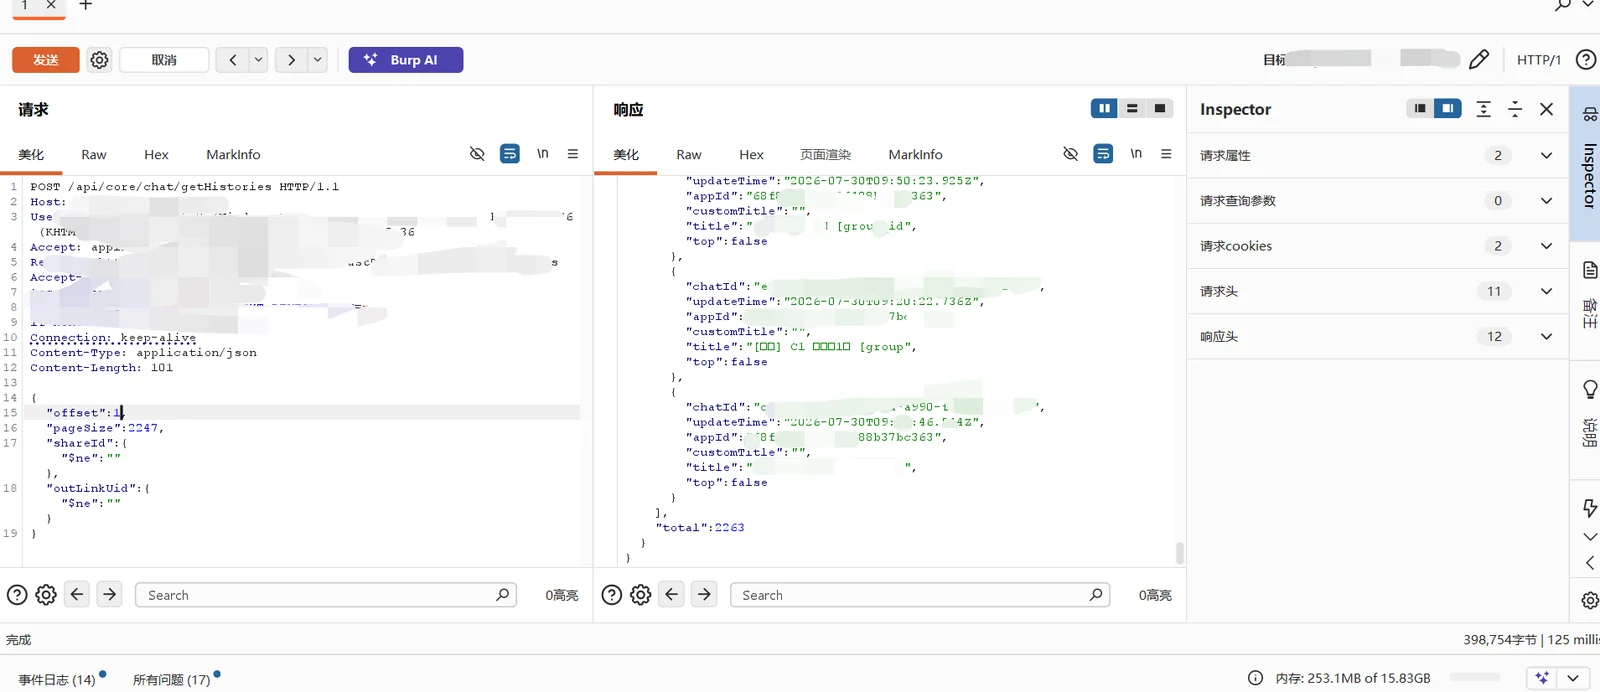 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 d0n601/cve-2025-12585
MxChat – AI Chatbot for WordPress <= 2.5.1 - Unauthenticated Information Exposure
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
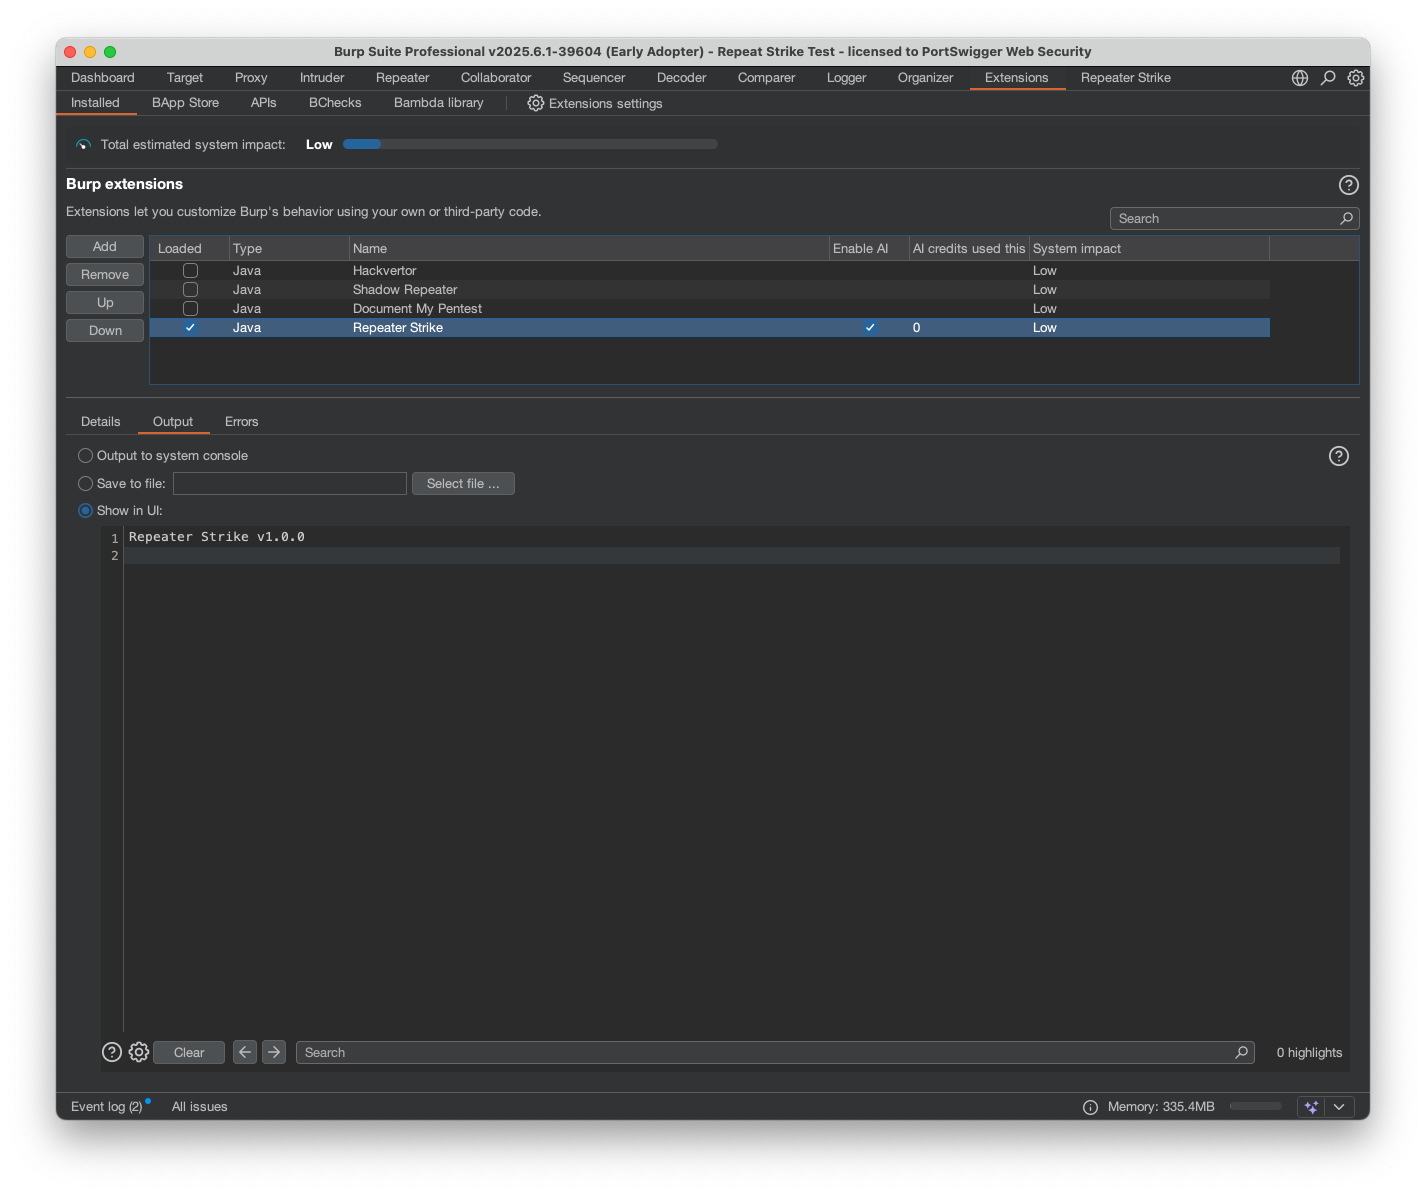 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
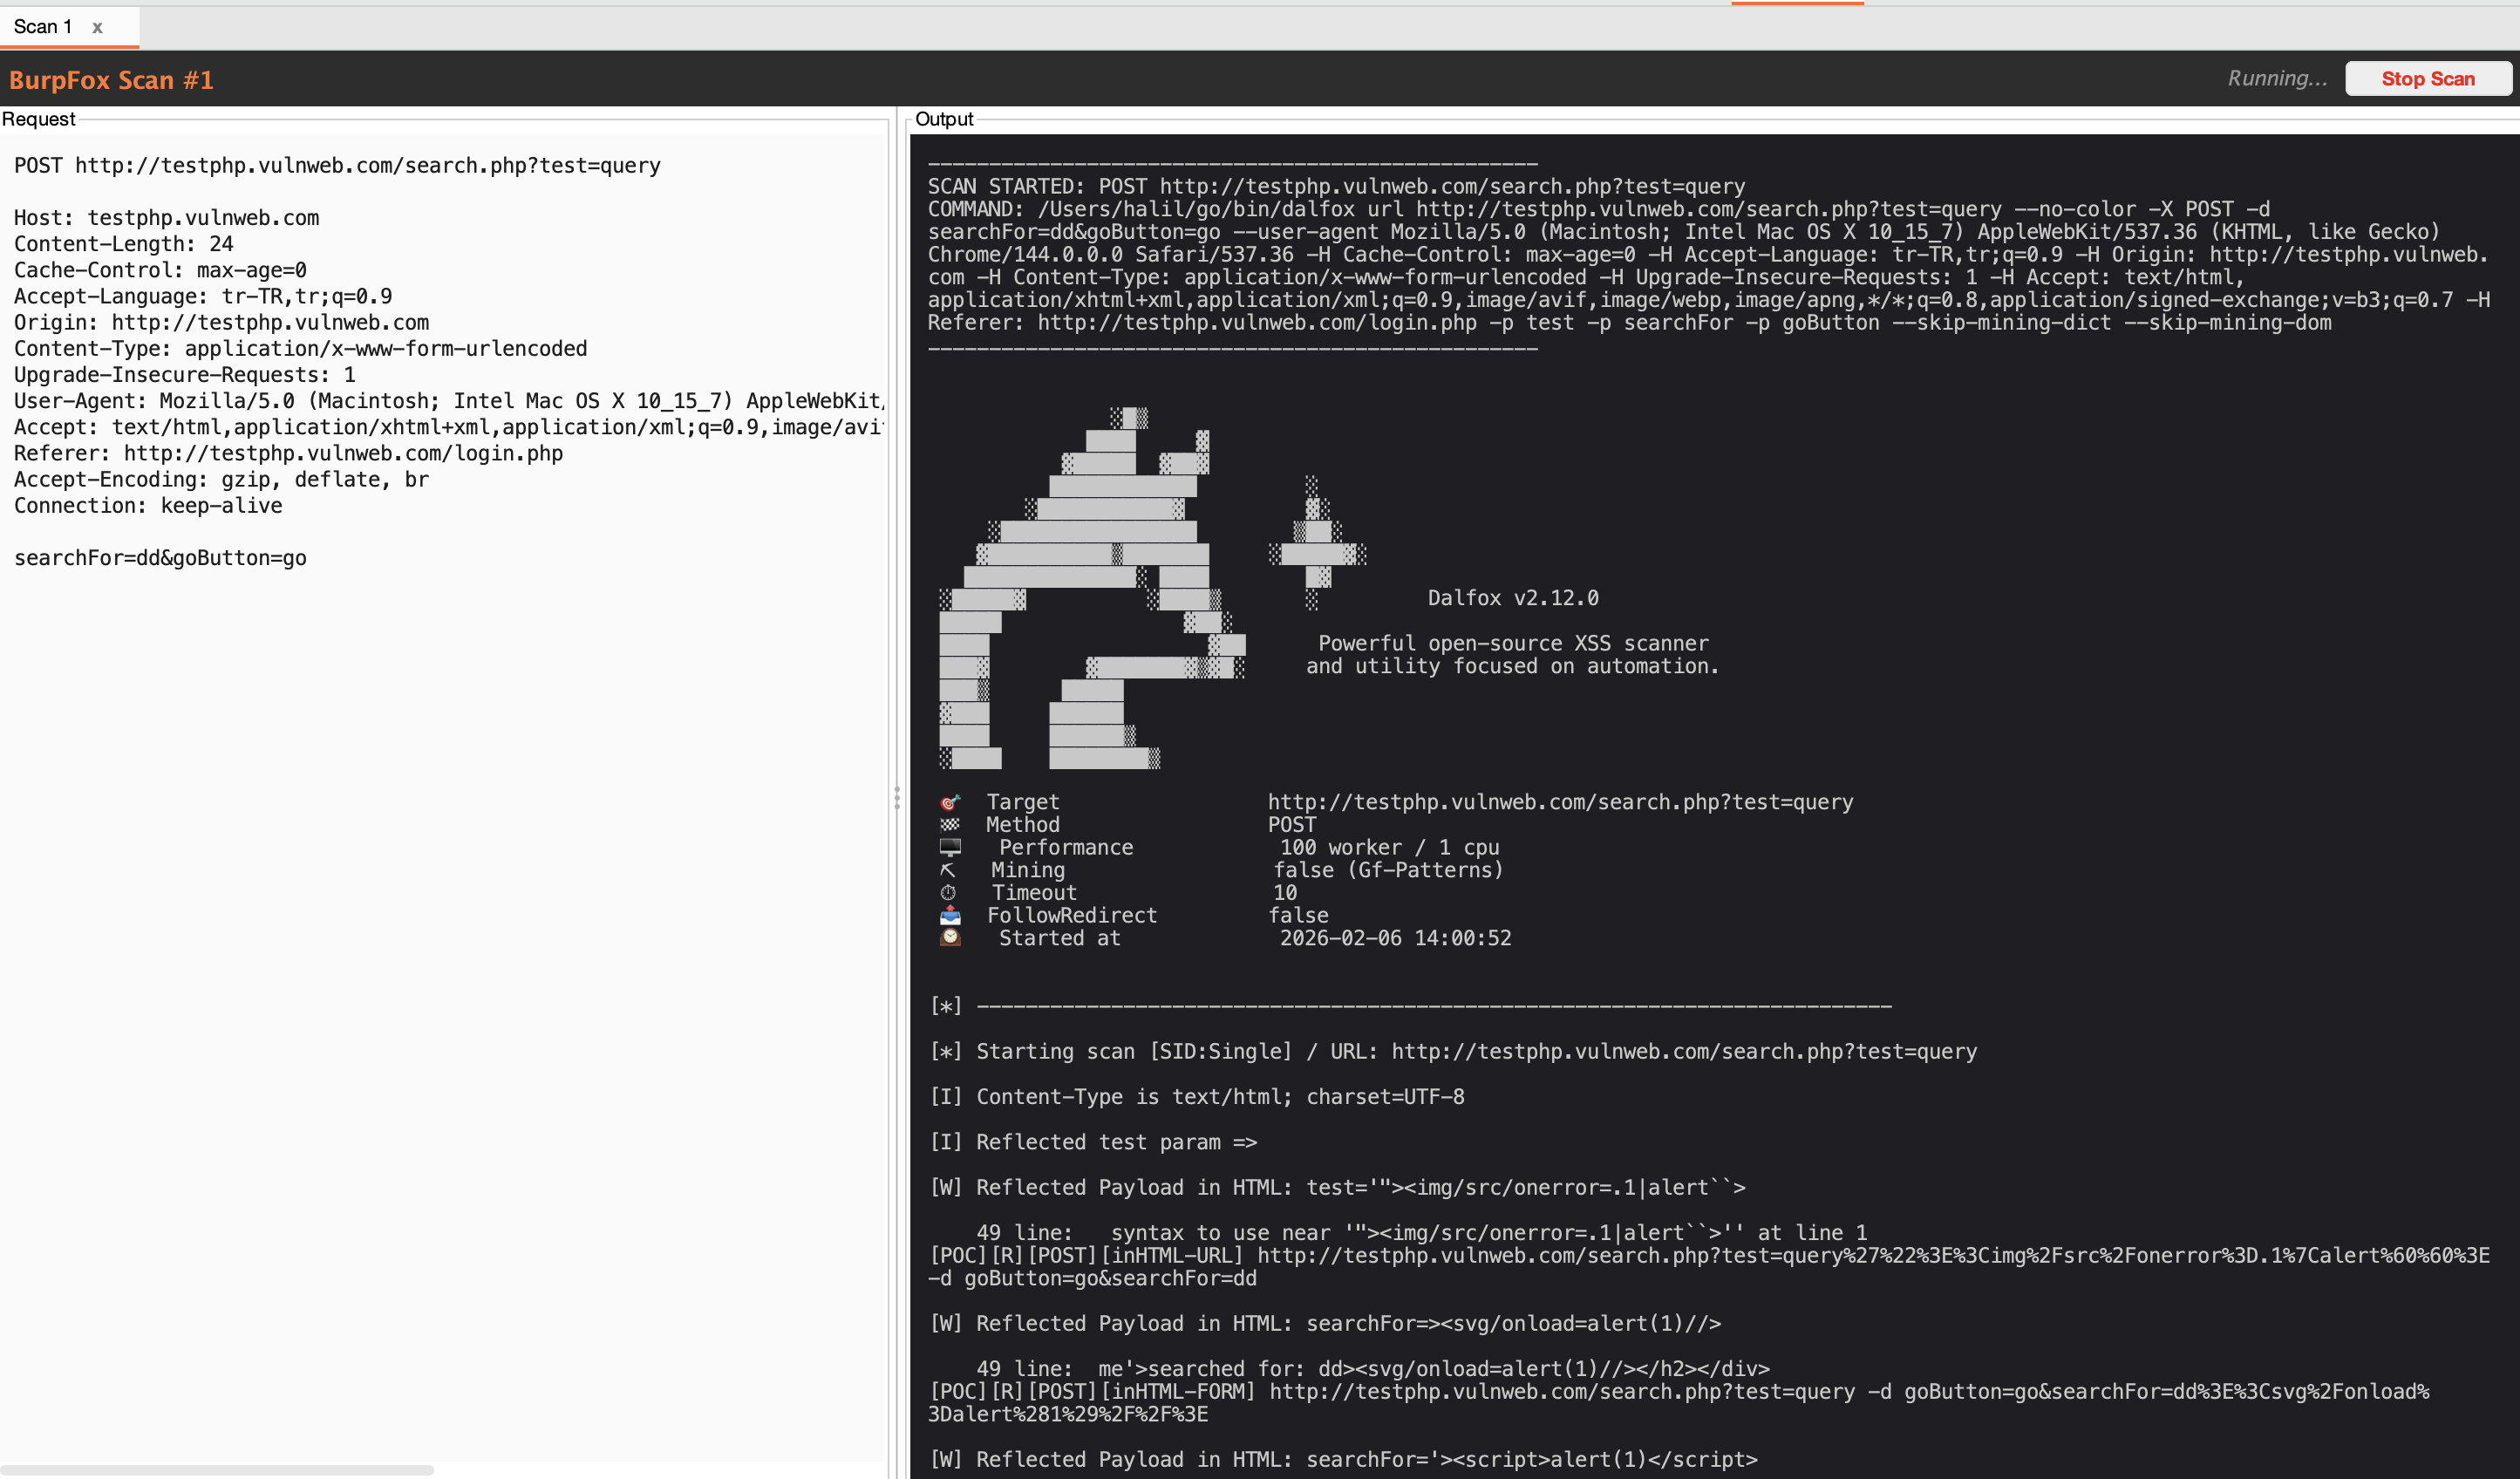 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.