CVE-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…

Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…

This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…

Info and exploit for CVE-2023-29930: blind file read/write in Genesys TFTP provisioning server configuration

Vulnerable configuration Apache HTTP Server version 2.4.49

Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…

Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset

PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…

Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…

Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…

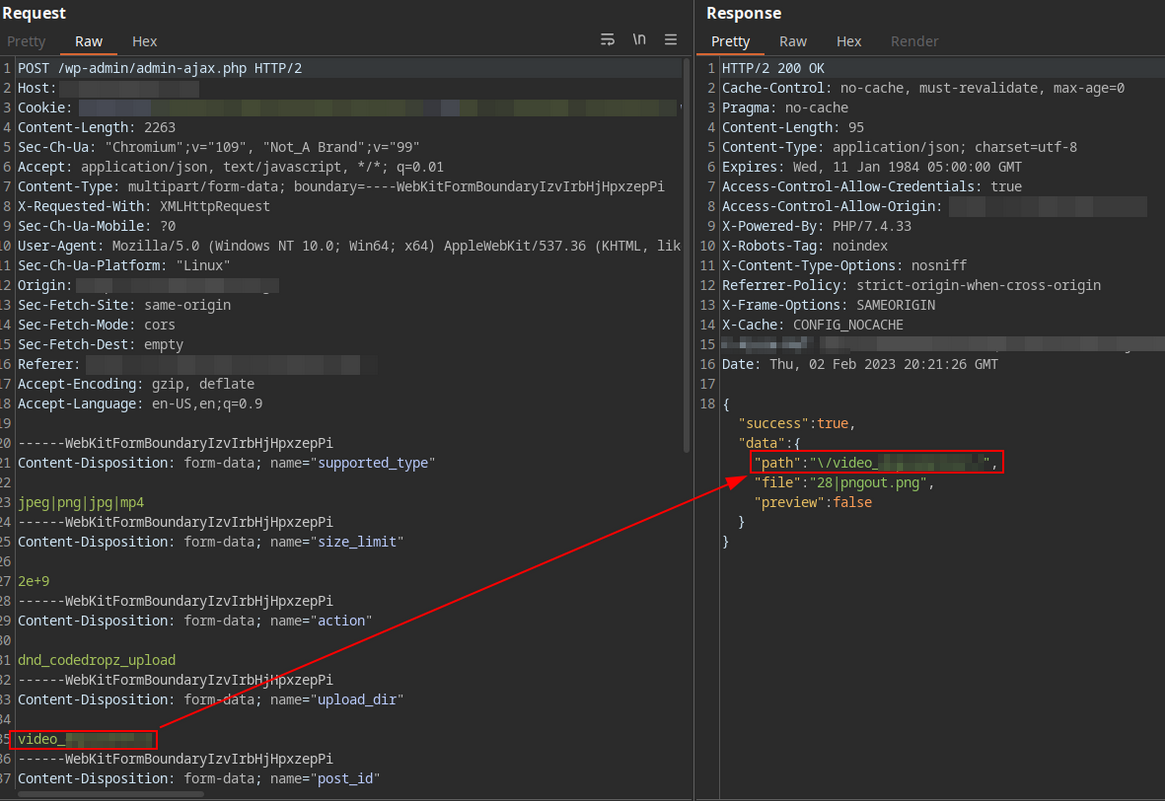
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths

A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation

HAProxy-CVE-2023-45539-PoC

A flaw was found in a change made to path normalization in Apache HTTP Server 2.4.49. An attacker could use a path traversal attack to map URLs to…

Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…