
CVE-2021-21239
 illera88/cve-2021-21239
Exploit for CVE-2021-21239: SAML signature validation bypass in pysaml2/Redash. Forges SAML responses with embedded public keys to impersonate users…
authenticationeducationexploitation+3
illera88/cve-2021-21239Exploit for CVE-2021-21239: SAML signature validation bypass in pysaml2/Redash. Forges SAML responses with embedded public keys to impersonate users…
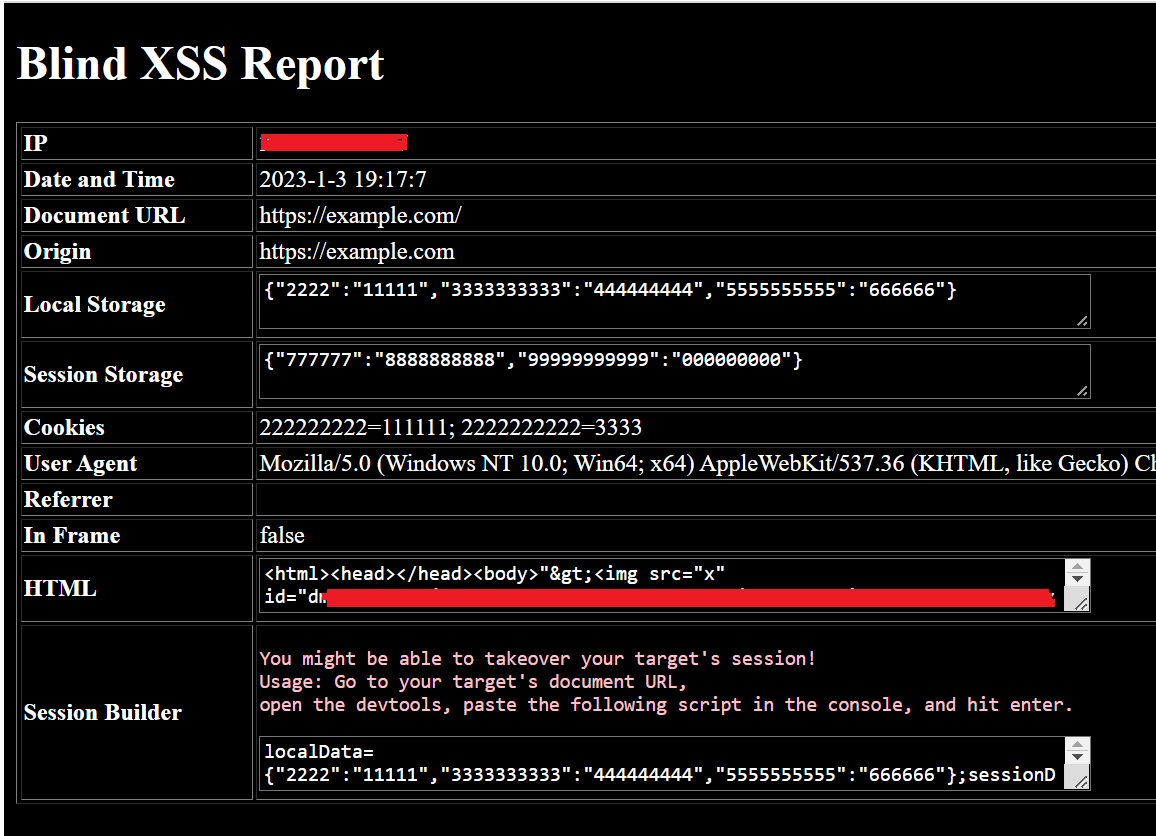 seifelsallamy/xssfire
A standalone Blind XSS Script.
 raphy76/wp2shell-poc-fulljs
full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)
 hasanuyarrr/cve-2026-18782-trex-mes-uygulamalarinda-sql-zafiyeti
Advisory and technical write-up for CVE-2026-18782, a critical SQL injection in TREX MES web API endpoints enabling auth bypass, data theft, and RCE…
 murataydemir/cve-2017-9822
[CVE-2017-9822] DotNetNuke Cookie Deserialization Remote Code Execution (RCE)
 v0lp3/cve-2022-39073
Proof of concept for the command injection vulnerability affecting the ZTE MF286R router, including an RCE exploit.
 wiseep/cve-2025-48827
Vbullettin RCE - CVE-2025-48827
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
 mbadanoiu/cve-2025-26865
CVE-2025-26865: FreeMarker Server-Side Template Injection via the "ecommerce" plugin in Apache OfBiz
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
 eriknl/cve-2020-16152
Proof-of-concept exploit for CVE-2020-16152: LFI-to-RCE in Aerohive/Extreme Networks HiveOS via PHP string truncation and log poisoning, enabling…
 horizon3ai/ivanti-epm-coercion-vulnerabilities
Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…