
CVE-2025-11174
 snailsploit/cve-2025-11174
Document Library Lite <= 1.1.6 - Missing Authorization to Sensitive Information Exposure | CVE-2025-11174
exploitationinformation-gatheringpenetration-testing+3
snailsploit/cve-2025-11174Document Library Lite <= 1.1.6 - Missing Authorization to Sensitive Information Exposure | CVE-2025-11174
 absholi7ly/microsoft-edge-information-disclosure
CVE-2024-30056 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability
 g4sul1n/cisco-ios-xe-cve-2023-20198
Exploit PoC for CVE-2023-20198
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV
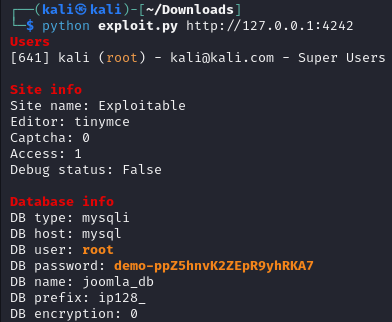 fernando-olv/joomla-cve-2023-23752
This Python implementation serves an educational purpose by demonstrating the exploitation of CVE-2023-23752. The code provides insight into the…
 alissonfaoli/cve-2023-23752
Joomla Unauthenticated Information Disclosure (CVE-2023-23752) exploit
 redrays-io/cve-2022-41272
Improper access control in SAP NetWeaver Process Integration
 r3dston3/cve-2023-23752
Proof-of-concept exploit for CVE-2023-23752 (Joomla 4.0.0-4.2.8) that extracts usernames and passwords via an information disclosure vulnerability.
 redrays-io/cve-2022-39802
[CVE-2022-39802] File path traversal vulnerability in SAP Manufacturing Execution
 halencarjunior/f5scan
CVE-2020-5902 scanner for F5 BIG-IP with Shodan host discovery, LFI file reading, and remote command execution capabilities.
 halencarjunior/cve-2023-36845
Scanner for CVE-2023-36845 with Shodan and Censys integration for automated host discovery and exploitation of Juniper devices.
 wellingtonespindula/ssi-cve-2022-21661
Study and exploit the vulnerability CVE-2022-21661 that allows SQL Injections through plugins POST requests to WordPress versions below 5.8.3.
 xiaoxiaoranxxx/cve-2025-70829
An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…
 adhikara13/cve-2022-44268-magileak
Tools for working with ImageMagick to handle arbitrary file read vulnerabilities. Generate, read, and apply profile information to PNG files using a…
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 carlos-mesquita/tpaslog4shellpoc
Proof of Concept for the Log4Shell vulnerability (CVE-2021-44228), developed as part of the coursework for the curricular unit TPAS in the Master's…
 saku0512/cve-2026-72744-poc
Proof-of-concept exploit for CVE-2026-72744, an information disclosure vulnerability in Nuxt dev server's Chrome DevTools workspace endpoint.…
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…