CVE-2026-73633
 cuteecat/cve-2026-73633
Proof-of-concept exploit for Apache Struts S2-072 (CVE-2026-73633), demonstrating CPU and memory exhaustion by sending crafted JSON requests to the…
exploitationpenetration-testingvulnerability-analysis+2
cuteecat/cve-2026-73633Proof-of-concept exploit for Apache Struts S2-072 (CVE-2026-73633), demonstrating CPU and memory exhaustion by sending crafted JSON requests to the…
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 cybertechajju/cve-2026-23869-exploit
Automated exploit tool for CVE-2026-23869, a remote DoS in React Server Components. Includes PoC, Nuclei template, and scanning scripts for detection…
 samb102/poc-cve-2025-48988-cve-2025-48976
Proof-of-concept exploit for Tomcat CVEs causing CPU exhaustion via parallel multipart requests, with Docker setup and remediation guidance.
 anjai7/tryhack3m-bricks-heist
TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification
 yohannslm/cve-2026-23869
Proof-of-concept exploit for CVE-2026-23869, a denial-of-service vulnerability in React Server Components allowing unauthenticated CPU exhaustion via…
 a0zhar/bad_hoist-writeup
A Writeup for Sleirsgoevy's version of the Exploit Implementation of CVE-2018-4386 by Fire30 called Bad_Hoist
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 mumu2020629/-cve-2022-22954-scanner
Scans for and exploits CVE-2022-22954 in VMware Workspace ONE Access, Identity Manager, and Realize Automation appliances. Automates detection and…
 s0haib518-ksa/cve-2025-1913-poc
A PoC demonstrating CVE-2025-1913, showing how the plugin’s unsafe unserialize handling can lead to high-impact behavior in controlled environments.…
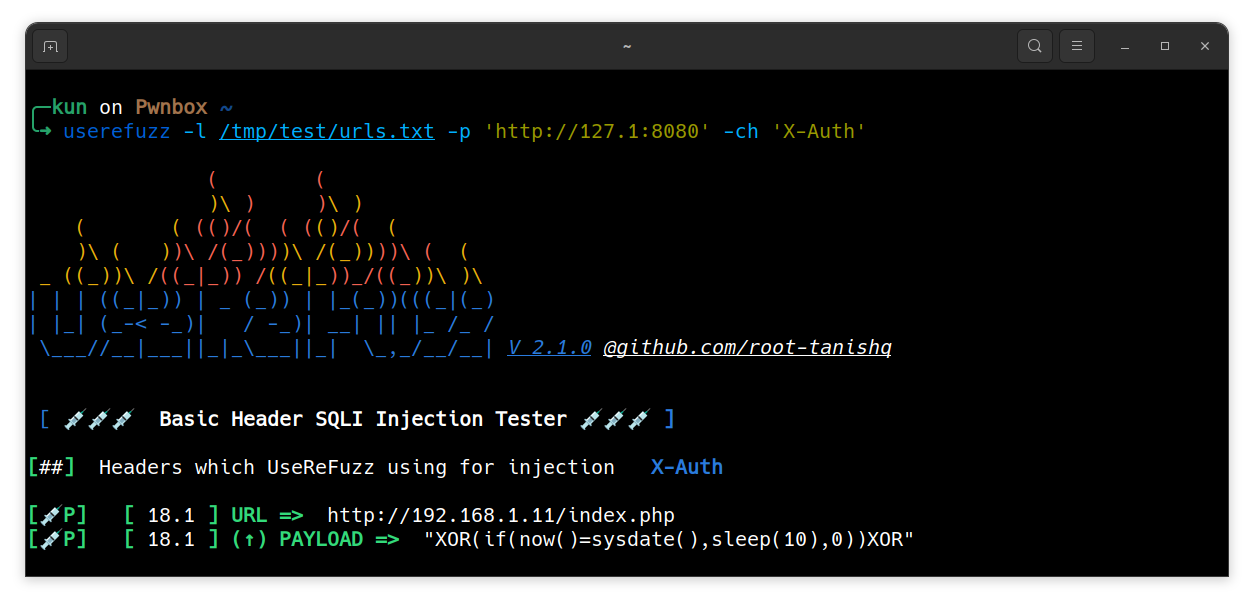 root-tanishq/userefuzz
User-Agent , X-Forwarded-For and Referer SQLI Fuzzer
 davidfortytwo/cve-2023-22518
Checker for CVE-2023-22518 vulnerability on Confluence
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
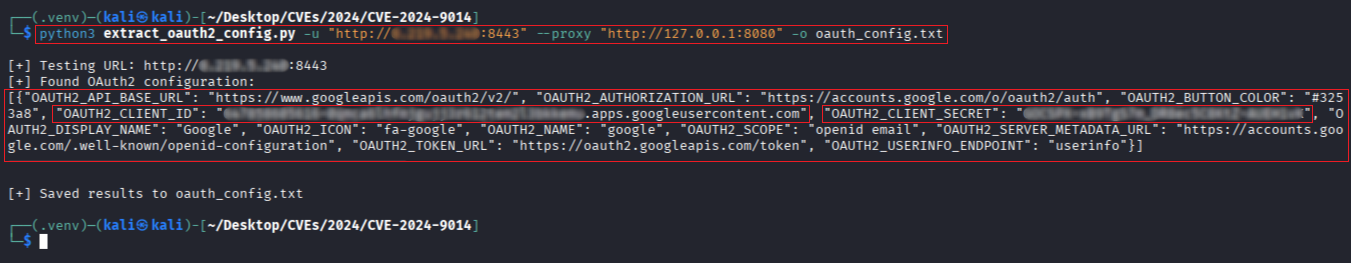 r0otk3r/cve-2024-9014
Scripts to detect and exploit CVE-2024-9014 OAuth2 authentication bypass in pgAdmin 4, including vulnerability checking and OAuth2 configuration…
 calebfin/exp-cve-2017-75
CVE-2017-7529- Check and EXPLOIT
 shivamdey/cve-2021-23017
Proof-of-concept exploit for CVE-2021-23017, a DNS resolver vulnerability in NGINX, demonstrating remote code execution via a crafted DNS response.