
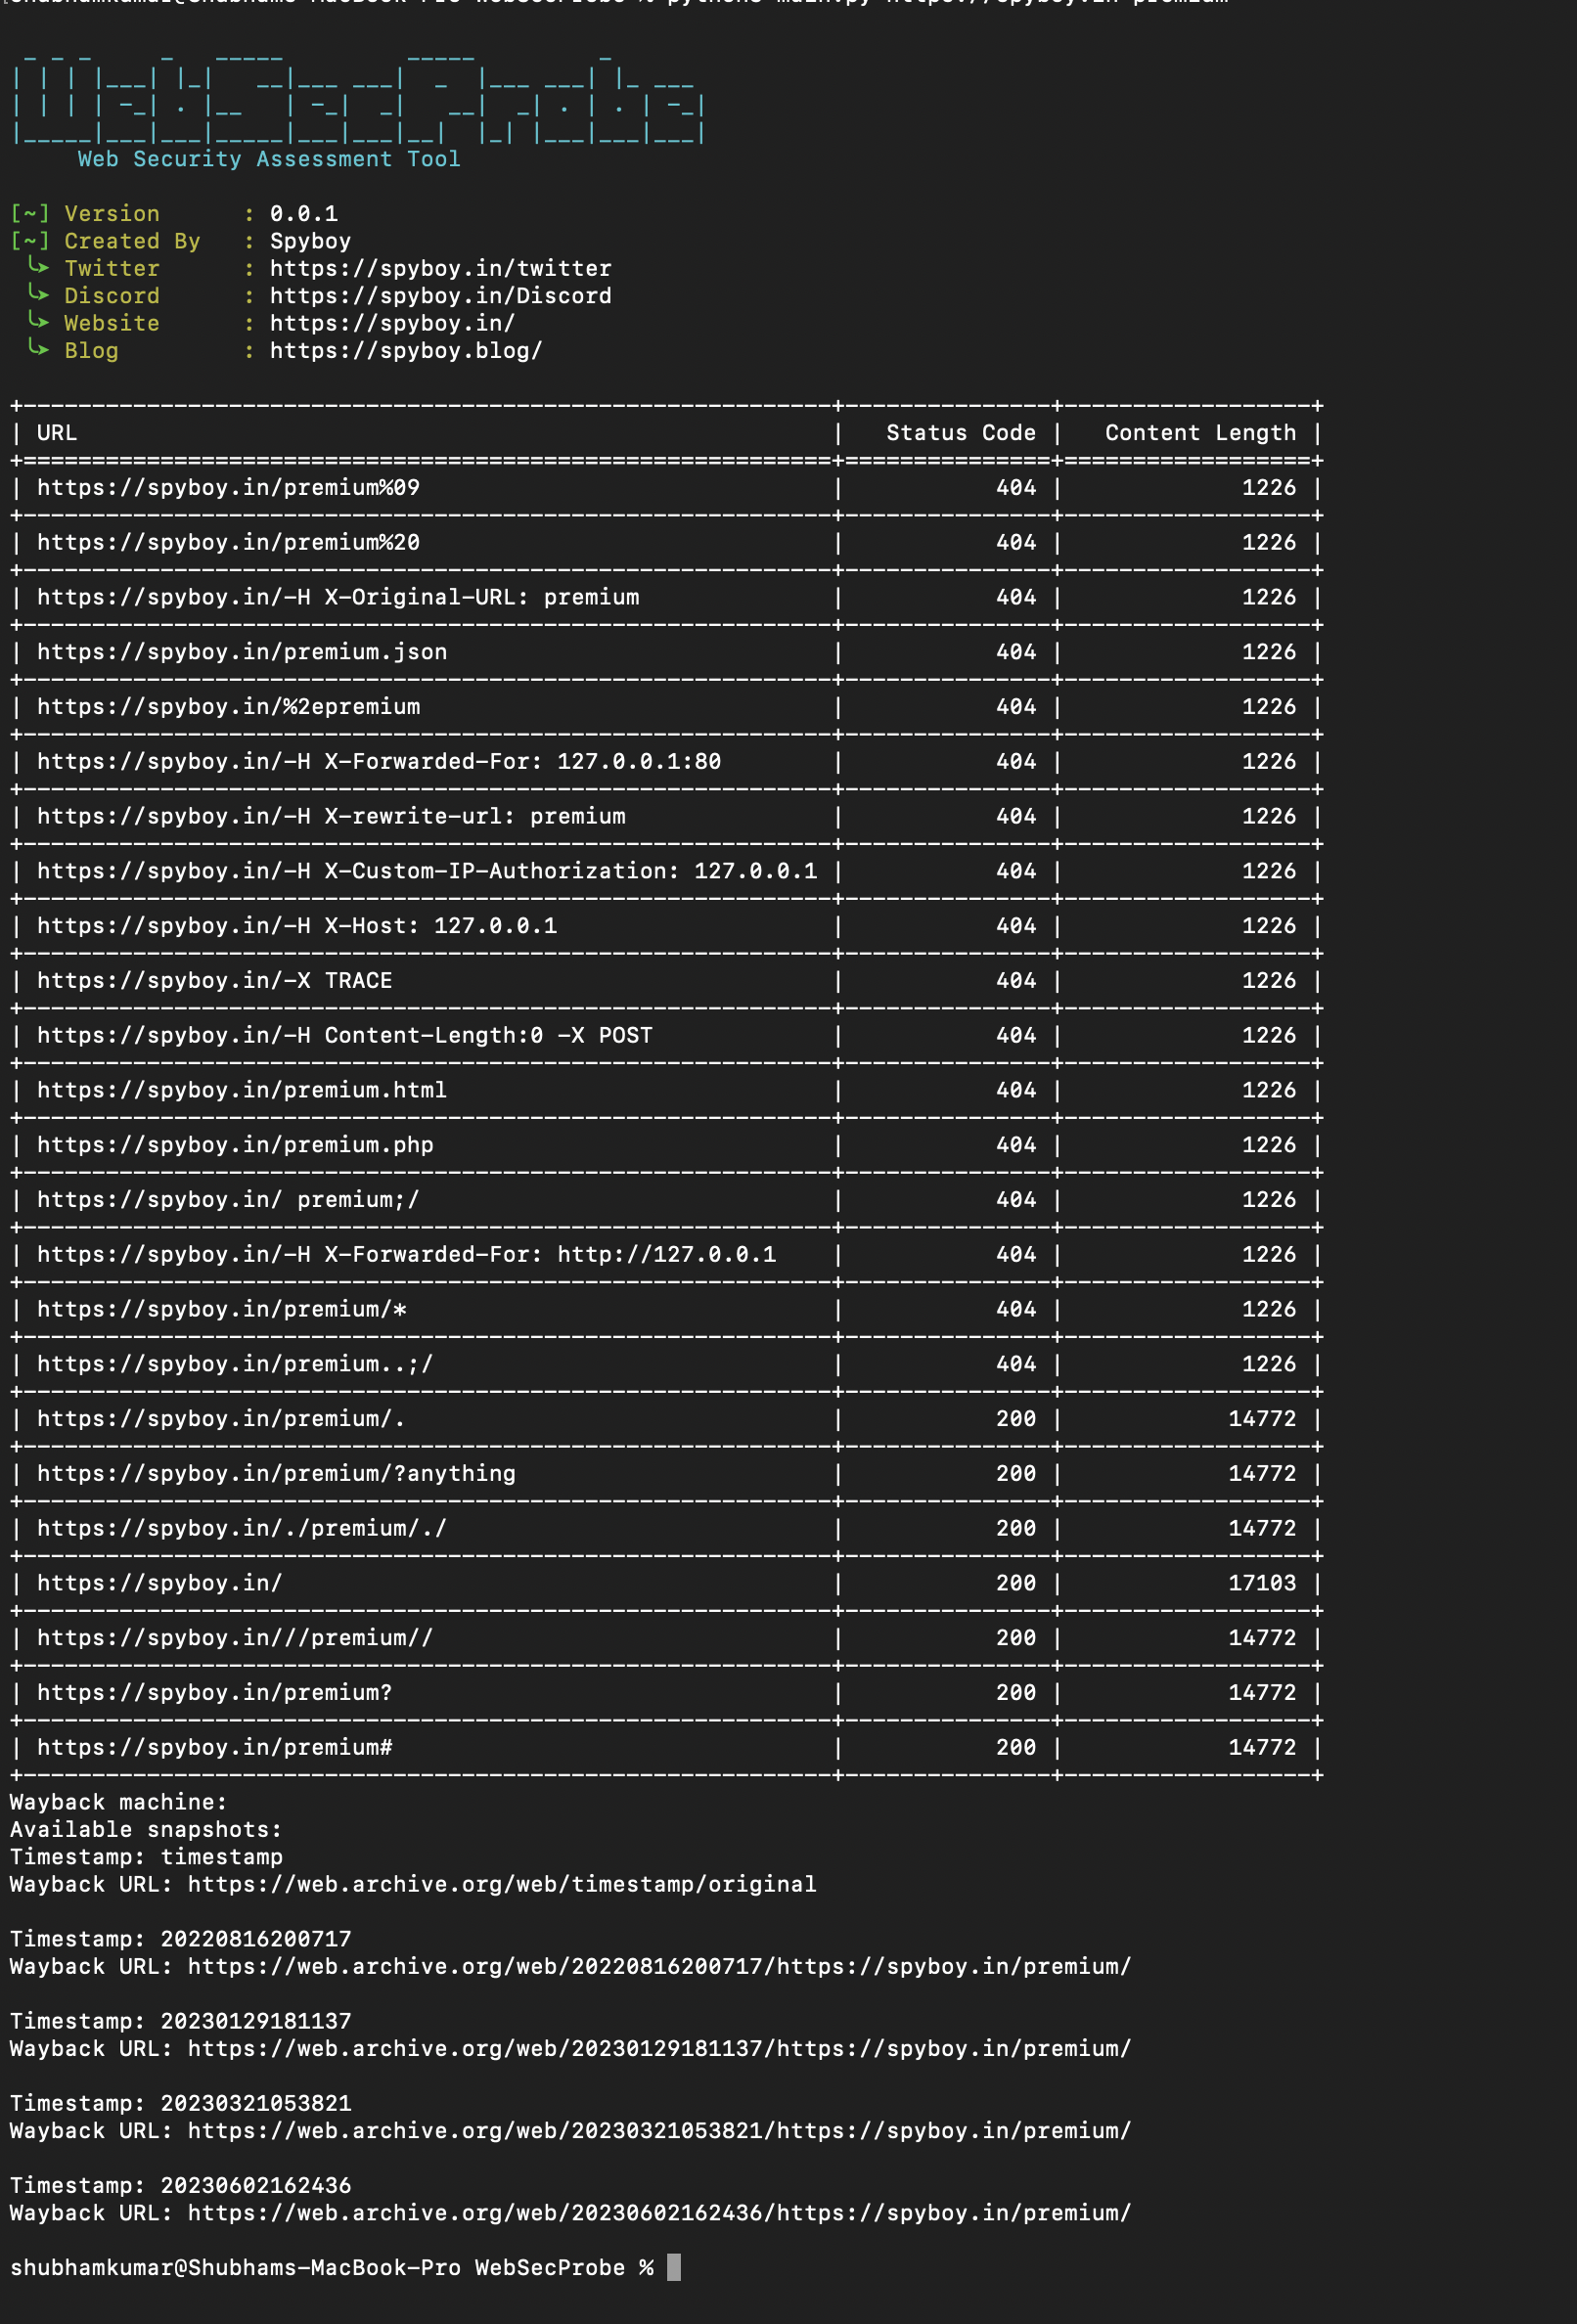
WebSecProbe
 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
misconfigurationpenetration-testingvulnerability-scanners+2
188
spyboy-productions/websecprobeSecurity testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 some-1hing/cve-2018-16763
Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.
 barcrange/cve-2025-0108-authentication-bypass-checker
Python script that tests PAN-OS devices for CVE-2025-0108 authentication bypass by sending crafted HTTP requests and analyzing responses.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 a-d-team/grafanaexp
A exploit tool for Grafana Unauthorized arbitrary file reading vulnerability (CVE-2021-43798), it can burst plugins / extract secret_key / decrypt…
 liamg/pax
:skull: :unlock: CLI tool for PKCS7 padding oracle attacks
 blacklanternsecurity/dp_cryptomg
Another tool for exploiting CVE-2017-9248, a cryptographic weakness in Telerik UI for ASP.NET AJAX dialog handler.
 sijido/cve-2022-22947
Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.
 madhusudhan-in/cve_2023_44487-rapid_reset
A comprehensive Python testing tool for CVE-2023-44487, the HTTP/2 Rapid Reset vulnerability. This enhanced version provides granular control over…
 jsongmax/fortinet-cve-2022-40684
Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…
 arrhenius975/cve-2024-38063-exploit-refactoring
Python-based exploit for CVE-2024-38063 targeting Windows IPv6 vulnerability. Automates network interface detection, packet crafting, and…
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 husam212/mitmer
Automated man-in-the-middle attack tool.
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 aytackalinci/cve-2024-47176
Vulnerability Scanner for CUPS: CVE-2024-47176