
CVE-2025-6218_WinRAR
 speinador/cve-2025-6218_winrar
Educational lab demonstrating CVE-2025-6218 path traversal in WinRAR. Includes a malicious RAR file and step-by-step guide to observe file overwrite…
binary-exploitationeducationexploitation+3
16
speinador/cve-2025-6218_winrarEducational lab demonstrating CVE-2025-6218 path traversal in WinRAR. Includes a malicious RAR file and step-by-step guide to observe file overwrite…
 xdezen/cve-2025-8110
Python proof-of-concept for CVE-2025-8110, demonstrating arbitrary file write to RCE in Gogs via symlink and API, with educational lab usage.

 javaamo/cve-2021-41773
Fixed shell exploit for Apache HTTP Server 2.4.49 CVE-2021-41773 path traversal and remote code execution vulnerability. Reads arbitrary files and…
 yukafake/cve-2024-32002-reverse-shell
Este script demuestra cómo explotar la vulnerabilidad CVE-2024-32002 para obtener una reverse shell, proporcionando acceso remoto al sistema…
 moften/cve-2023-44487-http-2-rapid-reset-attack
HTTP/2 Rapid Reset Exploit PoC
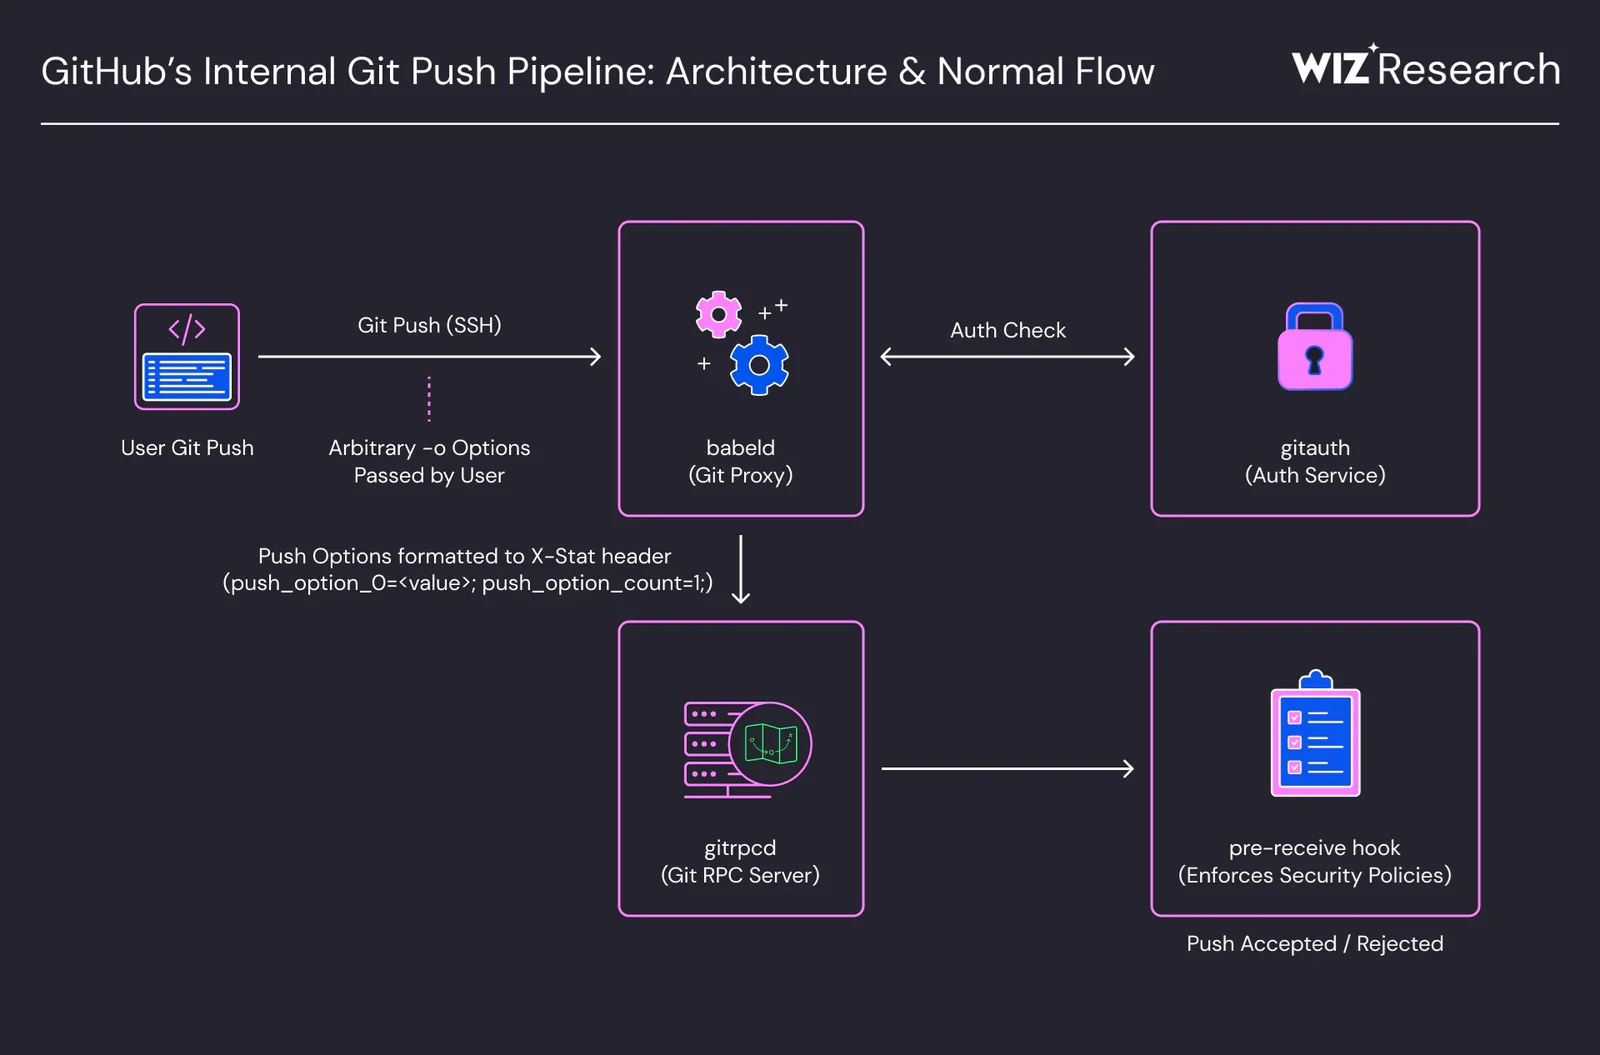 5kr1pt/cve-2026-3854
Technical breakdown of CVE-2026-3854, a GitHub RCE via header injection in git push, explaining the vulnerability, exploitation technique, and…
 jeanback1/cve-2023-30253-exploit
CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)
 richjj98/analise-vulnerabilidades-zabbix-notebooklm
Caderno Temático NotebookLM: análise de vulnerabilidades SQL Injection (CVE-2024-42327, CVE-2026-23921) no Zabbix, com engenharia de prompts, cadeia…
 fernandobortotti/cve-2024-24919
Automated exploit for CVE-2024-24919 with API-based vulnerable IP discovery and LFI brute-force using custom wordlists. Designed for educational…
 notrustedx/job-manager-disclosure
CVE-2015-6668, relacionada con el plugin WP Job Manager para WordPress (versiones ≤ 0.7.25).