
-CVE-2022-48150
 sahilh4ck4you/-cve-2022-48150
I Found the reflected xss vulnerability in shopware 5 .for more details check my poc video
information-gatheringpenetration-testingvulnerability-analysis+2
1
sahilh4ck4you/-cve-2022-48150I Found the reflected xss vulnerability in shopware 5 .for more details check my poc video
 with-fate/cve-2020-1938
Python script to verify Apache Tomcat CVE-2020-1938 vulnerability by sending crafted requests to the AJP port, allowing file read and potential code…
 gyaansastra/cve-2021-44228
Scanner and proof-of-concept exploit for the Log4Shell vulnerability (CVE-2021-44228) in Apache Log4j, enabling detection and exploitation of remote…
 sealldeveloper/cve-2023-40931-poc
The sqlmap payload to exploit CVE-2023-40931
 pwcno-cto/cve-2021-21234
Directory traversal vulnerability in the spring-boot-actuator-logview library
 shield-cyber/react2shell-scanner
Scanner to detect the presence of CVE-2025-55182 & CVE-2025-66478 on targeted web services.
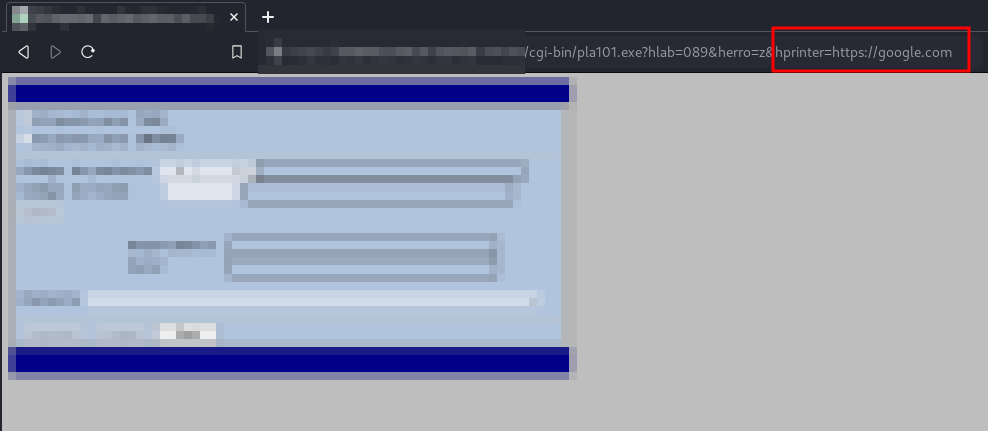 elizeuopain/poc-cve-2024-24034
Proof-of-concept exploit for CVE-2024-24034, an Open Redirect vulnerability in S.I.L 3.0 via the 'hprinter' parameter, enabling URL redirection…
 zer0-dave/cve-2023-1545-poc
Copy of the POC for CVE-2023-1545
 bigzooooz/cve-2024-55060
Proof-of-concept exploit for a stored XSS vulnerability in Rafed CMS v1.44, demonstrating injection via the index.php parameter.
 betillogalvanfbc/poc-cve-2022-44268
Proof-of-concept exploit for CVE-2022-44268, demonstrating the vulnerability and providing a working exploit for security testing and research.
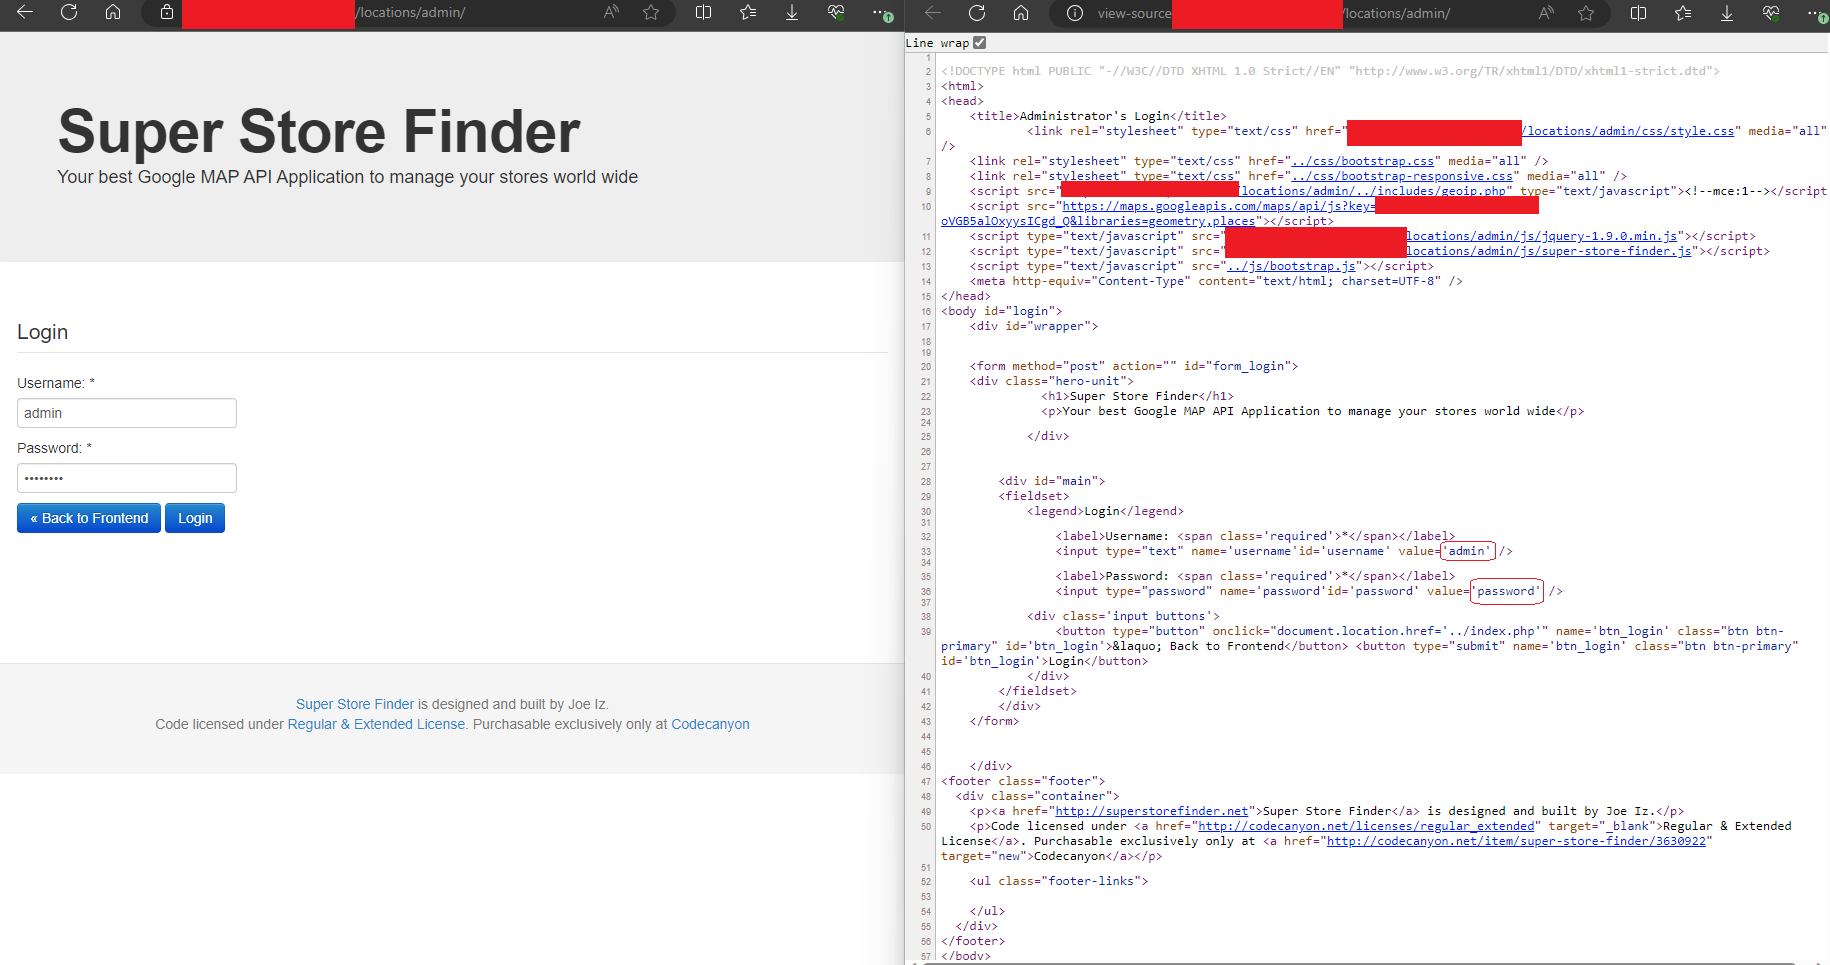 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 thecybergeek/cve-2019-19369
Authenticated remote code execution exploit for FusionPBX versions <= 4.5.10, leveraging the PHP-Editor function to inject a payload and gain a shell…
 erengozaydin/microfinance-management-system-v1.0-sql-injection-vulnerability-unauthenticated
Proof-of-concept exploit for an unauthenticated SQL injection vulnerability in Microfinance Management System V1.0, allowing remote data extraction…
 nebian/cve-2024-23897
Scraping tool to ennumerate directories or files with the CVE-2024-23897 vulnerability in Jenkins.
 arc4he/cve-2024-23334-poc
Proof of concept of the parh traversal in python AioHTTP library =< 3.9.1
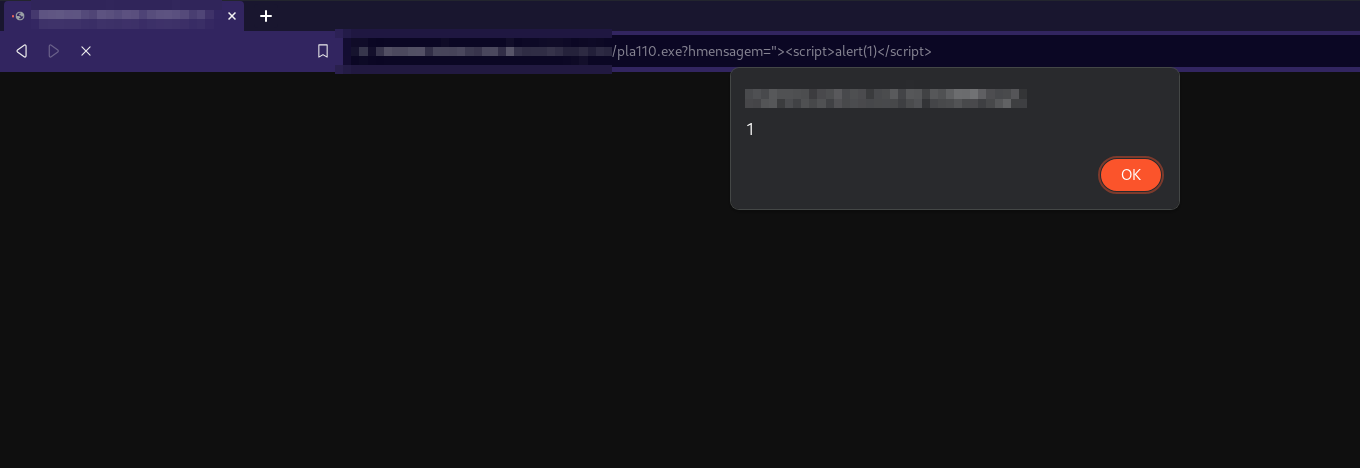 elizeuopain/poc-cve-2024-24035
Proof-of-concept exploit for DOM-based Cross-Site Scripting (XSS) vulnerability in SIL 3.1 via the 'hmessage' parameter, demonstrating the attack…
 rosemary1337/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an unauthenticated authentication bypass in cPanel/WHM using CRLF injection to leak security tokens and…
 kielvaughn/cve-2021-38603
Proof-of-concept for CVE-2021-38603: stored cross-site scripting (XSS) vulnerability in PluXML's profile edit page. Demonstrates injection via the…