
Archived
frevvomapexec
 hateshape/frevvomapexec
PoC Exploit for CVE-2018-8820
authenticationexploitationpenetration-testing+2
hateshape/frevvomapexecPoC Exploit for CVE-2018-8820
 0vercl0k/cve-2019-11708
Full exploit chain (CVE-2019-11708 & CVE-2019-9810) against Firefox on Windows 64-bit.
 bytereaper77/cve-2025-41373
PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 bytereaper77/cve-2025-7753
PoC Exploit for CVE-2025-7753 — Time-Based SQL Injection in Online Appointment Booking System 1.0 via the username parameter. Exploit written in C…
 bytereaper77/cve-2025-54589
PoC for CVE-2025-54589 – a reflected XSS vulnerability in Copyparty ≤ 1.18.6.
 progfay/nodejs-http-transfer-encoding-smuggling-poc
PoC of HTTP Request Smuggling in nodejs (CVE-2020-8287)
 tin-z/cve-2018-14714-poc
POC CVE-2018-14714
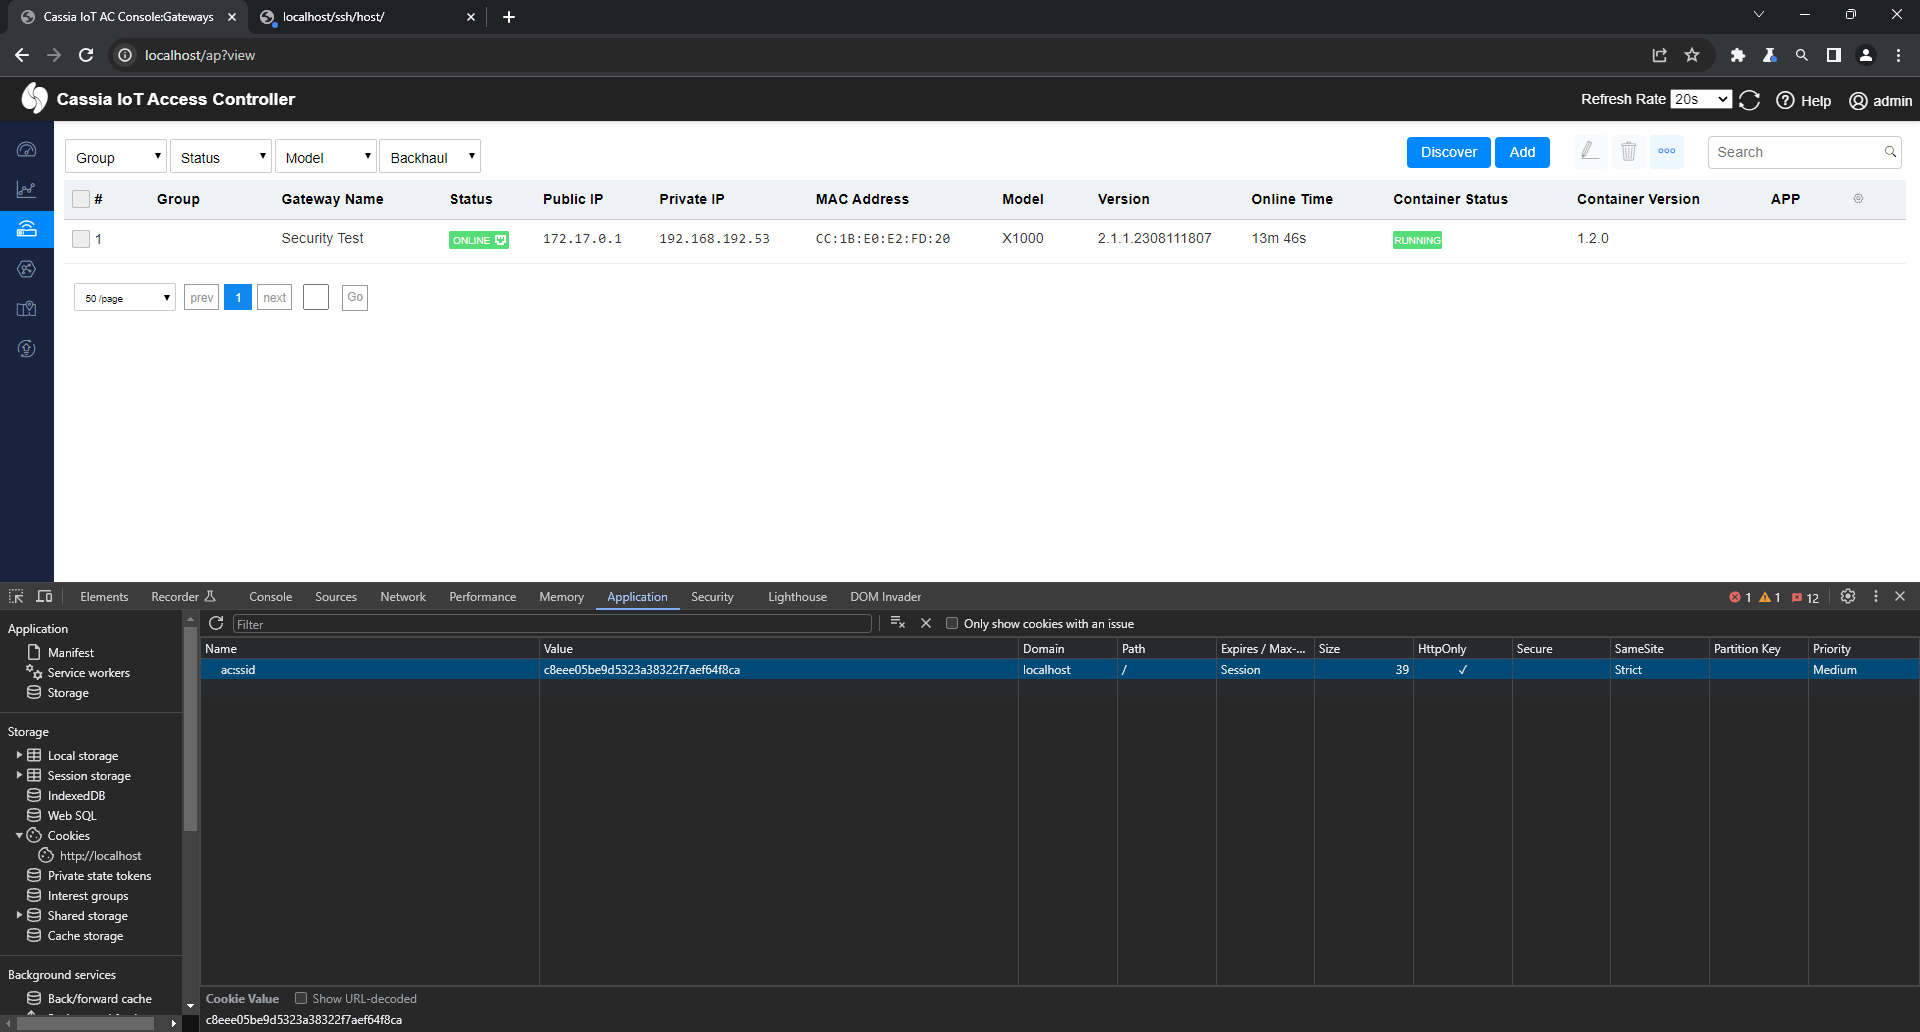 dodge-mptc/cve-2023-35793-csrf-on-web-ssh
Repository contains description for CVE-2023-35793
 bytereaper77/cve-2025-8471
Exploit SQL injection in projectworlds Online Admissions System v1.0
 hlldz/wildpwn
Brute forcer and shell deployer for WildFly
 bumheehan/cve-2021-44228-log4j-test
Demonstrates Log4Shell (CVE-2021-44228) exploitation with LDAP server, malicious JNDI payload, and vulnerable Spring Boot application for security…
 ap0dexme0/cve-2023-32315
Perform With Massive Openfire Unauthenticated Users
 li8u99/spring-data-mongodb-demo
Demo environment for CVE-2022-22980 (Spring Data MongoDB SpEL injection RCE) with vulnerable application code for security testing and education.
 jonpichel/cve-2017-7358
Proof-of-concept exploit for CVE-2017-7358, demonstrating a specific vulnerability in a software application. Intended for security research and…
 edgarloyola/cve-2021-36563
Proof-of-concept for stored and reflected XSS vulnerabilities in CheckMK Management Web Console versions 1.5.0 to 2.0.0p9, with detailed disclosure…
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 419066074/cve-2021-40859
Auerswald COMpact 8.0B Backdoors exploit
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…