
CVE-2023-6702
 kaist-hacking/cve-2023-6702
Chrome Renderer 1day RCE via Type Confusion in Async Stack Trace (v8ctf submission)
binary-exploitationctfeducation+3
872 years ago
kaist-hacking/cve-2023-6702Chrome Renderer 1day RCE via Type Confusion in Async Stack Trace (v8ctf submission)
 exploits-forsale/cve-2024-21345
Proof-of-concept exploit for CVE-2024-21345, demonstrating a specific vulnerability with functional code for security testing and validation.
 dgh05t/vmware_esxi_openslp_pocs
CVE-2020-3992 & CVE-2019-5544

 theori-io/cve-2022-26717-safari-webgl-exploit
Proof-of-concept exploit for CVE-2022-26717, a use-after-free vulnerability in Safari's WebGL implementation, enabling remote code execution via…
 flowerwind/autogeneratexalanpayload
cve-2022-34169 延伸出的Jdk Xalan的payload自动生成工具,可根据不同的Jdk生成出其所对应的xslt文件
 spiralbl0ck/chrome-v8-rce-cve-2021-38003
CVE-2021-38003 exploits extracted from https://twitter.com/WhichbufferArda/status/1609604183535284224
 idan5x/switcheroo
Exploiting CVE-2016-4657 to JailBreak the Nintendo Switch
 mbanyamer/cve-2025-30397---windows-server-2025-jscript-rce-use-after-free-
Remote Code Execution via Use-After-Free in JScript.dll (CVE-2025-30397)
 xuechiyaobai/cve-2019-9810-poc
Array.prototype.slice wrong alias information.
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 onlytoxi/cve-2025-8088-winrar-tool
Advanced WinRAR Path Traversal Exploit Tool for CVE-2025-8088
 0730nophone/cve-2022-22947-
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947) 注入哥斯拉内存马
 striga-ai/cve-2026-23918
Double-free in Apache httpd mod_http2 stream cleanup leading to pre-auth RCE.
 embedi/dir8xx_poc
Proof-of-Concept exploits for D-Link DIR8xx routers
 easis/cve-2018-20250-winrar-ace
Proof of concept code in C# to exploit the WinRAR ACE file extraction path (CVE-2018-20250).
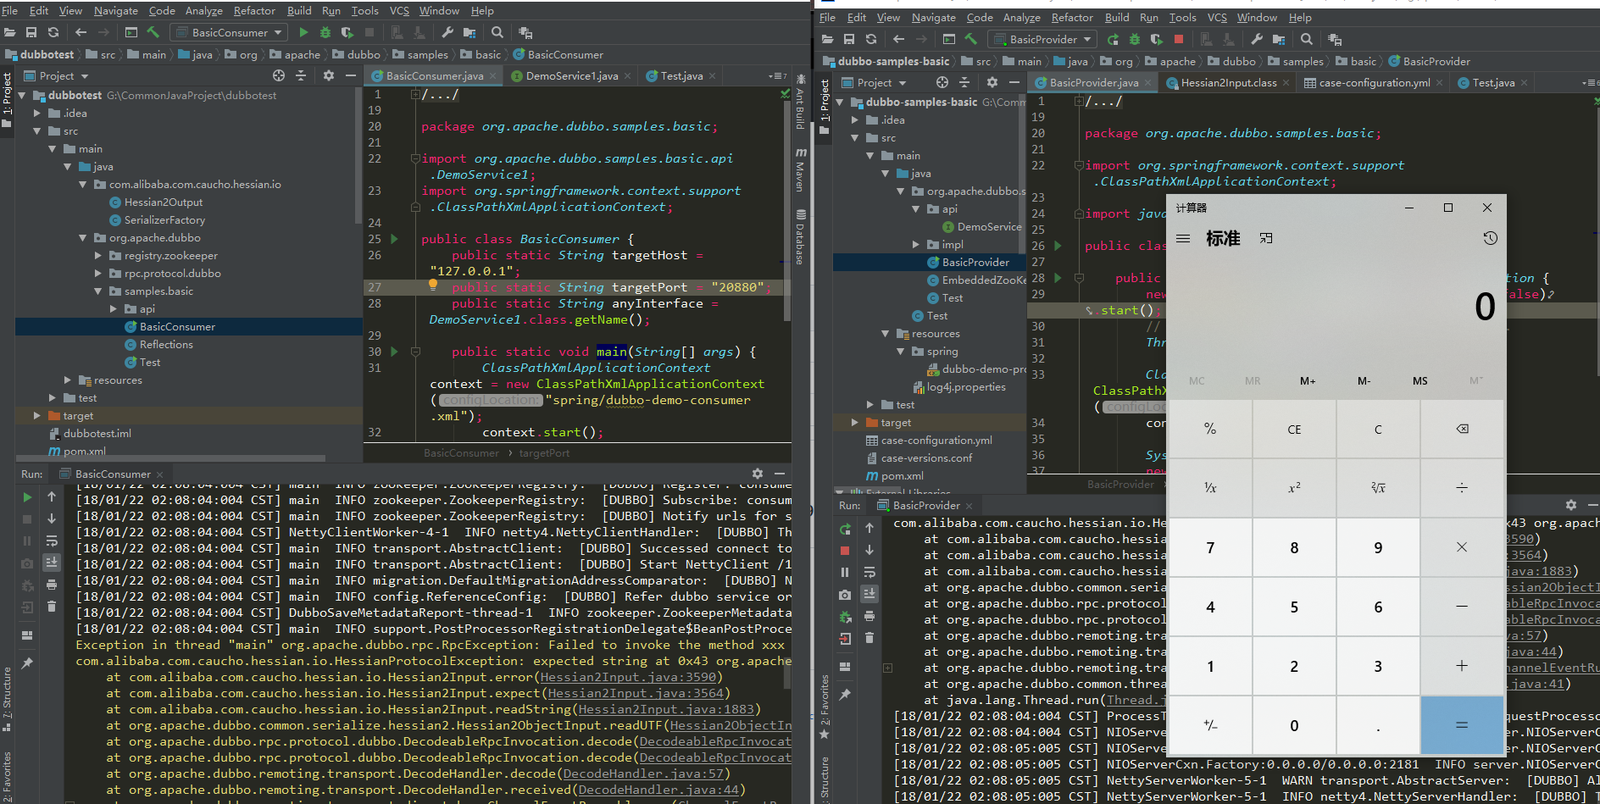 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 testanull/project_cve-2021-21985_poc
Proof-of-concept exploit for CVE-2021-21985, a critical remote code execution vulnerability in VMware vCenter Server, with JNI-based payload…