

CVE-2021-40539
 synacktiv/cve-2021-40539
Exploitation code for CVE-2021-40539
exploitationpenetration-testingred-teaming+2
synacktiv/cve-2021-40539Exploitation code for CVE-2021-40539
 dinhbaouit/cve-2021-26084
Exploit for CVE-2021-26084 targeting Confluence Server OGNL injection vulnerability for unauthenticated remote code execution.
 samwcyo/cve-2021-27651-poc
RCE for Pega Infinity >= 8.2.1, Pega Infinity <= 8.5.2
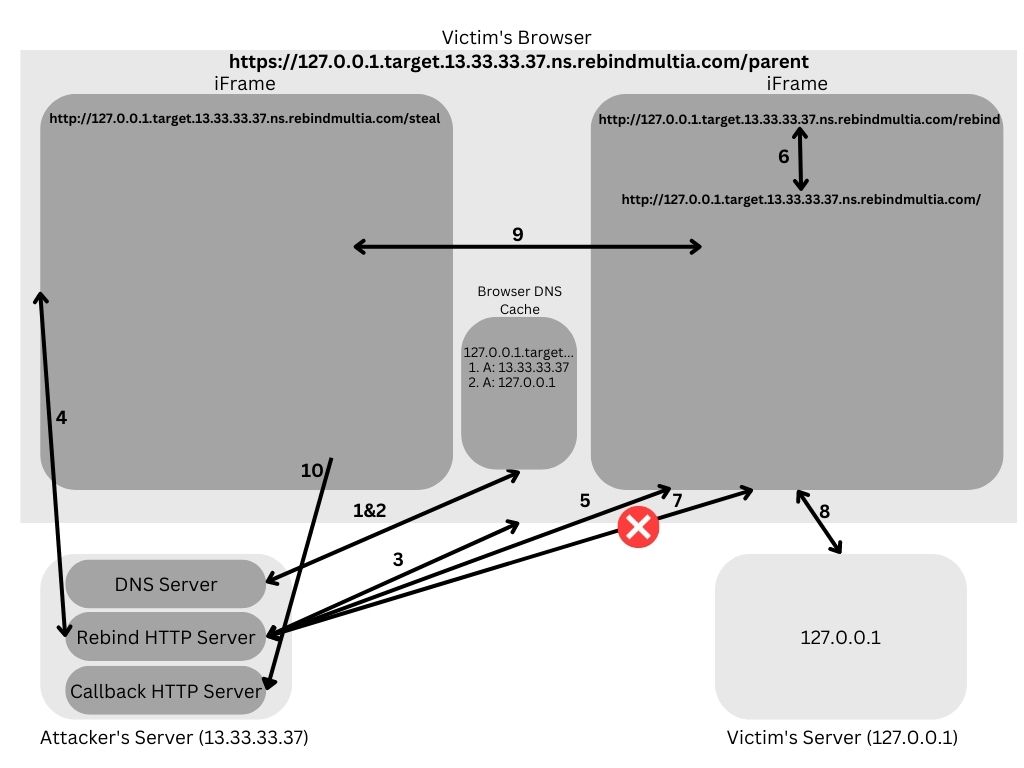 rhynorater/rebindmultia
DNS rebinding attack tool exploiting multiple A records to bypass same-origin policy and exfiltrate data from internal network services via browser…
 yassineaboukir/cve-2020-5902
Proof of concept for CVE-2020-5902
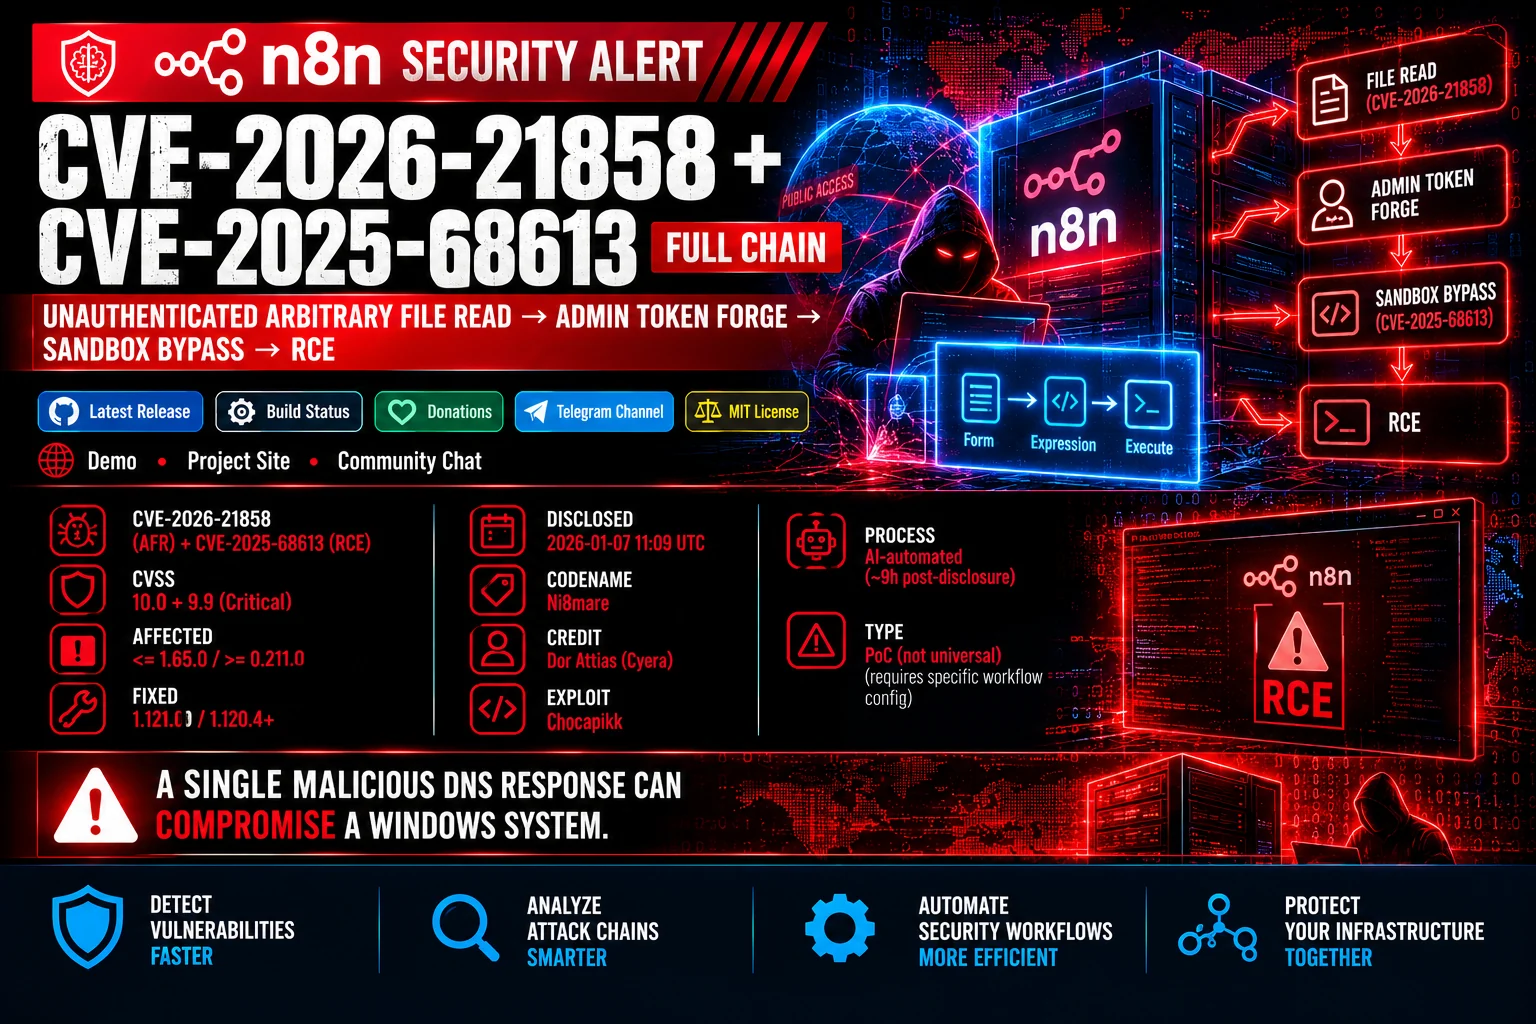 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
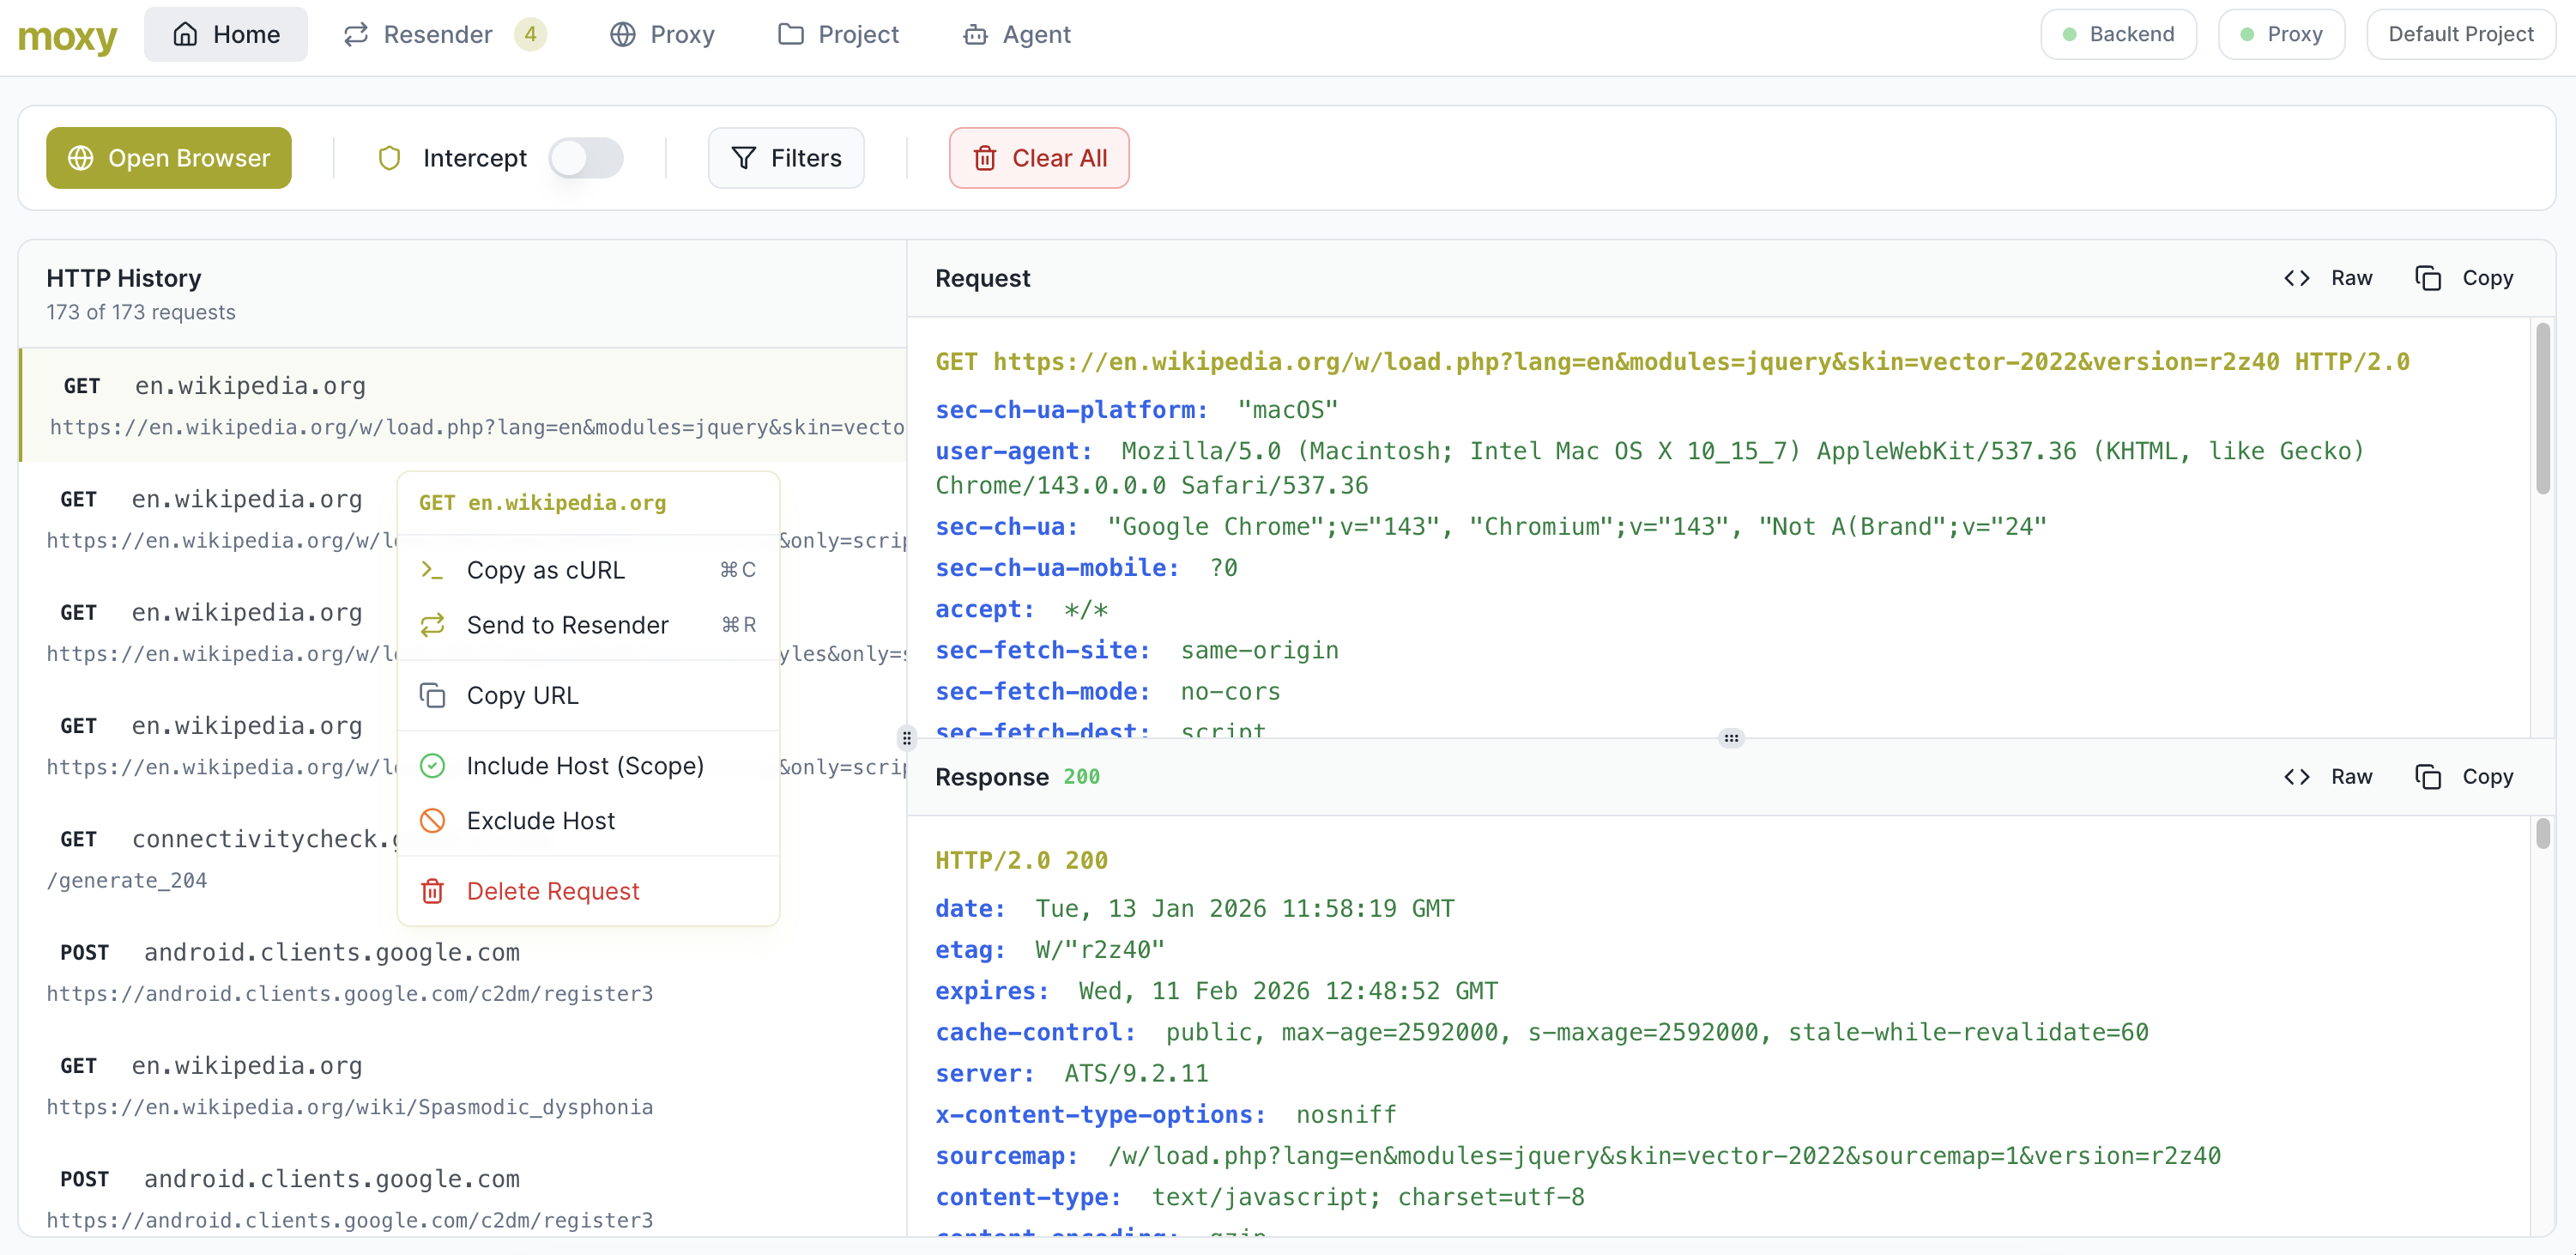 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 watchtowrlabs/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for CVE-2024-55591, demonstrating authentication bypass in FortiOS management interfaces via WebSocket race condition to…
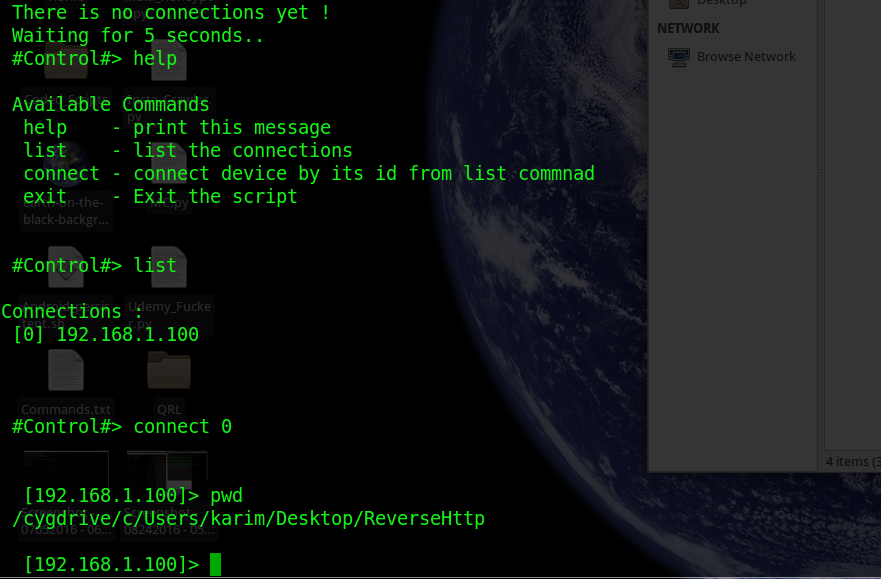 d4vinci/reversehttp
Python backdoor that uses http post/get requests to communicate
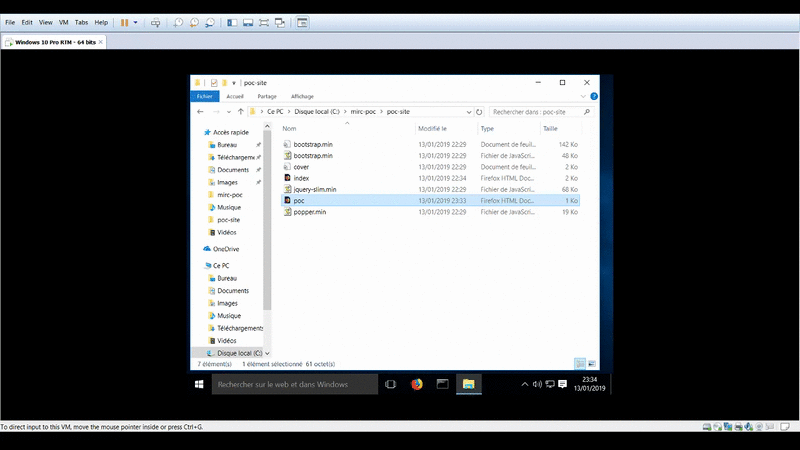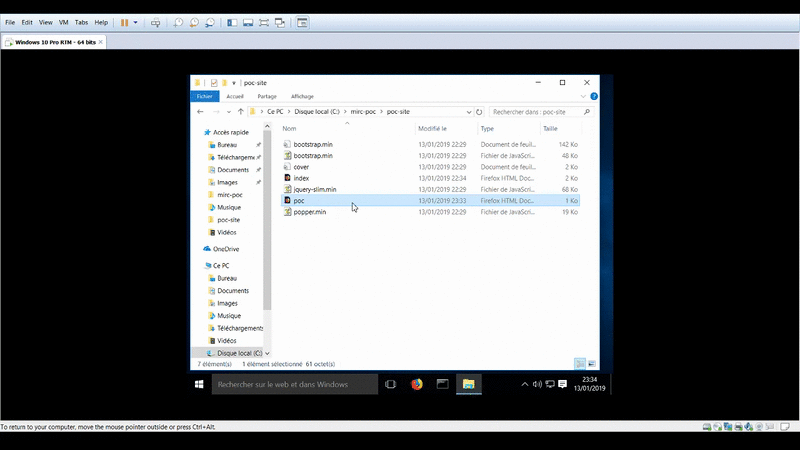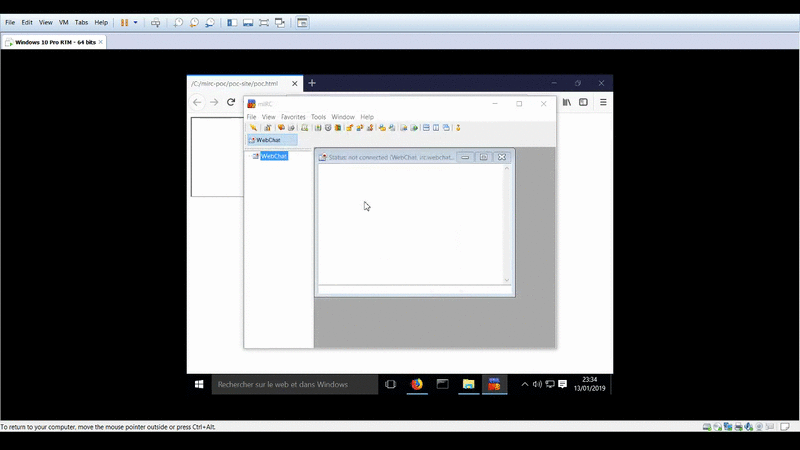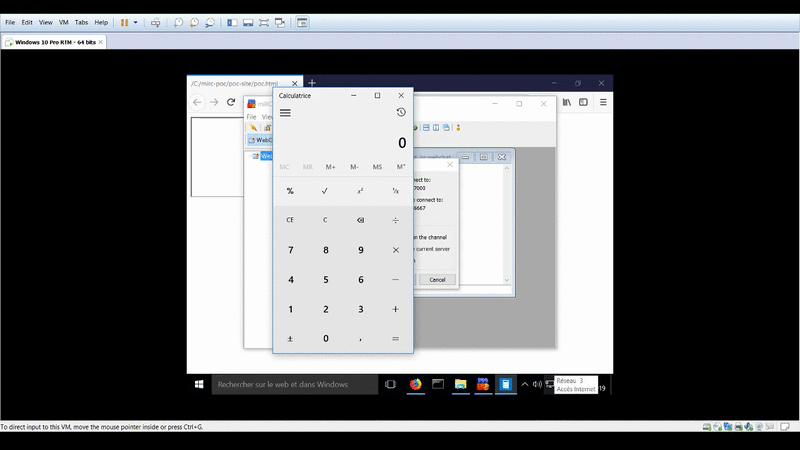 proofofcalc/cve-2019-6453-poc
Proof of calc for CVE-2019-6453
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
 jiansiting/cve-2019-2725
Exploit for CVE-2019-2725 targeting WebLogic WLS remote code execution vulnerability, enabling unauthenticated attackers to execute arbitrary…
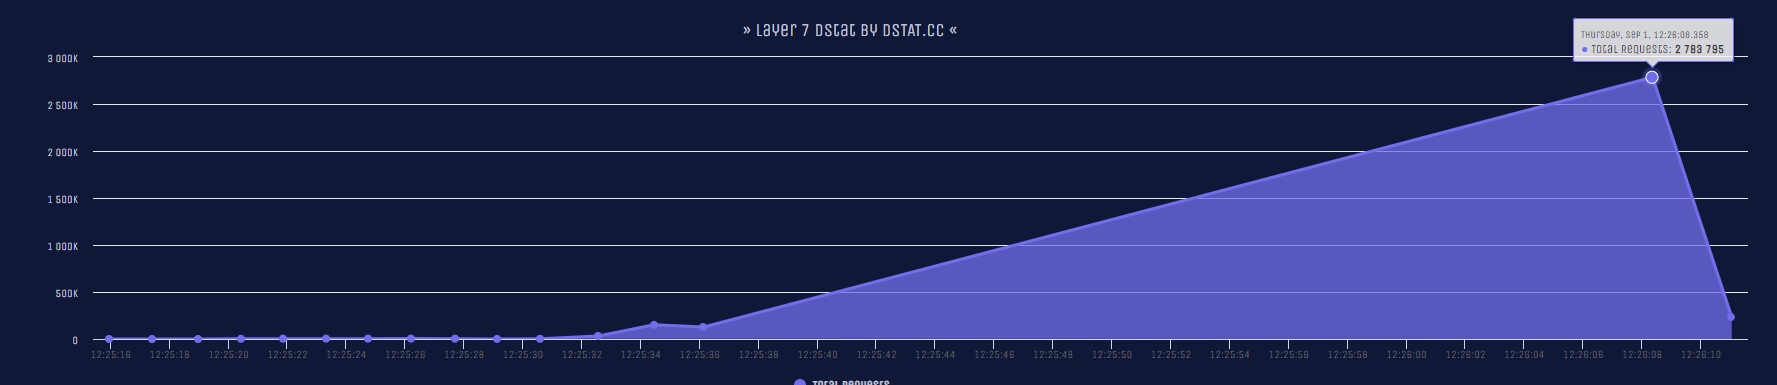 nayumidev/cc-ddos
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
 rsatan/next.js-exploit-tool
Next.js-Exploit-Tool 图形化综合利用工具,基于 Go 开发,一款针对 CVE-2025-55182 的独立安全评估工具。
 sfewer-r7/cve-2023-34362
CVE-2023-34362: MOVEit Transfer Unauthenticated RCE
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
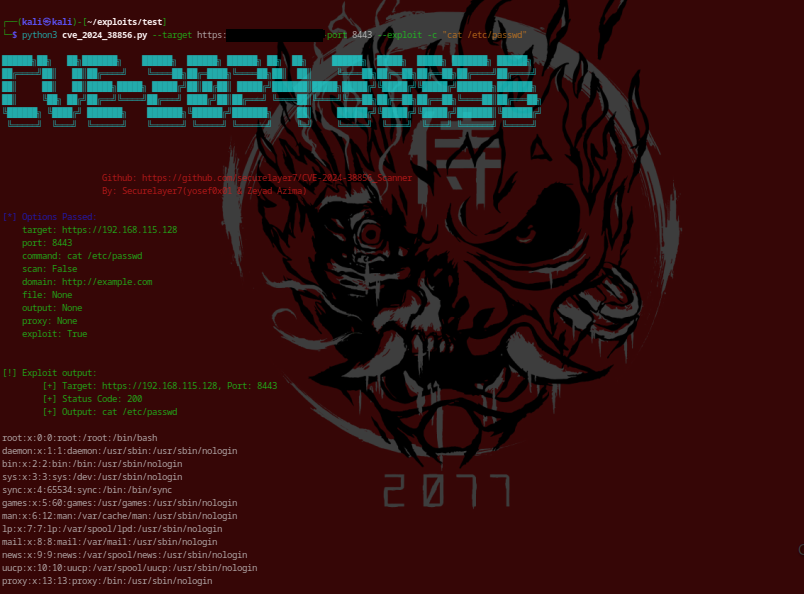 securelayer7/cve-2024-38856_scanner
Apache OFBiz RCE Scanner & Exploit (CVE-2024-38856)
 vnhacker1337/cve-2022-27925-poc
Zimbra RCE simple poc