
Archived
CVE-2021-46398
 laliea/cve-2021-46398
A Proof of Concept for the CVE-2021-46398 flaw exploitation
educationexploitationlabs-practice+3
laliea/cve-2021-46398A Proof of Concept for the CVE-2021-46398 flaw exploitation
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…


 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 urbanadventurer/whatweb
Next generation web scanner
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 theori-io/cve-2022-26717-safari-webgl-exploit
Proof-of-concept exploit for CVE-2022-26717, a use-after-free vulnerability in Safari's WebGL implementation, enabling remote code execution via…
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
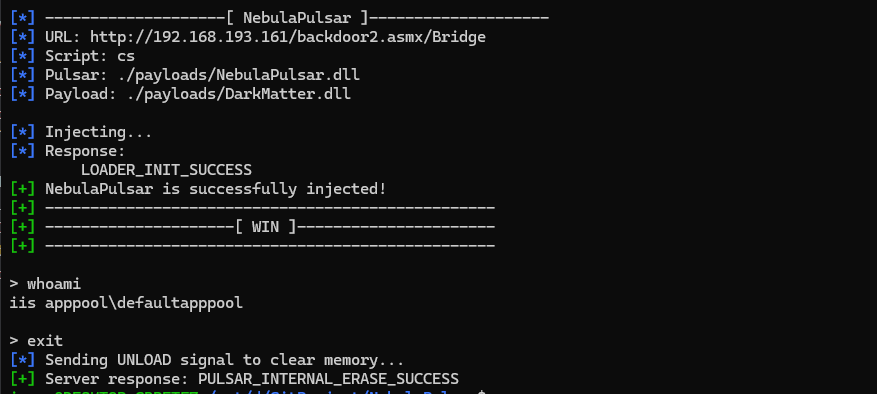 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 0730nophone/cve-2022-22947-
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947) 注入哥斯拉内存马
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.
 feliam/cve-2013-2730
Proof-of-concept exploit for CVE-2013-2730, demonstrating a memory corruption vulnerability with a C-based implementation for security research and…