

raider
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
owasp/raiderOWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 leo-mitch/cve-2024-41570-havoc-c2-rce
This is a Chained RCE in the Havoc C2 framework using github.com/chebuya and github.com/IncludeSecurity pocs
 jakeotte/badbizness-cve-2023-51467
Auto exploit script for the Java web framework OF Biz under CVE-2023-51467.
 shoucheng3/apache__myfaces_cve-2011-4367_2-0-11
Exploit for CVE-2011-4367 targeting Apache MyFaces JSF implementation, demonstrating a remote code execution vulnerability in the Jakarta Faces…
 forse01/cve-2020-11990-cordova
Proof-of-concept exploit for CVE-2020-11990 targeting Apache Cordova applications, demonstrating a remote code execution vulnerability in the mobile…
 c0rel0ader/east
Exploits and Security Tools Framework 2.0.1
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 math-x-io/cve-2024-54152
PoC exploit for Angular Expressions sandbox escape (CVE-2024-54152) achieving RCE via malicious expression. Includes Docker environment and payload…
 ant1sec-ops/cve-2024-33453
Sensitive Data exposure
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 glowbase/cve-2019-19609
Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
 certitude-consulting/cve-2025-25599
Proof of Concept for CVE-2025-25599
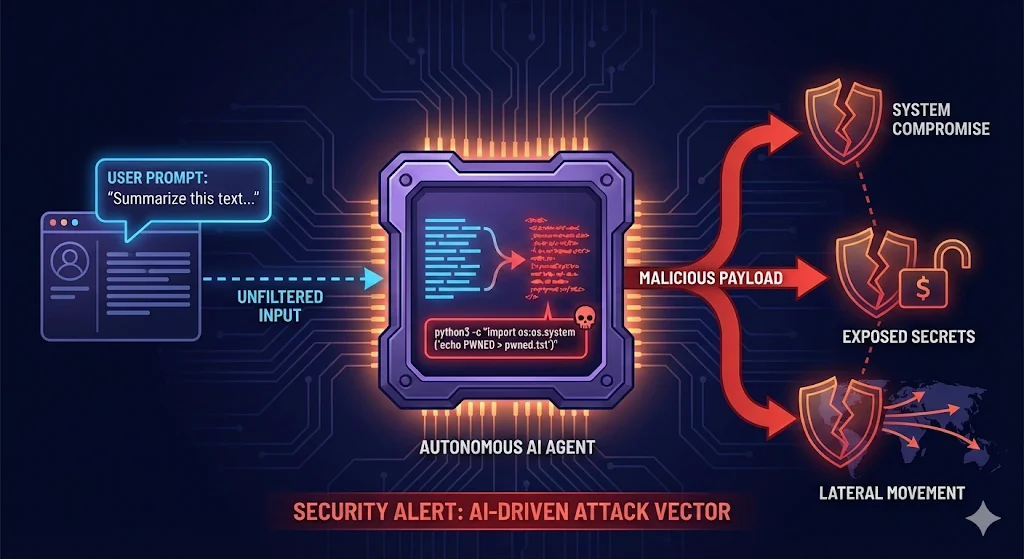 itamar-yochpaz/cve-2026-2256-poc
Proof-of-concept demonstrating a command injection vulnerability in MS-Agent Shell tool, enabling arbitrary command execution and reverse shell via…
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…