
dotnetpaddingoracle
 nccgroup/dotnetpaddingoracle
Python Implementation of a .NET Padding Oracle Assessment Tool
cryptographyencryption-decryption-toolsexploitation+3
31
nccgroup/dotnetpaddingoraclePython Implementation of a .NET Padding Oracle Assessment Tool
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 cybermaksx/cve-2022-46364-proof-of-the-concept
This vulnerability allows an attacker to perform SSRF (Server-Side Request Forgery) attacks on Apache CXF webservices that accept MTOM/XOP requests.…
 jra89/cve-2019-19654
Proof-of-concept exploit for CVE-2019-19654: Chevereto denial of service via path traversal in the bulk importer, allowing authenticated admin to…
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
 megafart1/cve-2026-2472-vertex-ai-sdk-google-cloud
Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.
 mr-kasim-mehar/cve-2024-24919-exploit
Java-based scanner that checks IP addresses for CVE-2024-24919 vulnerability, with interactive options to print response data and change target file…
 exploit-io/cve-2021-41349
Exploit tool for CVE-2021-41349 that generates an HTML form to deliver XSS payloads to Microsoft Exchange servers, enabling execution of arbitrary…
 0xgh057r3c0n/cve-2026-10580
PoC exploit for CVE-2026-10580 - Authentication Bypass in Hippoo Mobile App for WooCommerce <= 1.9.4 leading to Admin Account Takeover
 teymurnovruzov/cve-2019-9053-python3-remastered
The script has been remastered by Teymur Novruzov to ensure compatibility with Python 3. This tool is intended for educational purposes only.…
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 mohandacherir/cve-2021-23639
Exploit of CVE-2021-23639 for the vulnerable library 'md-to-pdf' in JS
 revoltsecurities/cve-2023-22518
An Exploitation tool to exploit the confluence server that are vulnerable to CVE-2023-22518 Improper Authorization
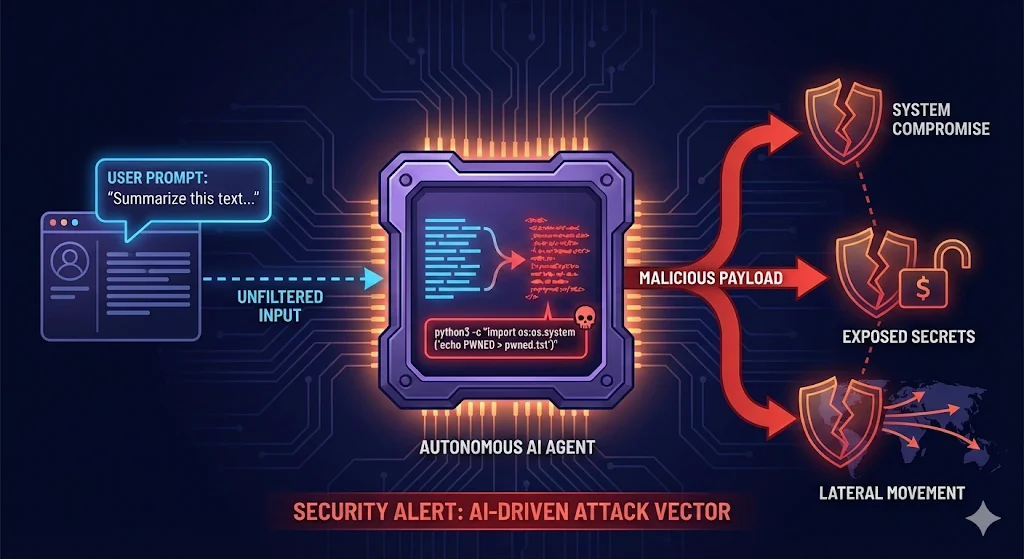 itamar-yochpaz/cve-2026-2256-poc
Proof-of-concept demonstrating a command injection vulnerability in MS-Agent Shell tool, enabling arbitrary command execution and reverse shell via…
 k3ystr0k3r/cve-2024-3273-exploit
A PoC exploit for CVE-2024-3273 - D-Link Remote Code Execution RCE
 aj2108/cve-2026-8347
CVE-2026-8347 is an Insecure Direct Object Reference (IDOR) combined with a wrong authorization level vulnerability in Concrete CMS versions 9.5.0…
 xenophil90/edb-49263-fixed
Fixed version of the Python script to exploit CVE-2018-19571 and CVE-2018-19585 (GitLab 11.4.7 - Authenticated Remote Code Execution) that is…
 jayngng/cve-2021-22911
Modifed ver of the original exploit to save some times on password reseting for unprivileged user