
exchange_proxylogon
 mekhalleh/exchange_proxylogon
Module pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
exploit-frameworkspayload-developmentpenetration-testing-frameworks+2
4
mekhalleh/exchange_proxylogonModule pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
 realistic-security/cve-2017-16524
Unrestricted file upload vulnerability - Web Viewer 1.0.0.193 on Samsung SRN-1670D
 randomrobbiebf/wordpress-php-object-helper
Know a plugin has a php object exploit but need to find which lib to use?
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 lazytitan33/cve-2026-67599_clearos_rce
Authenticated Blind OS Command Injection in ClearOS
 securifera/cve-2026-20217
Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
 anggatechi/cve-2026-63030
WordPress Core Pre-Auth RCE — Batch Route Confusion + SQL Injection
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
 wind010/cve-2026-39987_poc
A proof-of-concept for CVE-2026-39987
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
 dsfau/wordpress-cve-2018-6389
Metasploit module for WordPress DOS load-scripts.php CVE-2018-638
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 jenderal92/csrf-exploit-generator
The CSRF Exploit Generator allows users to generate a CSRF exploit form with configurable parameters.
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…
 puppetma4ster/metasploit-wordpress-canto-exploit-rce
this is a metasploit exploit module for CVE-2024-25096 and CVE-2023-3452
 tdawg506/mailenable-cve-2022-36934
Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE
 s1gh/quickbox-pro-2.1.8-authenticated-rce
Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…
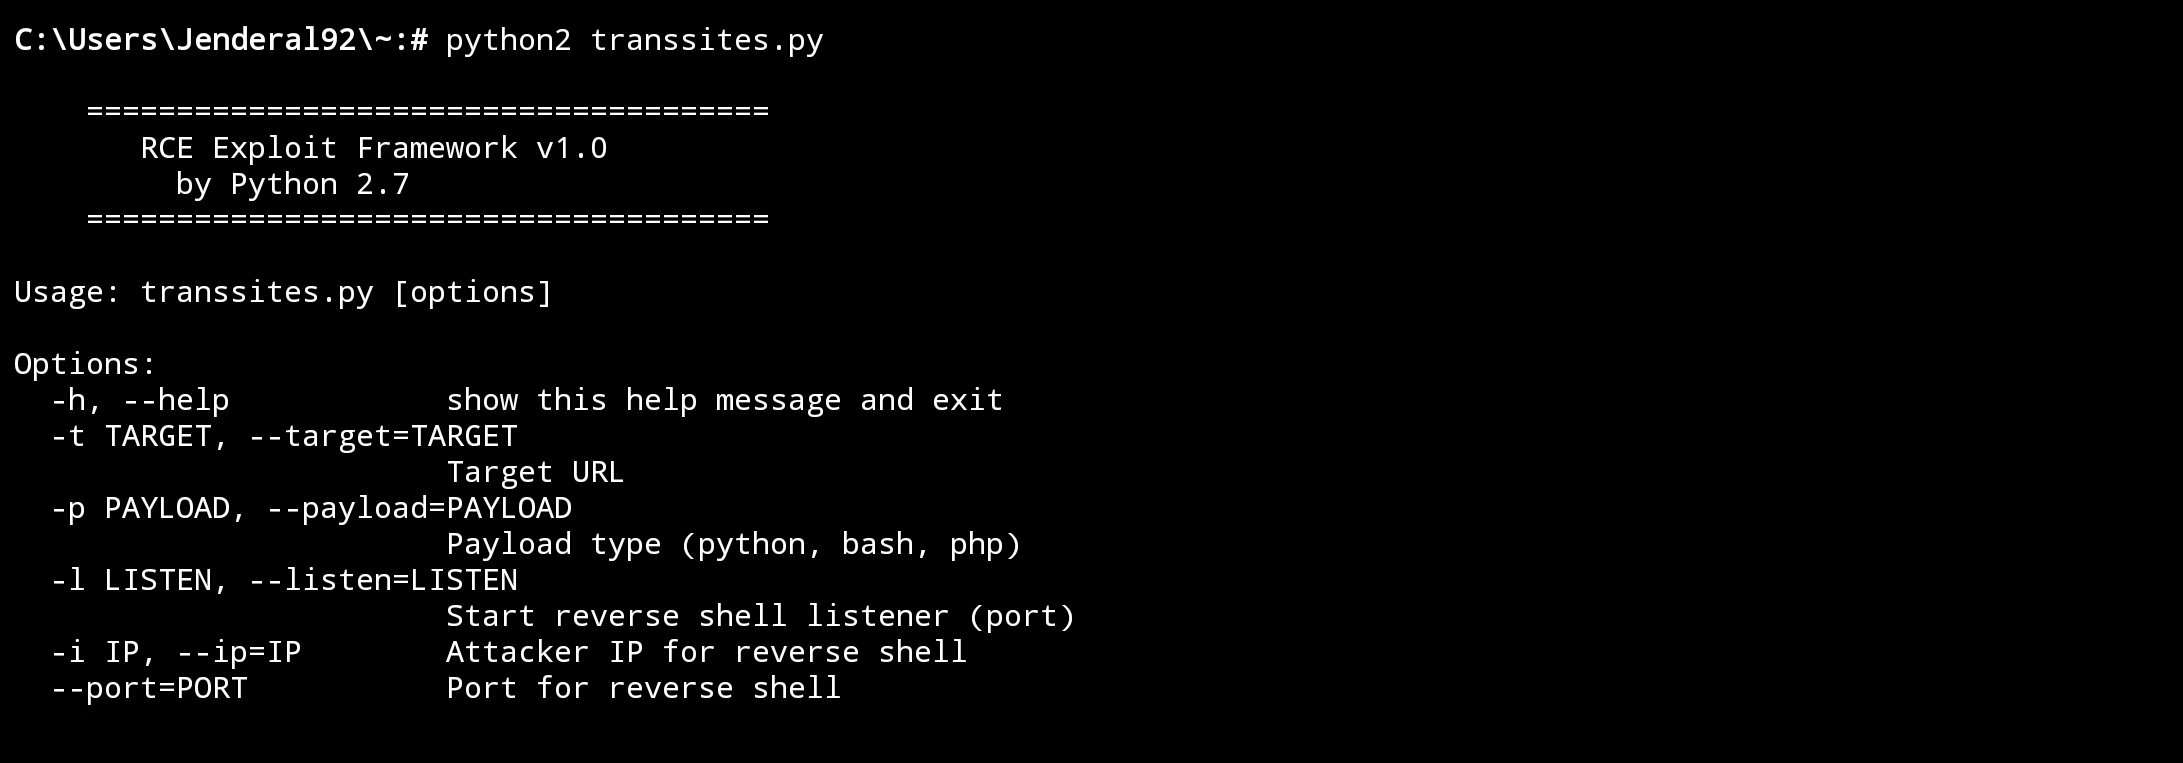 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.