CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…

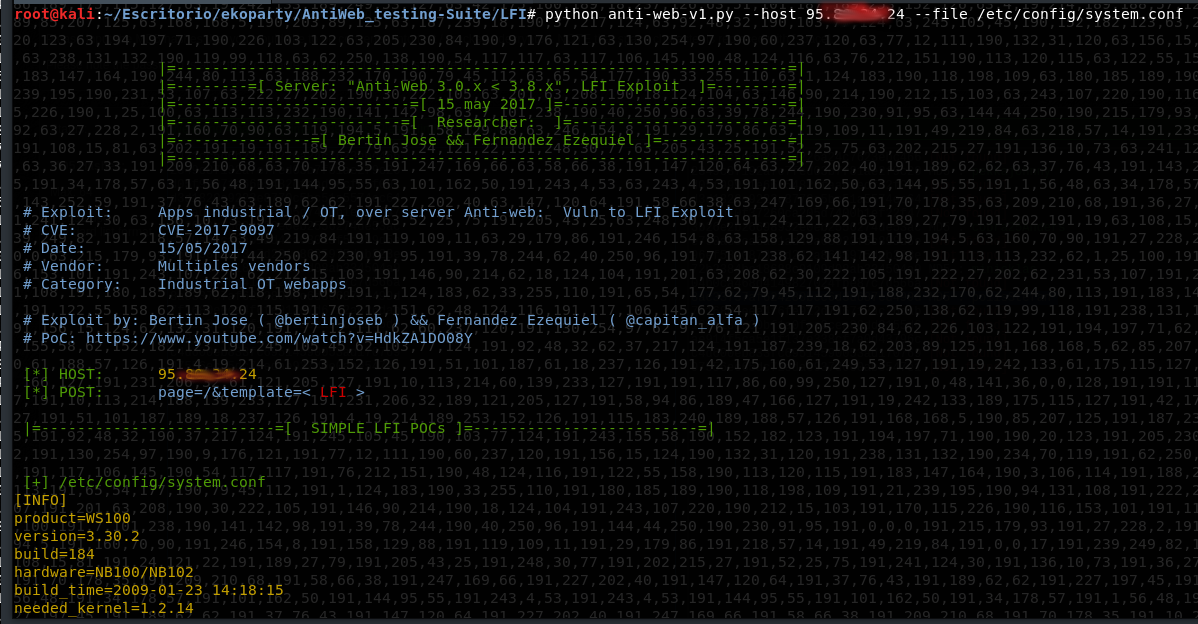
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)

Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…

Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.

This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.

Exploit for CVE-2025-2011

CMS Made Simple < 2.2.10 - SQL Injection . Actual working version

Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…

Improved code of Daniele Scanu SQL Injection exploit

Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…

Proof of Concept code for exploitation of CVE-2024-38793 (Best Restaurant Menu by PriceListo <= 1.4.1 - Authenticated (Contributor+) SQL Injection)

Exploits Python cve-2019-9053– by HackHeart

Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.