
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
107 results
CVE-2026-66492 preview

CVE-2026-66492

GitHubtoanln-cov/cve-2026-66492

The Joomla extension PhocaCommander is vulnerable to Path Traversal in the file upload action - CVSS 6.1

exploitationpenetration-testingvulnerability-analysis+2
1 month ago
CVE-2026-66491 preview

CVE-2026-66491

GitHubtoanln-cov/cve-2026-66491

The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
exploitationinformation-gatheringpenetration-testing+3
1 month ago
CVE-2026-13001 preview

CVE-2026-13001

GitHubghostpels/cve-2026-13001

Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…

educationexploitationpayload-development+3
2 months ago
magento2-session-reaper-patch preview

magento2-session-reaper-patch

GitHubwubinworks/magento2-session-reaper-patch

Patch for CVE-2025-54236(a.k.a Session Reaper) which allows customer account takeover and RCE under certain conditions. This patch is actually a…

authenticationexploitationvulnerability-analysis+2
410 months ago
CVE-2026-48939_PoC preview

CVE-2026-48939_PoC

GitHubchiefyoru/cve-2026-48939_poc

iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
code-analysisexploitationvulnerability-analysis+1
2 months ago
CVE-2026-56291_PoC preview

CVE-2026-56291_PoC

GitHubchiefyoru/cve-2026-56291_poc

The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…
exploitationpayload-generationpenetration-testing+2
2 months ago
CVE-2026-56290_PoC preview

CVE-2026-56290_PoC

GitHubchiefyoru/cve-2026-56290_poc

The Joomla extension Page Builder CK is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to…

exploitationpayload-generationpenetration-testing+2
2 months ago
asdsadsadasdasdsadsad preview

asdsadsadasdasdsadsad

GitHubfrada321/asdsadsadasdasdsadsad

CVE-2026-49049 - Unauthenticated File Deletion, Arbitrary Write & XSS Injection for Helix3 Joomla Extension

exploitationpenetration-testingvulnerability-analysis+2
2 months ago
CVE-2026-48907_PoC preview

CVE-2026-48907_PoC

GitHubchiefyoru/cve-2026-48907_poc

Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla
exploitationpenetration-testingred-teaming+2
12 months ago
CVE-2017-10952 preview

CVE-2017-10952

GitHubafbase/cve-2017-10952

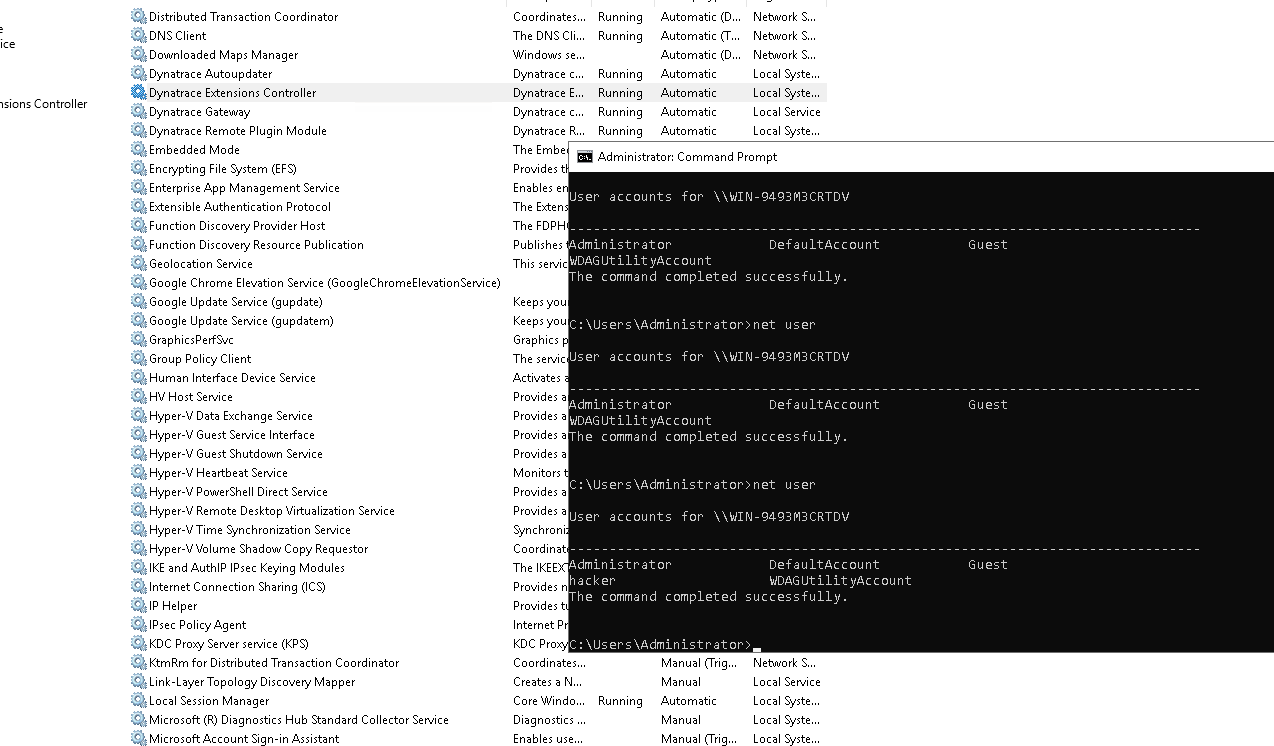
Demonstrates a local code execution exploit for Foxit PDF Reader via XFA-based PDFs, with step-by-step attack reproduction and extension to related…
binary-exploitationeducationexploitation+2
16 years ago
CVE-2025-61304 preview

CVE-2025-61304

GitHubpentastic-be/cve-2025-61304

OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address

exploitationpayload-generationpost-exploitation+3
211 months ago
CVE-2019-15120 preview

CVE-2019-15120

GitHubh3llraiser/cve-2019-15120

Exploit for XSS via BBCode on Kunena extension before 5.1.14 for Joomla!
educationexploitationpenetration-testing+3
16 years ago
CVE-2026-48907 preview

CVE-2026-48907

GitHubwearehackers160/cve-2026-48907

CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…

exploitationpayload-generationpenetration-testing+3
3 months ago
CVE-2026-46275 preview

CVE-2026-46275

GitHubxxconi/cve-2026-46275

Python exploit for CVE-2026-46725, achieving unauthenticated remote code execution in TYPO3 ceselector extension via PHP object injection and Monolog…

code-analysiseducationexploitation+4
4 months ago
chyrp-lite-rce-poc preview

chyrp-lite-rce-poc

GitHubiltosec/chyrp-lite-rce-poc

CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation
educationexploitationpayload-development+4
3 months ago
R2SAE preview

R2SAE

GitHuboscar-mine/r2sae

Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
command-and-controlexploitationpayload-generation+5
4 months ago
CVE-2024-9264-Fixed preview

CVE-2024-9264-Fixed

GitHubexerrdev/cve-2024-9264-fixed

Fixed proof-of-concept exploit for CVE-2024-9264, a critical Grafana RCE via DuckDB SQL expressions. Executes reverse shell using corrected shellfs…

educationexploitationpayload-development+3
1 year ago
CVE-2018-19518 preview

CVE-2018-19518

GitHubensimag-security/cve-2018-19518

Docker-based lab environment demonstrating CVE-2018-19518 RCE exploit via PHP IMAP extension, with step-by-step usage and WAF integration for…

educationexploitationlabs-practice+2
7 years ago
Previous123456Next