

CVE-2021-22204
 pentestical/cve-2021-22204
Shell script exploit for CVE-2021-22204 targeting Exiftool, generating a malicious .djvu file to achieve remote code execution on vulnerable systems.
exploitationpayload-generationremote-access-tool+2
3
pentestical/cve-2021-22204Shell script exploit for CVE-2021-22204 targeting Exiftool, generating a malicious .djvu file to achieve remote code execution on vulnerable systems.
 ahmedshamsddin/cve-2025-55182
Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…
 royall-researchers/cve-2024-9264
Python proof-of-concept for remote code execution in Grafana via SQL Expressions, exploiting insufficient input sanitization to execute arbitrary…
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 darkcast/cve-2020-10257
Shell exploit script for CVE-2020-10257, an unauthenticated RCE in the WordPress TRX Addons plugin that creates admin users via the wp-json API…
 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 prnjlksingh/php-cve-2026-115560-demo
Local intentionally vulnerable PHP lab demonstrating CVE-2026-115560: session serialize_handler mismatch leading to unserialize() gadget RCE, with a…
 0xm4ud/proftpd_cve-2015-3306
Exploit for ProFTPD 1.3.5 CVE-2015-3306 that writes a PHP backdoor to the target webroot and spawns a reverse shell for remote code execution.
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 godylockz/cve-2021-44967
Proof-of-concept exploit for CVE-2021-44967 enabling remote code execution in LimeSurvey 5.2.4 via malicious plugin upload, with reverse shell…
 housma/cve-2019-9978-social-warfare-wordpress-plugin-rce
The `swp_debug` parameter in `admin-post.php` allows remote attackers to include external files containing malicious PHP code, which are evaluated on…
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
 mananispiwpiw/cve-2025-8110-poc
One-shot exploit for Gogs symlink RCE (CVE-2025-8110) that triggers a reverse shell via a single PUT request to UpdateRepoFile.
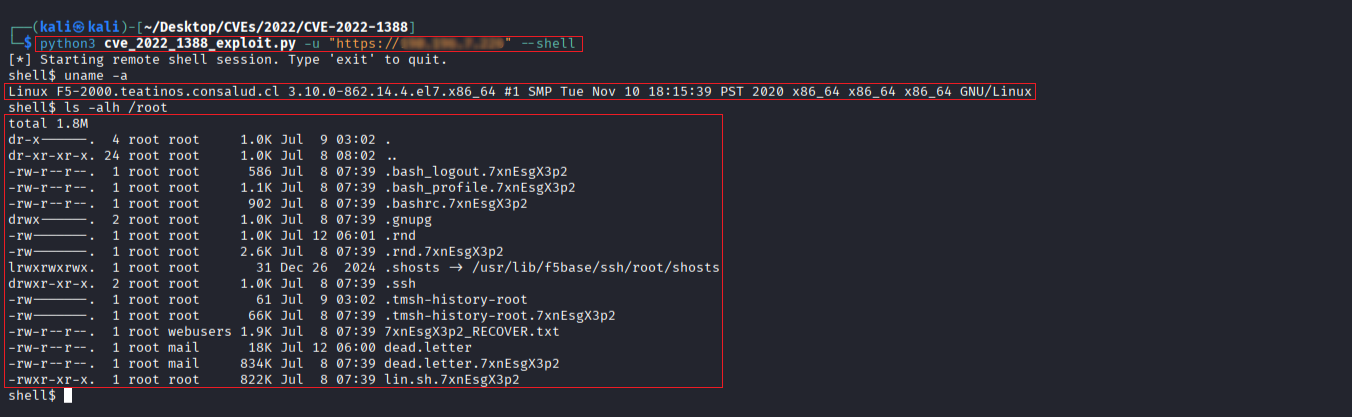 r0otk3r/cve-2022-1388
Python exploit for CVE-2022-1388, an unauthenticated remote command execution vulnerability in F5 BIG-IP iControl REST. Supports single commands and…
 godylockz/cve-2024-42327
POC for CVE-2024-42327: Zabbix Privilege Escalation -> RCE
 hadrian3689/webmin_1.920
Python3 exploit for CVE-2019-15107 Webmin 1.920 unauthenticated remote command execution, delivering reverse shells or firewall-evading…