
CVE-2024-3400
 wa6n3r/cve-2024-3400
Multi-threaded exploit tool for CVE-2024-3400 in Palo Alto PAN-OS with automated artifact download and detailed logging for confirmed RCE.
exploitationpenetration-testingreconnaissance+3
1
wa6n3r/cve-2024-3400Multi-threaded exploit tool for CVE-2024-3400 in Palo Alto PAN-OS with automated artifact download and detailed logging for confirmed RCE.
 vesperp/cve-2021-42237-sitecore-xp
Automated exploit tool for CVE-2021-42237 targeting SiteCore XP. Reads target URLs from a file and leverages DNSLog for out-of-band detection.
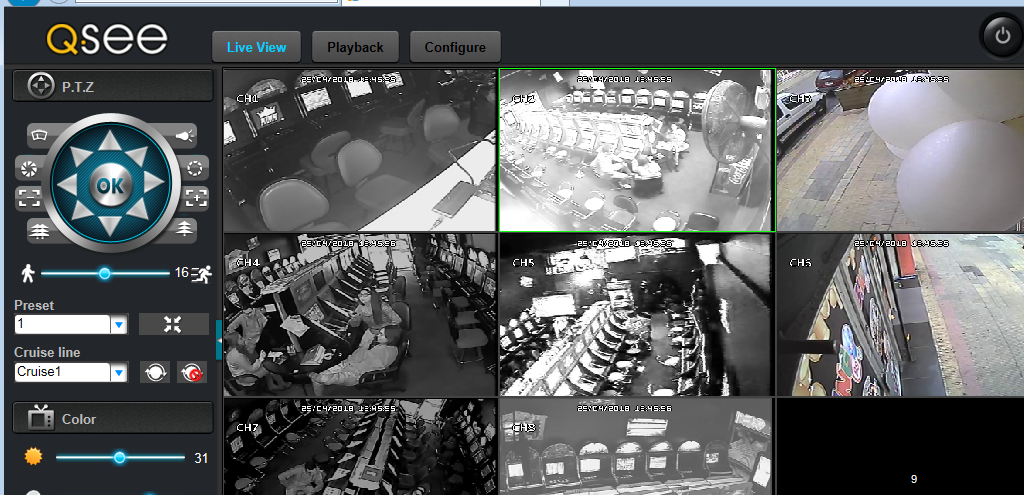 mrali-code/cve-2018-9995_dvr_credentials
Exploit tool for CVE-2018-9995 that extracts DVR credentials via unauthenticated HTTP request to vulnerable Nov, CeNova, QSee, and other DVR devices.
 imbas007/cve-2025-25257
Python-based exploit tool for CVE-2025-25257 in FortiWeb. Automates SQL injection detection, webshell upload, and remote command execution on…
 nhpt/cve-2022-24086-rce
Python-based exploit tool for CVE-2022-24086 (Magento RCE) with batch scanning of 334,300+ hosts from Shodan. Automates vulnerability detection and…
 givemefivw/cve-2021-3019
Automated exploitation tool for CVE-2021-3019 that reads target IPs from a text file and executes the exploit against HTTP endpoints.
 overgrowncarrot1/dejavu-cve-2021-22205
Exploit tool for CVE-2021-22205, targeting a remote code execution vulnerability in GitLab. Enables automated exploitation and security assessment.
 srcx404/cve-2024-39722
Exploit tool for CVE-2024-39722, a model existence disclosure vulnerability in Ollama. Performs version checks, crawls official model library, and…
 kkyehit/log4j_cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) targeting vulnerable Log4j instances for remote code execution and security testing.
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 voidsshadows/hikvision-city-hunter
This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
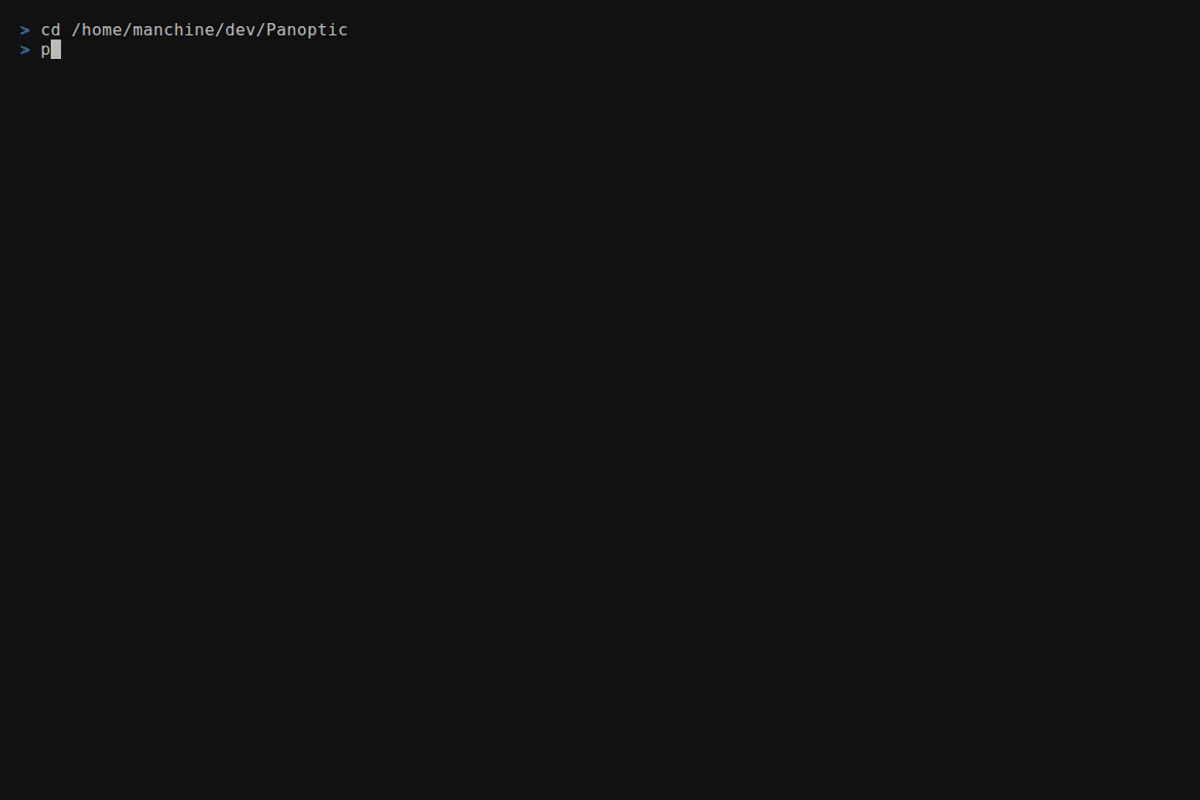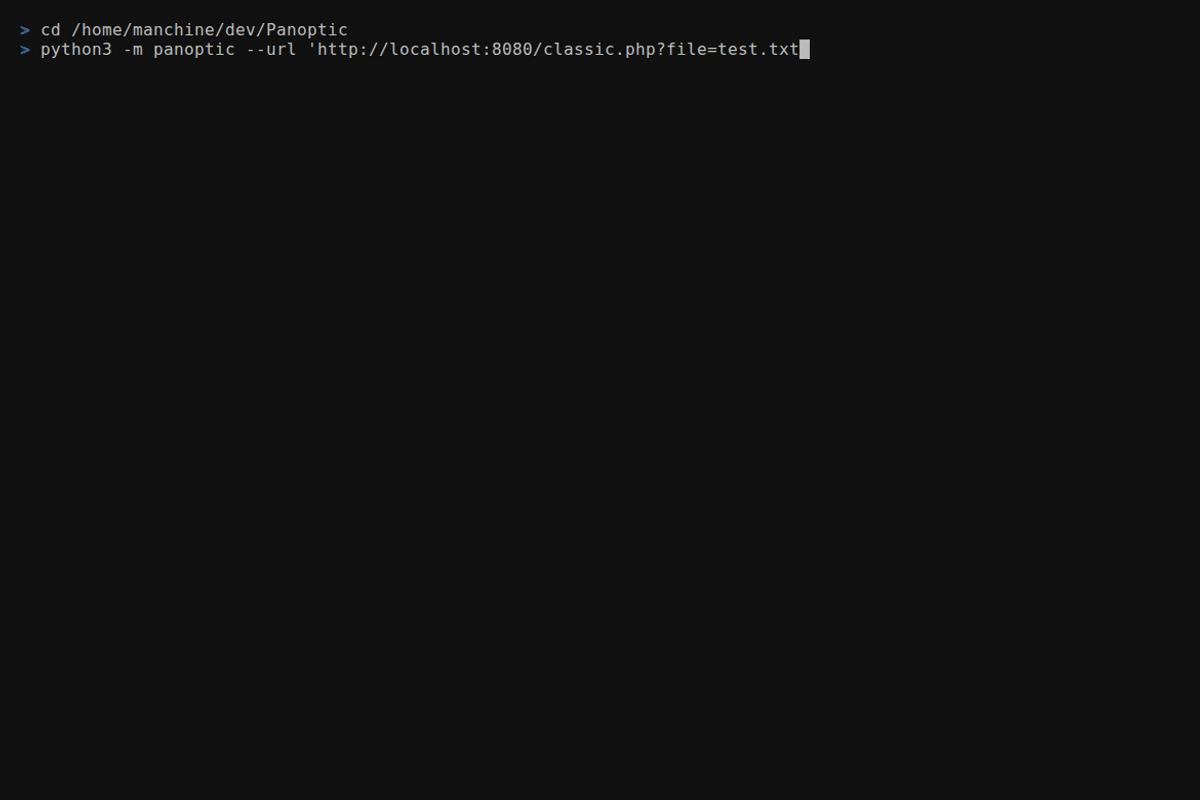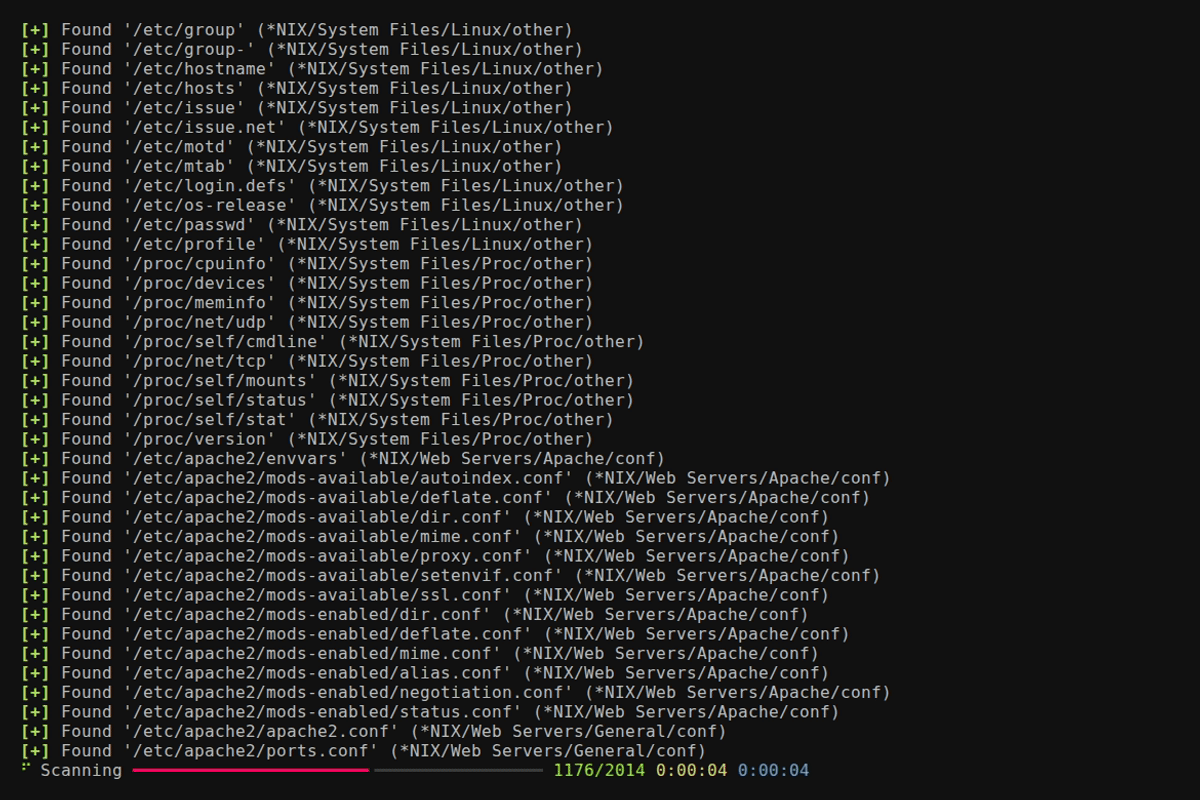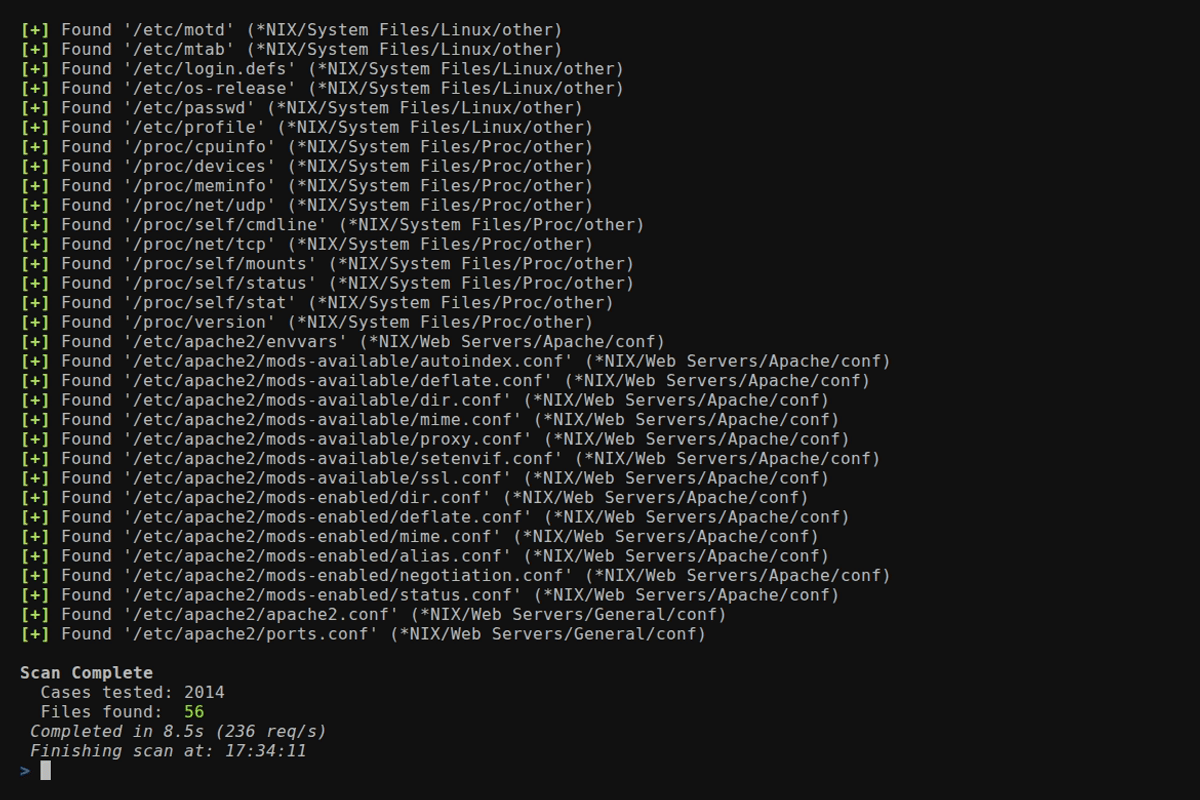 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 egi08/cve-2019-12102-scanner
Automated scanner for CVE-2019-12102 unauthenticated file upload vulnerability in Kentico CMS. Checks domains, verifies with hash parameter, and…
 gazettel/cve-2020-17519
Python-based directory traversal exploit for CVE-2020-17519 (Apache Flink) with multi-threading, proxy support, and configurable depth for retrieving…