
Alfa-Perl-RCE-ZoneH-Grabber-Python
 jenderal92/alfa-perl-rce-zoneh-grabber-python
Python2.7
information-gatheringosintreconnaissance+2
1
jenderal92/alfa-perl-rce-zoneh-grabber-pythonPython2.7
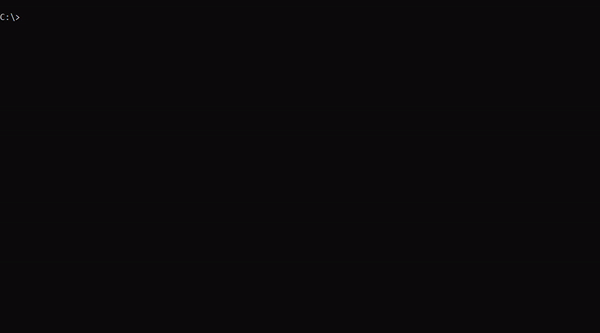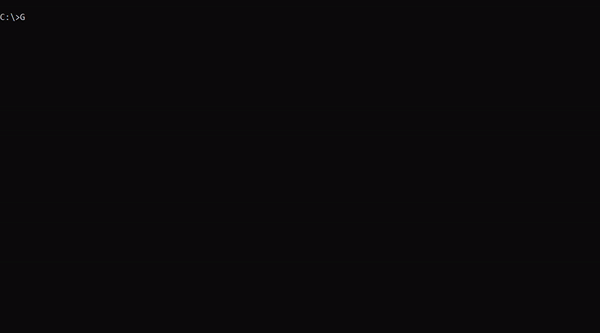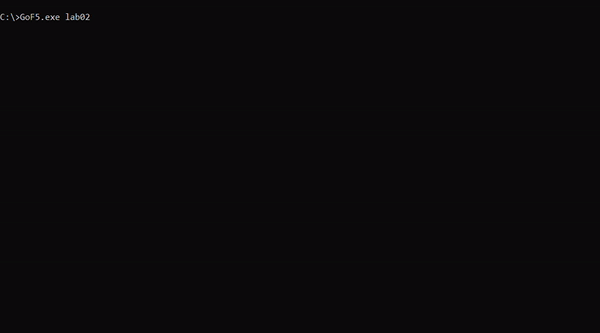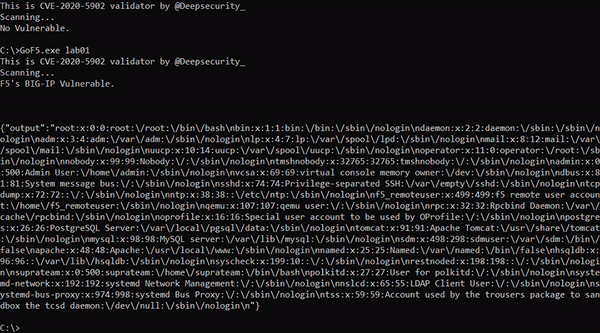 deepsecurity-pe/gof5-cve-2020-5902
Script para validar CVE-2020-5902 hecho en Go.
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 keraattin/cve-2026-39987
Detection and exploitation toolkit for CVE-2026-39987, a pre-auth RCE in Marimo notebooks. Includes Python scanner and Nmap NSE script to identify…
 cybercrewinc/cve-2025-64027
Reflected Cross-Site Scripting in Snipe-IT CSV Import Workflow
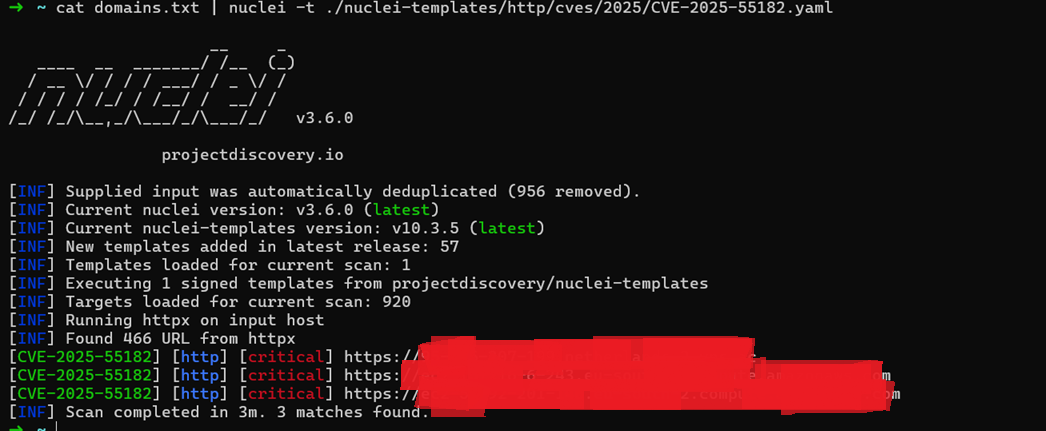 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 pog-frog/cve-2022-44268
Generates malicious PNG files to exploit ImageMagick LFI vulnerability (CVE-2022-44268) for arbitrary file read, with extraction script for…
 gmh5225/cve-2022-24716-2
CVE-2022-24716 (Arbitrary File Disclosure Icingaweb2)
 jakabakos/cve-2024-36401-geoserver-rce
Python script to detect and exploit CVE-2024-36401, a critical RCE vulnerability in GeoServer/GeoTools, with optional OOB server support for blind…
 raghu66669999/wordpress-snapcreek
snapcreek_duplicator file read vulnerability https://www.cvedetails.com/cve/CVE-2020-11738/
 zs1n/cve-2024-47533
PoC of CVE-2025-47533 Clobber RCE
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 btnz-k/emby_ssrf
Metasploit auxiliary module that identifies Emby Media Server version and exploits CVE-2020-26948 SSRF vulnerability to scan internal network…
 labsbots/cve-2017-9506
Atlassian Jira XSS attack via Server Side Request Forgery (SSRF).
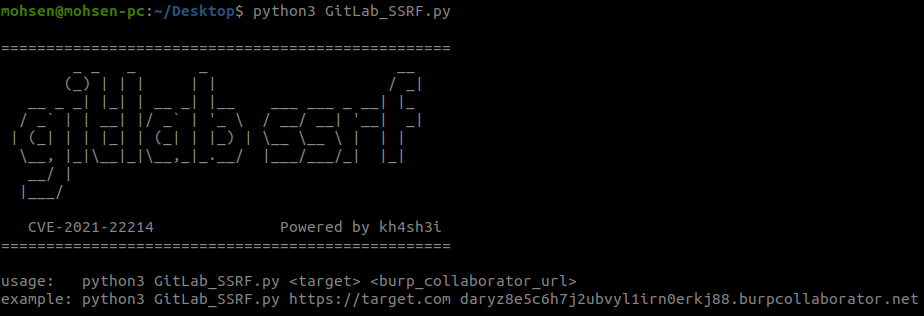 kh4sh3i/gitlab-ssrf-cve-2021-22214
Proof-of-concept exploit for CVE-2021-22214, a server-side request forgery in GitLab webhooks, allowing unauthenticated attackers to make internal…
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 argonx21/cve-2022-43980
Stored Cross Site Scripting Vulnerability in the network maps edit functionality