
CVE-2026-71205-PoC
 nel-droid/cve-2026-71205-poc
PoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)
authenticationexploitationpassword-attacks+4
nel-droid/cve-2026-71205-pocPoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)
 hussainfathy/cve-2024-28999
Exploit for CVE-2024-28999 SolarWinds Platform Race Condition Vulnerability - login page
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
 redteampentesting/cve-2023-33243
PoC for login with password hash in STARFACE
 rajneeshkarya/cve-2023-3460
Exploit for the vulnerability of Ultimate Member Plugin.
 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
 zycoder0day/cve-2026-5076
Proof-of-concept exploit for CVE-2026-5076 demonstrating unauthenticated admin account takeover in ARMember Premium via SQL injection and plaintext…
 vincent-vbg/cve-2025-58434-poc
This repository contains a Proof of Concept (PoC) Python script for CVE-2025-58434, which enables attackers to change passwords of other users…
 1beelze/cve-2026-11387
Exploits unauthenticated privilege escalation in SMS Alert WooCommerce plugin (CVE-2026-11387) via OTP bypass and arbitrary password reset, with…
 0xdtc/bludit-3.9.2-auth-bruteforce-bypass-cve-2019-17240
Bludit 3.9.2 - Auth Bruteforce Bypass CVE:2019-17240 Refurbish In bash
 redsplit/shiguresh
CVE-2004-1769 // Mass cPanel Reset password
 anothersec/cve-2025-4796
eventin <= 4.0.34 - privilege escalation via user email change / account takeover for authenticated contributor+
 hatlesswizard/cve-2023-6875
CVE-2023-6875 exploit written for Xakep.Ru
 nxploited/cve-2025-15030
User Profile Builder < 3.15.2 - Unauthenticated Arbitrary Password Reset
 aakashtyal/2fa-bypass-using-a-brute-force-attack-cve-2025-60424
Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…
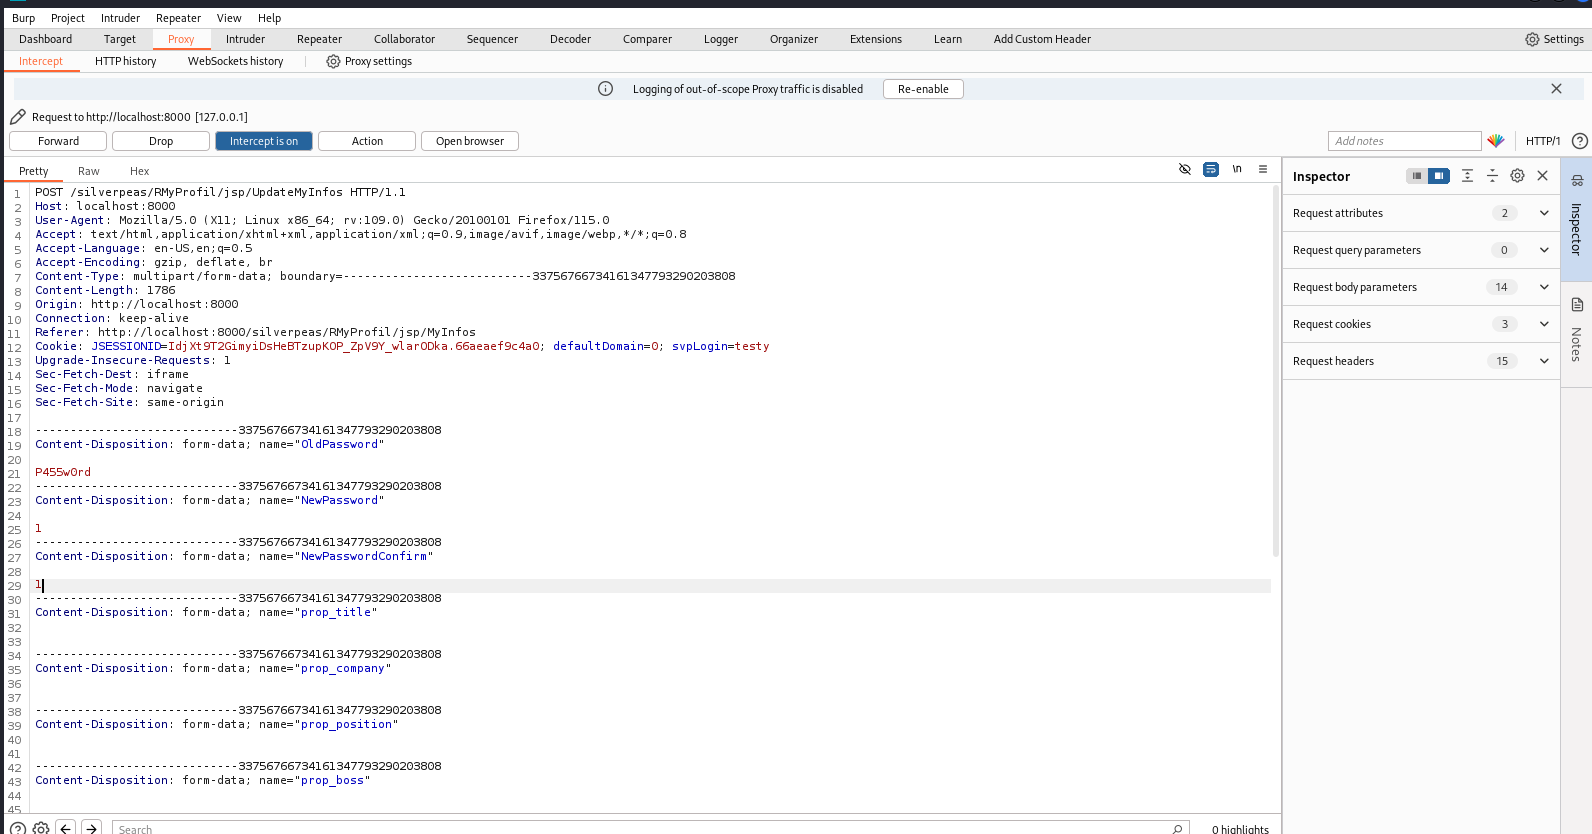 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.