
wp2shell
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
api-securityexploitationpassword-cracking+4
iqbalx7/wp2shellunauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 kyomahooin/cve-2008-6970
Blind SQL injection brute force.
 1n3/wordpress-xmlrpc-brute-force-exploit
Wordpress XMLRPC System Multicall Brute Force Exploit (0day) by 1N3 @ CrowdShield
 inflixim4be/cve-2020-15392
Proof-of-concept exploit for user enumeration vulnerability in Supravizio BPM 10.1.2 via password recovery response differences, enabling brute force…
 kavishgr/xmlrpc-bruteforcer
An XMLRPC brute forcer targeting Wordpress written in Python 3. (DISCONTINUED)
 artemy-ccrsky/cve-2024-39211
User Enumeration vulnerability in Kaiten (workflow management system)
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 aakashtyal/2fa-bypass-using-a-brute-force-attack-cve-2025-60424
Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…
 gl1tch0x1/ghost-cms-exploit
Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…
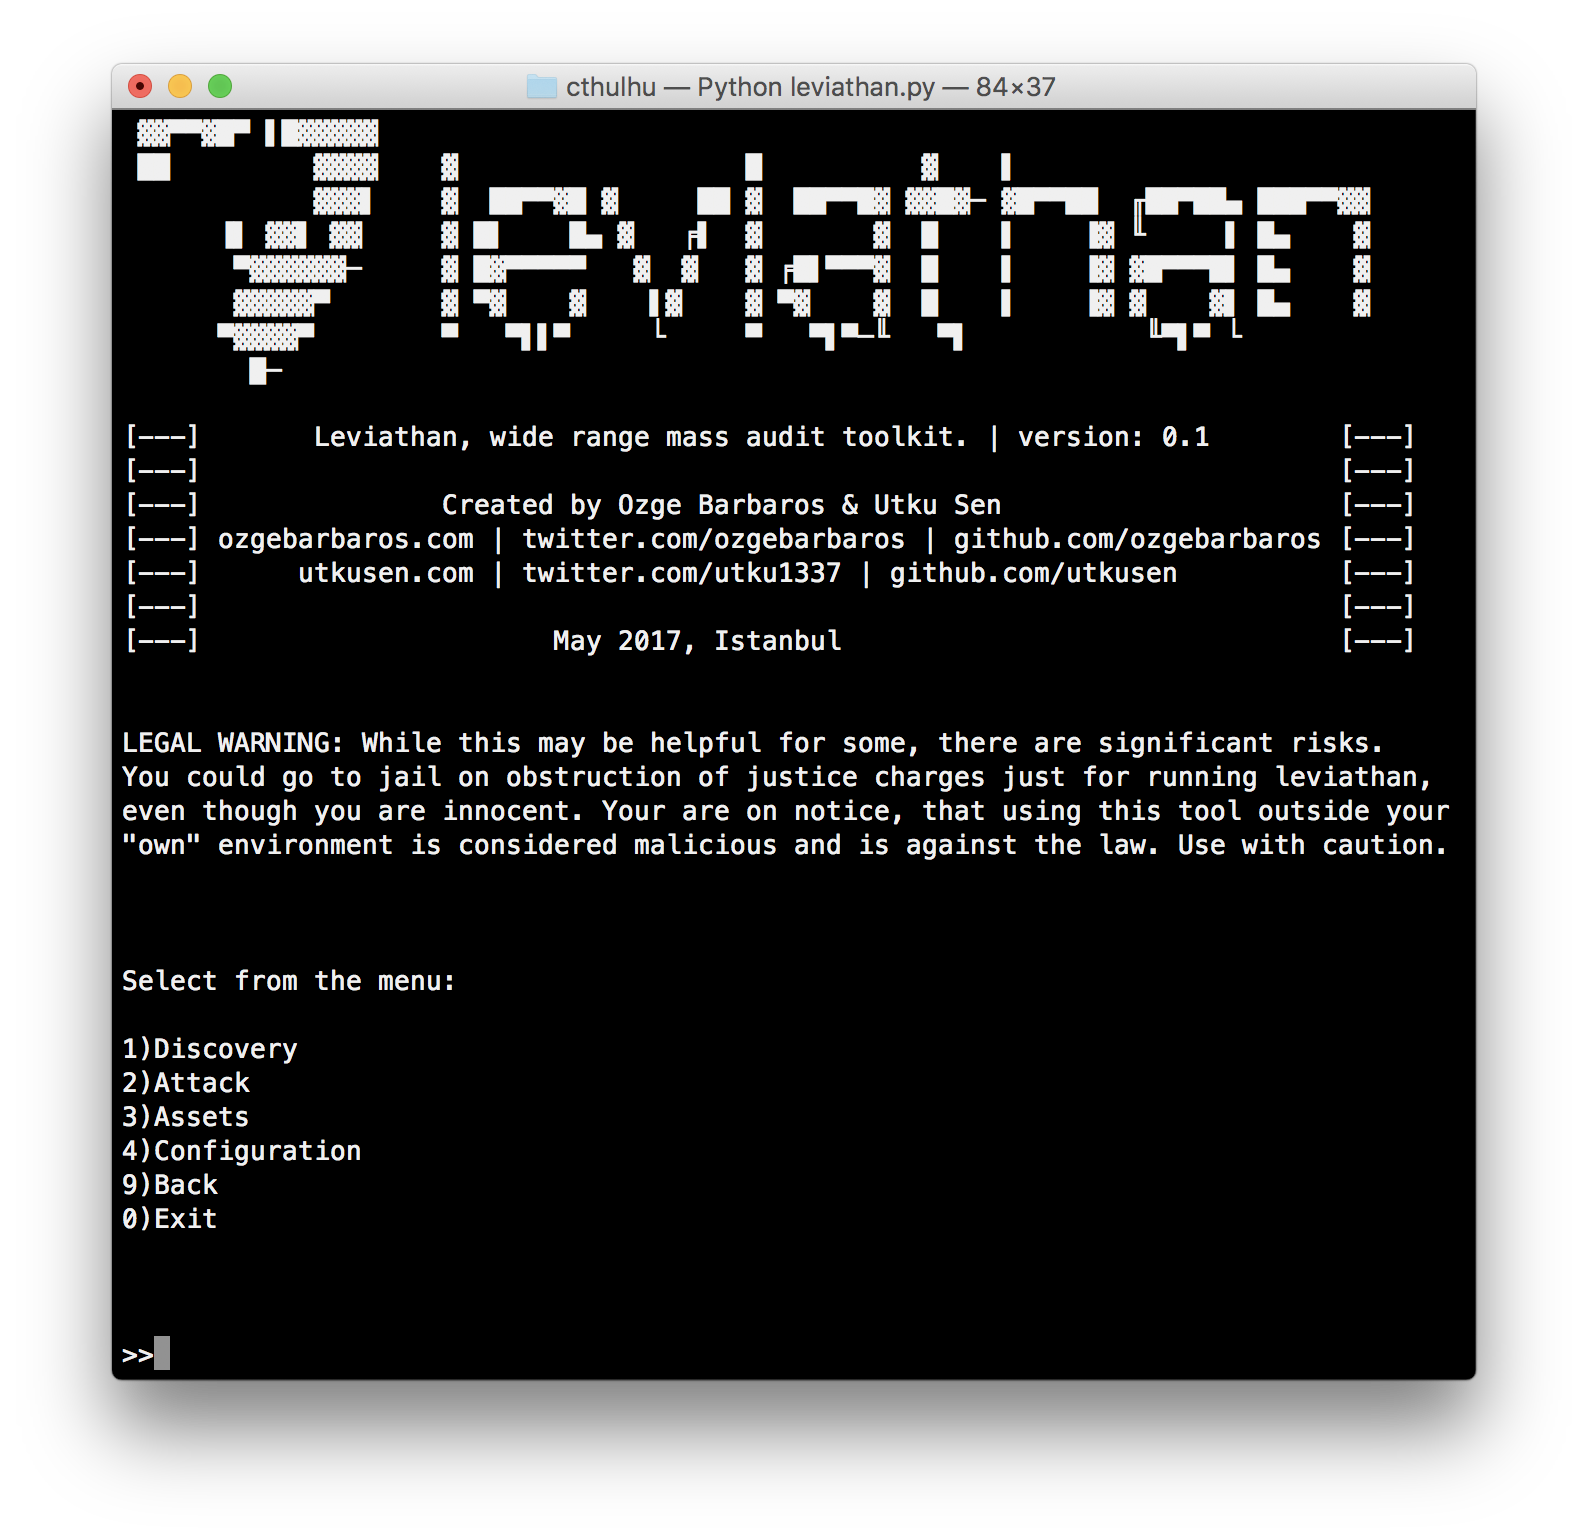 utkusen/leviathan
wide range mass audit toolkit
 coalfire-research/doozer
Password cracking utility
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…