CMS-Made-Simple-2.2.9-CVE-2019-9053

Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…

Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…

Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…

Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…

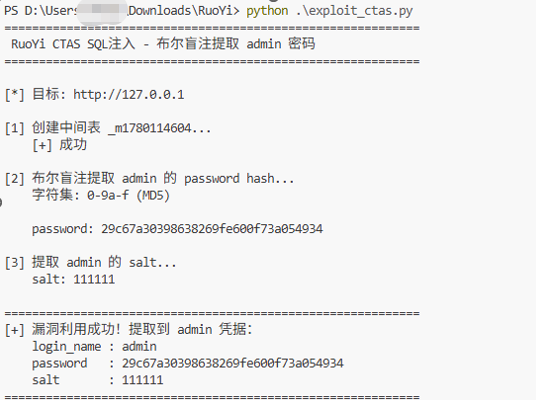
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3

Exploit for CVE-2025-2011

This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.

CMS Made Simple < 2.2.10 - SQL Injection . Actual working version

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.

Blind SQL injection brute force.

Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…

Improved code of Daniele Scanu SQL Injection exploit

Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…

Proof of Concept code for exploitation of CVE-2024-38793 (Best Restaurant Menu by PriceListo <= 1.4.1 - Authenticated (Contributor+) SQL Injection)

Exploits Python cve-2019-9053– by HackHeart

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…