

joomla-bruteforce
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
authenticationpassword-attackspassword-cracking+4
138
ajnik/joomla-bruteforcePython script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 iltosec/cve-2026-54596
Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database…
 leonardobg/cve-2023-36144
Proof-of-concept exploit for CVE-2023-36144 demonstrating unauthenticated backup file download on Intelbras SG 2404 MR L2+ switch, exposing device…
 jcarabantes/cve-2022-23046
Proof-of-concept exploit for CVE-2022-23046, an authenticated SQL injection in PhpIPAM v1.4.4. Extracts server info, SMTP settings, user hashes, and…
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 x3rx3ssec/cve-2025-2011
Exploit for CVE-2025-2011
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
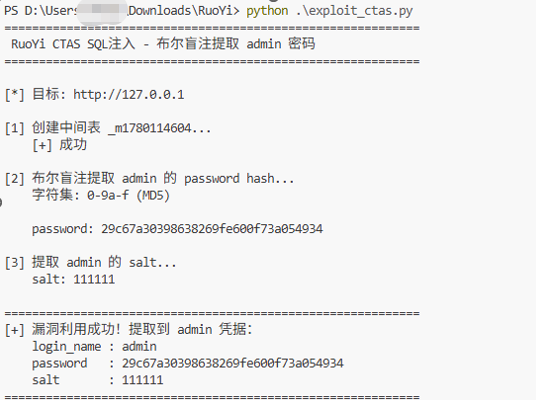 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 kyomahooin/cve-2008-6970
Blind SQL injection brute force.
 ret2desync/cve-2024-38793-poc
Proof of Concept code for exploitation of CVE-2024-38793 (Best Restaurant Menu by PriceListo <= 1.4.1 - Authenticated (Contributor+) SQL Injection)
 offxec/thedoc
Automates SQL injection exploitation with SQLMAP, crawls for vulnerabilities, extracts database credentials, finds admin login pages, and cracks…