
CVE-2025-50565
 m0b1u3/cve-2025-50565
Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.
database-securityinformation-gatheringpenetration-testing+2
m0b1u3/cve-2025-50565Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.
 caffeinated-labs/cve-2023-36644
Proof-of-concept exploit for CVE-2023-36644, demonstrating remote information disclosure via incorrect access control in ITB-GmbH TradePro v9.5…
 randomrobbiebf/cve-2023-5070
Social Media Share Buttons & Social Sharing Icons <= 2.8.5 - Information Exposure
 randomrobbiebf/learning-management-system
Masteriyo - LMS for WordPress <= 1.6.7 - Sensitive Information Exposure
 p33d/cve-2024-8275
Exploit script for CVE-2024-8275, a critical unauthenticated SQL injection in The Events Calendar WordPress plugin, enabling database information…
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV
 joaosilva21/cve-2024-43018
Proof-of-concept for CVE-2024-43018: SQL injection in Piwigo 13.8.0 via unsanitized max_level and min_register parameters, enabling information…
 gunzf0x/cve-2023-23752
Go-based exploit for CVE-2023-23752 targeting Joomla CMS. Performs authenticated information disclosure and privilege escalation via a single…
 svaltheim/cve-2023-23752
Python exploit for Joomla! v4.2.8 unauthenticated information disclosure vulnerability (CVE-2023-23752). Extracts sensitive configuration data from…
 nxploited/cve-2023-47668
Python exploit for CVE-2023-47668 that extracts sensitive log information from vulnerable Restrict Content WordPress plugin versions <= 3.2.7.
 koyomihack00/cve-2025-47226
This CVE - PoC about information on the CVEs I found.
 omershaik0/cve-2023-36085_sisqualwfm-host-header-injection
This repository contains information related CVE-2023-36085 a host header injection vulnerability discovered in SISQUALWFM version 7.1.319.103, which…
 guillermogm4/cve-2024-1302---badgermeter-moni-tool-sensitive-information-exposure
Proof-of-concept exploit for CVE-2024-1302 demonstrating unauthenticated log file download in Badgermeter moni:tool, exposing sensitive information…
 jfriedli/cve-2023-3897
Exploit for CVE-2023-3897 enabling username enumeration via CAPTCHA bypass in On-premise SureMDM on Windows. Includes PoC script for local user…
 nxploited/cve-2024-12542-poc
Proof-of-concept exploit for CVE-2024-12542 targeting unauthenticated sensitive information exposure in WordPress linkID plugin via missing…
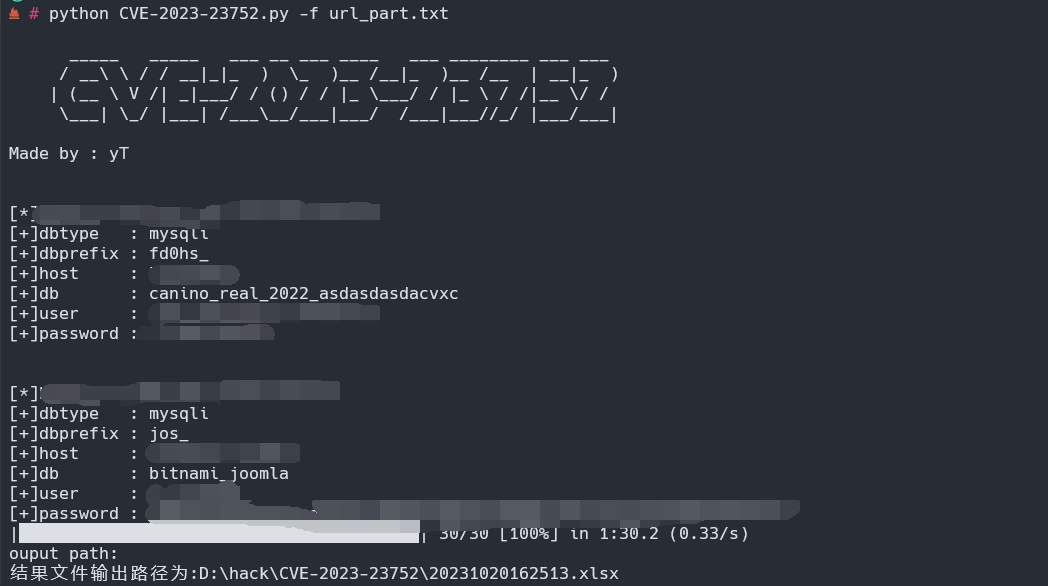 ytxzx/cve-2023-23752
Python-based exploit for CVE-2023-23752 targeting Joomla 4.0.0-4.2.7 unauthorized REST API access, enabling sensitive information disclosure through…
 0xx01/cve-2023-23752
A simple bash script to exploit Joomla! < 4.2.8 - Unauthenticated information disclosure
 ktn1990/cve-2024-13513
Oliver POS – A WooCommerce Point of Sale (POS) <= 2.4.2.3 - Sensitive Information Exposure to Privilege Escalation